
Match the PowerSploit module/script to the respective description.
Place the options in the following order:
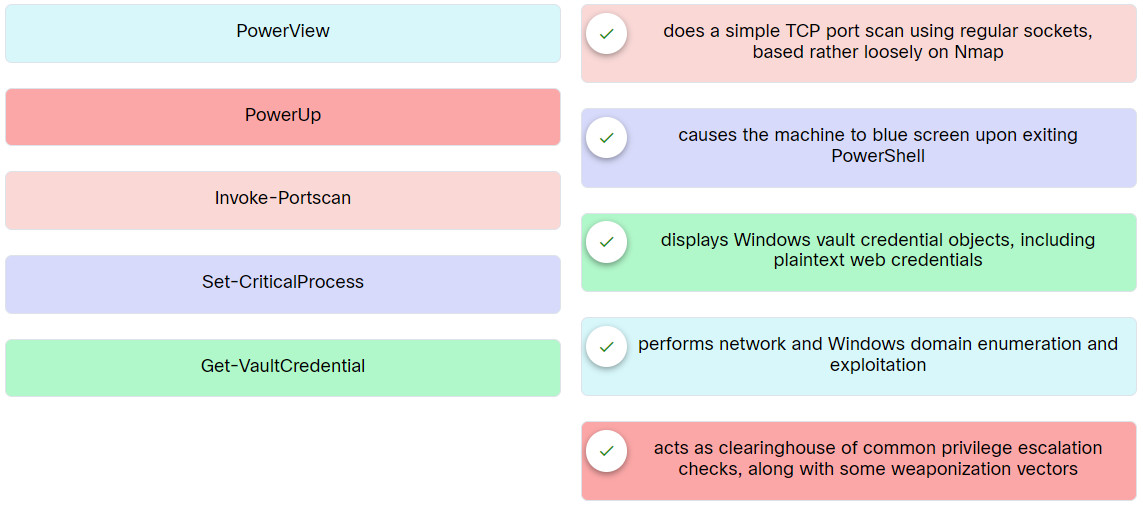
| Invoke-Portscan | does a simple TCP port scan using regular sockets, based rather loosely on Nmap |
| PowerUp | acts as clearinghouse of common privilege escalation checks, along with some weaponization vectors |
| PowerView | performs network and Windows domain enumeration and exploitation |
| Get-VaultCredential | displays Windows vault credential objects, including plaintext web credentials |
| Set-CriticalProcess | causes the machine to blue screen upon exiting PowerShell |
Related exam: Ethical Hacker: Course Final Exam Answers
