1. True or False? A HIPS can be configured in either promiscuous or inline mode.
- True
- False
2. What is true of a NIPS that is running in inline mode?
- It can not stop malicious traffic from reaching its destination.
- NIPS post-event responses require assistance from other networking devices.
- It can add latency to the network.
- It requires SPAN to perform traffic mirroring in order to operate.
3. What is true of a HIPS?
- HIPS software combines anti-virus, anti-malware, and firewall functionality.
- HIPS software makes a network-based IPS unnecessary.
- HIPS software is aware of conditions throughout the network.
- HIPS can not prevent hosts from participating in DDoS attacks.
4. What is an example of a HIPS?
- a Cisco Firepower appliance
- Windows Defender
- a router with IPS software
- an ASA firewall device
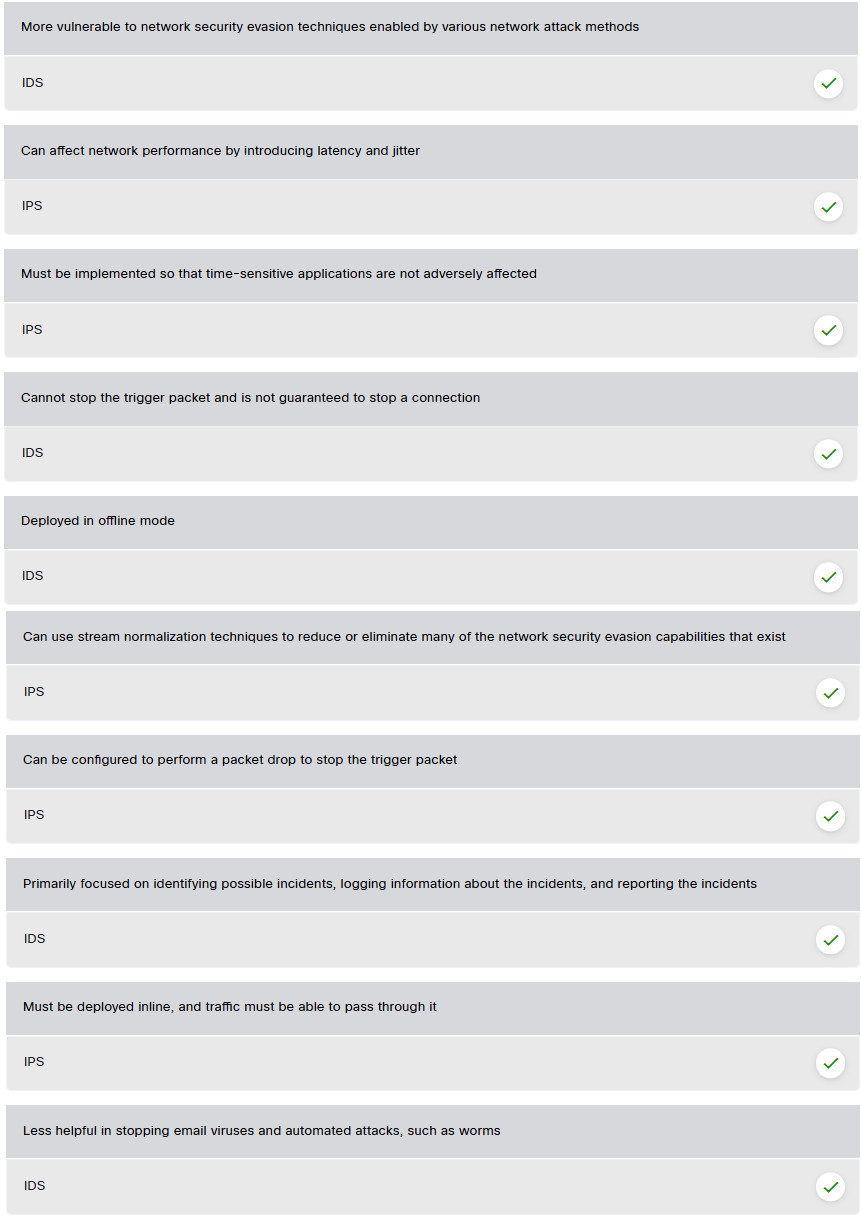
5. Select the corresponding delivery method for each characteristic.
More vulnerable to network security evasion techniques enabled by various network attack methods
- IDS
Can affect network performance by introducing latency and jitter
- IPS
Must be implemented so that time-sensitive applications are not adversely affected
- IPS
Cannot stop the trigger packet and is not guaranteed to stop a connection
- IDS
Deployed in offline mode
- IDS
Can use stream normalization techniques to reduce or eliminate many of the network security evasion capabilities that exist
- IPS
Can be configured to perform a packet drop to stop the trigger packet
- IPS
Primarily focused on identifying possible incidents, logging information about the incidents, and reporting the incidents
- IDS
Must be deployed inline, and traffic must be able to pass through it
- IPS
Less helpful in stopping email viruses and automated attacks, such as worms
- IDS