
Cybersecurity Essentials (CyberEss) Course Final Exam Answers v3.0
Cybersecurity Essentials 1.1 Final Quiz Answers Full Questions
1. Which statement best describes a motivation of hacktivists?
- They are trying to show off their hacking skills.
- They are interested in discovering new exploits.
- They are curious and learning hacking skills.
- They are part of a protest group behind a political cause.
2. Which type of cybercriminal is the most likely to create malware to compromise an organization by stealing credit card information?
- white hat hackers
- black hat hackers
- gray hat hackers
- script kiddies
3. A specialist in the HR department is invited to promote the cybersecurity program in community schools. Which three topics would the specialist emphasize in the presentation to draw students to this field? (Choose three.)
- a career-field in high-demand
- service to the public
- high earning potential
- a job with routine, day-to-day tasks
- a field requiring a PhD degree
- the CompTIA A+ certification provides an adequate knowledge base for the field
4. An organization allows employees to work from home two days a week. Which technology should be implemented to ensure data confidentiality as data is transmitted?
- SHS
- VLANS
- RAID
- VPN
5. Which type of networks poses increasing challenges to cybersecurity specialists due to the growth of BYOD on campus?
- wireless networks
- wired networks
- sneaker net
- virtual networks
6. A cybersecurity specialist is working with the IT staff to establish an effective information security plan. Which combination of security principles forms the foundation of a security plan?
- confidentiality, integrity, and availability
- technologies, policies, and awareness
- secrecy, identify, and nonrepudiation
- encryption, authentication, and identification
7. Which framework should be recommended for establishing a comprehensive information security management system in an organization?
- ISO/IEC 27000
- ISO OSI model
- NIST/NICE framework
- CIA Triad
8. What are three states of data during which data is vulnerable? (Choose three.)
- data in-process
- stored data
- data in-transit
- data encrypted
- purged data
- data decrypted
9. Users report that the database on the main server cannot be accessed. A database administrator verifies the issue and notices that the database file is now encrypted. The organization receives a threatening email demanding payment for the decryption of the database file. What type of attack has the organization experienced?
- man-in-the-middle attack
- ransomeware
- Trojan horse
- DoS attack
10. What three best practices can help defend against social engineering attacks? (Choose three.)
- Enable a policy that states that the IT department should supply information over the phone only to managers.
- Add more security guards.
- Resist the urge to click on enticing web links.
- Deploy well-designed firewall appliances.
- Educate employees regarding policies.
- Do not provide password resets in a chat window.
11. Which statement describes a distributed denial of service attack?
- An attacker sends an enormous quantity of data that a server cannot handle.
- An attacker builds a botnet comprised of zombies.
- An attacker views network traffic to learn authentication credentials.
- One computer accepts data packets based on the MAC address of another computer.
12. A cyber criminal sends a series of maliciously formatted packets to the database server. The server cannot parse the packets and the event causes the server crash. What is the type of attack the cyber criminal launches?
- DoS
- man-in-the-middle
- packet Injection
- SQL injection
13. An executive manager went to an important meeting. The secretary in the office receives a call from a person claiming that the executive manager is about to give an important presentation but the presentation files are corrupted. The caller sternly recommends that the secretary email the presentation right away to a personal email address. The caller also states that the executive is holding the secretary responsible for the success of this presentation. Which type of social engineering tactic would describe this scenario?
- urgency
- intimidation
- familiarity
- trusted partners
14. What are the two most effective ways to defend against malware? (Choose two.)
- Implement network firewalls.
- Install and update antivirus software.
- Implement RAID.
- Update the operating system and other application software.
- Implement strong passwords.
- Implement a VPN.
15. The employees in a company receive an email stating that the account password will expire immediately and requires a password reset within 5 minutes. Which statement would classify this email?
- It is a piggy-back attack.
- It is an impersonation attack.
- It is a DDoS attack.
- It is a hoax.
16. In which situation would a detective control be warranted?
- when the organization needs to look for prohibited activity
- after the organization has experienced a breach in order to restore everything back to a normal state
- when the organization cannot use a guard dog, so it is necessary to consider an alternative
- when the organization needs to repair damage
17. An organization has implemented antivirus software. What type of security control did the company implement?
- recovery control
- deterrent control
- detective control
- compensative control
18. Alice and Bob are using public key encryption to exchange a message. Which key should Alice use to encrypt a message to Bob?
- the private key of Alice
- the public key of Bob
- the private key of Bob
- the public key of Alice
19. Which statement describes a characteristics of block ciphers?
- Block ciphers encrypt plaintext one bit at a time to form a block.
- Block ciphers result in output data that is larger than the input data most of the time.
- Block ciphers result in compressed output.
- Block ciphers are faster than stream ciphers.
20. The IT department is tasked to implement a system that controls what a user can and cannot do on the corporate network. Which process should be implemented to meet the requirement?
- user login auditing
- a set of attributes that describes user access rights
- observations to be provided to all employees
- a biometric fingerprint reader
21. Alice and Bob use a pre-shared key to exchange a confidential message. If Bob wants to send a confidential message to Carol, what key should he use?
- the same pre-shared key he used with Alice
- the private key of Carol
- a new pre-shared key
- the public key of Bob
22. Which access control strategy allows an object owner to determine whether to allow access to the object?
- RBAC
- DAC
- MAC
- ACL
23. Which method is used by steganography to hide text in an image file?
- data obfuscation
- data masking
- least significant bit
- most significant bit
24. The X.509 standards defines which security technology?
- digital certificates
- biometrics
- strong passwords
- security tokens
25. Which hashing algorithm is recommended for the protection of sensitive, unclassified information?
- MD5
- AES-256
- 3DES
- SHA-256
26. Technicians are testing the security of an authentication system that uses passwords. When a technician examines the password tables, the technician discovers the passwords are stored as hash values. However, after comparing a simple password hash, the technician then discovers that the values are different from those on other systems. What are two causes of this situation? (Choose two.)
- Both systems scramble the passwords before hashing.
- The systems use different hashing algorithms.
- One system uses hashing and the other uses hashing and salting.
- Both systems use MD5.
- One system uses symmetrical hashing and the other uses asymmetrical hashing.
27. You have been asked to work with the data collection and entry staff in your organization in order to improve data integrity during initial data entry and data modification operations. Several staff members ask you to explain why the new data entry screens limit the types and size of data able to be entered in specific fields. What is an example of a new data integrity control?
- data encryption operations that prevent any unauthorized users from accessing sensitive data
- a limitation rule which has been implemented to prevent unauthorized staff from entering sensitive data
- data entry controls which only allow entry staff to view current data
- a validation rule which has been implemented to ensure completeness, accuracy, and consistency of data
28. What technology should be implemented to verify the identity of an organization, to authenticate its website, and to provide an encrypted connection between a client and the website?
- digital signature
- salting
- digital certificate
- asymmetric encryption
29. Your organization will be handling market trades. You will be required to verify the identify of each customer who is executing a transaction. Which technology should be implemented to authenticate and verify customer electronic transactions?
- data hashing
- asymmetrical encryption
- symmetrical encryption
- digital certificates
30. Alice and Bob are using a digital signature to sign a document. What key should Alice use to sign the document so that Bob can make sure that the document came from Alice?
- public key from Bob
- private key from Alice
- username and password from Alice
- private key from Bob
31. An organization has determined that an employee has been cracking passwords on administrative accounts in order to access very sensitive payroll information. Which tools would you look for on the system of the employee? (Choose three)
- rainbow tables
- lookup tables
- algorithm tables
- password digest
- rouge access points
- reverse lookup tables
32. An organization wants to adopt a labeling system based on the value, sensitivity, and criticality of the information. What element of risk management is recommended?
- asset classification
- asset identification
- asset availability
- asset standardization
33. An organization has recently adopted a five nines program for two critical database servers. What type of controls will this involve?
- stronger encryption systems
- improving reliability and uptime of the servers
- remote access to thousands of external users
- limiting access to the data on these systems
34. Being able to maintain availability during disruptive events describes which of the principles of high availability?
- single point of failure
- system resiliency
- fault tolerance
- uninterruptible services
35. Which risk mitigation strategies include outsourcing services and purchasing insurance?
- avoidance
- transfer
- reduction
- acceptance
36. The awareness and identification of vulnerabilities is a critical function of a cybersecurity specialist. Which of the following resources can be used to identify specific details about vulnerabilities?
- CVE national database
- NIST/NICE framework
- ISO/IEC 27000 model
- Infragard
37. Which technology would you implement to provide high availability for data storage?
- N+1
- software updates
- RAID
- hot standby
38. Which two values are required to calculate annual loss expectancy? (Choose two.)
- annual rate of occurrence
- asset value
- frequency factor
- exposure factor
- single loss expectancy
- quantitative loss value
39. What is it called when an organization only installs applications that meet its guidelines, and administrators increase security by eliminating all other applications?
- asset availability
- asset identification
- asset classification
- asset standardization
40. There are many environments that require five nines, but a five nines environment may be cost prohibitive. What is one example of where the five nines environment might be cost prohibitive?
- department stores at the local mall
- the front office of a major league sports team
- the U.S. Department of Education
- the New York Stock Exchange
41. Which technology can be used to protect VoIP against eavesdropping?
- ARP
- encrypted voice messages
- strong authentication
- SSH
42. Mutual authentication can prevent which type of attack?
- wireless poisoning
- wireless IP spoofing
- wireless sniffing
- man-in-the-middle
43. Which of the following products or technologies would you use to establish a baseline for an operating system?
- SANS Baselining System (SBS)
- Microsoft Security Baseline Analyzer
- MS Baseliner
- CVE Baseline Analyzer
44. What Windows utility should be used to configure password rules and account lockout policies on a system that is not part of a domain?
- Active Directory Security tool
- Computer Management
- Local Security Policy tool
- Event Viewer security log
45. What describes the protection provided by a fence that is 1 meter in height?
- It deters casual trespassers only.
- It prevents casual trespassers because of its height.
- The fence deters determined intruders.
- It offers limited delay to a determined intruder.
46. Which wireless standard made AES and CCM mandatory?
- WPA2
- WEP
- WEP2
- WPA
47. Which three protocols can use Advanced Encryption Standard (AES)? (Choose three.)
- WEP
- WPA2
- WPA
- 802.11q
- 802.11i
- TKIP
48. Which website offers guidance on putting together a checklist to provide guidance on configuring and hardening operating systems?
- Internet Storm Center
- The Advanced Cyber Security Center
- The National Vulnerability Database website
- CERT
49. Which law was enacted to prevent corporate accounting-related crimes?
- The Federal Information Security Management Act
- Gramm-Leach-Bliley Act
- Import/Export Encryption Act
- Sarbanes-Oxley Act
50. Which cybersecurity weapon scans for use of default passwords, missing patches, open ports, misconfigurations, and active IP addresses?
- packet analyzers
- vulnerability scanners
- packet sniffers
- password crackers
51. A cybersecurity specialist is asked to identify the potential criminals known to attack the organization. Which type of hackers would the cybersecurity specialist be least concerned with?
- black hat hackers
- gray hat hackers
- script kiddies
- white hat hackers
52. What is an example of early warning systems that can be used to thwart cybercriminals?
- Infragard
- ISO/IEC 27000 program
- Honeynet project
- CVE database
53. Which technology should be used to enforce the security policy that a computing device must be checked against the latest antivirus update before the device is allowed to connect to the campus network?
- SAN
- VPN
- NAC
- NAS
54. Which data state is maintained in NAS and SAN services?
- stored data
- data in-transit
- encrypted data
- data in-process
55. Which technology can be used to ensure data confidentiality?
- hashing
- identity management
- encryption
- RAID
56. What is an impersonation attack that takes advantage of a trusted relationship between two systems?
- man-in-the-middle
- spoofing
- spamming
- sniffing
57. Users report that the network access is slow. After questioning the employees, the network administrator learned that one employee downloaded a third-party scanning program for the printer. What type of malware might be introduced that causes slow performance of the network?
- virus
- worm
- spam
- phishing
58. What type of application attack occurs when data goes beyond the memory areas allocated to the application?
- buffer overflow
- RAM Injection
- SQL injection
- RAM spoofing
59. What type of attack has an organization experienced when an employee installs an unauthorized device on the network to view network traffic?
- sniffing
- spoofing
- phishing
- spamming
60. A penetration testing service hired by the company has reported that a backdoor was identified on the network. What action should the organization take to find out if systems have been compromised?
- Look for policy changes in Event Viewer.
- Scan the systems for viruses.
- Look for unauthorized accounts.
- Look for usernames that do not have passwords.
61. Smart cards and biometrics are considered to be what type of access control?
- administrative
- technological
- logical
- physical
62. Which access control should the IT department use to restore a system back to its normal state?
- compensative
- preventive
- corrective
- detective
63. A user has a large amount of data that needs to be kept confidential. Which algorithm would best meet this requirement?
- 3DES
- ECC
- RSA
- Diffie-Hellman
64. What happens as the key length increases in an encryption application?
- Keyspace increases proportionally.
- Keyspace decreases exponentially.
- Keyspace decreases proportionally.
- Keyspace increases exponentially.
65. You have been asked to describe data validation to the data entry clerks in accounts receivable. Which of the following are good examples of strings, integers, and decimals?
- 800-900-4560, 4040-2020-8978-0090, 01/21/2013
- male, $25.25, veteran
- female, 9866, $125.50
- yes/no 345-60-8745, TRF562
66. Which hashing technology requires keys to be exchanged?
- salting
- AES
- HMAC
- MD5
67. What is a feature of a cryptographic hash function?
- Hashing requires a public and a private key.
- The hash function is a one-way mathematical function.
- The output has a variable length.
- The hash input can be calculated given the output value.
68. A VPN will be used within the organization to give remote users secure access to the corporate network. What does IPsec use to authenticate the origin of every packet to provide data integrity checking?
- salting
- HMAC
- CRC
- password
69. Your risk manager just distributed a chart that uses three colors to identify the level of threat to key assets in the information security systems. Red represents high level of risk, yellow represents average level of threat and green represents low level of threat. What type of risk analysis does this chart represent?
- quantitative analysis
- exposure factor analysis
- loss analysis
- qualitative analysis
70. Keeping data backups offsite is an example of which type of disaster recovery control?
- management
- preventive
- detective
- corrective
71. What are two incident response phases? (Choose two.)
- detection and analysis
- confidentiality and eradication
- prevention and containment
- mitigation and acceptance
- containment and recovery
- risk analysis and high availability
72. The team is in the process of performing a risk analysis on the database services. The information collected includes the initial value of these assets, the threats to the assets and the impact of the threats. What type of risk analysis is the team performing by calculating the annual loss expectancy?
- quantitative analysis
- qualitative analysis
- loss analysis
- protection analysis
73. What approach to availability provides the most comprehensive protection because multiple defenses coordinate together to prevent attacks?
- obscurity
- limiting
- layering
- diversity
74. Which utility uses the Internet Control Messaging Protocol (ICMP)?
- NTP
- ping
- RIP
- DNS
75. In a comparison of biometric systems, what is the crossover error rate?
- rate of false positives and rate of acceptability
- rate of false negatives and rate of false positives
- rate of rejection and rate of false negatives
- rate of acceptability and rate of false negatives
76. Which protocol would be used to provide security for employees that access systems remotely from home?
- WPA
- SSH
- SCP
- Telnet
77. Which threat is mitigated through user awareness training and tying security awareness to performance reviews?
- user-related threats
- device-related threats
- cloud-related threats
- physical threats
78. HVAC, water system, and fire systems fall under which of the cybersecurity domains?
- device
- network
- physical facilities
- user
79. Technologies like GIS and IoE contribute to the growth of large data stores. What are two reasons that these technologies increase the need for cybersecurity specialists? (Choose two.)
- They require 24-hour monitoring.
- They collect sensitive information.
- They contain personal information.
- They increase processing requirements.
- They require more equipment.
- They make systems more complicated.
80. Which two groups of people are considered internal attackers? (Choose two.)
- ex-employees
- amateurs
- black hat hackers
- hacktivists
- trusted partners
81. Which methods can be used to implement multifactor authentication?
- IDS and IPS
- tokens and hashes
- VPNs and VLANs
- passwords and fingerprints
82. A security specialist is asked for advice on a security measure to prevent unauthorized hosts from accessing the home network of employees. Which measure would be most effective?
- Implement a firewall.
- Implement intrusion detection systems.
- Implement a VLAN.
- Implement RAID.
83. What type of attack will make illegitimate websites higher in a web search result list?
- DNS poisoning
- browser hijacker
- spam
- SEO poisoning
84. What is a nontechnical method that a cybercriminal would use to gather sensitive information from an organization?
- man-in-the-middle
- social engineering
- pharming
- ransomeware
85. Which algorithm will Windows use by default when a user intends to encrypt files and folders in an NTFS volume?
- RSA
- DES
- AES
- 3DES
86. Before data is sent out for analysis, which technique can be used to replace sensitive data in nonproduction environments to protect the underlying information?
- data masking substitution
- steganography
- software obfuscation
- steganalysis
87. An organization plans to implement security training to educate employees about security policies. What type of access control is the organization trying to implement?
- administrative
- technological
- physical
- logical
88. Passwords, passphrases, and PINs are examples of which security term?
- authorization
- access
- authentication
- identification
89. What technique creates different hashes for the same password?
- SHA-256
- HMAC
- CRC
- salting
90. You have been asked to implement a data integrity program to protect data files that need to be electronically downloaded by the sales staff. You have decided to use the strongest hashing algorithm available on your systems. Which hash algorithm would you select?
- SHA-1
- AES
- MD5
- SHA-256
91. What kind of integrity does a database have when all its rows have a unique identifier called a primary key?
- entity integrity
- referential integrity
- domain integrity
- user-defined integrity
92. What approach to availability involves using file permissions?
- layering
- simplicity
- obscurity
- limiting
93. Which national resource was developed as a result of a U.S. Executive Order after a ten-month collaborative study involving over 3,000 security professionals?
- ISO OSI model
- NIST Framework
- ISO/IEC 27000
- the National Vulnerability Database (NVD)
94. Which two protocols pose switching threats? (Choose two.)
- RIP
- IP
- ICMP
- WPA2
- STP
- ARP
95. What is the most difficult part of designing a cryptosystem?
- encryption algorithm
- reverse engineering
- key length
- key management
96. What technology should you implement to ensure that an individual cannot later claim that he or she did not sign a given document?
- asymmetric encryption
- digital certificate
- digital signature
- HMAC
97. Which type of cybercriminal attack would interfere with established network communication through the use of constructed packets so that the packets look like they are part of the normal communication?
- packet sniffing
- DNS spoofing
- packet forgery
- rogue Wi-Fi AP
98. An organization just completed a security audit. Your division was cited for not conforming to X.509 requirements. What is the first security control you need to examine?
- VPNs and encryption services
- hashing operations
- data validation rules
- digital certificates
99. Which network logs contain information that a security analyst can use to determine if packets received from the web are in response to legitimate requests or are part of an exploit?
- NBAR logs
- content filter logs
- NetFlow logs
- proxy logs
100. Which technology can be used to prevent a cracker from launching a dictionary or brute-force attack of a hash?
- AES
- MD5
- HMAC
- rainbow tables
101. Which technology can be implemented as part of an authentication system to verify the identification of employees?
- a smart card reader
- SHA-1 hash
- a virtual fingerprint
- a Mantrap
102. Netbus belongs to which malware type?
- backdoor
- logic bomb
- keylogger
- grayware
103. A user complains about frequently receiving messages on the smartphone that urges the user to visit different insurance websites. If the user clicks the link to visit, a user login message will pop up and ask the user to register first. Which wireless and mobile device attack has the user experienced?
- Grayware
- SMiShing
- Bluejacking
- Bluesnarfing
104. Which two commands could be used to check if DNS name resolution is working properly on a Windows PC? (Choose two.)
- net cisco.com
- ipconfig /flushdns
- nbtstat cisco.com
- ping cisco.com
- nslookup cisco.com
105. A router has an existing ACL that permits all traffic from 172.16.0.0. The administrator wants to block packets from host 172.16.0.1 but receives an error. What action can the administrator take?
- Create a second access list denying the host and apply it to the same interface.
- Add a deny any any ACE to access-list 1.
- Manually add the new deny ACE with a sequence number of 5.
- Manually add the new deny ACE with a sequence number of 15.
106. Why would an attacker want to spoof a MAC address?
- so that a switch on the LAN will start forwarding all frames toward the device that is under control of the attacker (that can then capture the LAN traffic)
- so that the attacker can launch another type of attack in order to gain access to the switch
- so that the attacker can capture traffic from multiple VLANs rather than from just the VLAN that is assigned to the port to which the attacker device is attached
- so that a switch on the LAN will start forwarding frames to the attacker instead of to the legitimate host
107. What is the result in the self zone if a router is the source or destination of traffic?
- Only traffic that is destined for the router is permitted.
- No traffic is permitted.
- All traffic is permitted.
- Only traffic that originates in the router is permitted.
108. What are two shared characteristics of the IDS and the IPS? (Choose two.)
- Both are deployed as sensors.
- Both rely on an additional network device to respond to malicious traffic.
- Both have minimal impact on network performance.
- Both use signatures to detect malicious traffic.
- Both analyze copies of network traffic.
109. Which two types of hackers are typically classified as grey hat hackers? (Choose two.)
- cyber criminals
- script kiddies
- hacktivists
- state-sponsored hackers
- vulnerability brokers
110. Which network security tool can detect open TCP and UDP ports on most versions of Microsoft Windows?
- SuperScan
- Nmap
- Zenmap
- L0phtcrack
111. What is the motivation of a white hat attacker?
- fine tuning network devices to improve their performance and efficiency
- studying operating systems of various platforms to develop a new system
- taking advantage of any vulnerability for illegal personal gain
- discovering weaknesses of networks and systems to improve the security level of these systems
112. What are two uses of an access control list? (Choose two.)
- ACLs can control which areas a host can access on a network.
- ACLs provide a basic level of security for network access.
- ACLs can permit or deny traffic based upon the MAC address originating on the router.
- ACLs assist the router in determining the best path to a destination.
- Standard ACLs can restrict access to specific applications and ports.
113. What is the investigator attempting to prove about the USB drive when the evidence is submitted in court?
- The data in the image is an exact copy and nothing has been altered by the process.
- An exact copy cannot be made of a device.
- The investigator found a USB drive and was able to make a copy of it.
- The data is all there.
114. Which two application layer protocols manage the exchange of messages between a client with a web browser and a remote web server? (Choose two.)
- HTTP
- DNS
- HTTPS
- HTML
- DHCP
115. What would be the target of an SQL injection attack?
- DNS
- DHCP
- database
116. Which wireless parameter is used by an access point to broadcast frames that include the SSID?
- passive mode
- channel setting
- security mode
- active mode
117. Match the commonly used ports on a Linux server with the corresponding service:
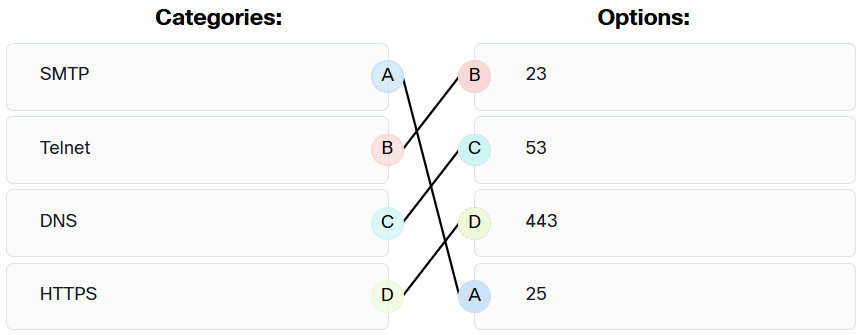
HTTPS → 443
SMTP → 25
Telnet → 23
DNS → 53
118. What is the outcome when a Linux administrator enters the man man command?
- The man man command configures the network interface with a manual address.
- The man man command opens the most recent log file.
- The man man command provides a list of commands available at the current prompt.
- The man man command provides documentation about the man command.
119. How can IMAP be a security threat to a company?
- It can be used to encode stolen data and send to a threat actor.
- Encrypted data is decrypted.
- Someone inadvertently clicks on a hidden iFrame.
- An email can be used to bring malware to a host.
120. Which information can be provided by the Cisco NetFlow utility?
- peak usage times and traffic routing
- source and destination UDP port mapping
- IDS and IPS capabilities
- security and user account restrictions
121. Refer to the exhibit. A security analyst is reviewing an alert message generated by Snort. What does the number 2100498 in the message indicate?

- the message length in bits
- the session number of the message
- the Snort rule that is triggered
- the id of the user that triggers the alert
122. What is an example of a privilege escalation attack?
- A DDoS attack is launched against a government server and causes the server to crash.
- A port scanning attack finds that the FTP service is running on a server that allows anonymous access.
- A threat actor sends an email to an IT manager to request the root access.
- A threat actor performs an access attack and gains the administrator password
123. According to NIST standards, which incident response stakeholder is responsible for coordinating an incident response with other stakeholders to minimize the damage of an incident?
- human resources
- IT support
- management
- legal department
124. Which meta-feature element in the Diamond Model describes information gained by the adversary?
- methodology
- resources
- results
- direction
125. A network administrator is creating a network profile to generate a network baseline. What is included in the critical asset address space element?
- the TCP and UDP daemons and ports that are allowed to be open on the server
- the IP addresses or the logical location of essential systems or data
- the time between the establishment of a data flow and its termination
- the list of TCP or UDP processes that are available to accept data
126. What is the term used when a malicious party sends a fraudulent email disguised as being from a legitimate, trusted source?
- phishing
- Trojan
- backdoor
- vishing
127. What is indicated by a Snort signature ID (SID) that is below 3464?
- The SID was created by Sourcefire and distributed under a GPL agreement.
- This is a custom signature developed by the organization to address locally observed rules.
- The SID was created by the Snort community and is maintained in Community Rules.
- The SID was created by members of EmergingThreats.
128. What is a characteristic of CybOX?
- It is a set of standardized schemata for specifying, capturing, characterizing, and communicating events and properties of network operations.
- It enables the real-time exchange of cyberthreat indicators between the U.S. Federal Government and the private sector.
- It is a set of specifications for exchanging cyberthreat information between organizations.
- It is the specification for an application layer protocol that allows the communication of CTI over HTTPS.
129. What is a feature of distributed firewalls?
- They combine the feature of host-based firewalls with centralized management.
- They all use an open sharing standard platform.
- They use only iptables to configure network rules.
- They use only TCP wrappers to configure rule-based access control and logging systems.
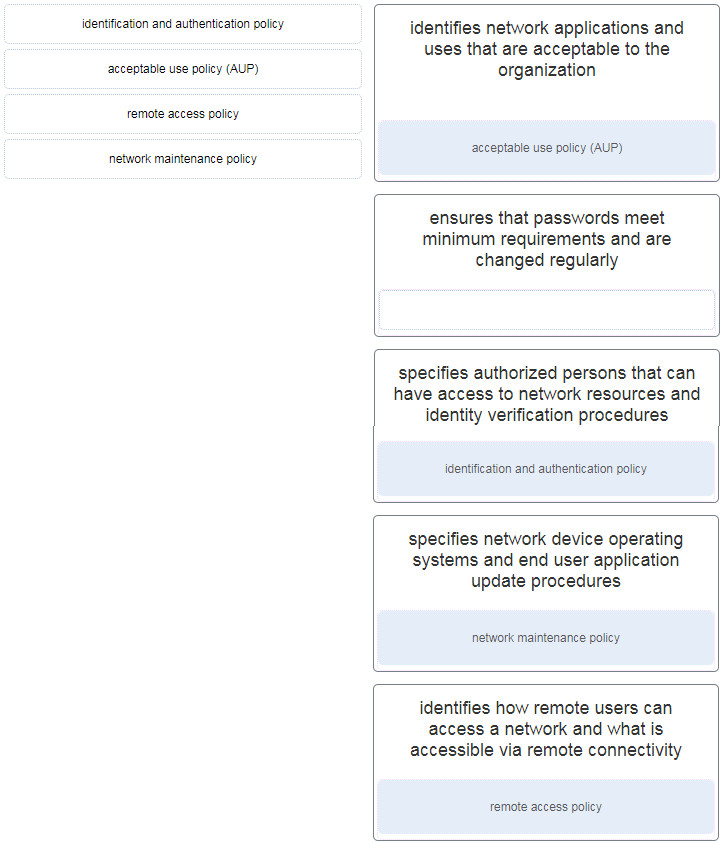
130. Match the security policy with the description:
131. What are two differences between stateful and stateless firewalls? (Choose two.)
- A stateless firewall will provide more logging information than a stateful firewall.
- A stateless firewall provides more stringent control over security than a stateful firewall.
- A stateless firewall is able to filter sessions that use dynamic port negotiations while a stateful firewall cannot.
- A stateless firewall will examine each packet individually while a stateful firewall observes the state of a connection.
- A stateful firewall will prevent spoofing by determining whether packets belong to an existing connection while a stateless firewall follows pre-configured rule sets.
132. Designing a ZPF requires several steps. Which step involves dictating the number of devices between most-secure and least-secure zones and determining redundant devices?
- identify subsets within zones and merge traffic requirements
- design the physical infrastructure
- establish policies between zones
- determine the zones
133. The entrepreneur is concerned about employees having uninterrupted access to important resources and data. Which of the CIA triad components would address the concern?
- integrity
- authentication
- confidentiality
- availability
134. Which cloud security domain describes controls related to securing the data itself?
- Data Security and Encryption
- Application Security
- Security as a Service
- Infrastructure Security
135. Which two advantages in security controls are provided by software-defined networks (SDN) over traditional network security solutions? (Choose two.)
- higher performance than hardware firewalls
- easier insertion into the traffic path
- apply to assets based on more flexible criteria than hardware firewalls
- easier network isolation without constraints of physical hardware
- offer more security features than hardware firewalls
136. A SOHO office is using a public cloud provider to host their website. The IT technician is choosing an approach to protect transaction data between the website and visitors from the internet. Which type of encryption key management method should the technician choose?
- shared-secret key encryption
- secret key encryption
- private key encryption
- public key encryption
137. Which role in a data governance program is responsible for compliance, assigning classifications, and determining access criteria for information assets?
- data controller
- data protection officer
- data owner
- data custodian
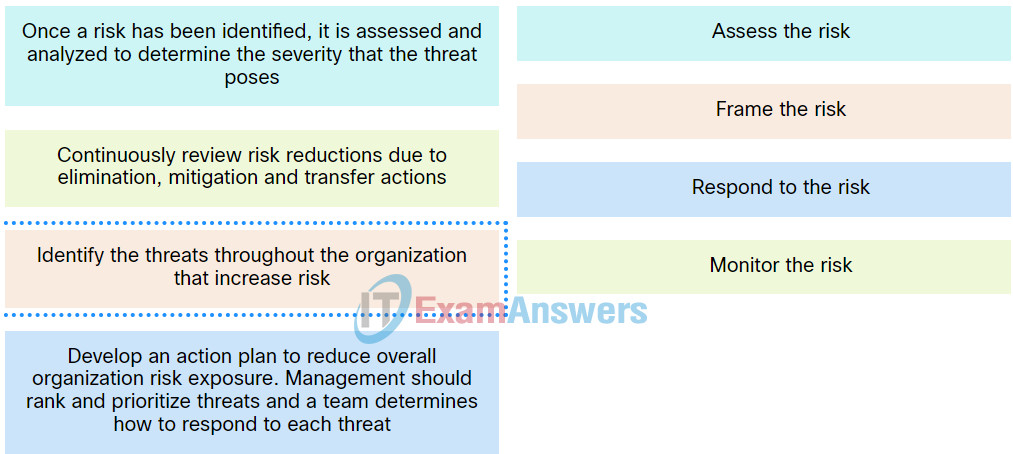
138. Match the stages in the risk management process to the description:
139. A company manages sensitive customer data and currently uses username and passphrase authentication. They want to mitigate the risk of employee credential compromise. What should they do?
- Purchase an insurance policy
- Enhance data encryption with an advanced algorithm
- Implement multi-factor authentication
- Install fingerprint or retinal scanners
140. As a cybersecurity analyst, which organization maintains the weekly digest called NewsBites?
- MITRE
- CIS
- (ISC)2
- SANS
141. Match the threat intelligence service with the description.
| FireEye | blocks attacks across the web and email threat vectors, and latent malware that resides on file shares |
| Cisco Talos | collects information about active, existing, and emerging threats and provides comprehensive protection against these attacks to subscribers |
| MITRE Corporation | creates and maintains a catalog of known security threats called Common Vulnerabilities and Exposures (CVE) |
| DHS Automated Indicator Sharing | provides a real-time exchange of cyber threat indicators between the U.S. Government and the private sector |
142. Which four metrics are key considerations in a Business Impact Analysis (BIA)?
- Recovery point times (RPTs)
- Recovery point objectives (RPOs)
- Mean time to repair (MTTR)
- Recovery time objectives (RTOs)
- Mean time between failures (MTBF)
- Mean time between objectives (RBOs)
143. An audit revealed weak passwords, stolen credentials, and phishing attacks. What single measure can mitigate all these risks?
- Institute a password reset for all accounts
- Change the minimum password length rules
- Change password complexity rules
- Implement MFA
144. An IT cybersecurity technician wants to conduct a layer-3 port scan and use decoy hosts on the same LAN to mask the scan source. Which tool should be used?
- Tripwire
- SIEM
- Nmap
- Superscan
145. Why is it important to conduct server profiling on live networks?
- Ensure all servers have the same configurations
- Establish a security baseline for a given server
- Create a traffic profile to identify data-loss potential
- Detect attacks using Big Data analytics
- Detect worm activity
146. Which type of cyber threat could cause electrical power outages?
- Sabotage
- Hardware failure
- Utility interruption
- Human error
147. A threat actor uses a Smurf attack to overwhelm a target host. What type of threat is this?
- TCP SYN flood attack
- MAC address spoofing attack
- Amplification and reflection attack
- UDP flood attack
148. Which statement describes a characteristic of WLANs?
- IEEE 802.11 prescribes CSMA/CD for collision avoidance
- The 5 GHz band is more prone to interference than 2.4 GHz
- Tethering is a variation of infrastructure mode
- An attacker may not have to physically enter the workplace to gain access to a WLAN
149. What cybersecurity mitigation phase involves limiting the spread of a worm infection to areas of the network that are already affected?
- inoculation
- quarantine
- containment
- treatment
150. Which is a Windows 10 feature that encrypts removable drives?
- Leafpad
- BitLocker To Go
- XProtect
- MRT
151. Which security strategy applies the terms layering, limiting, and obscurity?
- defense-in-depth
- physical security
- traffic filtering
- data encryption
152. What is a significant factor in the high vulnerability of industrial and embedded systems?
- These systems often have numerous points of administrative access.
- Many devices in these systems have poor authentication and cannot be upgraded or patched.
- Improving the security of these often low-cost systems would increase the cost excessively.
- Many of these systems have deployed, which means that implementing security is expensive and time-consuming.
153. What is a feature of a Zero Trust approach to network security?
- A user must re-authenticate even if they have successfully passed access control.
- Zone-based Policy Firewalls manage all network traffic.
- Defense-in-depth policies apply to identifying assets, threats, and vulnerabilities.
- A hashing algorithm applies to all network traffic.
154 What is used by an application layer gateway to connect to remote servers on behalf of clients?
- stateful firewall
- intrusion detection system
- proxy server
- packet filter
155. What actions are employed when configuring an IOS ZPF (Zone-Based Policy Firewall) for network traffic?
- policy-map
- zone pair
- class-map
- inspect action
156. How can three algorithms in the SSL/TLS cipher suite be updated if cryptanalysis reveals flaws? (Choose three.)
- encryption algorithm
- AAA algorithm
- authentication algorithm
- key exchange algorithm
- Certificate Authority algorithm
- hashing algorithm
157. What is an example of transaction data recorded by a network security monitoring tool?
- source and destination IP addresses of two network endpoints
- source and destination port numbers of two network endpoints
- the IP code for the protocol in use
- requests and replies between the two network endpoints
158. Why could network Syslog servers be a target for threat actors?
- Syslog servers could contain information that could lead to the detection of an exploit by a hacker.
- Syslog servers contain configurations and passwords for all devices on the network.
- Syslog data could be encrypted by the attacker and used as ransomware.
- Syslog servers are usually not installed behind a firewall.
159. What is the reason for disabling SSID broadcasting and changing the default SSID on a wireless access point?
- Anyone with the default SSID can gain access to the access point and change the configuration.
- Wireless clients must then have the SSID manually configured to connect to the wireless network.
- The access point stops broadcasting its own MAC address, thus preventing unauthorized wireless clients from connecting to the network.
- Disabling SSID broadcasting frees up radio frequency bandwidth and increases the data throughput of the access point.
160. Refer to the exhibit. A router has an existing ACL that permits all traffic from the 172.16.0.0 network. The administrator attempts to add a new ACE to the ACL that denies packets from host 172.16.0.1 and receives the error message that is shown in the exhibit. What action can the administrator take to block packets from host 172.16.0.1 while still permitting all other traffic from the 172.16.0.0 network?
Router(config)# access-list 1 deny 172.16.0.1
% Access rule can't be configured at higher sequence num
as it is part of the existing rule at sequence num 10
Router(config)# exit
Router# show access-lists 1
Standard IP access list 1
10 permit 172.16.0.0, wildcard bits 0.0.255.255- Add a deny any any ACE to access-list 1.
- Create a second access list denying the host and apply it to the same interface.
- Manually add the new deny ACE with a sequence number of 15.
- Manually add the new deny ACE with a sequence number of 5.
161. To facilitate the troubleshooting process, which inbound ICMP message should be permitted on an outside interface?
- Echo request
- Router advertisement
- Time-stamp reply
- Time-stamp request
- Echo reply
162. What does a rootkit modify?
- Programs
- Operating system
- Notepad
- Microsoft Word
- Screen savers
163. What are two types of attacks used on DNS open resolvers? (Choose two.)
- Fast flux
- Amplification and reflection
- Cushioning
- Resource utilization
- ARP poisoning
164. Which method can be used to harden a device?
- Allow default services to remain enabled
- Maintain use of the same passwords
- Allow USB auto-detection
- Use SSH and disable the root account access over SSH
165. What is the purpose of mobile device management (MDM) software?
- It is used to implement security policies, setting, and software configurations on mobile devices.
- It is used by threat actors to penetrate the system.
- It is used to identify potential mobile device vulnerabilities.
- It is used to create a security policy.
166. Which statement describes the anomaly-based intrusion detection approach?
- It compares the signatures of incoming traffic to a known intrusion database.
- It compares the behavior of a host to an established baseline to identify potential intrusions.
- It compares the antivirus definition file to a cloud-based repository for the latest updates.
- It compares the operations of a host against a well-defined security policy.
167. Which step in the Vulnerability Management Life Cycle performs inventory of all assets across the network and identifies host details, including operating system and open services?
- Remediate
- Assess
- Prioritize assets
- Discover
168. What are three benefits of using symbolic links over hard links in Linux? (Choose three.)
- They can show the location of the original file.
- They can be encrypted.
- Symbolic links can be exported.
- They can link to a file in a different file system.
- They can be compressed.
- They can link to a directory.
169. Match the security service with the description.

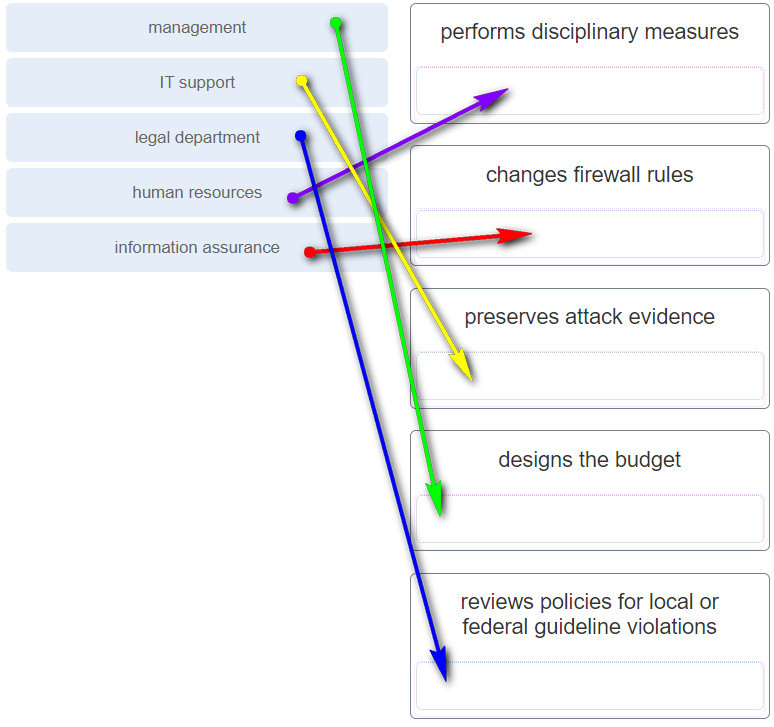
170. Match the security incident stakeholder with the role.
171. Which type of evidence cannot prove an IT security fact on its own?
- best
- corroborative
- hearsay
- indirect
172. A company implements a security policy that ensures that a file sent from the headquarters office to the branch office can only be opened with a predetermined code. This code is changed every day. Which two algorithms can be used to achieve this task? (Choose two.)
- AES
- SHA-1
- MD5
- HMAC
- 3DES
173. What is the first step taken in risk assessment?
- Compare to any ongoing risk assessment as a means of evaluating risk management effectiveness.
- Establish a baseline to indicate risk before security controls are implemented.
- Perform audits to verify threats are eliminated.
- Identify threats and vulnerabilities and the matching of threats with vulnerabilities.
174. Which Windows log contains information about installations of software, including Windows updates?
- system logs
- security logs
- application logs
- setup logs
175. What is the function of the pass action on a Cisco IOS Zone-Based Policy Firewall?
- logging of rejected or dropped packets
- inspecting traffic between zones for traffic control
- tracking the state of connections between zones
- forwarding traffic from one zone to another
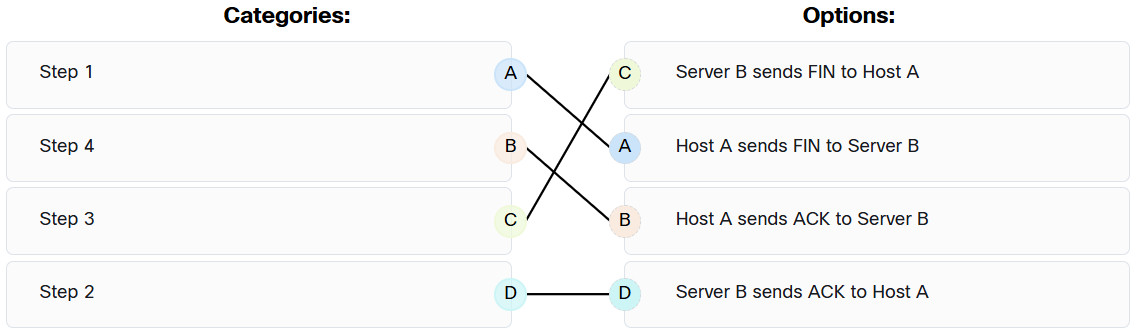
176. After host A receives a web page from server B, host A terminates the connection with server B. Match each option to its correct step in the normal termination process for a TCP connection.
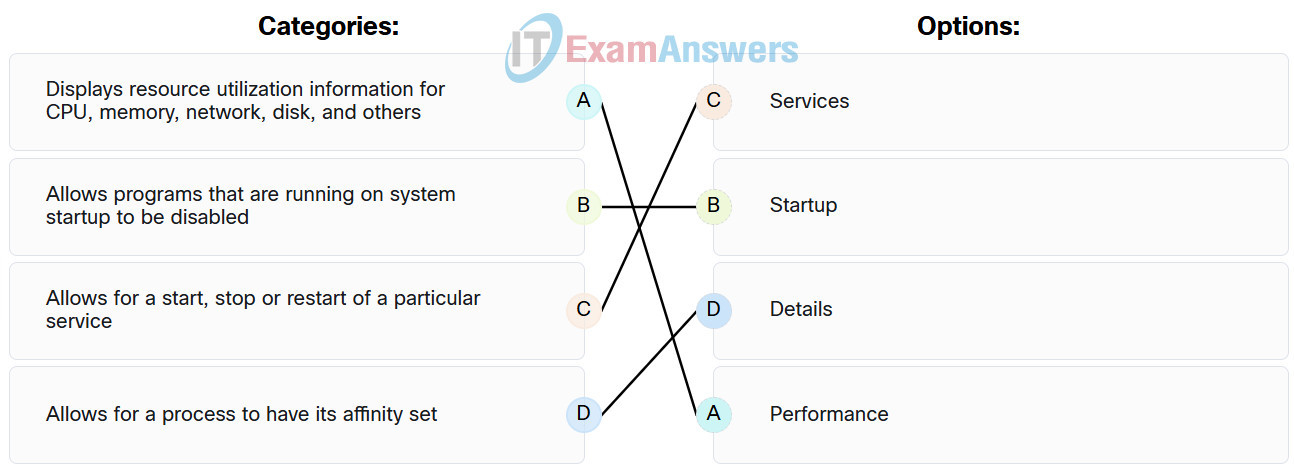
177. Match the tabs of the Windows 10 Task Manager to their functions.
178. What is a feature of virtual LANs (VLANs)?
- A single collision domain is enabled on a switch that is shared between VLANs.
- Switch port utilization is decreased because each port is only associated with one broadcast domain.
- Communication between different VLANs on the one switch is enabled by default.
- Logical segmentation is provided by creating multiple broadcast domains on a single switch.
179. What three security tools does Cisco Talos maintain security incident detection rule sets for? (Choose three.)
- NetStumbler
- Snort
- ClamAV
- SpamCop
- Socat
180. A network administrator is reviewing server alerts because of reports of network slowness. The administrator confirms that an alert was an actual security incident. What is the security alert classification of this type of scenario?
- true negative
- true positive
- false positive
- false negative
181. What is an attack vector as it relates to network security?
- a defense-in-depth approach to security
- a path by which a threat actor can gain access to an internal network device
- a particular section of a network design where security is applied
- a method of reverse engineering binary files
182. When implementing a ZPF, what is the default security setting when forwarding traffic between two interfaces in the same zone?
- Traffic between interfaces in the same zone is not subject to any policy and passes freely.
- Traffic between interfaces in the same zone is selectively forwarded based on Layer 3 information.
- Traffic between interfaces in the same zone is blocked.
- Traffic between interfaces in the same zone is selectively forwarded based on the default policy restrictions.
183. A company is deploying a customer service web application on AWS. A network administrator is installing and configuring a VM instance. Which three actions should the administrator take to protect the VM? (Choose three.)
- Install an IPS appliance in the VM.
- Enforce account management policies.
- Plan subnet placement.
- Configure RAID to ensure storage fault tolerance.
- Deploy an advanced firewall appliance.
- Disable unneeded ports and services.
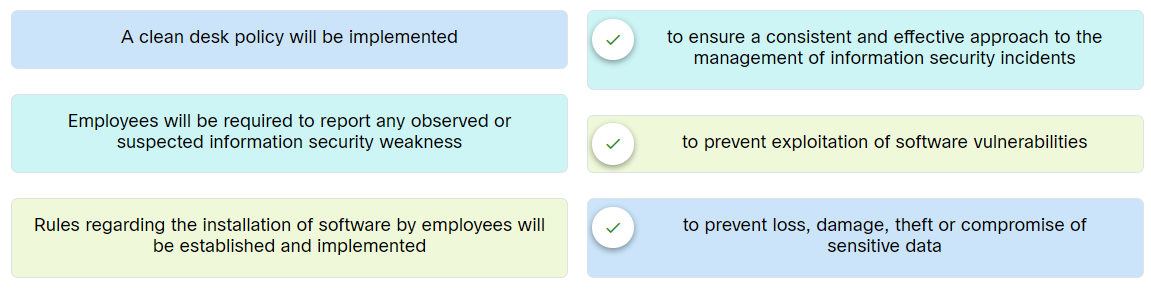
184. A company is preparing for an ISMS audit. Match the right control for each control objective.
185. An organization is developing a data governance program that follows regulations and policies. Which role in the program is responsible for ensuring compliance with policies and procedures, assigning the proper classification to information assets, and determining the criteria for accessing information assets?
- data custodian
- data owner
- data protection officer
- data controller
186. A cybersecurity analyst is testing a new vulnerability scanner on a system. The analyst chooses to run an intrusive credentialed scan. A few moments later, the system that was running the scan crashed. What is the most probable cause of the crash?
- a false positive
- a hardware failure
- a false negative
- the intrusive scan
187. An IT cybersecurity technician wants to conduct a layer three port scanning on the network systems but wishes to use decoy hosts on the same LAN as target hosts to mask the source of the scan. What security tool functions allow the technician to do this?
- Tripwire
- SIEM
- Superscan
- Nmap
188. Which file system is for Mac OS X computers, and Windows users may use third-party software to open and save files from this file system?
- EXT
- NTFS
- HFS+
- exFAT
189. What is the need for data integrity in forums and personal pages on social media?
- high
- critical
- low
- mid
190. Why can ACLs give a false sense of security if overly relied upon as a network security technology?
- ACLs can be applied to network interfaces in one direction only.
- Packets are permitted by default when ACL statements don’t match.
- ACLs only log denied traffic, not permitted traffic.
- Attackers can determine which IP addresses, protocols, and ports are allowed by ACLs.
192. What is required in order to connect a Wi-Fi enabled laptop to a WPA secured wireless network?
- a security encryption key
- a username and password
- an updated wireless driver
- a MAC address
193. Place the steps for configuring zone-based policy (ZPF) firewalls in order from first to last.
| 1st | Create zones. |
| 2nd | Create policies. |
| 3rd | Apply policies. |
| 4th | Assign zones to interfaces. |
| 5th |
194. Which two options can limit the information discovered from port scanning? (Choose two.)
- firewall
- intrusion prevention system
- authentication
- encryption
- passwords
195. What type of security test uses simulated attacks to determine possible consequences of a real threat?
- penetration testing
- vulnerability scanning
- integrity checking
- network scanning
196. What are two tasks that can be accomplished with the Nmap and Zenmap network tools? (Choose two.)
- password recovery
- password auditing
- validation of IT system configuration
- TCP and UDP port scanning
- identification of Layer 3 protocol support on hosts
197. A new PC is taken out of the box, started up and connected to the Internet. Patches were downloaded and installed. Antivirus was updated. In order to further harden the operating system what can be done?
- Give the computer a nonroutable address.
- Install a hardware firewall.
- Turn off the firewall.
- Remove unnecessary programs and services.
- Remove the administrator account.
- Disconnect the computer from the network.
198. What are two methods to maintain certificate revocation status? (Choose two.)
- CRL
- OCSP
- LDAP
- subordinate CA
- DNS
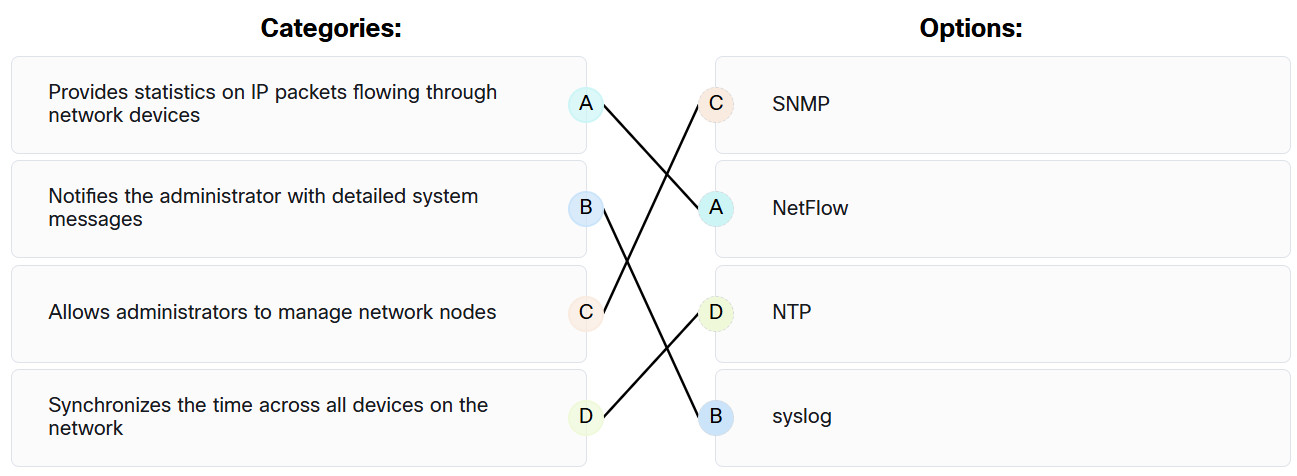
199. Match the network service with the description.
200. Which user can override file permissions on a Linux computer?
- only the creator of the file
- any user that has ‘group’ permission to the file
- any user that has ‘other’ permission to the file
- root user
201. Which two tools have a GUI interface and can be used to view and analyze full packet captures? (Choose two.)
- tcpdump
- nfdump
- Cisco Prime Network Analysis Module
- Splunk
- Wireshark
202. A threat actor has identified the potential vulnerability of the web server of an organization and is building an attack. What will the threat actor possibly do to build an attack weapon?
- Obtain an automated tool in order to deliver the malware payload through the vulnerability.
- Install a webshell on the web server for persistent access.
- Collect credentials of the web server developers and administrators.
- Create a point of persistence by adding services.
203. Which Windows tool can be used by a cybersecurity administrator to secure stand-alone computers that are not part of an active directory domain?
- Local Security Policy
- PowerShell
- Windows Firewall
- Windows Defender
204. Which two classes of metrics are included in the CVSS Base Metric Group? (Choose two.)
- Exploit Code Maturity
- Exploitability
- Confidentiality Requirement
- Modified Base
- Impact metrics
205. Which statement describes Cisco IOS Zone-Based Policy Firewall operation?
- Router management interfaces must be manually assigned to the self zone.
- Service policies are applied in interface configuration mode.
- A router interface can belong to multiple zones.
- The pass action works in only one direction.
206. Match the correct sequence of steps typically taken by a threat actor carrying out a domain shadowing attack.
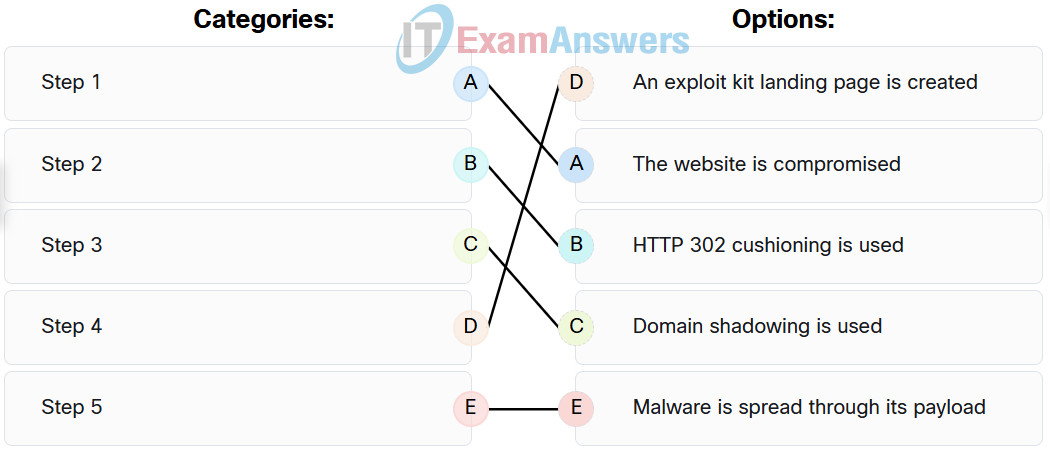
207. A flood of packets with invalid source IP addresses requests a connection on the network. The server busily tries to respond, resulting in valid requests being ignored. What type of attack has occurred?
- UDP flood
- TCP SYN flood
- TCP session hijacking
- TCP reset
208. In an attempt to prevent network attacks, cyber analysts share unique identifiable attributes of known attacks with colleagues. What three types of attributes or indicators of compromise are helpful to share? (Choose three.)
- netbios names of compromised firewalls
- IP addresses of attack servers
- features of malware files
- changes made to end system software
- BIOS of attacking systems
- system ID of compromised systems
209. When ACLs are configured to block IP address spoofing and DoS flood attacks, which ICMP message should be allowed both inbound and outbound?
- echo
- echo reply
- source quench
- unreachable
210. What does the telemetry function provide in host-based security software?
- It updates the heuristic antivirus signature database.
- It blocks the passage of zero-day attacks.
- It enables updates of malware signatures.
- It enables host-based security programs to have comprehensive logging functions.
211. A network administrator is trying to download a valid file from an internal server. However, the process triggers an alert on a NMS tool. What condition describes this alert?
- true positive
- false positive
- true negative
- false negative
212. What device would be used as the third line of defense in a defense-in-depth approach?
- firewall
- edge router
- host
- internal router
213. Which three security services are provided by digital signatures? (Choose three.)
- provides nonrepudiation using HMAC functions
- provides data encryption
- authenticates the destination
- guarantees data has not changed in transit
- provides confidentiality of digitally signed data
- authenticates the source
214. A company is using a public cloud provider to host its software development and distribution processes. What two cloud resources is the company solely responsible for in the shared security responsibility model? (Choose two.)
- application
- identity management
- data
- network control
- customer endpoints
215. What is the function of SDKs in application development?
- to prevent software from being reverse engineered by replacing sensitive data with fictional data
- to store precompiled SQL statements that execute tasks
- to verify software can run under required security settings
- to maintain data integrity and identify malicious input
- to provide a repository of code to reduce time and cost of application development
216. The manager of a new data center requisitions magnetic door locks. The locks will require employees to swipe an ID card to open. Which type of security control is being implemented?
- corrective
- compensative
- recovery
- preventive
217. Which security organization maintains a list of common vulnerabilities and exposures (CVE) and is used by prominent security organizations?
- SANS
- MITRE
- CIS
- SecurityNewsWire
218. As a Cybersecurity Analyst, it is very important to keep current. It was suggested by some colleagues that NewsBites contains many good current articles to read. What network security organization maintains this weekly digest?
- CIS
- SANS
- (ISC)2
- Mitre
219. Match the IT security governance role with its description.
| Data controller | A person who determines the purposes for which and how to process personal data. |
| Data custodian | A person who implements the classification and security controls for the data in accordance with the rules set out by the data owner. |
| Data protection officer | A person who oversees an organization’s data protection strategy. |
| Data processor | A person or organization processes personal data on behalf of the data controller. |
| Data steward | A person who ensures that data supports an organization’s business needs and meets regulatory requirements. |
| Data owner | A person who ensures compliance with policies and procedures assigns the proper classification to information assets and determines the criteria for accessing information assets. |
220. An organization has experienced several data breaches over the last five years. These data breaches have cost the organization financially and damaged its reputation. The organization has hired a cybersecurity penetration team to perform a full security audit on the entire organization. This independent contractor conducted the audit and found the following vulnerabilities:
- Several user accounts allowed unauthorized and escalated privileges.
- Systems and information without formal authorization.
What two steps can the organization take to mitigate these risks? (Choose two.)
- log when elevated privileges are used
- assign the least privilege to perform the given task
- adopt a no reuse of passwords on different applications policy
- terminate access and reset all passwords
221. Which device is the first line of defense in a defense-in-depth approach to network security?
- edge router
- internal router
- switch
- firewall
222. Refer to the exhibit. Which technology generated the event log?
Traffic Contribution: 8% (3/37)

Flow information:
IPv4 SOURCE ADDRESS:        10.1.1.2
IPv4 DESTINATION ADDRESS:   13.1.1.2
INTERFACE INPUT:            Se0/0/1
TRNS SOURCE PORT:           8974
TRNS DESTINATION PORT:      80
IP TOS:                     0x00
IP PROTOCOL:                6
FLOW SAMPLER ID:            0
FLOW DIRECTION:             Input
ipv4 source mask:           /0
ipv4 destination mask:      /8
counter bytes:              205
ipv4 next hop address:      13.1.1.2
tcp flags:                  0x1b
interface output:           Fa0/0
counter packets:            5
timestamp first:            00:09:12.596
timestamp last:             00:09:12.606
ip source as:               0
- Wireshark
- web proxy
- syslog
- Netflow
223. An investigator finds a USB drive at a crime scene and wants to present it as evidence in court. The investigator takes the USB drive and creates a forensic image of it and takes a hash of both the original USB device and the image that was created. What is the investigator attempting to prove about the USB drive when the evidence is submitted in court?
- The investigator found a USB drive and was able to make a copy of it.
- The data is all there.
- An exact copy cannot be made of a device.
- The data in the image is an exact copy and nothing has been altered by the process.
224. Match the security concept to the description.
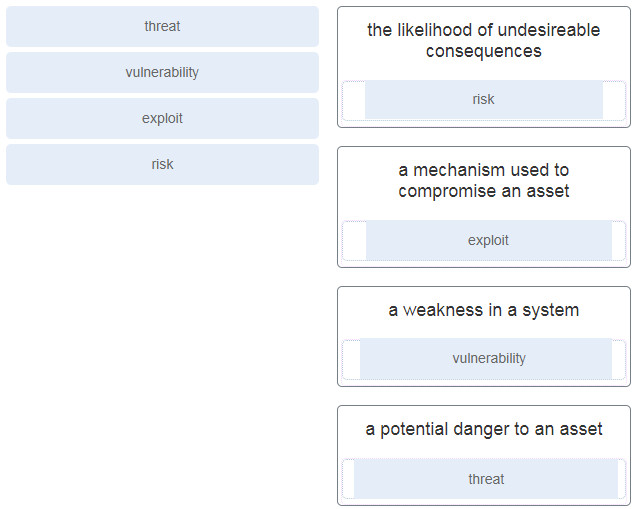
225. What is the principle behind the nondiscretionary access control model?
- It applies the strictest access control possible.
- It allows access decisions to be based on roles and responsibilities of a user within the organization.
- It allows users to control access to their data as owners of that data.
- It allows access based on attributes of the object be to accessed.
226. What is an example of a local exploit?
- Port scanning is used to determine if the Telnet service is running on a remote server.
- A threat actor performs a brute force attack on an enterprise edge router to gain illegal access.
- A buffer overflow attack is launched against an online shopping website and causes the server crash.
- A threat actor tries to gain the user password of a remote host by using a keyboard capture software installed on it by a Trojan.
227. Why would threat actors prefer to use a zero-day attack in the Cyber Kill Chain weaponization phase?
- to get a free malware package
- to launch a DoS attack toward the target
- to avoid detection by the target
- to gain faster delivery of the attack on the target
228. A network administrator is checking the system logs and notices unusual connectivity tests to multiple well-known ports on a server. What kind of potential network attack could this indicate?
- access
- information theft
- reconnaissance
- denial of service
229. In which configuration would an outbound ACL placement be preferred over an inbound ACL placement?
- when an outbound ACL is closer to the source of the traffic flow
- when a router has more than one ACL
- when an interface is filtered by an outbound ACL and the network attached to the interface is the source network being filtered within the ACL
- when the ACL is applied to an outbound interface to filter packets coming from multiple inbound interfaces before the packets exit the interface
230. Which statement describes a DNS stealth attack using threat actors' double IP flux technique?
- They use it in malware to randomly generate domain names that can then be used as rendezvous points to command and control servers.
- They hide phishing and malware delivery sites behind a quickly-changing network of compromised DNS hosts.
- They rapidly change the hostname to IP address mappings and to also change the authoritative name server to be difficult to identify the source of the attack.
- They gather domain account credentials to silently create multiple sub-domains to be used during the attacks.
231. Which ICMP message type should be stopped inbound?
- source quench
- unreachable
- echo
- echo-reply
232. A technician has installed a third party utility that is used to manage a Windows 7 computer. However, the utility does not automatically start whenever the computer is started. What can the technician do to resolve this problem?
- Set the application registry key value to one.
- Change the startup type for the utility to Automatic in Services.
- Uninstall the program and then choose Add New Programs in the Add or Remove Programs utility to install the application.
- Use the Add or Remove Programs utility to set program access and defaults.
233. The IT security personnel of an organization notice that the web server deployed in the DMZ is frequently targeted by threat actors. The decision is made to implement a patch management system to manage the server. Which risk management strategy method is being used to respond to the identified risk?
- risk reduction
- risk sharing
- risk retention
- risk avoidance
234. A cybersecurity analyst is going to verify security alerts using the Security Onion. Which tool should the analyst visit first?
- Sguil
- Bro
- ELK
- CapME
235. In what order are the steps in the vulnerability management life cycle conducted?
- discover, prioritize assets, assess, remediate, verify, report
- discover, prioritize assets, assess, remediate, report, verify
- discover, prioritize assets, assess, report, remediate, verify
- discover, assess, prioritize assets, report, remediate, verify
236. When implementing components into an enterprise network, what is the purpose of a firewall?
- A firewall is a system that inspects network traffic and makes forwarding decisions based solely on Layer 2 Ethernet MAC addresses.
- A firewall is a system that stores vast quantities of sensitive and business-critical information.
- A firewall is a system that is designed to secure, monitor, and manage mobile devices, including corporate-owned devices and employee-owned devices.
- A firewall is a system that enforces an access control policy between internal corporate networks and external networks.
237. Which type of firewall makes use of a proxy server to connect to remote servers on behalf of clients?
- stateful firewall
- application gateway firewall
- stateless firewall
- packet filtering firewall
238. A company is developing security policies. Which security policy would address the rules that determine access to and use of network resources and define the consequences of policy violations?
- acceptable use policy
- data policy
- password policy
- remote access policy
239. What key considerations does a business impact analysis (BIA) examine? (Choose four)
- Mean time between objectives (RBOs)
- Recovery point objectives (RPOs)
- Mean time between failures (MTBF)
- Mean time to repair (MTTR)
- Recovery time objectives (RTOs)
- Recovery point times (RPTs)
240. Match the command line tool with its function.

241. Why are honeypots positioned in the cloud?
- to have a faster solution to gather information
- to have easier access to the honeypots
- to isolate the honeypots from production networks
- to create DMZ zones within the cloud
242. Which statement describes the characteristics of intrusion detection and intrusion prevention systems?
- An IDS technology is a host-based approach, while IPS technology is a network-based approach.
- IDS technology has no impact on network, while IPS technology might impact network traffic.
- IDS can detect atomic patterns, while IPS can detect composite patterns.
- IDS and IPS sensors kill the malicious traffic and send it to a "Bit Bucket".
243. What is the function provided by the Burpsuite tool in Kali Linux?
- penetration test
- managing
- scanning
- logging
244. Which three aspects of an organization must cybersecurity analysts identify before developing a comprehensive security policy? (Choose three.)
- security budget
- the placement of firewalls
- potential threats
- system vulnerabilities
- the type of network data traffic
- organization assets
245. Which two security alert classifications do cybersecurity analysts prefer? (Choose two.)
- true positive
- true negative
- false positive
- false negative
246. A network security engineer is examining the Zone-based Policy Firewall configuration on a Cisco router and observes the following output:
policy-map type inspect PRIV-TO-PUB-POLICY
 class type inspect HTTP-TRAFFIC
  inspect
 class class-default
  drop
What is the purpose of the class class-default and drop commands in this configuration segment?
- It will apply default security policies to specified traffic class traffic members.
- It will cause all traffic that is not a member of the specified traffic class to be dropped.
- It ensures the logging of all traffic of the specified traffic class.
- It will apply stated-based traffic control to default traffic allowed to pass between specific zones.
247. How does the Diamond Model of intrusion analysis assist cybersecurity analysts?
- by illustrating the tactics, techniques, and procedures (TTP) as part of intrusion defense and attribution
- by illustrating how an adversary pivots from one intrusion event to the next
- by tracing the stages of an intrusion event from the early reconnaissance stages to the exfiltration of data
- by conveying the common attributes and severity of intrusion vulnerabilities in computer hardware and software systems
