16.5.1 Packet Tracer - Secure Network Devices Answers
Topology
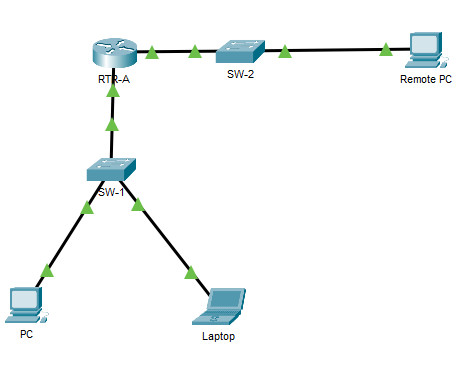
16.5.1 Packet Tracer - Secure Network Devices
Addressing Table
| Device | Interface | Address | Mask | Gateway |
|---|---|---|---|---|
| RTR-A | G0/0/0 | 192.168.1.1 | 255.255.255.0 | N/A |
| G0/0/1 | 192.168.2.1 | 255.255.255.0 | N/A | |
| SW-1 | SVI | 192.168.1.254 | 255.255.255.0 | 192.168.1.1 |
| PC | NIC | 192.168.1.2 | 255.255.255.0 | 192.168.1.1 |
| Laptop | NIC | 192.168.1.10 | 255.255.255.0 | 192.168.1.1 |
| Remote PC | NIC | 192.168.2.10 | 255.255.255.0 | 192.168.2.1 |
Requirements
Note: To keep this activity brief and easy to manage, some security configuration settings have not been made. In other cases, security best practices have not been followed.
In this activity you will configure a router and a switch based on a list of requirements.
Instructions
Step 1: Document the Network
Complete the addressing table with the missing information.
Step 2: Router configuration requirements:
- Prevent IOS from attempting to resolve mistyped commands to domain names.
Router(config)# no ip domain-lookup
- Hostnames that match the values in the addressing table.
Router(config)# hostname RTR-A
- Require that newly created passwords be at least 10 characters in length.
RTR-A(config)# security passwords min-length 10
- A strong ten-character password for the console line. Use @Cons1234!
RTR-A(config)# line console 0
RTR-A(config-line)# password @Cons1234!
RTR-A(config-line)# login
- Ensure that console and VTY sessions close after 7 minutes exactly.
RTR-A(config)# line console 0
RTR-A(config-line)# exec-timeout 7 0
RTR-A(config-line)# line vty 0 4
RTR-A(config-line)# exec-timeout 7 0
- A strong, encrypted ten-character password for the privileged EXEC mode. For this activity, it is permissible to use the same password as the console line.
RTR-A(config)# enable secret @Cons1234!
- A MOTD banner that warns about unauthorized access to the devices.
RTR-A(config)# banner motd #Unauthorized access prohibited.#
- Password encryption for all passwords.
RTR-A(config)# service password-encryption
- A user name of NETadmin with encrypted password LogAdmin!9.
RTR-A(config)# username NETadmin secret LogAdmin!9
- Enable SSH.
- Use security.com as the domain name.
- Use a modulus of 1024.
RTR-A(config)# ip domain-name security.com
RTR-A(config)# crypto key generate rsa general-keys modulus 1024
- The VTY lines should use SSH for incoming connections.
RTR-A(config)# line vty 0 4
RTR-A(config-line)# transport input ssh
- The VTY lines should use the username and password that were configured to authenticate logins.
RTR-A(config)# line vty 0 4
RTR-A(config-line)# login local
- Impede brute force login attempts by using a command that blocks login attempts for 45 seconds if someone fails three attempts within 100 seconds.
RTR-A(config)# login block-for 45 attempts 3 within 100
Step 3: Switch configuration requirements:
Switch(config)# hostname SW-1
- All unused switch ports are administratively down.
SW-1(config)# interface range fastethernet 0/1, fastethernet 0/3 - 9, fastethernet 0/11 - 24, gigabitethernet 0/2
SW-1(config-if-range)# shutdown
- The SW-1 default management interface should accept connections over the network. Use the information shown in the addressing table. The switch should be reachable from remote networks.
SW-1(config)# interface vlan 1
SW-1(config-if)# ip address 192.168.1.254 255.255.255.0
SW-1(config-if)# no shutdown
SW-1(config)# ip default-gateway 192.168.1.1
- Use @Cons1234! as the password for the privileged EXEC mode.
SW-1(config)# enable secret @Cons1234!
- Configure SSH as was done for the router.
SW-1(config)# ip domain-name security.com
SW-1(config)# crypto key generate rsa general-keys modulus 1024
- Create a user name of NETadmin with encrypted secret password LogAdmin!9
SW-1(config)# username NETadmin secret LogAdmin!9
- The VTY lines should only accept connections over SSH.
SW-1(config)# line vty 0 15
SW-1(config-line)# transport input ssh
- The VTY lines should only allow the network administrator account to access the switch management interface.
SW-1(config)# line vty 0 15
SW-1(config-line)# login local
- Hosts on both LANs should be able to ping the switch management interface.
C:\> ping 192.168.1.254
C:\> ping 192.168.1.254
Device Configs - Final
ROUTER RTR-A
! ==============================================================
!--- 16.5.1 Packet Tracer - Secure Network Devices
!--- ANSWER SCRIPT FOR ROUTER RTR-A
!--- Usage: copy this whole file and paste it into the RTR-A terminal (start at the Router> prompt). G0/0/0 and G0/0/1 are already addressed in the activity. Every line beginning with "!" is a comment; IOS ignores it.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Step 2: Router configuration requirements.
! --------------------------------------------------------------

!--- Prevent IOS from attempting to resolve mistyped commands to domain names.
no ip domain-lookup

!--- Hostname that matches the Addressing Table.
hostname RTR-A

!--- Require newly created passwords to be at least 10 characters (set this before the passwords below).
security passwords min-length 10

!--- Console line: strong ten-character password, require login, close idle sessions after exactly 7 minutes.
line console 0
 password @Cons1234!
 login
 exec-timeout 7 0
 exit

!--- Strong, encrypted ten-character password for privileged EXEC mode (same as the console password).
enable secret @Cons1234!

!--- MOTD banner that warns about unauthorized access.
banner motd #Unauthorized access prohibited.#

!--- Encrypt all plaintext passwords.
service password-encryption

!--- User NETadmin with an encrypted (secret) password.
username NETadmin secret LogAdmin!9

!--- Enable SSH: domain name security.com, then 1024-bit RSA keys (one line, no prompt).
ip domain-name security.com
crypto key generate rsa general-keys modulus 1024

!--- VTY lines: SSH only, log in with the local user, close idle sessions after exactly 7 minutes.
line vty 0 4
 transport input ssh
 login local
 exec-timeout 7 0
 exit

!--- Block logins for 45 seconds after 3 failed attempts within 100 seconds.
login block-for 45 attempts 3 within 100

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip ssh                  -> SSH Enabled, key size 1024
!---   show run | section line      -> console and vty 0 4: exec-timeout 7 0; vty: login local, transport input ssh
!---   show login                   -> 45-second block after 3 failures within 100 seconds
!---   From PC: ssh -l NETadmin 192.168.1.1 (password LogAdmin!9)
! ==============================================================
SWITCH SW-1
! ==============================================================
!--- 16.5.1 Packet Tracer - Secure Network Devices
!--- ANSWER SCRIPT FOR SWITCH SW-1
!--- Usage: copy this whole file and paste it into the SW-1 terminal (start at the Switch> prompt). Every line beginning with "!" is a comment; IOS ignores it.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Step 3: Switch configuration requirements.
! --------------------------------------------------------------

!--- Hostname that matches the Addressing Table.
hostname SW-1

!--- Shut down all unused ports. F0/2, F0/10 and G0/1 are in use (PC, Laptop, RTR-A).
interface range fastethernet 0/1, fastethernet 0/3 - 9, fastethernet 0/11 - 24, gigabitethernet 0/2
 shutdown
 exit

!--- Management SVI (VLAN 1) from the Addressing Table, enabled so the switch accepts connections over the network.
interface vlan 1
 ip address 192.168.1.254 255.255.255.0
 no shutdown
 exit

!--- Default gateway (RTR-A G0/0/0) so the switch is reachable from remote networks.
ip default-gateway 192.168.1.1

!--- Privileged EXEC password.
enable secret @Cons1234!

!--- Configure SSH as on the router: domain name security.com, then 1024-bit RSA keys (one line, no prompt).
ip domain-name security.com
crypto key generate rsa general-keys modulus 1024

!--- User NETadmin with an encrypted secret password.
username NETadmin secret LogAdmin!9

!--- All 16 VTY lines: SSH only, and only the local NETadmin account can log in.
line vty 0 15
 transport input ssh
 login local
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief  -> Vlan1 192.168.1.254 up/up; unused ports administratively down
!---   show ip ssh              -> SSH Enabled, key size 1024
!---   From PC and Remote PC: ping 192.168.1.254 -> replies (hosts on both LANs reach the switch)
! ==============================================================


