CCNA 2 v7 - SRWE Practice PT Skills Assessment (PTSA) - Part 2 Answers
[Updated on Sep 2021 – 100% Scored]
CCNAv7: Switching, Routing, and Wireless Essentials v7.0 (SRWE)
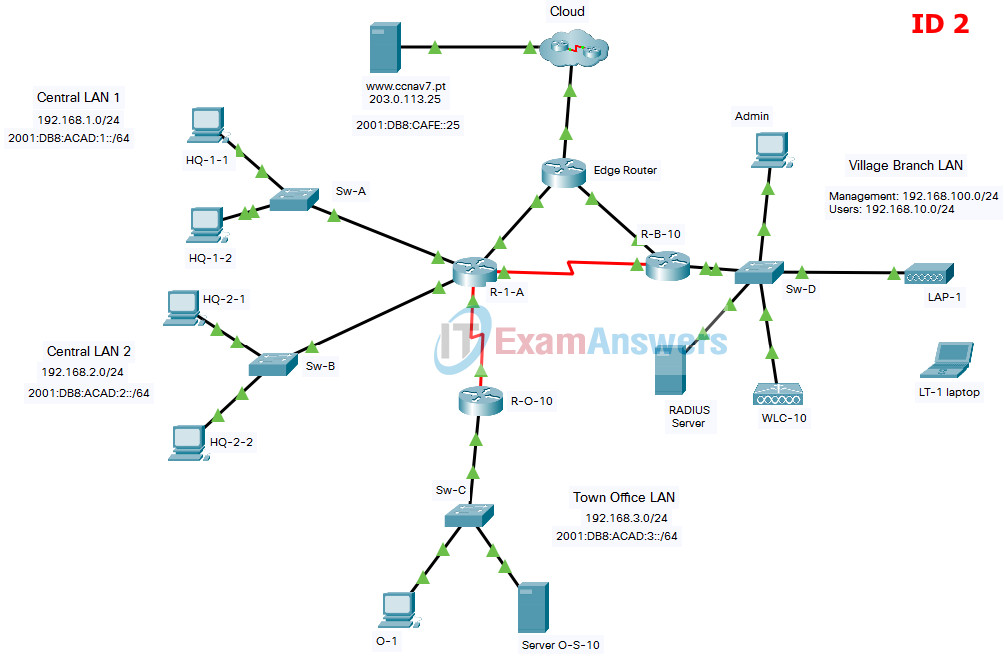
SRWE Practice PT Skills Assessment (PTSA) - Part 2 - ID 2
SRWE Practice Packet Tracer Assessment - Part 2
A few things to keep in mind while completing this activity:
- Do not use the browser Back button or close or reload any exam windows during the exam.
- Do not close Packet Tracer when you are done. It will close automatically.
- Click the Submit Assessment button in the browser window to submit your work.
Addressing Table
| Device | Interface | Address and Prefix |
|---|---|---|
| R-1-A | G0/0/0 | 192.168.1.1/24 |
| 2001:db8:acad:1::1/64 | ||
| fe80::1 | ||
| G0/0/1 | 192.168.2.1/24 | |
| 2001:db8:acad:2::1/64 | ||
| fe80::1 | ||
| G0/0/2 | 10.1.0.1/30 | |
| 2001:db8:acad:a::1/64 | ||
| fe80::2 | ||
| S0/1/0 | 10.2.0.1/30 | |
| 2001:db8:acad:b::1/64 | ||
| fe80::2 | ||
| S0/1/1 | 10.4.0.1/30 | |
| 2001:db8:acad:d::1/64 | ||
| R-O-10 | S0/1/1 | 10.4.0.2/30 |
| 2001:db8:acad:d::2/64 | ||
| fe80::2 | ||
| G0/0/0 | 192.168.3.1/24 | |
| 2001:db8:acad:3::1/64 | ||
| fe80::1 | ||
| R-B-10 | G0/0/0.10 | 192.168.10.1/24 |
| G0/0/0.100 | 192.168.100.1/24 | |
| G0/0/0.172 | 172.16.1.1/24 | |
| G0/0/1 | DHCP | |
| 2001:db8:acad:c::2/64 | ||
| S0/1/0 | 10.2.0.2/30 | |
| 2001:db8:acad:b::2/64 | ||
| Edge Router | G0/0/0 | 10.1.0.2/24 |
| 2001:DB8:ACAD:A::2/64 | ||
| G0/0/1 | 10.3.0.1/24 | |
| 2001:DB8:ACAD:C::1/64 | ||
| WLC-10 | management | 192.168.100.254 |
| WLAN 10 | 192.168.10.254/24 | |
| Server O-S-10 | NIC | 192.168.3.122 |
| 2001:db8:acad:3::122 | ||
| Website | NIC | 203.0.113.25 |
| 2001:db8:acad:cafe:25 | ||
| DNS Server | NIC | 198.51.100.163 |
| 2001:DB8:face::163 | ||
| Management Host (Admin PC) | NIC | 192.168.100.23 |
| Wireless Host | NIC | DHCP |
| RADIUS server | NIC | 172.16.1.100/24 |
| HQ-1-1 | NIC | 192.168.1.10/24 |
| 2001:db8:acad:1::10/64 | ||
| HQ-1-2 | NIC | 192.168.1.11/24 |
| 2001:db8:acad:1::11/64 | ||
| HQ-2-1 | NIC | 192.168.2.20/24 |
| 2001:db8:acad:2::20/64 | ||
| HQ-2-2 | NIC | 192.168.2.21/24 |
| 2001:db8:acad:2::21/64 | ||
| O-1 | NIC | 192.168.3.30/24 |
| 2001:db8:acad:3::30/64 |
Objectives
In this assessment, you will configure the following:
- Floating static and default routes in IPv4 and IPv6.
- Host routes in IPv4 and IPv6.
- DHCP pools and scopes.
- Switch security including port security.
- Enhanced LAN security with DHCP snooping, dynamic ARP inspection, PortFast, and BPDU guard.
- Wireless LAN Controller-based wireless LAN with enterprise authentication.
You will only configure the R-1-A and R-B-10 routers, the Sw-A switch, and the WLC-10 wireless LAN controller. Access to other devices is not available.
Background / Scenario
Cisco Demo LLC is reworking their network. You have been asked to prototype the network in Packet Tracer for evaluation by senior network staff.
Instructions
Part 1: Configure Switch Security
In this part of the assessment you will configure switch Sw-A with switch security features. Switch ports FastEthernet0/1 to FastEthernet0/5 are the active switch ports. Port GigabitEthernet0/1 is a dedicated link to router R-1-A. All other ports should be secured.
Step 1: Configure VLANs
a. Configure VLAN 10 with name users.
Sw-A(config)# vlan 10
Sw-A(config-vlan)# name users
b. Configure VLAN 999 with the name unused.
Sw-A(config-vlan)# vlan 999
Sw-A(config-vlan)# name unused
Step 2: Configure active switch ports.
On the active switch ports configure the following:
a. Configure FastEthernet 0/1 through 0/5 and GigabitEthernet 0/1 as static access ports in VLAN 10.
Sw-A(config)# interface range fastethernet 0/1 - 5, gigabitethernet 0/1
Sw-A(config-if-range)# switchport mode access
Sw-A(config-if-range)# switchport access vlan 10
b. Activate port security on the ports.
Sw-A(config)# interface range fastethernet 0/1 - 5
Sw-A(config-if-range)# switchport port-security
- Configure the active ports to accept a maximum of 4 MAC addresses.
Sw-A(config-if-range)# switchport port-security maximum 4
- If a violation occurs, configure the ports to drop frames from the unauthorized MAC address, log it, and send an alert.
Sw-A(config-if-range)# switchport port-security violation restrict
- MAC addresses should be present in the MAC address table for a maximum of 10 minutes before they are removed.
Sw-A(config-if-range)# switchport port-security aging time 10
- Ports should add the learned MAC addresses to the running configuration.
Sw-A(config-if-range)# switchport port-security mac-address sticky
- Configure the MAC address of HQ-1-1 as a static address on port FastEthernet0/1.
Sw-A(config)# interface fastethernet 0/1
Sw-A(config-if)# switchport port-security mac-address 00D0.D3DC.2825
c. Protect against DHCP snooping.
Note: In this simulated network, DHCP snooping may not operate correctly in Packet Tracer. Configure it as you would normally. You will receive full credit for a configuration that meets the requirements below.
- Activate DHCP snooping globally.
Sw-A(config)# ip dhcp snooping
- Activate DHCP snooping for the two VLANs that you configured.
Sw-A(config)# ip dhcp snooping vlan 10,999
- Configure the ports to limit the rate to 5 DHCP packets per second.
Sw-A(config)# interface range fastethernet 0/1 - 5, gigabitethernet 0/1
Sw-A(config-if-range)# ip dhcp snooping limit rate 5
- Configure the port that links to the router as trusted.
Sw-A(config)# interface gigabitethernet 0/1
Sw-A(config-if)# ip dhcp snooping trust
d. Guard against ARP attacks by implementing DAI.
- Activate DAI globally.
- Activate DAI on the two VLANs.
Sw-A(config)# ip arp inspection vlan 10,999
- Configure the port that links to the router as trusted.
Sw-A(config)# interface gigabitethernet 0/1
Sw-A(config-if)# ip arp inspection trust
e. Mitigate STP attacks by configuring BPDUguard and PortFast on the active ports.
Sw-A(config)# interface range fastethernet 0/1 - 5
Sw-A(config-if-range)# spanning-tree portfast
Sw-A(config-if-range)# spanning-tree bpduguard enable
Step 3: Secure unused switch ports.
a. Move all unused switch ports to VLAN 999.
Sw-A(config)# interface range fastethernet 0/6 - 24, gigabitethernet 0/2
Sw-A(config-if-range)# switchport access vlan 999
b. Configure all unused switch ports as static access ports.
Sw-A(config-if-range)# switchport mode access
c. Deactivate all unused switch ports.
Sw-A(config-if-range)# shutdown
Part 2: Configure Addressing and DHCP
You will configure DHCP and interface addressing on router R-B-10 to prepare for implementing the wireless LAN controller network.
Step 1: Configure and address a subinterface for the WLAN user network.
a. Configure subinterface 10 on the router interface that is connected to the switch Sw-D.
R-B-10(config)# interface gigabitethernet 0/0/0.10
R-B-10(config-subif)# description Gateway for VLAN 10 (WLAN users)
b. The router should provide router-on-a-stick routing to VLAN 10.
R-B-10(config-subif)# encapsulation dot1q 10
c. Configure the subinterface with the address from the Addressing Table.
R-B-10(config-subif)# ip address 192.168.10.1 255.255.255.0
Step 2: Configure a DHCP pool for WLAN user network.
a. Exclude the router interface address and the management address of the WLC.
R-B-10(config)# ip dhcp excluded-address 192.168.10.1
R-B-10(config)# ip dhcp excluded-address 192.168.10.254
b. Configure a DHCP pool that will be used by hosts that are connecting to the WLAN.
- Name the pool WLAN-hosts.
R-B-10(config)# ip dhcp pool WLAN-hosts
- Configure the pool to use addresses in the 192.168.10.0/24 network.
R-B-10(dhcp-config)# network 192.168.10.0 255.255.255.0
- The pool should also provide the default gateway and DNS server addresses.
R-B-10(dhcp-config)# default-router 192.168.10.1
R-B-10(dhcp-config)# dns-server 198.51.100.163
Step 3: Configure an interface as a DHCP client.
On R-B-10, configure the interface that is connected to Edge Router to receive its address over DHCP.
R-B-10(config)# interface gigabitethernet 0/0/1
R-B-10(config-if)# ip address dhcp
Part 3: Configure Static Routes
In this part of the assessment you will configure static, default, floating static, and host routes in both IPv4 and IPv6. You will configure the R-1-A and R-B-10 routers. Cisco Demo LLC has decided that it wants to use static routing between all its networks. In addition, the company wants to use the Ethernet links between routers for most data traffic and reserve serial link between R-1-A and R-B-10 for backup purposes in case one of the Ethernet links becomes unavailable. You will be configuring floating static and default routes.
Step 1: Configure static routes on R-1-A.
a. Configure IPv4 default routes to the cloud using the Ethernet link as the preferred link and the serial link as the floating backup. Use an administrative distance of 10 for the backup route. These routes should be configured as directly connected routes.
Note: Ethernet interfaces will give a warning when configured without a next-hop address. In this configuration, the interface is point-to-point, so the warning can be ignored.
R-1-A(config)# ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/2
R-1-A(config)# ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10
b. Ensure that the device is configured to route IPv6.
R-1-A(config)# ipv6 unicast-routing
c. Configure IPv6 default routes to the cloud. Use the Ethernet link as the primary route, and the serial link as the floating backup. Use an administrative distance of 10 for the backup route. These routes should specify the next hop interface address.
R-1-A(config)# ipv6 route ::/0 2001:db8:acad:a::2
R-1-A(config)# ipv6 route ::/0 2001:db8:acad:b::2 10
d. Configure IPv4 static routes to the Village Branch LAN WLAN user network following the same guidelines as above for type of route and administrative distance.
R-1-A(config)# ip route 192.168.10.0 255.255.255.0 GigabitEthernet0/0/2
R-1-A(config)# ip route 192.168.10.0 255.255.255.0 Serial0/1/0 10
e. Configure IPv4 and IPv6 host routes on R-1-A to the Server O-S-10 on the Town Office LAN. Create a directly connected route for IPv4 and a next-hop route for IPv6.
R-1-A(config)# ip route 192.168.3.122 255.255.255.255 Serial0/1/1
R-1-A(config)# ipv6 route 2001:db8:acad:3::122/128 2001:db8:acad:d::2
Step 2: Configure static routes on R-B-10.
R-B-10 must also be configured with static routes to the other three networks in the Cisco Demo LLC network. It will require floating static and default routes in IPv4 and IPv6 following the same guidelines as were used for the R-1-A static routes.
- IPv6 routes use next-hop address arguments.
- IPv4 routes use exit interface arguments.
- All routes should prefer the Ethernet links over the serial link.
- Backup floating routes use an administrative distance of 10.
a. Configure IPv4 default routes to the cloud using the Ethernet link as the preferred link and the serial link as the backup.
R-B-10(config)# ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/1
R-B-10(config)# ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10
b. Ensure that the device is configured to route IPv6.
R-B-10(config)# ipv6 unicast-routing
c. Configure IPv6 default routes to the cloud. Use the Ethernet link as the primary route, and the serial link as backup. Use an administrative distance of 10 for the backup route. These routes should specify the next hop interface address.
R-B-10(config)# ipv6 route ::/0 2001:db8:acad:c::1
R-B-10(config)# ipv6 route ::/0 2001:db8:acad:b::1 10
Part 4: Configure a Wireless LAN using a Wireless LAN Controller
In this part of the assessment, you will configure the wireless LAN controller to provide wireless access to the network. Username and password are the default admin/admin. Connect to the WLC over HTTPS to the management interface.
Click Management Host (Admin PC), open the Desktop tab, then Web Browser, and go to the WLC management address over HTTPS: https://192.168.100.254
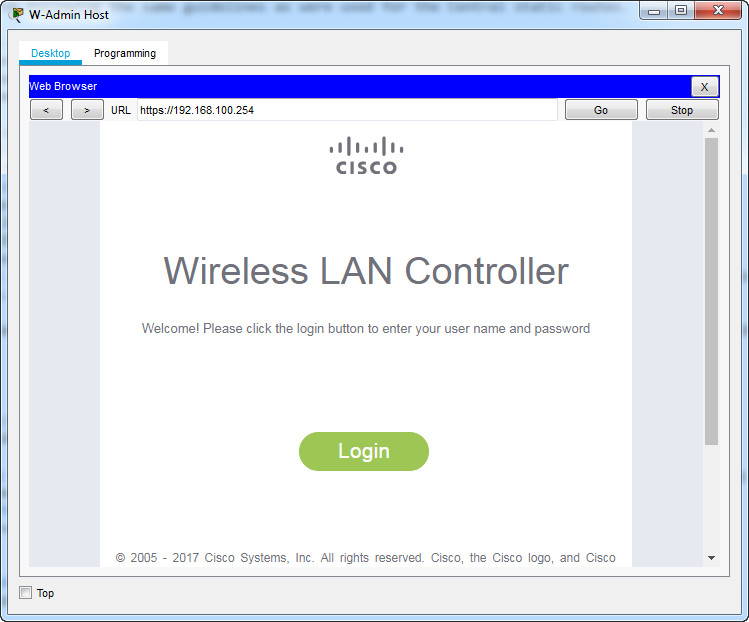
Log in with the username admin and the password admin.
Step 1: Configure a VLAN interface.
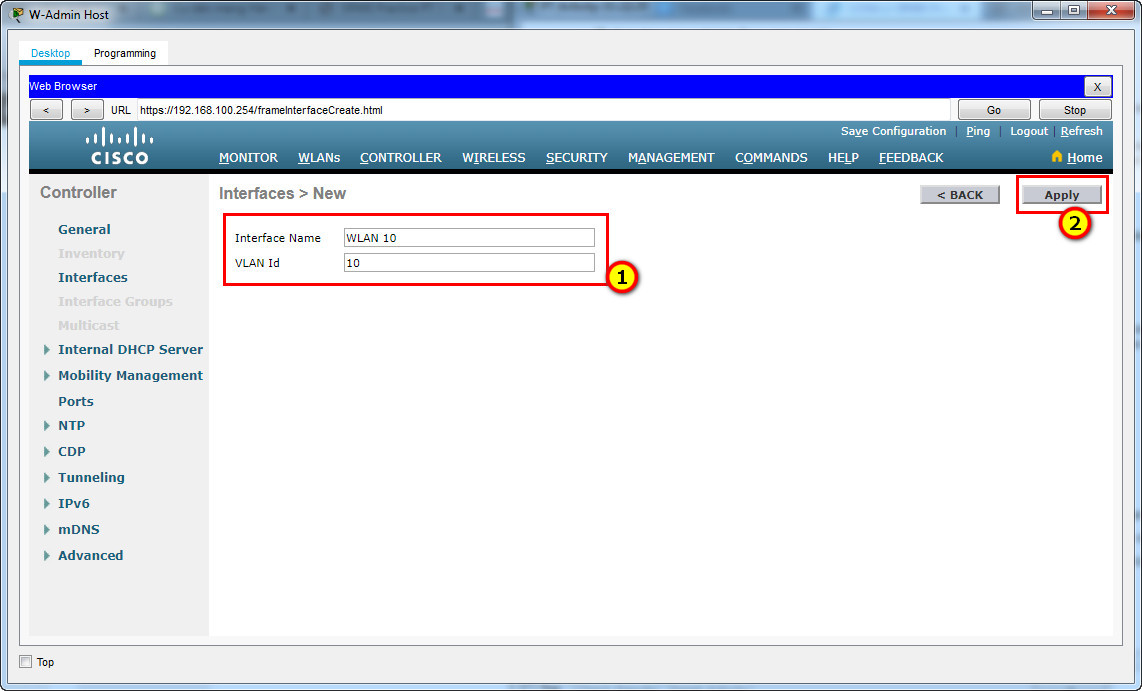
a. Create a new interface and name it WLAN 10. The interface should use VLAN 10 and physical port 1.
Go to CONTROLLER > Interfaces and click New....
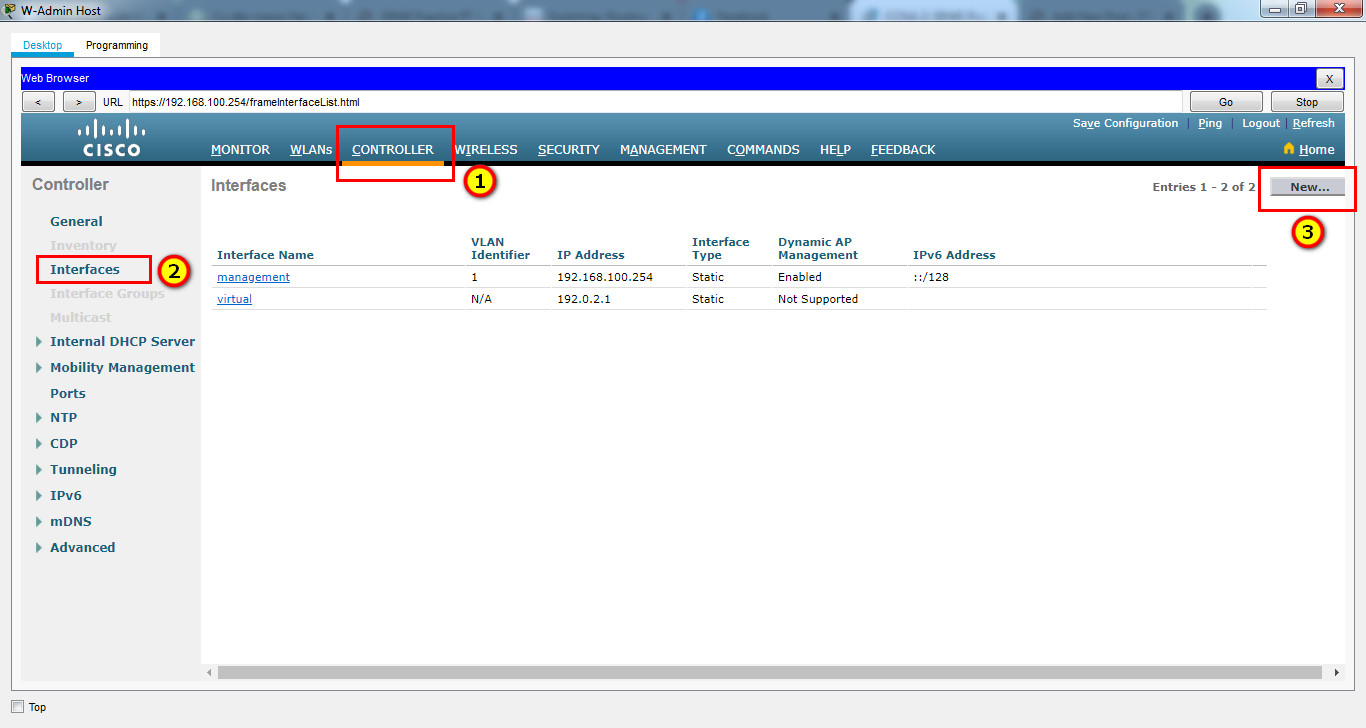
On the Interfaces > New page, enter WLAN 10 in the Interface Name box and 10 in the VLAN Id box, then click Apply.
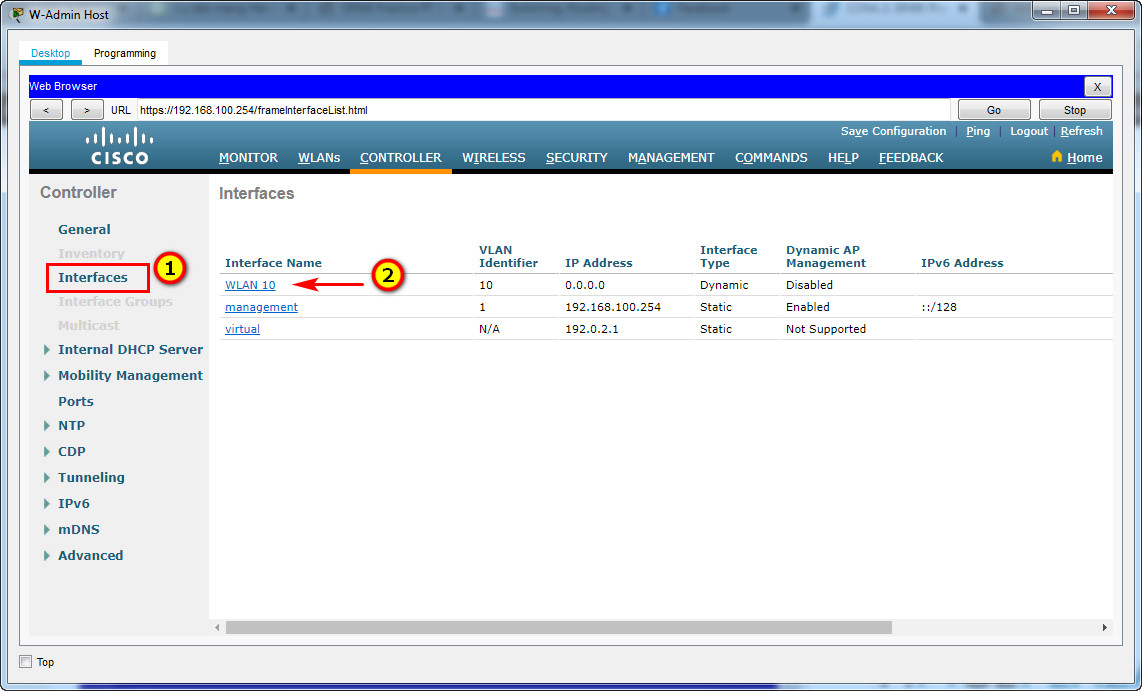
b. Use the information in the addressing table to configure the addressing settings for the interface. The interface will be using a DHCP pool that is configured on the subinterface that is assigned to VLAN 10 on router R-B-10.
Go back to CONTROLLER > Interfaces and click the WLAN 10 interface you just created.
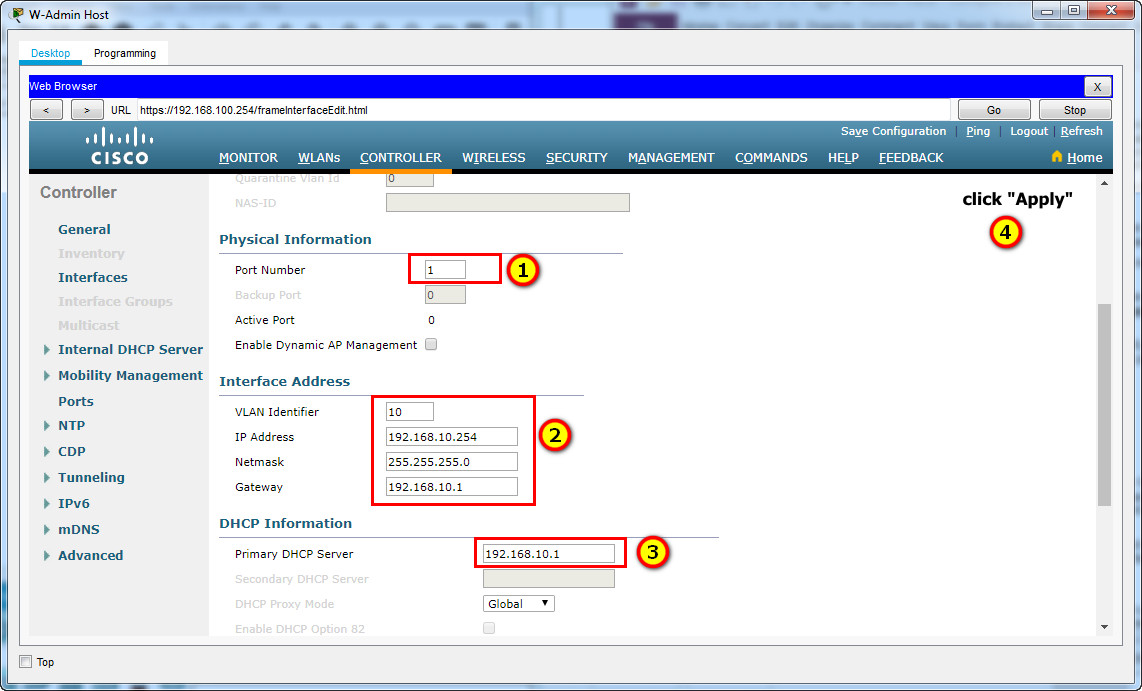
Enter the values from the table below in the matching fields, then click Apply.
| Setting | Value |
|---|---|
| Port Number | 1 |
| VLAN Identifier | 10 |
| IP Address | 192.168.10.254 |
| Netmask | 255.255.255.0 |
| Gateway | 192.168.10.1 |
| Primary DHCP Server | 192.168.10.1 |
Step 2: Configure a RADIUS server.
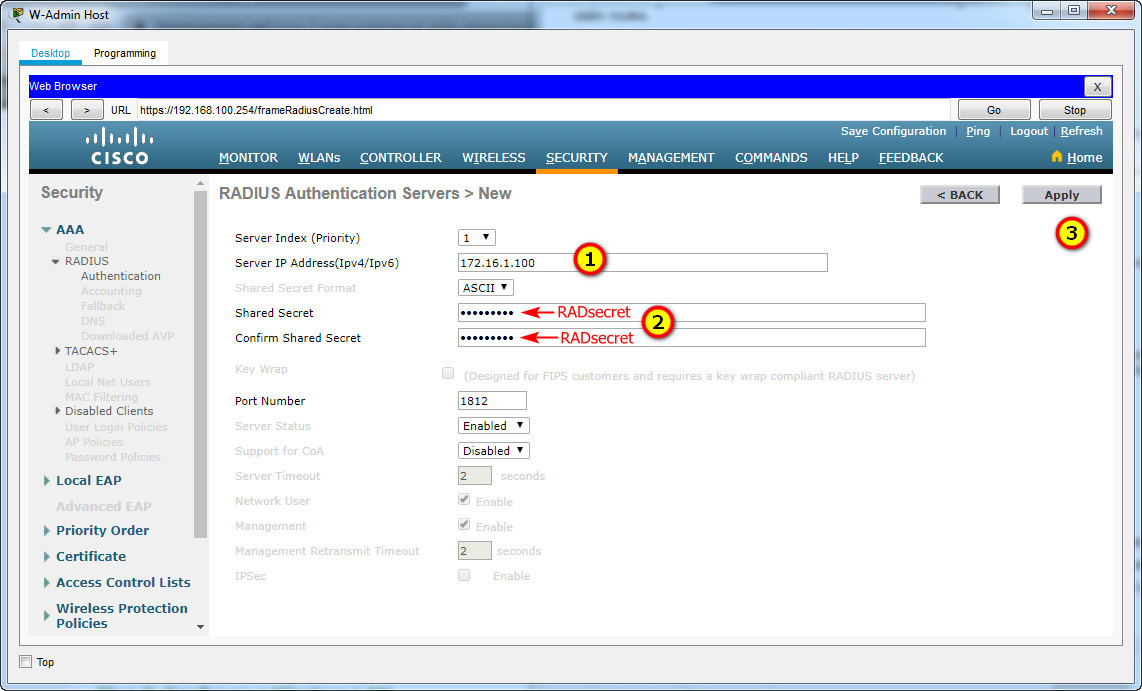
a. Configure the WLC with the RADIUS server IPv4 address.
b. Use a shared secret of RADsecret.
Go to SECURITY > RADIUS > Authentication and click New....
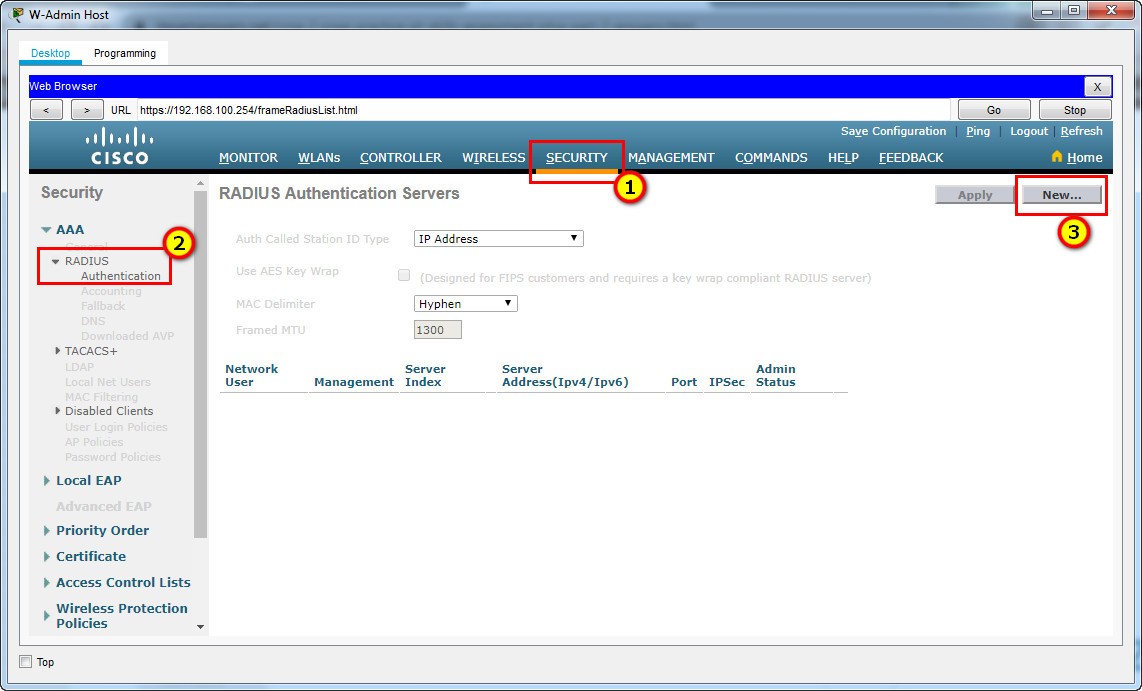
On the RADIUS Authentication Servers > New page, enter the values from the table below, then click Apply.
| Setting | Value |
|---|---|
| Server IP Address | 172.16.1.100 |
| Shared Secret | RADsecret |
| Confirm Shared Secret | RADsecret |
Step 3: Configure a Wireless LAN.
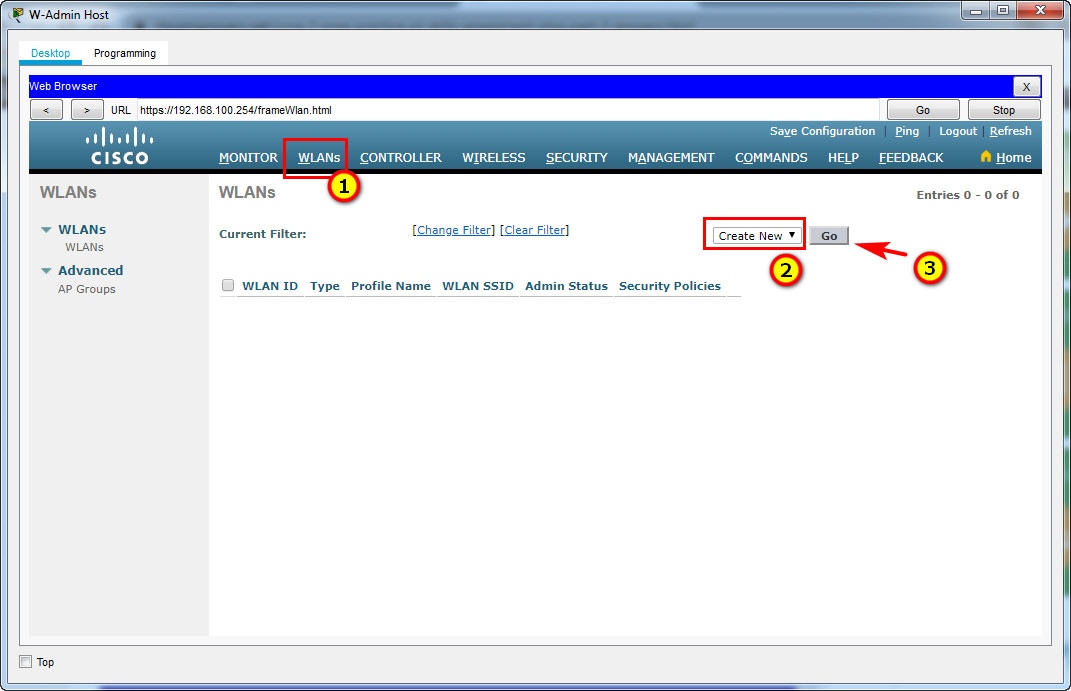
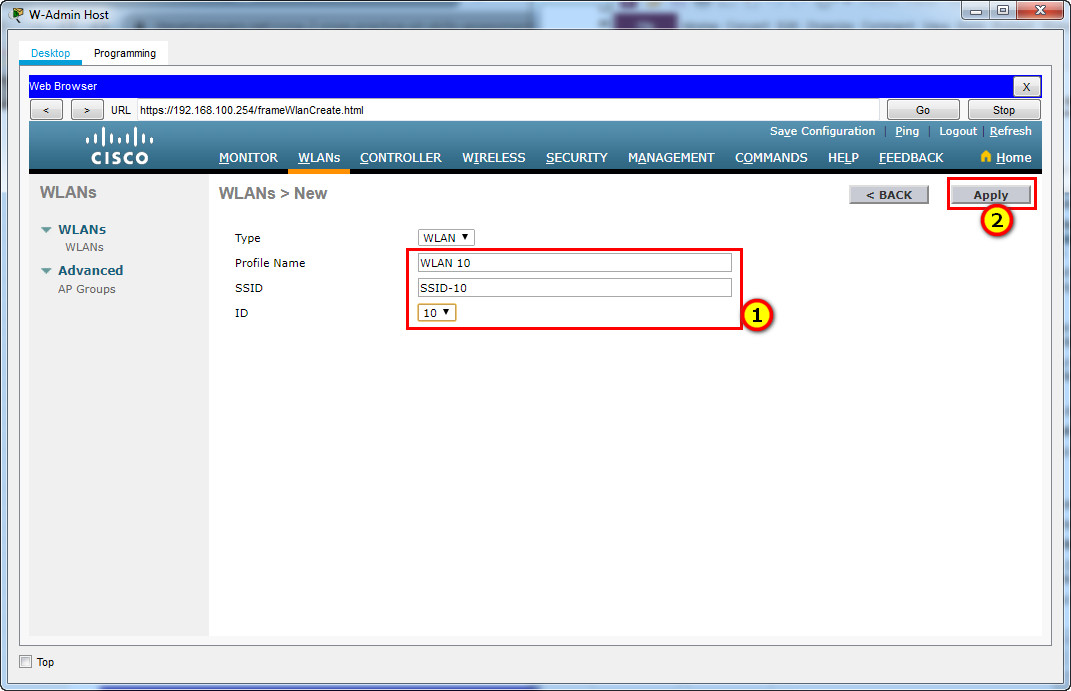
a. Create a new WLAN. Name it WLAN 10 and configure the SSID as SSID-10.
Go to the WLANs menu, select Create New from the drop-down list and click Go.
On the WLANs > New page, enter WLAN 10 as the Profile Name and SSID-10 as the SSID, select 10 in the ID list, then click Apply.
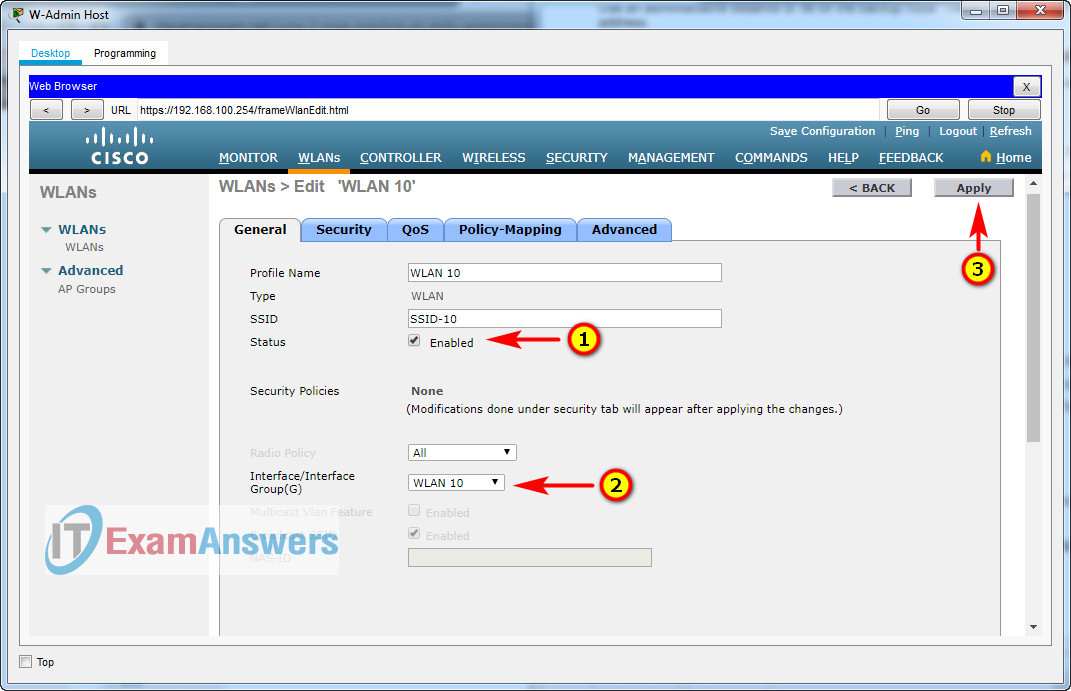
b. The wireless LAN should use the VLAN interface that was previously configured.
On the WLANs > Edit 'WLAN 10' page, General tab, check Enabled next to Status, select WLAN 10 in the Interface/Interface Group(G) list, then click Apply.
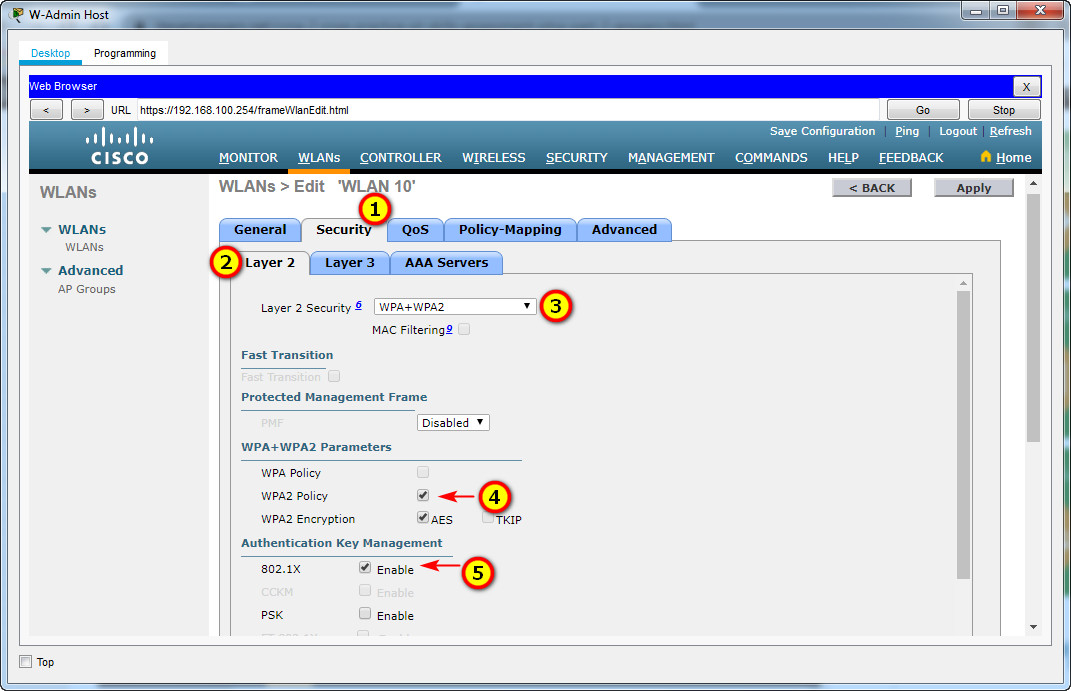
c. Configure the WLAN to use the WPA2 security policy and dot1x Authentication Key Management.
Open the Security tab, then the Layer 2 tab. Set Layer 2 Security to WPA+WPA2, check WPA2 Policy (with AES encryption), and under Authentication Key Management check Enable next to 802.1X.
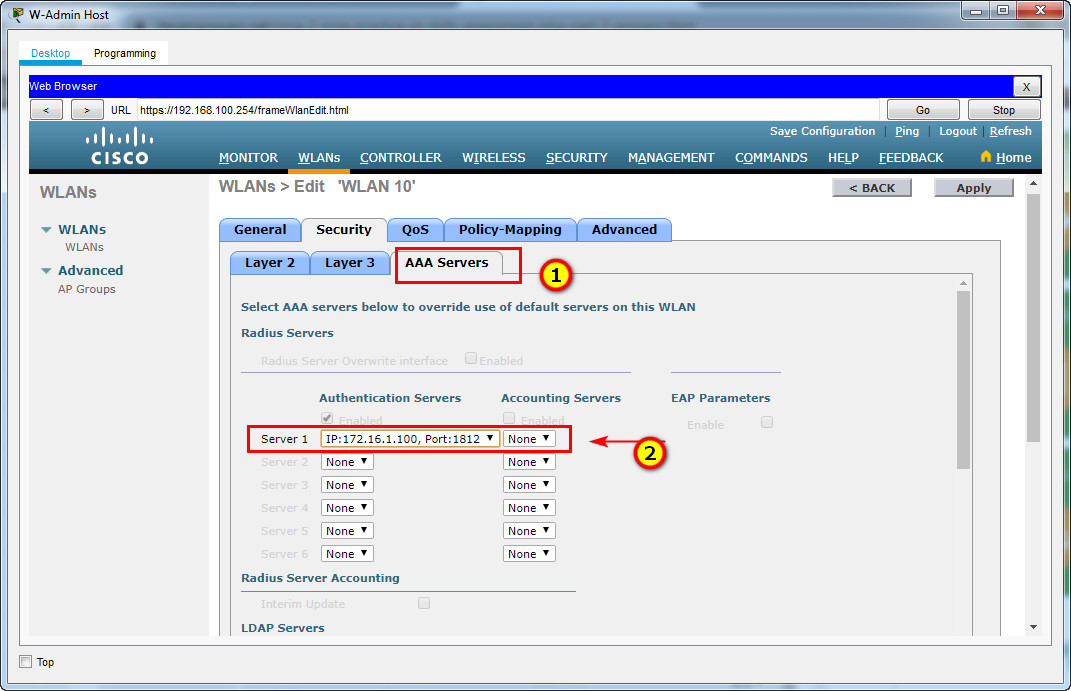
d. Configure the WLAN to use the RADIUS server that was previously configured to authenticate wireless users.
Open the AAA Servers tab. Under Server 1, select IP:172.16.1.100, Port:1812.
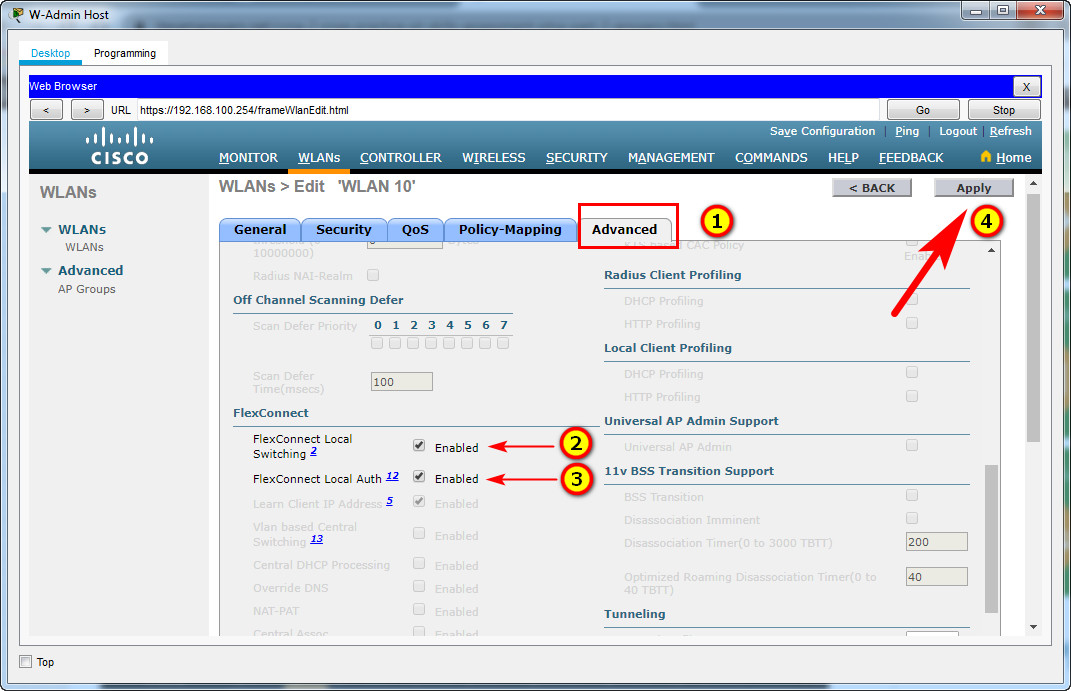
e. Open the Advanced tab and scroll down to the Flexconnect sections. Activate FlexConnect Local Switching and FlexConnect Local Auth.
Open the Advanced tab and scroll down to the FlexConnect section. Check Enabled for both FlexConnect Local Switching and FlexConnect Local Auth, then click Apply.
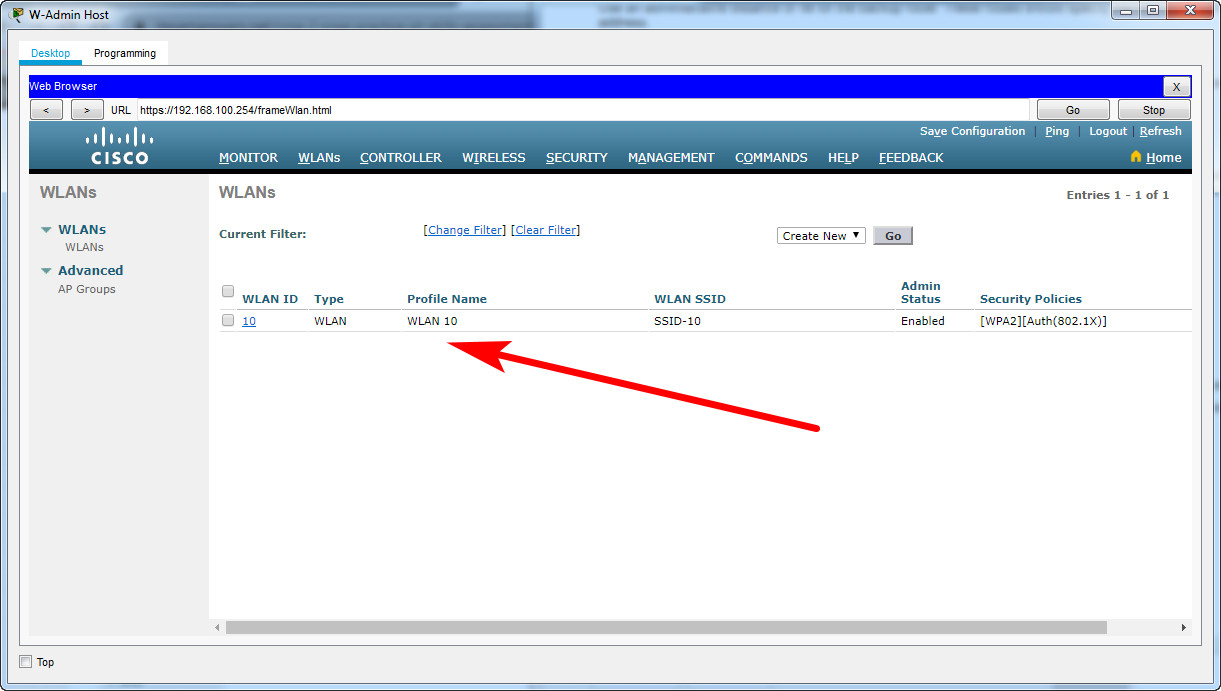
f. Verify that the WLAN is configured and operational.
Go back to the WLANs page and check that WLAN 10 (SSID SSID-10) is listed with an Admin Status of Enabled.
Step 4: Configure a DHCP scope for the management network.
Configure a new DHCP scope to be used by the LAPs and other management devices on the network.
a. Name the DHCP scope Wired_Admin.
Go to CONTROLLER, expand Internal DHCP Server, click DHCP Scope, then click New....
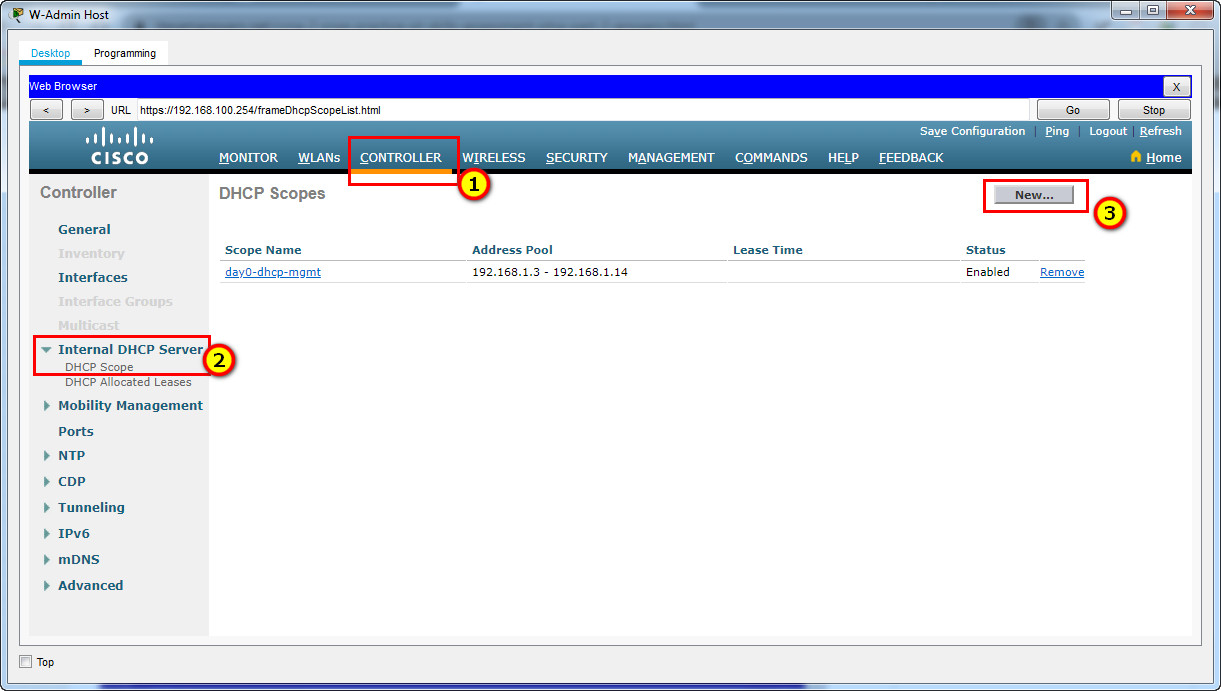
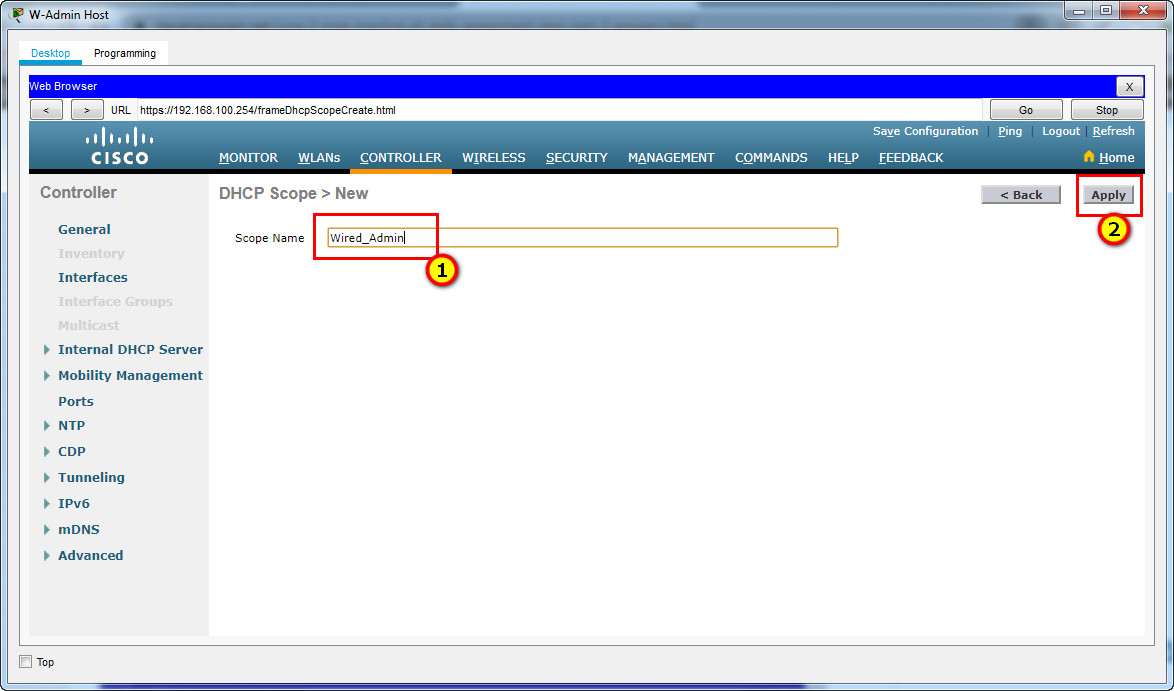
On the DHCP Scope > New page, enter Wired_Admin as the Scope Name, then click Apply.
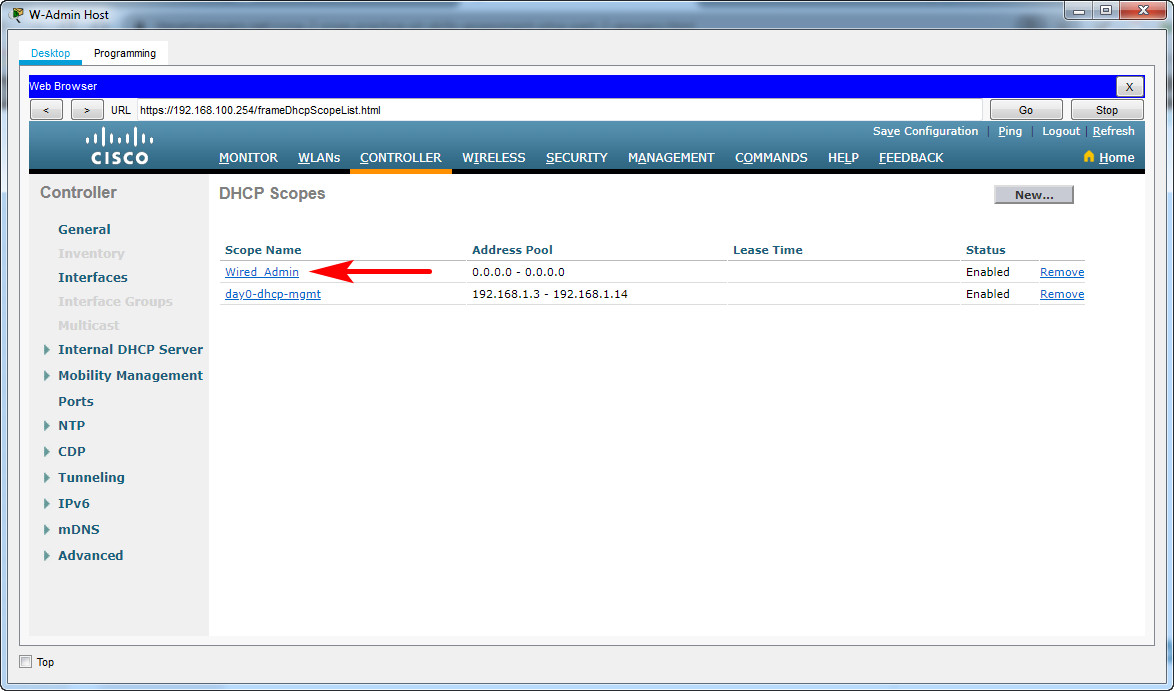
b. Start the scope at address 192.168.100.240. End the scope at address 192.168.100.249.
Click the Wired_Admin scope you just created.
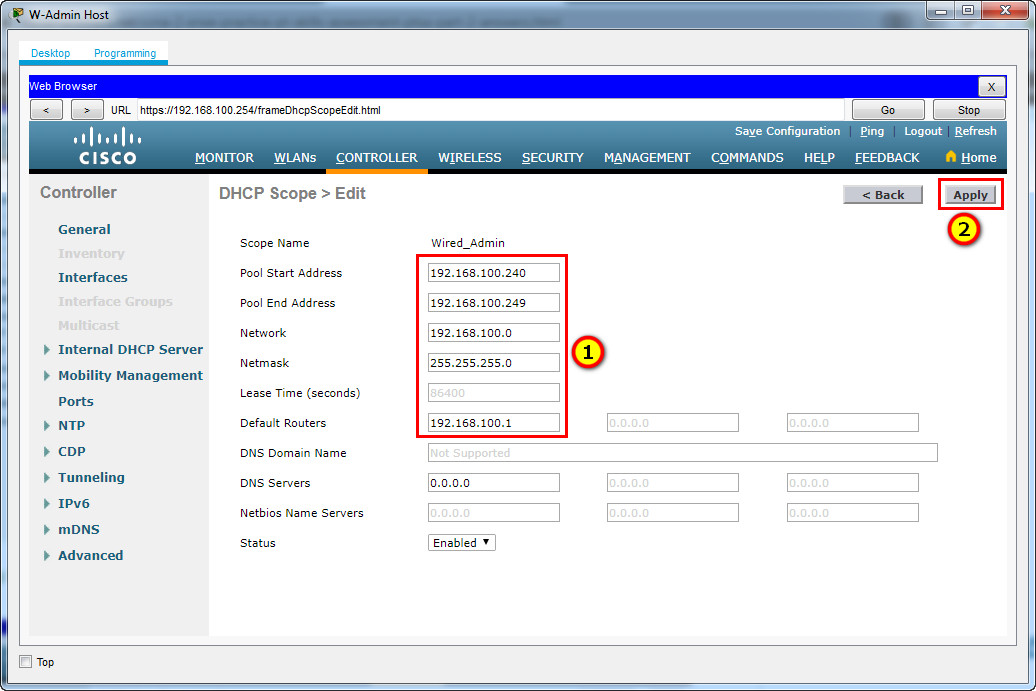
On the DHCP Scope > Edit page, enter the values from the table below, then click Apply.
| Setting | Value |
|---|---|
| Scope Name | Wired_Admin |
| Pool Start Address | 192.168.100.240 |
| Pool End Address | 192.168.100.249 |
| Network | 192.168.100.0 |
| Netmask | 255.255.255.0 |
| Default Routers | 192.168.100.1 |
c. Other information that is required can be found in the Addressing Table.
Step 5: Configure an SNMP server.
Configure an SNMP server to receive traps from the WLC.
a. Use the community name branch-wireless.
b. Use 172.16.1.100 as the server address.
Go to MANAGEMENT, expand SNMP, click Trap Receivers, then click New....
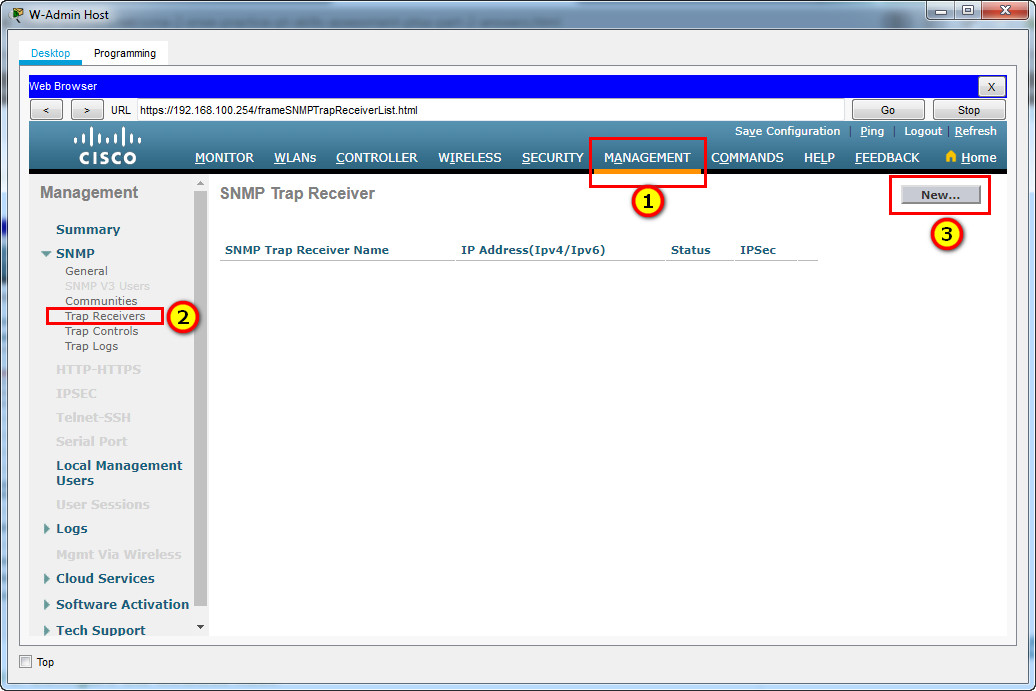
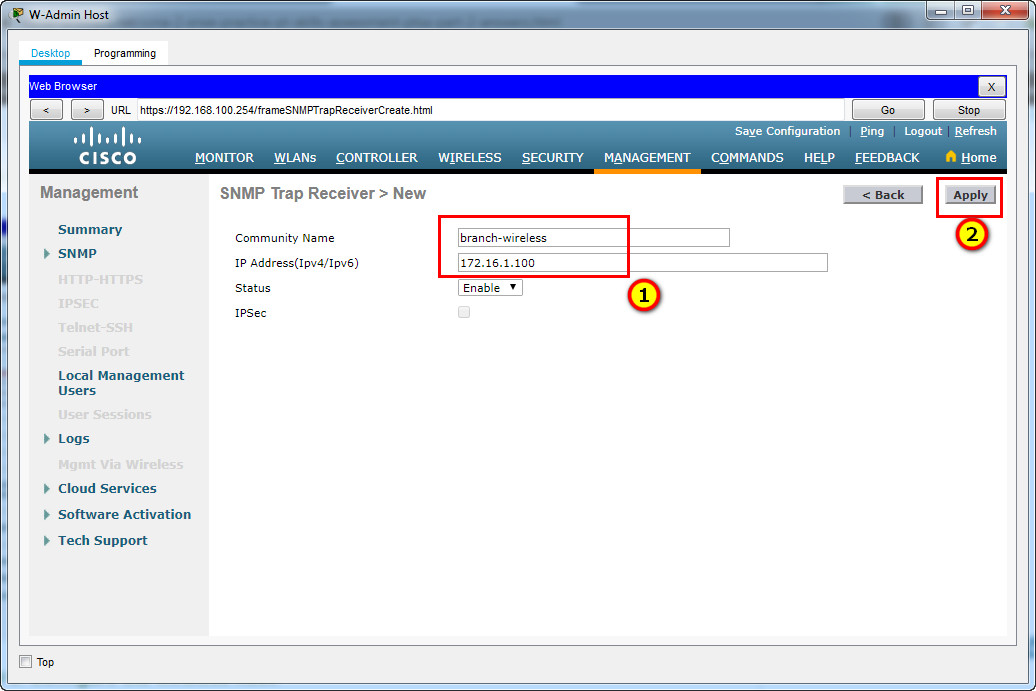
On the SNMP Trap Receiver > New page, enter branch-wireless as the Community Name and 172.16.1.100 as the IP Address(Ipv4/Ipv6), then click Apply.
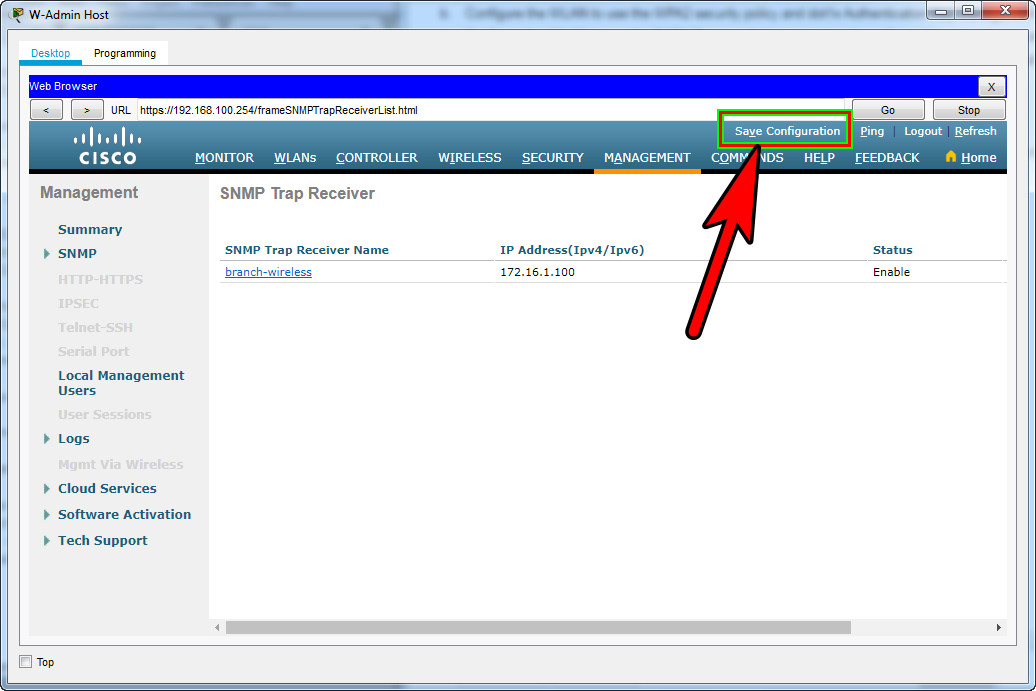
Click Save Configuration at the top-right of the page to save all WLC settings.
Step 6: Configure the wireless host.
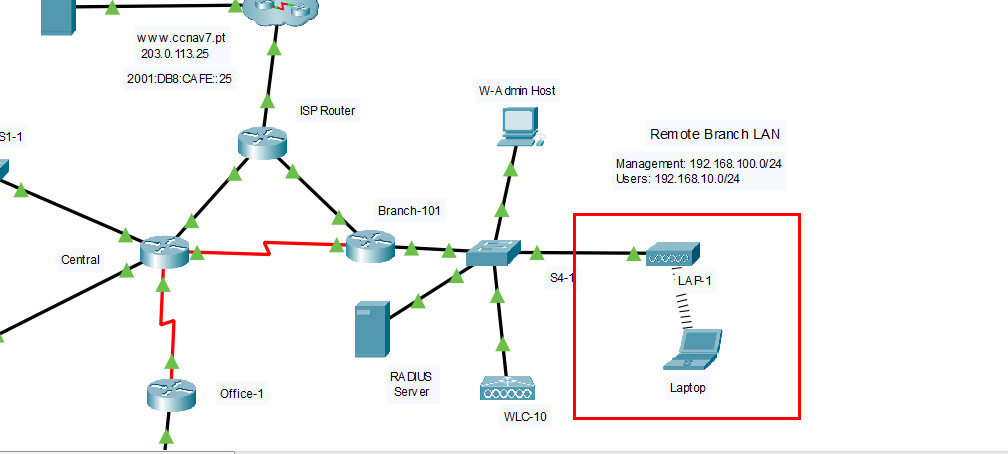
Configure the LT-1 laptop to connect to the WLAN.
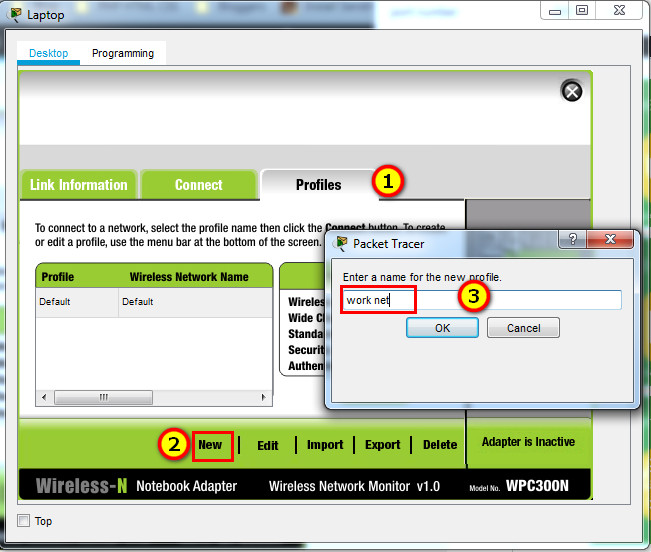
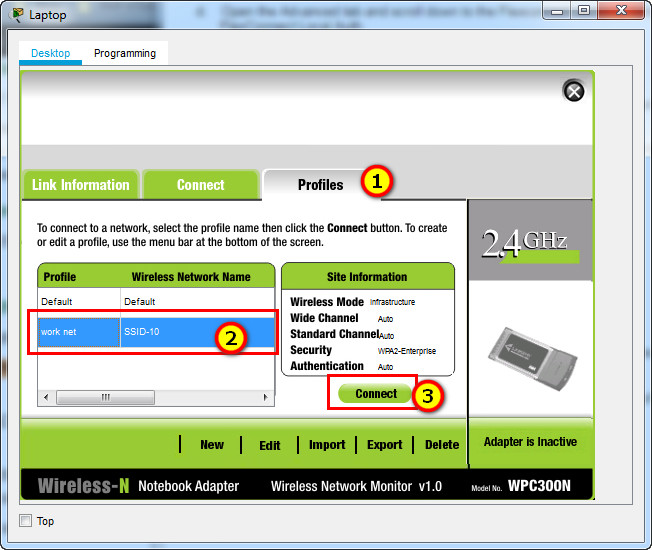
a. Create a new wireless profile on the host. Use the name work net for the profile.
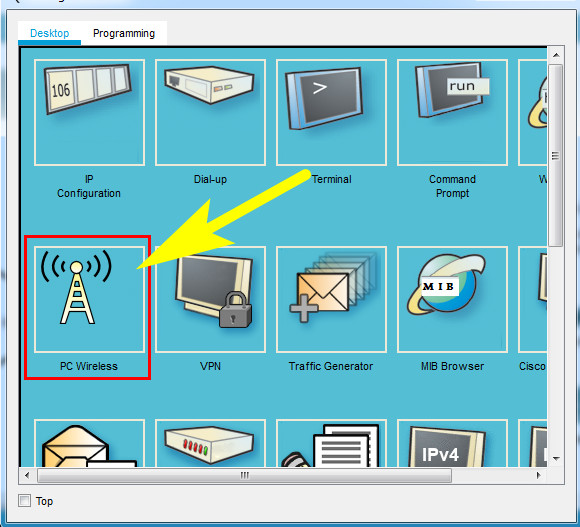
Click the LT-1 laptop, open the Desktop tab, then click PC Wireless. On the Profiles tab, click New and enter work net as the profile name.
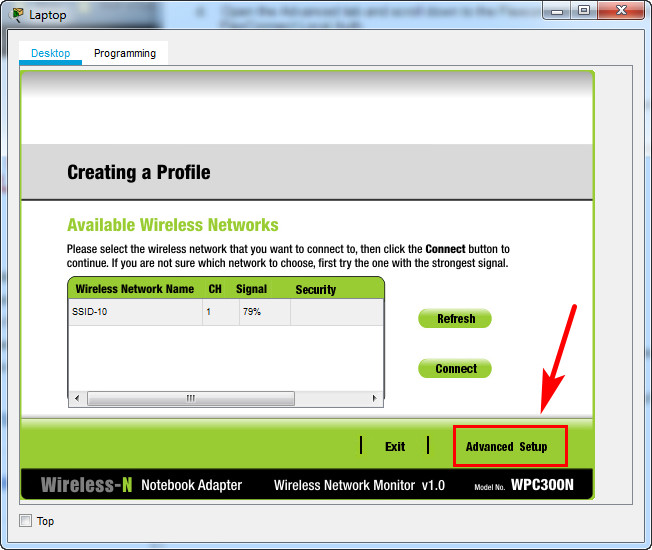
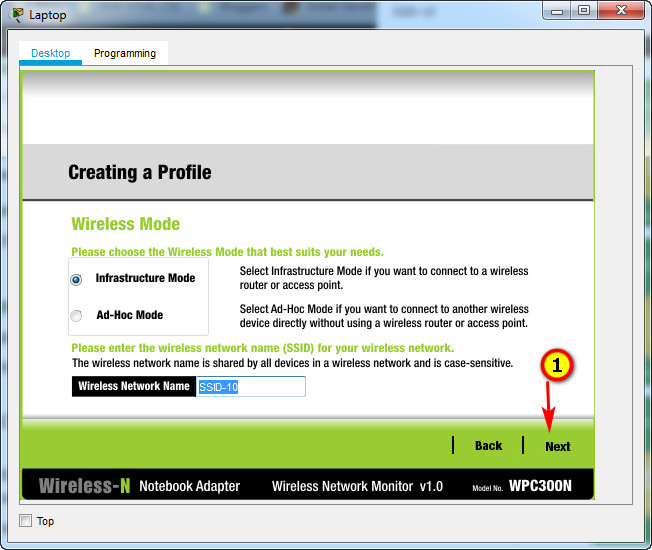
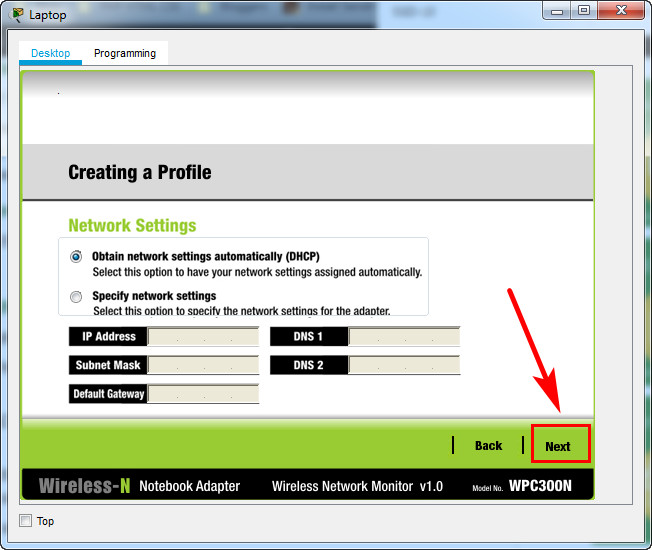
b. Configure the profile for the SSID of the WLAN.
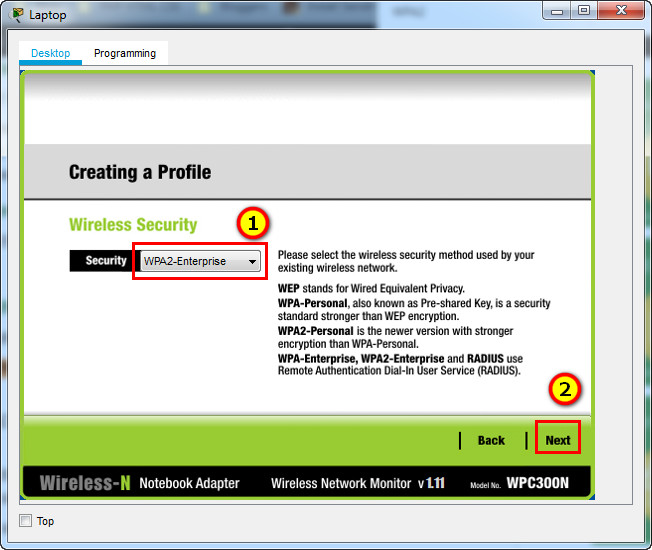
c. Use enterprise authentication with a username of user1 and password of user1Pass.
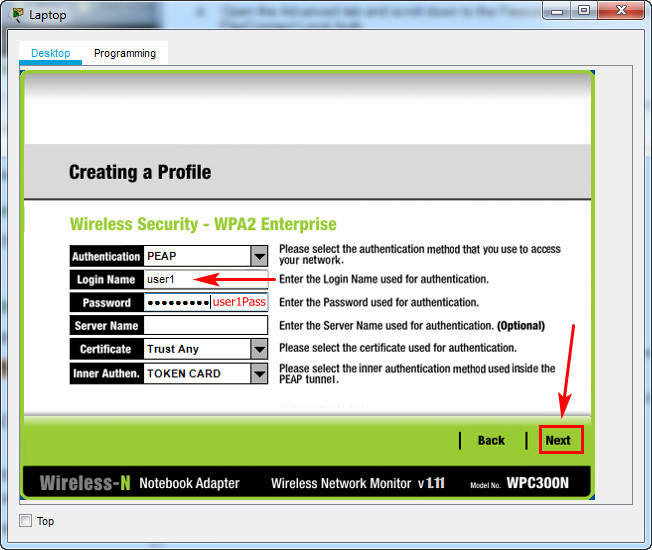
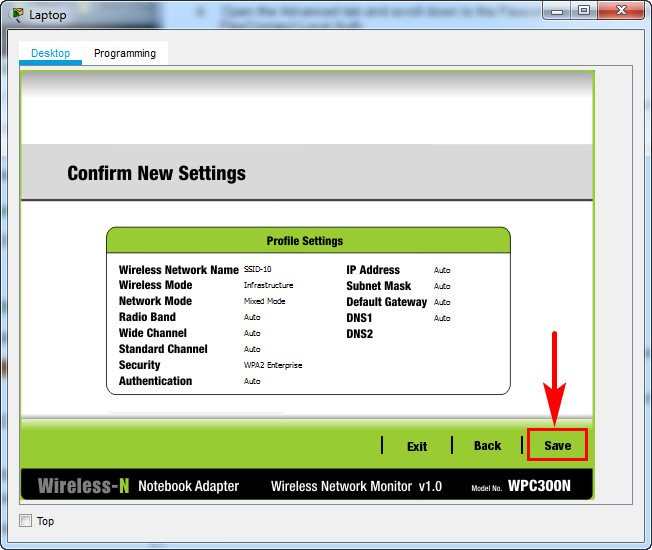
d. When you are finished, click Connect to Network. It will take time for the connection to be established.
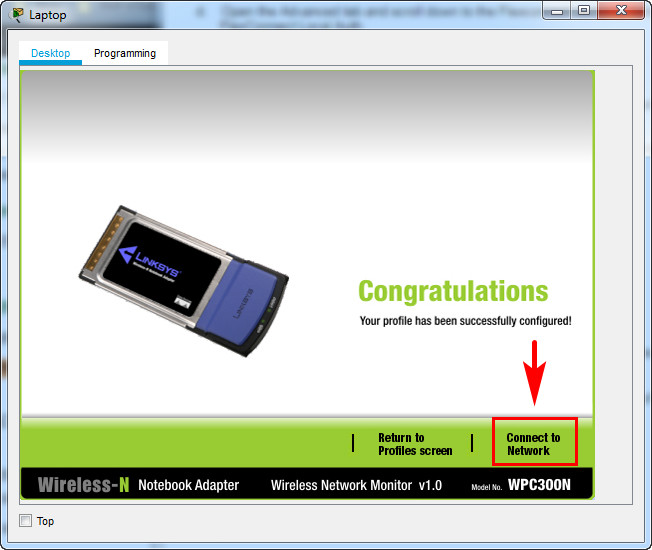
Result
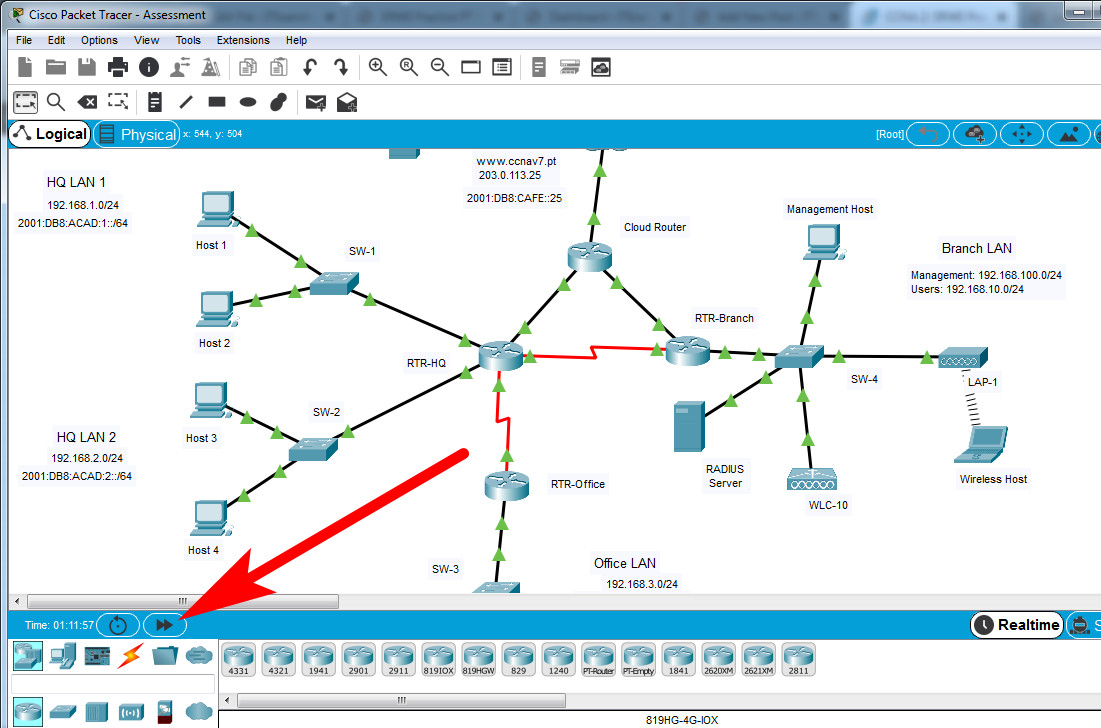
Click Fast Forward Time to speed up the process.
Device Configs - Final
ROUTER R-1-A
! ==============================================================
!--- SRWE Practice Packet Tracer Assessment - Part 2 - ID 2
!--- ANSWER SCRIPT FOR ROUTER R-1-A
!--- Usage: copy this whole file and paste it into the R-1-A terminal (start at the R-1-A> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: Configure Static Routes.
! --------------------------------------------------------------

!--- Step 1a. Directly connected IPv4 default route through the Ethernet link, floating backup through the serial link with AD 10.
ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/2
ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10

!--- Step 1b. Route IPv6.
ipv6 unicast-routing

!--- Step 1c. IPv6 default route to the Edge Router (next hop), floating backup to R-B-10 over the serial link with AD 10.
ipv6 route ::/0 2001:db8:acad:a::2
ipv6 route ::/0 2001:db8:acad:b::2 10

!--- Step 1d. Directly connected IPv4 static route to the Village Branch WLAN user network, floating backup with AD 10.
ip route 192.168.10.0 255.255.255.0 GigabitEthernet0/0/2
ip route 192.168.10.0 255.255.255.0 Serial0/1/0 10

!--- Step 1e. Host routes to Server O-S-10: directly connected for IPv4, next hop for IPv6.
ip route 192.168.3.122 255.255.255.255 Serial0/1/1
ipv6 route 2001:db8:acad:3::122/128 2001:db8:acad:d::2

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip route static             -> S* 0.0.0.0/0 and S 192.168.10.0/24 via GigabitEthernet0/0/2; S 192.168.3.122/32 via Serial0/1/1
!---   show ipv6 route                  -> S ::/0 via 2001:DB8:ACAD:A::2; S 2001:DB8:ACAD:3::122/128 via 2001:DB8:ACAD:D::2
!--- Note: the floating routes (AD 10) appear in the routing table only when the Ethernet link is down.
! ==============================================================
ROUTER R-B-10
! ==============================================================
!--- SRWE Practice Packet Tracer Assessment - Part 2 - ID 2
!--- ANSWER SCRIPT FOR ROUTER R-B-10
!--- Usage: copy this whole file and paste it into the R-B-10 terminal (start at the R-B-10> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2: Configure Addressing and DHCP.
! --------------------------------------------------------------

!--- Step 1. Subinterface 10 on G0/0/0 (to Sw-D): router-on-a-stick for VLAN 10 with the address from the Addressing Table.
interface gigabitethernet 0/0/0.10
 description Gateway for VLAN 10 (WLAN users)
 encapsulation dot1q 10
 ip address 192.168.10.1 255.255.255.0
 exit

!--- Step 2a. Exclude the router interface address and the WLC address.
ip dhcp excluded-address 192.168.10.1
ip dhcp excluded-address 192.168.10.254

!--- Step 2b. DHCP pool WLAN-hosts: 192.168.10.0/24, default gateway and DNS server.
ip dhcp pool WLAN-hosts
 network 192.168.10.0 255.255.255.0
 default-router 192.168.10.1
 dns-server 198.51.100.163
 exit

!--- Step 3. G0/0/1 (to Edge Router) receives its address over DHCP.
interface gigabitethernet 0/0/1
 ip address dhcp
 exit

! --------------------------------------------------------------
!--- Part 3: Configure Static Routes.
! --------------------------------------------------------------

!--- Step 2a. IPv4 default route through the Ethernet link (exit interface), floating backup through the serial link with AD 10.
ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/1
ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10

!--- Step 2b. Route IPv6.
ipv6 unicast-routing

!--- Step 2c. IPv6 default route to the Edge Router (next hop), floating backup to R-1-A over the serial link with AD 10.
ipv6 route ::/0 2001:db8:acad:c::1
ipv6 route ::/0 2001:db8:acad:b::1 10

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief          -> G0/0/0.10 192.168.10.1; G0/0/1 address learned by DHCP
!---   show ip dhcp pool                -> pool WLAN-hosts, 192.168.10.0/24
!---   show ip route static             -> S* 0.0.0.0/0 via GigabitEthernet0/0/1
!---   show ipv6 route                  -> S ::/0 via 2001:DB8:ACAD:C::1
! ==============================================================
SWITCH Sw-A
! ==============================================================
!--- SRWE Practice Packet Tracer Assessment - Part 2 - ID 2
!--- ANSWER SCRIPT FOR SWITCH Sw-A
!--- Usage: copy this whole file and paste it into the Sw-A terminal (start at the Sw-A> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1: Configure Switch Security.
! --------------------------------------------------------------

!--- Step 1a. VLAN 10 with name users.
vlan 10
 name users
 exit

!--- Step 1b. VLAN 999 with name unused.
vlan 999
 name unused
 exit

!--- Step 2a. F0/1-5 and G0/1 as static access ports in VLAN 10.
interface range fastethernet 0/1 - 5, gigabitethernet 0/1
 switchport mode access
 switchport access vlan 10
 exit

!--- Step 2b. Port security on the active ports: maximum 4 MAC addresses, restrict on violation (drop, log, alert), 10-minute aging, sticky learning.
interface range fastethernet 0/1 - 5
 switchport port-security
 switchport port-security maximum 4
 switchport port-security violation restrict
 switchport port-security aging time 10
 switchport port-security mac-address sticky
 exit

!--- Step 2b-5. MAC address of HQ-1-1 as a static secure address on F0/1.
interface fastethernet 0/1
 switchport port-security mac-address 00D0.D3DC.2825
 exit

!--- Step 2c-1/2. DHCP snooping globally and for VLANs 10 and 999.
ip dhcp snooping
ip dhcp snooping vlan 10,999

!--- Step 2c-3. Limit the active ports to 5 DHCP packets per second.
interface range fastethernet 0/1 - 5, gigabitethernet 0/1
 ip dhcp snooping limit rate 5
 exit

!--- Step 2c-4. The port that links to the router is trusted for DHCP snooping.
interface gigabitethernet 0/1
 ip dhcp snooping trust
 exit

!--- Step 2d-1/2. DAI on VLANs 10 and 999.
ip arp inspection vlan 10,999

!--- Step 2d-3. The port that links to the router is trusted for DAI.
interface gigabitethernet 0/1
 ip arp inspection trust
 exit

!--- Step 2e. PortFast and BPDU guard on the active ports.
interface range fastethernet 0/1 - 5
 spanning-tree portfast
 spanning-tree bpduguard enable
 exit

!--- Step 3. All unused ports: VLAN 999, static access, shut down.
interface range fastethernet 0/6 - 24, gigabitethernet 0/2
 switchport access vlan 999
 switchport mode access
 shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show vlan brief                  -> F0/1-5, G0/1 in VLAN 10 (users); F0/6-24, G0/2 in VLAN 999 (unused)
!---   show port-security               -> F0/1-5: max 4, violation Restrict
!---   show ip dhcp snooping            -> enabled on VLANs 10,999; G0/1 trusted; rate limit 5
!---   show ip arp inspection           -> enabled on VLANs 10,999
! ==============================================================
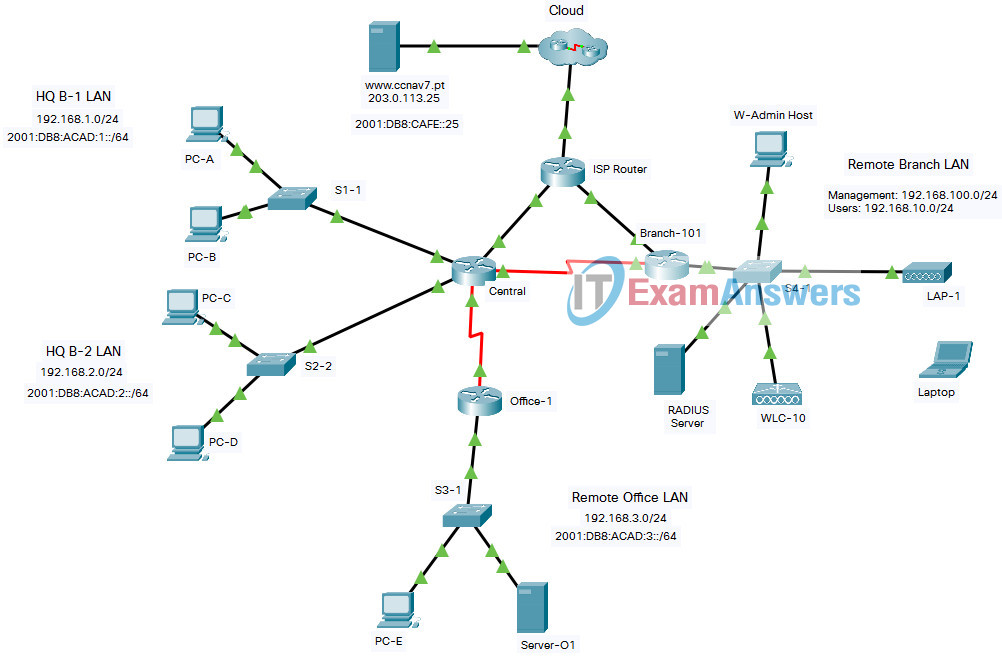
SRWE Practice PT Skills Assessment (PTSA) - Part 2 ID 1
SRWE Practice Packet Tracer Assessment - Part 2
A few things to keep in mind while completing this activity:
- Do not use the browser Back button or close or reload any exam windows during the exam.
- Do not close Packet Tracer when you are done. It will close automatically.
- Click the Submit Assessment button in the browser window to submit your work.
Addressing Table
| Device | Interface | Address and Prefix |
|---|---|---|
| Central | G0/0/0 | 192.168.1.1/24 |
| 2001:db8:acad:1::1/64 | ||
| fe80::1 | ||
| G0/0/1 | 192.168.2.1/24 | |
| 2001:db8:acad:2::1/64 | ||
| fe80::1 | ||
| G0/0/2 | 10.1.0.1/30 | |
| 2001:db8:acad:a::1/64 | ||
| fe80::2 | ||
| S0/1/0 | 10.2.0.1/30 | |
| 2001:db8:acad:b::1/64 | ||
| fe80::2 | ||
| S0/1/1 | 10.4.0.1/30 | |
| 2001:db8:acad:d::1/64 | ||
| Office-1 | S0/1/1 | 10.4.0.2/30 |
| 2001:db8:acad:d::2/64 | ||
| fe80::2 | ||
| G0/0/0 | 192.168.3.1/24 | |
| 2001:db8:acad:3::1/64 | ||
| fe80::1 | ||
| Branch-101 | G0/0/0.10 | 192.168.10.1/24 |
| G0/0/0.100 | 192.168.100.1/24 | |
| G0/0/0.172 | 172.16.1.1/24 | |
| G0/0/1 | DHCP | |
| 2001:db8:acad:c::2/64 | ||
| S0/1/0 | 10.2.0.2/30 | |
| 2001:db8:acad:b::2/64 | ||
| ISP Router | G0/0/0 | 10.1.0.2/24 |
| 2001:DB8:ACAD:A::2/64 | ||
| G0/0/1 | 10.3.0.1/24 | |
| 2001:DB8:ACAD:C::1/64 | ||
| WLC-10 | management | 192.168.100.254 |
| WLAN 10 | 192.168.10.254/24 | |
| Server-O1 | NIC | 192.168.3.122 |
| 2001:db8:acad:3::122 | ||
| Internet Server | NIC | 203.0.113.25 |
| 2001:db8:acad:cafe:25 | ||
| DNS Server | NIC | 198.51.100.163 |
| 2001:DB8:face::163 | ||
| Management Host (Admin PC) | NIC | 192.168.100.23 |
| Wireless Host | NIC | DHCP |
| RADIUS server | NIC | 172.16.1.100/24 |
| PC-A | NIC | 192.168.1.10/24 |
| 2001:db8:acad:1::10/64 | ||
| PC-B | NIC | 192.168.1.11/24 |
| 2001:db8:acad:1::11/64 | ||
| PC-C | NIC | 192.168.2.20/24 |
| 2001:db8:acad:2::20/64 | ||
| PC-D | NIC | 192.168.2.21/24 |
| 2001:db8:acad:2::21/64 | ||
| PC-E | NIC | 192.168.3.30/24 |
| 2001:db8:acad:3::30/64 |
Objectives
In this assessment, you will configure the following:
- Floating static and default routes in IPv4 and IPv6.
- Host routes in IPv4 and IPv6.
- DHCP pools and scopes.
- Switch security including port security.
- Enhanced LAN security with DHCP snooping, dynamic ARP inspection, PortFast, and BPDU guard.
- Wireless LAN Controller-based wireless LAN with enterprise authentication.
You will only configure the Central and Branch-101 routers, the S1-1 switch, and the WLC-10 wireless LAN controller. Access to other devices is not available.
Background / Scenario
Netacad PLC is reworking their network. You have been asked to prototype the network in Packet Tracer for evaluation by senior network staff.
Instructions
Part 1: Configure Switch Security
In this part of the assessment you will configure switch S1-1 with switch security features. Switch ports FastEthernet0/1 to FastEthernet0/5 are the active switch ports. Port GigabitEthernet0/1 is a dedicated link to router Central. All other ports should be secured.
Step 1: Configure VLANs
a. Configure VLAN 10 with name users.
S1-1(config)# vlan 10
S1-1(config-vlan)# name users
b. Configure VLAN 999 with the name unused.
S1-1(config-vlan)# vlan 999
S1-1(config-vlan)# name unused
Step 2: Configure active switch ports.
On the active switch ports configure the following:
a. Configure FastEthernet 0/1 through 0/5 and GigabitEthernet 0/1 as static access ports in VLAN 10.
S1-1(config)# interface range fastethernet 0/1 - 5, gigabitethernet 0/1
S1-1(config-if-range)# switchport mode access
S1-1(config-if-range)# switchport access vlan 10
b. Activate port security on the ports.
S1-1(config)# interface range fastethernet 0/1 - 5
S1-1(config-if-range)# switchport port-security
- Configure the active ports to accept a maximum of 4 MAC addresses.
S1-1(config-if-range)# switchport port-security maximum 4
- If a violation occurs, configure the ports to drop frames from the unauthorized MAC address, log it, and send an alert.
S1-1(config-if-range)# switchport port-security violation restrict
- MAC addresses should be present in the MAC address table for a maximum of 10 minutes before they are removed.
S1-1(config-if-range)# switchport port-security aging time 10
- Ports should add the learned MAC addresses to the running configuration.
S1-1(config-if-range)# switchport port-security mac-address sticky
- Configure the MAC address of PC-A as a static address on port FastEthernet0/1.
S1-1(config)# interface fastethernet 0/1
S1-1(config-if)# switchport port-security mac-address 00D0.D3DC.2825
c. Protect against DHCP snooping.
Note: In this simulated network, DHCP snooping may not operate correctly in Packet Tracer. Configure it as you would normally. You will receive full credit for a configuration that meets the requirements below.
- Activate DHCP snooping globally.
S1-1(config)# ip dhcp snooping
- Activate DHCP snooping for the two VLANs that you configured.
S1-1(config)# ip dhcp snooping vlan 10,999
- Configure the ports to limit the rate to 5 DHCP packets per second.
S1-1(config)# interface range fastethernet 0/1 - 5, gigabitethernet 0/1
S1-1(config-if-range)# ip dhcp snooping limit rate 5
- Configure the port that links to the router as trusted.
S1-1(config)# interface gigabitethernet 0/1
S1-1(config-if)# ip dhcp snooping trust
d. Guard against ARP attacks by implementing DAI.
- Activate DAI globally.
- Activate DAI on the two VLANs.
S1-1(config)# ip arp inspection vlan 10,999
- Configure the port that links to the router as trusted.
S1-1(config)# interface gigabitethernet 0/1
S1-1(config-if)# ip arp inspection trust
e. Mitigate STP attacks by configuring BPDUguard and PortFast on the active ports.
S1-1(config)# interface range fastethernet 0/1 - 5
S1-1(config-if-range)# spanning-tree portfast
S1-1(config-if-range)# spanning-tree bpduguard enable
Step 3: Secure unused switch ports.
a. Move all unused switch ports to VLAN 999.
S1-1(config)# interface range fastethernet 0/6 - 24, gigabitethernet 0/2
S1-1(config-if-range)# switchport access vlan 999
b. Configure all unused switch ports as static access ports.
S1-1(config-if-range)# switchport mode access
c. Deactivate all unused switch ports.
S1-1(config-if-range)# shutdown
Part 2: Configure Addressing and DHCP
You will configure DHCP and interface addressing on router Branch-101 to prepare for implementing the wireless LAN controller network.
Step 1: Configure and address a subinterface for the WLAN user network.
a. Configure subinterface 10 on the router interface that is connected to the switch S4-1.
Branch-101(config)# interface gigabitethernet 0/0/0.10
Branch-101(config-subif)# description Gateway for VLAN 10 (WLAN users)
b. The router should provide router-on-a-stick routing to VLAN 10.
Branch-101(config-subif)# encapsulation dot1q 10
c. Configure the subinterface with the address from the Addressing Table.
Branch-101(config-subif)# ip address 192.168.10.1 255.255.255.0
Step 2: Configure a DHCP pool for WLAN user network.
a. Exclude the router interface address and the management address of the WLC.
Branch-101(config)# ip dhcp excluded-address 192.168.10.1
Branch-101(config)# ip dhcp excluded-address 192.168.10.254
b. Configure a DHCP pool that will be used by hosts that are connecting to the WLAN.
- Name the pool WLAN-hosts.
Branch-101(config)# ip dhcp pool WLAN-hosts
- Configure the pool to use addresses in the 192.168.10.0/24 network.
Branch-101(dhcp-config)# network 192.168.10.0 255.255.255.0
- The pool should also provide the default gateway and DNS server addresses.
Branch-101(dhcp-config)# default-router 192.168.10.1
Branch-101(dhcp-config)# dns-server 198.51.100.163
Step 3: Configure an interface as a DHCP client.
On Branch-101, configure the interface that is connected to ISP Router to receive its address over DHCP.
Branch-101(config)# interface gigabitethernet 0/0/1
Branch-101(config-if)# ip address dhcp
Part 3: Configure Static Routes
In this part of the assessment you will configure static, default, floating static, and host routes in both IPv4 and IPv6. You will configure the Central and Branch-101 routers. Netacad PLC has decided that it wants to use static routing between all its networks. In addition, the company wants to use the Ethernet links between routers for most data traffic and reserve serial link between Central and Branch-101 for backup purposes in case one of the Ethernet links becomes unavailable. You will be configuring floating static and default routes.
Step 1: Configure static routes on Central.
a. Configure IPv4 default routes to the cloud using the Ethernet link as the preferred link and the serial link as the floating backup. Use an administrative distance of 10 for the backup route. These routes should be configured as directly connected routes.
Note: Ethernet interfaces will give a warning when configured without a next-hop address. In this configuration, the interface is point-to-point, so the warning can be ignored.
Central(config)# ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/2
Central(config)# ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10
b. Ensure that the device is configured to route IPv6.
Central(config)# ipv6 unicast-routing
c. Configure IPv6 default routes to the cloud. Use the Ethernet link as the primary route, and the serial link as the floating backup. Use an administrative distance of 10 for the backup route. These routes should specify the next hop interface address.
Central(config)# ipv6 route ::/0 2001:db8:acad:a::2
Central(config)# ipv6 route ::/0 2001:db8:acad:b::2 10
d. Configure IPv4 static routes to the Remote Branch LAN WLAN user network following the same guidelines as above for type of route and administrative distance.
Central(config)# ip route 192.168.10.0 255.255.255.0 GigabitEthernet0/0/2
Central(config)# ip route 192.168.10.0 255.255.255.0 Serial0/1/0 10
e. Configure IPv4 and IPv6 host routes on Central to the Server-O1 on the Remote Office LAN. Create a directly connected route for IPv4 and a next-hop route for IPv6.
Central(config)# ip route 192.168.3.122 255.255.255.255 Serial0/1/1
Central(config)# ipv6 route 2001:db8:acad:3::122/128 2001:db8:acad:d::2
Step 2: Configure static routes on Branch-101.
Branch-101 must also be configured with static routes to the other three networks in the Netacad PLC network. It will require floating static and default routes in IPv4 and IPv6 following the same guidelines as were used for the Central static routes.
- IPv6 routes use next-hop address arguments.
- IPv4 routes use exit interface arguments.
- All routes should prefer the Ethernet links over the serial link.
- Backup floating routes use an administrative distance of 10.
a. Configure IPv4 default routes to the cloud using the Ethernet link as the preferred link and the serial link as the backup.
Branch-101(config)# ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/1
Branch-101(config)# ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10
b. Ensure that the device is configured to route IPv6.
Branch-101(config)# ipv6 unicast-routing
c. Configure IPv6 default routes to the cloud. Use the Ethernet link as the primary route, and the serial link as backup. Use an administrative distance of 10 for the backup route. These routes should specify the next hop interface address.
Branch-101(config)# ipv6 route ::/0 2001:db8:acad:c::1
Branch-101(config)# ipv6 route ::/0 2001:db8:acad:b::1 10
Part 4: Configure a Wireless LAN using a Wireless LAN Controller
In this part of the assessment, you will configure the wireless LAN controller to provide wireless access to the network. Username and password are the default admin/admin. Connect to the WLC over HTTPS to the management interface.
Click Management Host (Admin PC), open the Desktop tab, then Web Browser, and go to the WLC management address over HTTPS: https://192.168.100.254
Log in with the username admin and the password admin.
Step 1: Configure a VLAN interface.
a. Create a new interface and name it WLAN 10. The interface should use VLAN 10 and physical port 1.
Go to CONTROLLER > Interfaces and click New....
On the Interfaces > New page, enter WLAN 10 in the Interface Name box and 10 in the VLAN Id box, then click Apply.
b. Use the information in the addressing table to configure the addressing settings for the interface. The interface will be using a DHCP pool that is configured on the subinterface that is assigned to VLAN 10 on router Branch-101.
Go back to CONTROLLER > Interfaces and click the WLAN 10 interface you just created.
Enter the values from the table below in the matching fields, then click Apply.
| Setting | Value |
|---|---|
| Port Number | 1 |
| VLAN Identifier | 10 |
| IP Address | 192.168.10.254 |
| Netmask | 255.255.255.0 |
| Gateway | 192.168.10.1 |
| Primary DHCP Server | 192.168.10.1 |
Step 2: Configure a RADIUS server.
a. Configure the WLC with the RADIUS server IPv4 address.
b. Use a shared secret of RADsecret.
Go to SECURITY > RADIUS > Authentication and click New....
On the RADIUS Authentication Servers > New page, enter the values from the table below, then click Apply.
| Setting | Value |
|---|---|
| Server IP Address | 172.16.1.100 |
| Shared Secret | RADsecret |
| Confirm Shared Secret | RADsecret |
Step 3: Configure a Wireless LAN.
a. Create a new WLAN. Name it WLAN 10 and configure the SSID as SSID-10.
Go to the WLANs menu, select Create New from the drop-down list and click Go.
On the WLANs > New page, enter WLAN 10 as the Profile Name and SSID-10 as the SSID, select 10 in the ID list, then click Apply.
b. The wireless LAN should use the VLAN interface that was previously configured.
On the WLANs > Edit 'WLAN 10' page, General tab, check Enabled next to Status, select WLAN 10 in the Interface/Interface Group(G) list, then click Apply.
c. Configure the WLAN to use the WPA2 security policy and dot1x Authentication Key Management.
Open the Security tab, then the Layer 2 tab. Set Layer 2 Security to WPA+WPA2, check WPA2 Policy (with AES encryption), and under Authentication Key Management check Enable next to 802.1X.
d. Configure the WLAN to use the RADIUS server that was previously configured to authenticate wireless users.
Open the AAA Servers tab. Under Server 1, select IP:172.16.1.100, Port:1812.
e. Open the Advanced tab and scroll down to the Flexconnect sections. Activate FlexConnect Local Switching and FlexConnect Local Auth.
Open the Advanced tab and scroll down to the FlexConnect section. Check Enabled for both FlexConnect Local Switching and FlexConnect Local Auth, then click Apply.
f. Verify that the WLAN is configured and operational.
Go back to the WLANs page and check that WLAN 10 (SSID SSID-10) is listed with an Admin Status of Enabled.
Step 4: Configure a DHCP scope for the management network.
Configure a new DHCP scope to be used by the LAPs and other management devices on the network.
a. Name the DHCP scope Wired_Admin.
Go to CONTROLLER, expand Internal DHCP Server, click DHCP Scope, then click New....
On the DHCP Scope > New page, enter Wired_Admin as the Scope Name, then click Apply.
b. Start the scope at address 192.168.100.240. End the scope at address 192.168.100.249.
Click the Wired_Admin scope you just created.
On the DHCP Scope > Edit page, enter the values from the table below, then click Apply.
| Setting | Value |
|---|---|
| Scope Name | Wired_Admin |
| Pool Start Address | 192.168.100.240 |
| Pool End Address | 192.168.100.249 |
| Network | 192.168.100.0 |
| Netmask | 255.255.255.0 |
| Default Routers | 192.168.100.1 |
c. Other information that is required can be found in the Addressing Table.
Step 5: Configure an SNMP server.
Configure an SNMP server to receive traps from the WLC.
a. Use the community name branch-wireless.
b. Use 172.16.1.100 as the server address.
Go to MANAGEMENT, expand SNMP, click Trap Receivers, then click New....
On the SNMP Trap Receiver > New page, enter branch-wireless as the Community Name and 172.16.1.100 as the IP Address(Ipv4/Ipv6), then click Apply.
Click Save Configuration at the top-right of the page to save all WLC settings.
Step 6: Configure the wireless host.
Configure the LT-1 laptop to connect to the WLAN.
a. Create a new wireless profile on the host. Use the name work net for the profile.
Click the LT-1 laptop, open the Desktop tab, then click PC Wireless. On the Profiles tab, click New and enter work net as the profile name.
b. Configure the profile for the SSID of the WLAN.
c. Use enterprise authentication with a username of user1 and password of user1Pass.
d. When you are finished, click Connect to Network. It will take time for the connection to be established.
Result
Click Fast Forward Time to speed up the process.
Device Configs - Final
ROUTER Central
! ==============================================================
!--- SRWE Practice Packet Tracer Assessment - Part 2 - ID 1
!--- ANSWER SCRIPT FOR ROUTER Central
!--- Usage: copy this whole file and paste it into the Central terminal (start at the Central> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: Configure Static Routes.
! --------------------------------------------------------------

!--- Step 1a. Directly connected IPv4 default route through the Ethernet link, floating backup through the serial link with AD 10.
ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/2
ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10

!--- Step 1b. Route IPv6.
ipv6 unicast-routing

!--- Step 1c. IPv6 default route to the ISP Router (next hop), floating backup to Branch-101 over the serial link with AD 10.
ipv6 route ::/0 2001:db8:acad:a::2
ipv6 route ::/0 2001:db8:acad:b::2 10

!--- Step 1d. Directly connected IPv4 static route to the Remote Branch WLAN user network, floating backup with AD 10.
ip route 192.168.10.0 255.255.255.0 GigabitEthernet0/0/2
ip route 192.168.10.0 255.255.255.0 Serial0/1/0 10

!--- Step 1e. Host routes to Server-O1: directly connected for IPv4, next hop for IPv6.
ip route 192.168.3.122 255.255.255.255 Serial0/1/1
ipv6 route 2001:db8:acad:3::122/128 2001:db8:acad:d::2

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip route static             -> S* 0.0.0.0/0 and S 192.168.10.0/24 via GigabitEthernet0/0/2; S 192.168.3.122/32 via Serial0/1/1
!---   show ipv6 route                  -> S ::/0 via 2001:DB8:ACAD:A::2; S 2001:DB8:ACAD:3::122/128 via 2001:DB8:ACAD:D::2
!--- Note: the floating routes (AD 10) appear in the routing table only when the Ethernet link is down.
! ==============================================================
ROUTER Branch-101
! ==============================================================
!--- SRWE Practice Packet Tracer Assessment - Part 2 - ID 1
!--- ANSWER SCRIPT FOR ROUTER Branch-101
!--- Usage: copy this whole file and paste it into the Branch-101 terminal (start at the Branch-101> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2: Configure Addressing and DHCP.
! --------------------------------------------------------------

!--- Step 1. Subinterface 10 on G0/0/0 (to S4-1): router-on-a-stick for VLAN 10 with the address from the Addressing Table.
interface gigabitethernet 0/0/0.10
 description Gateway for VLAN 10 (WLAN users)
 encapsulation dot1q 10
 ip address 192.168.10.1 255.255.255.0
 exit

!--- Step 2a. Exclude the router interface address and the WLC address.
ip dhcp excluded-address 192.168.10.1
ip dhcp excluded-address 192.168.10.254

!--- Step 2b. DHCP pool WLAN-hosts: 192.168.10.0/24, default gateway and DNS server.
ip dhcp pool WLAN-hosts
 network 192.168.10.0 255.255.255.0
 default-router 192.168.10.1
 dns-server 198.51.100.163
 exit

!--- Step 3. G0/0/1 (to ISP Router) receives its address over DHCP.
interface gigabitethernet 0/0/1
 ip address dhcp
 exit

! --------------------------------------------------------------
!--- Part 3: Configure Static Routes.
! --------------------------------------------------------------

!--- Step 2a. IPv4 default route through the Ethernet link (exit interface), floating backup through the serial link with AD 10.
ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/1
ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10

!--- Step 2b. Route IPv6.
ipv6 unicast-routing

!--- Step 2c. IPv6 default route to the ISP Router (next hop), floating backup to Central over the serial link with AD 10.
ipv6 route ::/0 2001:db8:acad:c::1
ipv6 route ::/0 2001:db8:acad:b::1 10

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief          -> G0/0/0.10 192.168.10.1; G0/0/1 address learned by DHCP
!---   show ip dhcp pool                -> pool WLAN-hosts, 192.168.10.0/24
!---   show ip route static             -> S* 0.0.0.0/0 via GigabitEthernet0/0/1
!---   show ipv6 route                  -> S ::/0 via 2001:DB8:ACAD:C::1
! ==============================================================
SWITCH S1-1
! ==============================================================
!--- SRWE Practice Packet Tracer Assessment - Part 2 - ID 1
!--- ANSWER SCRIPT FOR SWITCH S1-1
!--- Usage: copy this whole file and paste it into the S1-1 terminal (start at the S1-1> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1: Configure Switch Security.
! --------------------------------------------------------------

!--- Step 1a. VLAN 10 with name users.
vlan 10
 name users
 exit

!--- Step 1b. VLAN 999 with name unused.
vlan 999
 name unused
 exit

!--- Step 2a. F0/1-5 and G0/1 as static access ports in VLAN 10.
interface range fastethernet 0/1 - 5, gigabitethernet 0/1
 switchport mode access
 switchport access vlan 10
 exit

!--- Step 2b. Port security on the active ports: maximum 4 MAC addresses, restrict on violation (drop, log, alert), 10-minute aging, sticky learning.
interface range fastethernet 0/1 - 5
 switchport port-security
 switchport port-security maximum 4
 switchport port-security violation restrict
 switchport port-security aging time 10
 switchport port-security mac-address sticky
 exit

!--- Step 2b-5. MAC address of PC-A as a static secure address on F0/1.
interface fastethernet 0/1
 switchport port-security mac-address 00D0.D3DC.2825
 exit

!--- Step 2c-1/2. DHCP snooping globally and for VLANs 10 and 999.
ip dhcp snooping
ip dhcp snooping vlan 10,999

!--- Step 2c-3. Limit the active ports to 5 DHCP packets per second.
interface range fastethernet 0/1 - 5, gigabitethernet 0/1
 ip dhcp snooping limit rate 5
 exit

!--- Step 2c-4. The port that links to the router is trusted for DHCP snooping.
interface gigabitethernet 0/1
 ip dhcp snooping trust
 exit

!--- Step 2d-1/2. DAI on VLANs 10 and 999.
ip arp inspection vlan 10,999

!--- Step 2d-3. The port that links to the router is trusted for DAI.
interface gigabitethernet 0/1
 ip arp inspection trust
 exit

!--- Step 2e. PortFast and BPDU guard on the active ports.
interface range fastethernet 0/1 - 5
 spanning-tree portfast
 spanning-tree bpduguard enable
 exit

!--- Step 3. All unused ports: VLAN 999, static access, shut down.
interface range fastethernet 0/6 - 24, gigabitethernet 0/2
 switchport access vlan 999
 switchport mode access
 shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show vlan brief                  -> F0/1-5, G0/1 in VLAN 10 (users); F0/6-24, G0/2 in VLAN 999 (unused)
!---   show port-security               -> F0/1-5: max 4, violation Restrict
!---   show ip dhcp snooping            -> enabled on VLANs 10,999; G0/1 trusted; rate limit 5
!---   show ip arp inspection           -> enabled on VLANs 10,999
! ==============================================================
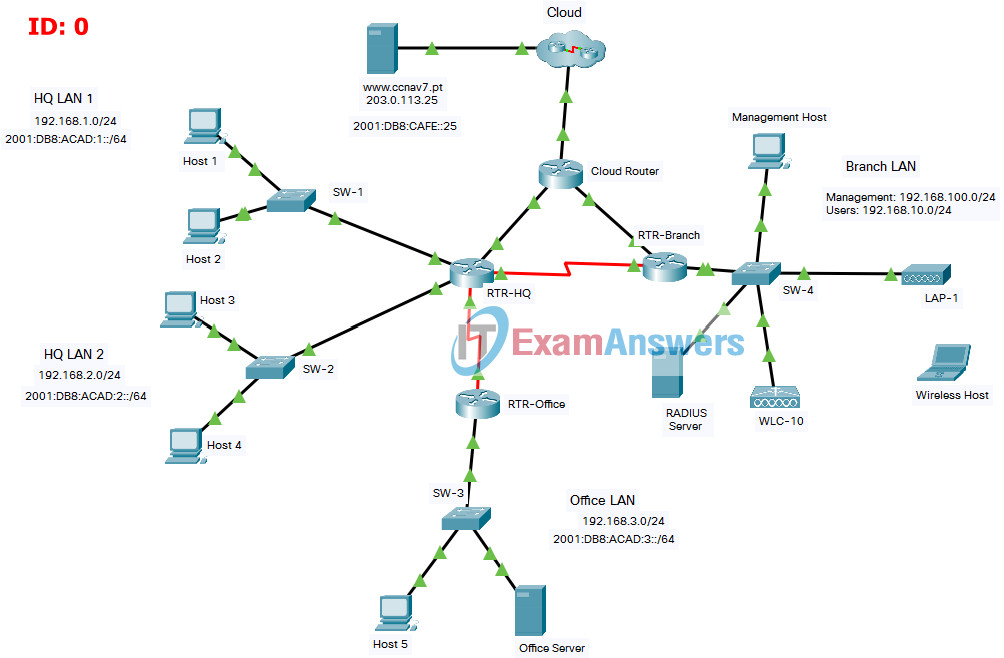
SRWE Practice PT Skills Assessment (PTSA) - Part 2 ID 0
SRWE Practice Packet Tracer Assessment - Part 2
A few things to keep in mind while completing this activity:
- Do not use the browser Back button or close or reload any exam windows during the exam.
- Do not close Packet Tracer when you are done. It will close automatically.
- Click the Submit Assessment button in the browser window to submit your work.
Addressing Table
| Device | Interface | Address and Prefix |
|---|---|---|
| RTR-HQ | G0/0/0 | 192.168.1.1/24 |
| 2001:db8:acad:1::1/64 | ||
| fe80::1 | ||
| G0/0/1 | 192.168.2.1/24 | |
| 2001:db8:acad:2::1/64 | ||
| fe80::1 | ||
| G0/0/2 | 10.1.0.1/30 | |
| 2001:db8:acad:a::1/64 | ||
| fe80::2 | ||
| S0/1/0 | 10.2.0.1/30 | |
| 2001:db8:acad:b::1/64 | ||
| fe80::2 | ||
| S0/1/1 | 10.4.0.1/30 | |
| 2001:db8:acad:d::1/64 | ||
| RTR-Office | S0/1/1 | 10.4.0.2/30 |
| 2001:db8:acad:d::2/64 | ||
| fe80::2 | ||
| G0/0/0 | 192.168.3.1/24 | |
| 2001:db8:acad:3::1/64 | ||
| fe80::1 | ||
| RTR-Branch | G0/0/0.10 | 192.168.10.1/24 |
| G0/0/0.100 | 192.168.100.1/24 | |
| G0/0/0.172 | 172.16.1.1/24 | |
| G0/0/1 | DHCP | |
| 2001:db8:acad:c::2/64 | ||
| S0/1/0 | 10.2.0.2/30 | |
| 2001:db8:acad:b::2/64 | ||
| Cloud Router | G0/0/0 | 10.1.0.2/24 |
| 2001:DB8:ACAD:A::2/64 | ||
| G0/0/1 | 10.3.0.1/24 | |
| 2001:DB8:ACAD:C::1/64 | ||
| WLC-10 | management | 192.168.100.254 |
| WLAN 10 | 192.168.10.254/24 | |
| Office Server | NIC | 192.168.3.122 |
| 2001:db8:acad:3::122 | ||
| Web Server | NIC | 203.0.113.25 |
| 2001:db8:acad:cafe:25 | ||
| DNS Server | NIC | 198.51.100.163 |
| 2001:DB8:face::163 | ||
| Management Host (Admin PC) | NIC | 192.168.100.23 |
| Wireless Host | NIC | DHCP |
| RADIUS server | NIC | 172.16.1.100/24 |
| Host 1 | NIC | 192.168.1.10/24 |
| 2001:db8:acad:1::10/64 | ||
| Host 2 | NIC | 192.168.1.11/24 |
| 2001:db8:acad:1::11/64 | ||
| Host 3 | NIC | 192.168.2.20/24 |
| 2001:db8:acad:2::20/64 | ||
| Host 4 | NIC | 192.168.2.21/24 |
| 2001:db8:acad:2::21/64 | ||
| Host 5 | NIC | 192.168.3.30/24 |
| 2001:db8:acad:3::30/64 |
Objectives
In this assessment, you will configure the following:
- Floating static and default routes in IPv4 and IPv6.
- Host routes in IPv4 and IPv6.
- DHCP pools and scopes.
- Switch security including port security.
- Enhanced LAN security with DHCP snooping, dynamic ARP inspection, PortFast, and BPDU guard.
- Wireless LAN Controller-based wireless LAN with enterprise authentication.
You will only configure the RTR-HQ and RTR-Branch routers, the SW-1 switch, and the WLC-10 wireless LAN controller. Access to other devices is not available.
Background / Scenario
XYZ Corp. is reworking their network. You have been asked to prototype the network in Packet Tracer for evaluation by senior network staff.
Instructions
Part 1: Configure Switch Security
In this part of the assessment you will configure switch SW-1 with switch security features. Switch ports FastEthernet0/1 to FastEthernet0/5 are the active switch ports. Port GigabitEthernet0/1 is a dedicated link to router RTR-HQ. All other ports should be secured.
Step 1: Configure VLANs
a. Configure VLAN 10 with name users.
SW-1(config)# vlan 10
SW-1(config-vlan)# name users
b. Configure VLAN 999 with the name unused.
SW-1(config-vlan)# vlan 999
SW-1(config-vlan)# name unused
Step 2: Configure active switch ports.
On the active switch ports configure the following:
a. Configure FastEthernet 0/1 through 0/5 and GigabitEthernet 0/1 as static access ports in VLAN 10.
SW-1(config)# interface range fastethernet 0/1 - 5, gigabitethernet 0/1
SW-1(config-if-range)# switchport mode access
SW-1(config-if-range)# switchport access vlan 10
b. Activate port security on the ports.
SW-1(config)# interface range fastethernet 0/1 - 5
SW-1(config-if-range)# switchport port-security
- Configure the active ports to accept a maximum of 4 MAC addresses.
SW-1(config-if-range)# switchport port-security maximum 4
- If a violation occurs, configure the ports to drop frames from the unauthorized MAC address, log it, and send an alert.
SW-1(config-if-range)# switchport port-security violation restrict
- MAC addresses should be present in the MAC address table for a maximum of 10 minutes before they are removed.
SW-1(config-if-range)# switchport port-security aging time 10
- Ports should add the learned MAC addresses to the running configuration.
SW-1(config-if-range)# switchport port-security mac-address sticky
- Configure the MAC address of Host 1 as a static address on port FastEthernet0/1.
SW-1(config)# interface fastethernet 0/1
SW-1(config-if)# switchport port-security mac-address 00D0.D3DC.2825
c. Protect against DHCP snooping.
Note: In this simulated network, DHCP snooping may not operate correctly in Packet Tracer. Configure it as you would normally. You will receive full credit for a configuration that meets the requirements below.
- Activate DHCP snooping globally.
SW-1(config)# ip dhcp snooping
- Activate DHCP snooping for the two VLANs that you configured.
SW-1(config)# ip dhcp snooping vlan 10,999
- Configure the ports to limit the rate to 5 DHCP packets per second.
SW-1(config)# interface range fastethernet 0/1 - 5, gigabitethernet 0/1
SW-1(config-if-range)# ip dhcp snooping limit rate 5
- Configure the port that links to the router as trusted.
SW-1(config)# interface gigabitethernet 0/1
SW-1(config-if)# ip dhcp snooping trust
d. Guard against ARP attacks by implementing DAI.
- Activate DAI globally.
- Activate DAI on the two VLANs.
SW-1(config)# ip arp inspection vlan 10,999
- Configure the port that links to the router as trusted.
SW-1(config)# interface gigabitethernet 0/1
SW-1(config-if)# ip arp inspection trust
e. Mitigate STP attacks by configuring BPDUguard and PortFast on the active ports.
SW-1(config)# interface range fastethernet 0/1 - 5
SW-1(config-if-range)# spanning-tree portfast
SW-1(config-if-range)# spanning-tree bpduguard enable
Step 3: Secure unused switch ports.
a. Move all unused switch ports to VLAN 999.
SW-1(config)# interface range fastethernet 0/6 - 24, gigabitethernet 0/2
SW-1(config-if-range)# switchport access vlan 999
b. Configure all unused switch ports as static access ports.
SW-1(config-if-range)# switchport mode access
c. Deactivate all unused switch ports.
SW-1(config-if-range)# shutdown
Part 2: Configure Addressing and DHCP
You will configure DHCP and interface addressing on router RTR-Branch to prepare for implementing the wireless LAN controller network.
Step 1: Configure and address a subinterface for the WLAN user network.
a. Configure subinterface 10 on the router interface that is connected to the switch S4-1.
RTR-Branch(config)# interface gigabitethernet 0/0/0.10
RTR-Branch(config-subif)# description Gateway for VLAN 10 (WLAN users)
b. The router should provide router-on-a-stick routing to VLAN 10.
RTR-Branch(config-subif)# encapsulation dot1q 10
c. Configure the subinterface with the address from the Addressing Table.
RTR-Branch(config-subif)# ip address 192.168.10.1 255.255.255.0
Step 2: Configure a DHCP pool for WLAN user network.
a. Exclude the router interface address and the management address of the WLC.
RTR-Branch(config)# ip dhcp excluded-address 192.168.10.1
RTR-Branch(config)# ip dhcp excluded-address 192.168.10.254
b. Configure a DHCP pool that will be used by hosts that are connecting to the WLAN.
- Name the pool WLAN-hosts.
RTR-Branch(config)# ip dhcp pool WLAN-hosts
- Configure the pool to use addresses in the 192.168.10.0/24 network.
RTR-Branch(dhcp-config)# network 192.168.10.0 255.255.255.0
- The pool should also provide the default gateway and DNS server addresses.
RTR-Branch(dhcp-config)# default-router 192.168.10.1
RTR-Branch(dhcp-config)# dns-server 198.51.100.163
Step 3: Configure an interface as a DHCP client.
On RTR-Branch, configure the interface that is connected to Cloud Router to receive its address over DHCP.
RTR-Branch(config)# interface gigabitethernet 0/0/1
RTR-Branch(config-if)# ip address dhcp
Part 3: Configure Static Routes
In this part of the assessment you will configure static, default, floating static, and host routes in both IPv4 and IPv6. You will configure the RTR-HQ and RTR-Branch routers. XYZ Corp. has decided that it wants to use static routing between all its networks. In addition, the company wants to use the Ethernet links between routers for most data traffic and reserve serial link between RTR-HQ and RTR-Branch for backup purposes in case one of the Ethernet links becomes unavailable. You will be configuring floating static and default routes.
Step 1: Configure static routes on RTR-HQ.
a. Configure IPv4 default routes to the cloud using the Ethernet link as the preferred link and the serial link as the floating backup. Use an administrative distance of 10 for the backup route. These routes should be configured as directly connected routes.
Note: Ethernet interfaces will give a warning when configured without a next-hop address. In this configuration, the interface is point-to-point, so the warning can be ignored.
RTR-HQ(config)# ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/2
RTR-HQ(config)# ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10
b. Ensure that the device is configured to route IPv6.
RTR-HQ(config)# ipv6 unicast-routing
c. Configure IPv6 default routes to the cloud. Use the Ethernet link as the primary route, and the serial link as the floating backup. Use an administrative distance of 10 for the backup route. These routes should specify the next hop interface address.
RTR-HQ(config)# ipv6 route ::/0 2001:db8:acad:a::2
RTR-HQ(config)# ipv6 route ::/0 2001:db8:acad:b::2 10
d. Configure IPv4 static routes to the Branch LAN WLAN user network following the same guidelines as above for type of route and administrative distance.
RTR-HQ(config)# ip route 192.168.10.0 255.255.255.0 GigabitEthernet0/0/2
RTR-HQ(config)# ip route 192.168.10.0 255.255.255.0 Serial0/1/0 10
e. Configure IPv4 and IPv6 host routes on RTR-HQ to the Office Server on the Office LAN. Create a directly connected route for IPv4 and a next-hop route for IPv6.
RTR-HQ(config)# ip route 192.168.3.122 255.255.255.255 Serial0/1/1
RTR-HQ(config)# ipv6 route 2001:db8:acad:3::122/128 2001:db8:acad:d::2
Step 2: Configure static routes on RTR-Branch.
RTR-Branch must also be configured with static routes to the other three networks in the XYZ Corp. network. It will require floating static and default routes in IPv4 and IPv6 following the same guidelines as were used for the RTR-HQ static routes.
- IPv6 routes use next-hop address arguments.
- IPv4 routes use exit interface arguments.
- All routes should prefer the Ethernet links over the serial link.
- Backup floating routes use an administrative distance of 10.
a. Configure IPv4 default routes to the cloud using the Ethernet link as the preferred link and the serial link as the backup.
RTR-Branch(config)# ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/1
RTR-Branch(config)# ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10
b. Ensure that the device is configured to route IPv6.
RTR-Branch(config)# ipv6 unicast-routing
c. Configure IPv6 default routes to the cloud. Use the Ethernet link as the primary route, and the serial link as backup. Use an administrative distance of 10 for the backup route. These routes should specify the next hop interface address.
RTR-Branch(config)# ipv6 route ::/0 2001:db8:acad:c::1
RTR-Branch(config)# ipv6 route ::/0 2001:db8:acad:b::1 10
Part 4: Configure a Wireless LAN using a Wireless LAN Controller
In this part of the assessment, you will configure the wireless LAN controller to provide wireless access to the network. Username and password are the default admin/admin. Connect to the WLC over HTTPS to the management interface.
Click Management Host (Admin PC), open the Desktop tab, then Web Browser, and go to the WLC management address over HTTPS: https://192.168.100.254
Log in with the username admin and the password admin.
Step 1: Configure a VLAN interface.
a. Create a new interface and name it WLAN 10. The interface should use VLAN 10 and physical port 1.
Go to CONTROLLER > Interfaces and click New....
On the Interfaces > New page, enter WLAN 10 in the Interface Name box and 10 in the VLAN Id box, then click Apply.
b. Use the information in the addressing table to configure the addressing settings for the interface. The interface will be using a DHCP pool that is configured on the subinterface that is assigned to VLAN 10 on router RTR-Branch.
Go back to CONTROLLER > Interfaces and click the WLAN 10 interface you just created.
Enter the values from the table below in the matching fields, then click Apply.
| Setting | Value |
|---|---|
| Port Number | 1 |
| VLAN Identifier | 10 |
| IP Address | 192.168.10.254 |
| Netmask | 255.255.255.0 |
| Gateway | 192.168.10.1 |
| Primary DHCP Server | 192.168.10.1 |
Step 2: Configure a RADIUS server.
a. Configure the WLC with the RADIUS server IPv4 address.
b. Use a shared secret of RADsecret.
Go to SECURITY > RADIUS > Authentication and click New....
On the RADIUS Authentication Servers > New page, enter the values from the table below, then click Apply.
| Setting | Value |
|---|---|
| Server IP Address | 172.16.1.100 |
| Shared Secret | RADsecret |
| Confirm Shared Secret | RADsecret |
Step 3: Configure a Wireless LAN.
a. Create a new WLAN. Name it WLAN 10 and configure the SSID as SSID-10.
Go to the WLANs menu, select Create New from the drop-down list and click Go.
On the WLANs > New page, enter WLAN 10 as the Profile Name and SSID-10 as the SSID, select 10 in the ID list, then click Apply.
b. The wireless LAN should use the VLAN interface that was previously configured.
On the WLANs > Edit 'WLAN 10' page, General tab, check Enabled next to Status, select WLAN 10 in the Interface/Interface Group(G) list, then click Apply.
c. Configure the WLAN to use the WPA2 security policy and dot1x Authentication Key Management.
Open the Security tab, then the Layer 2 tab. Set Layer 2 Security to WPA+WPA2, check WPA2 Policy (with AES encryption), and under Authentication Key Management check Enable next to 802.1X.
d. Configure the WLAN to use the RADIUS server that was previously configured to authenticate wireless users.
Open the AAA Servers tab. Under Server 1, select IP:172.16.1.100, Port:1812.
e. Open the Advanced tab and scroll down to the Flexconnect sections. Activate FlexConnect Local Switching and FlexConnect Local Auth.
Open the Advanced tab and scroll down to the FlexConnect section. Check Enabled for both FlexConnect Local Switching and FlexConnect Local Auth, then click Apply.
f. Verify that the WLAN is configured and operational.
Go back to the WLANs page and check that WLAN 10 (SSID SSID-10) is listed with an Admin Status of Enabled.
Step 4: Configure a DHCP scope for the management network.
Configure a new DHCP scope to be used by the LAPs and other management devices on the network.
a. Name the DHCP scope Wired_Admin.
Go to CONTROLLER, expand Internal DHCP Server, click DHCP Scope, then click New....
On the DHCP Scope > New page, enter Wired_Admin as the Scope Name, then click Apply.
b. Start the scope at address 192.168.100.240. End the scope at address 192.168.100.249.
Click the Wired_Admin scope you just created.
On the DHCP Scope > Edit page, enter the values from the table below, then click Apply.
| Setting | Value |
|---|---|
| Scope Name | Wired_Admin |
| Pool Start Address | 192.168.100.240 |
| Pool End Address | 192.168.100.249 |
| Network | 192.168.100.0 |
| Netmask | 255.255.255.0 |
| Default Routers | 192.168.100.1 |
c. Other information that is required can be found in the Addressing Table.
Step 5: Configure an SNMP server.
Configure an SNMP server to receive traps from the WLC.
a. Use the community name branch-wireless.
b. Use 172.16.1.100 as the server address.
Go to MANAGEMENT, expand SNMP, click Trap Receivers, then click New....
On the SNMP Trap Receiver > New page, enter branch-wireless as the Community Name and 172.16.1.100 as the IP Address(Ipv4/Ipv6), then click Apply.
Click Save Configuration at the top-right of the page to save all WLC settings.
Step 6: Configure the wireless host.
Configure the LT-1 laptop to connect to the WLAN.
a. Create a new wireless profile on the host. Use the name work net for the profile.
Click the LT-1 laptop, open the Desktop tab, then click PC Wireless. On the Profiles tab, click New and enter work net as the profile name.
b. Configure the profile for the SSID of the WLAN.
c. Use enterprise authentication with a username of user1 and password of user1Pass.
d. When you are finished, click Connect to Network. It will take time for the connection to be established.
Result
Click Fast Forward Time to speed up the process.
Device Configs - Final
ROUTER RTR-HQ
! ==============================================================
!--- SRWE Practice Packet Tracer Assessment - Part 2 - ID 0
!--- ANSWER SCRIPT FOR ROUTER RTR-HQ
!--- Usage: copy this whole file and paste it into the RTR-HQ terminal (start at the RTR-HQ> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: Configure Static Routes.
! --------------------------------------------------------------

!--- Step 1a. Directly connected IPv4 default route through the Ethernet link, floating backup through the serial link with AD 10.
ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/2
ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10

!--- Step 1b. Route IPv6.
ipv6 unicast-routing

!--- Step 1c. IPv6 default route to the Cloud Router (next hop), floating backup to RTR-Branch over the serial link with AD 10.
ipv6 route ::/0 2001:db8:acad:a::2
ipv6 route ::/0 2001:db8:acad:b::2 10

!--- Step 1d. Directly connected IPv4 static route to the Branch WLAN user network, floating backup with AD 10.
ip route 192.168.10.0 255.255.255.0 GigabitEthernet0/0/2
ip route 192.168.10.0 255.255.255.0 Serial0/1/0 10

!--- Step 1e. Host routes to Office Server: directly connected for IPv4, next hop for IPv6.
ip route 192.168.3.122 255.255.255.255 Serial0/1/1
ipv6 route 2001:db8:acad:3::122/128 2001:db8:acad:d::2

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip route static             -> S* 0.0.0.0/0 and S 192.168.10.0/24 via GigabitEthernet0/0/2; S 192.168.3.122/32 via Serial0/1/1
!---   show ipv6 route                  -> S ::/0 via 2001:DB8:ACAD:A::2; S 2001:DB8:ACAD:3::122/128 via 2001:DB8:ACAD:D::2
!--- Note: the floating routes (AD 10) appear in the routing table only when the Ethernet link is down.
! ==============================================================
ROUTER RTR-Branch
! ==============================================================
!--- SRWE Practice Packet Tracer Assessment - Part 2 - ID 0
!--- ANSWER SCRIPT FOR ROUTER RTR-Branch
!--- Usage: copy this whole file and paste it into the RTR-Branch terminal (start at the RTR-Branch> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2: Configure Addressing and DHCP.
! --------------------------------------------------------------

!--- Step 1. Subinterface 10 on G0/0/0 (to S4-1): router-on-a-stick for VLAN 10 with the address from the Addressing Table.
interface gigabitethernet 0/0/0.10
 description Gateway for VLAN 10 (WLAN users)
 encapsulation dot1q 10
 ip address 192.168.10.1 255.255.255.0
 exit

!--- Step 2a. Exclude the router interface address and the WLC address.
ip dhcp excluded-address 192.168.10.1
ip dhcp excluded-address 192.168.10.254

!--- Step 2b. DHCP pool WLAN-hosts: 192.168.10.0/24, default gateway and DNS server.
ip dhcp pool WLAN-hosts
 network 192.168.10.0 255.255.255.0
 default-router 192.168.10.1
 dns-server 198.51.100.163
 exit

!--- Step 3. G0/0/1 (to Cloud Router) receives its address over DHCP.
interface gigabitethernet 0/0/1
 ip address dhcp
 exit

! --------------------------------------------------------------
!--- Part 3: Configure Static Routes.
! --------------------------------------------------------------

!--- Step 2a. IPv4 default route through the Ethernet link (exit interface), floating backup through the serial link with AD 10.
ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/1
ip route 0.0.0.0 0.0.0.0 Serial0/1/0 10

!--- Step 2b. Route IPv6.
ipv6 unicast-routing

!--- Step 2c. IPv6 default route to the Cloud Router (next hop), floating backup to RTR-HQ over the serial link with AD 10.
ipv6 route ::/0 2001:db8:acad:c::1
ipv6 route ::/0 2001:db8:acad:b::1 10

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief          -> G0/0/0.10 192.168.10.1; G0/0/1 address learned by DHCP
!---   show ip dhcp pool                -> pool WLAN-hosts, 192.168.10.0/24
!---   show ip route static             -> S* 0.0.0.0/0 via GigabitEthernet0/0/1
!---   show ipv6 route                  -> S ::/0 via 2001:DB8:ACAD:C::1
! ==============================================================
SWITCH SW-1
! ==============================================================
!--- SRWE Practice Packet Tracer Assessment - Part 2 - ID 0
!--- ANSWER SCRIPT FOR SWITCH SW-1
!--- Usage: copy this whole file and paste it into the SW-1 terminal (start at the SW-1> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1: Configure Switch Security.
! --------------------------------------------------------------

!--- Step 1a. VLAN 10 with name users.
vlan 10
 name users
 exit

!--- Step 1b. VLAN 999 with name unused.
vlan 999
 name unused
 exit

!--- Step 2a. F0/1-5 and G0/1 as static access ports in VLAN 10.
interface range fastethernet 0/1 - 5, gigabitethernet 0/1
 switchport mode access
 switchport access vlan 10
 exit

!--- Step 2b. Port security on the active ports: maximum 4 MAC addresses, restrict on violation (drop, log, alert), 10-minute aging, sticky learning.
interface range fastethernet 0/1 - 5
 switchport port-security
 switchport port-security maximum 4
 switchport port-security violation restrict
 switchport port-security aging time 10
 switchport port-security mac-address sticky
 exit

!--- Step 2b-5. MAC address of Host 1 as a static secure address on F0/1.
interface fastethernet 0/1
 switchport port-security mac-address 00D0.D3DC.2825
 exit

!--- Step 2c-1/2. DHCP snooping globally and for VLANs 10 and 999.
ip dhcp snooping
ip dhcp snooping vlan 10,999

!--- Step 2c-3. Limit the active ports to 5 DHCP packets per second.
interface range fastethernet 0/1 - 5, gigabitethernet 0/1
 ip dhcp snooping limit rate 5
 exit

!--- Step 2c-4. The port that links to the router is trusted for DHCP snooping.
interface gigabitethernet 0/1
 ip dhcp snooping trust
 exit

!--- Step 2d-1/2. DAI on VLANs 10 and 999.
ip arp inspection vlan 10,999

!--- Step 2d-3. The port that links to the router is trusted for DAI.
interface gigabitethernet 0/1
 ip arp inspection trust
 exit

!--- Step 2e. PortFast and BPDU guard on the active ports.
interface range fastethernet 0/1 - 5
 spanning-tree portfast
 spanning-tree bpduguard enable
 exit

!--- Step 3. All unused ports: VLAN 999, static access, shut down.
interface range fastethernet 0/6 - 24, gigabitethernet 0/2
 switchport access vlan 999
 switchport mode access
 shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show vlan brief                  -> F0/1-5, G0/1 in VLAN 10 (users); F0/6-24, G0/2 in VLAN 999 (unused)
!---   show port-security               -> F0/1-5: max 4, violation Restrict
!---   show ip dhcp snooping            -> enabled on VLANs 10,999; G0/1 trusted; rate limit 5
!---   show ip arp inspection           -> enabled on VLANs 10,999
! ==============================================================
Download PDF and Packet Tracer files:


