16.4.6 Packet Tracer - Configure Secure Passwords and SSH Answers
16.4.6 Packet Tracer - Configure Secure Passwords and SSH
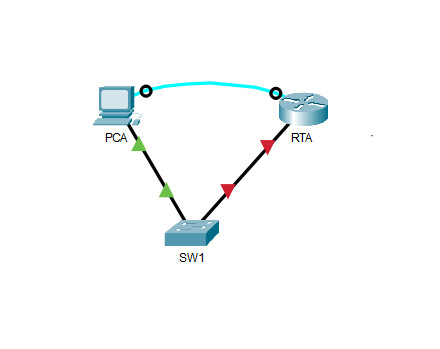
Addressing Table
| Device | Interface | IP Address | Subnet Mask | Default Gateway |
|---|---|---|---|---|
| RTA | G0/0 | 172.16.1.1 | 255.255.255.0 | N/A |
| PCA | NIC | 172.16.1.10 | 255.255.255.0 | 172.16.1.1 |
| SW1 | VLAN 1 | 172.16.1.2 | 255.255.255.0 | 172.16.1.1 |
Scenario
The network administrator has asked you to prepare RTA and SW1 for deployment. Before they can be connected to the network, security measures must be enabled.
Instructions
Step 1: Configure Basic Security on the Router
a. Configure IP addressing on PCA according to the Addressing Table.
b. Console into RTA from the Terminal on PCA.
c. Configure the hostname as RTA.
Router(config)# hostname RTA
d. Configure IP addressing on RTA and enable the interface.
RTA(config)# interface gigabitethernet 0/0
RTA(config-if)# ip address 172.16.1.1 255.255.255.0
RTA(config-if)# no shutdown
e. Encrypt all plaintext passwords.
RTA(config)# service password-encryption
f. Set the minimum password length to 10.
RTA(config)# security passwords min-length 10
g. Set a strong secret password of your choosing.
Note: Choose a password that you will remember, or you will need to reset the activity if you are locked out of the device.
RTA(config)# enable secret itexamanswers
h. Disable DNS lookup.
RTA(config)# no ip domain-lookup
i. Set the domain name to CCNA.com (case-sensitive for scoring in PT).
RTA(config)# ip domain-name CCNA.com
j. Create a user of your choosing with a strong encrypted password.
RTA(config)# username jony secret itexamanswers.net
k. Generate 1024-bit RSA keys.
Note: In Packet Tracer, enter the crypto key generate rsa command and press Enter to continue.
RTA(config)# crypto key generate rsa
The name for the keys will be: RTA.CCNA.com
Choose the size of the key modulus in the range of 360 to 2048 for your
   General Purpose Keys. Choosing a key modulus greater than 512 may take
   a few minutes.
How many bits in the modulus [512]: 1024
l. Block anyone for three minutes who fails to log in after four attempts within a two-minute period.
RTA(config)# login block-for 180 attempts 4 within 120
m. Configure all VTY lines for SSH access and use the local user profiles for authentication.
RTA(config)# line vty 0 4
RTA(config-line)# transport input ssh
RTA(config-line)# login local
n. Set the EXEC mode timeout to 6 minutes on the VTY lines.
RTA(config-line)# exec-timeout 6
o. Save the configuration to NVRAM.
RTA# copy running-config startup-config
p. Access the command prompt on the desktop of PCA to establish an SSH connection to RTA.
Note: Make sure PCA is configured with the IP address, subnet mask, and default gateway from the Addressing Table.
C:\> ssh /?
Packet Tracer PC SSH
Usage: SSH -l username target

C:\> ssh -l jony 172.16.1.1
Password: <~~ enter the user password (itexamanswers.net)

RTA>
Step 2: Configure Basic Security on the Switch
Configure switch SW1 with corresponding security measures. Refer to the configuration steps on the router if you need additional assistance.
a. Click on SW1 and select the CLI tab.
b. Configure the hostname as SW1.
Switch(config)# hostname SW1
c. Configure IP addressing on SW1 VLAN1 and enable the interface.
SW1(config)# interface vlan 1
SW1(config-if)# ip address 172.16.1.2 255.255.255.0
SW1(config-if)# no shutdown
d. Configure the default gateway address.
SW1(config)# ip default-gateway 172.16.1.1
e. Disable all unused switch ports.
Note: On a switch it is a good security practice to disable unused ports. One method of doing this is to simply shut down each port with the ‘shutdown’ command. This would require accessing each port individually. There is a shortcut method for making modifications to several ports at once by using the interface range command. On SW1 all ports except FastEthernet0/1 and GigabitEthernet0/1 can be shutdown with the following command:
SW1(config)# interface range fastethernet 0/2 - 24, gigabitethernet 0/2
SW1(config-if-range)# shutdown
%LINK-5-CHANGED: Interface FastEthernet0/2, changed state to administratively down

%LINK-5-CHANGED: Interface FastEthernet0/3, changed state to administratively down
<Output omitted>
%LINK-5-CHANGED: Interface FastEthernet0/24, changed state to administratively down

%LINK-5-CHANGED: Interface GigabitEthernet0/2, changed state to administratively down
The command used the port range of 2-24 for the FastEthernet ports and then a single port range of GigabitEthernet0/2.
f. Encrypt all plaintext passwords.
SW1(config)# service password-encryption
g. Set a strong secret password of your choosing.
SW1(config)# enable secret itexamanswers
h. Disable DNS lookup.
SW1(config)# no ip domain-lookup
i. Set the domain name to CCNA.com (case-sensitive for scoring in PT).
SW1(config)# ip domain-name CCNA.com
j. Create a user of your choosing with a strong encrypted password.
SW1(config)# username jony secret itexamanswers.net
k. Generate 1024-bit RSA keys.
SW1(config)# crypto key generate rsa general-keys modulus 1024
l. Configure all VTY lines for SSH access and use the local user profiles for authentication.
SW1(config)# line vty 0 15
SW1(config-line)# transport input ssh
SW1(config-line)# login local
m. Set the EXEC mode timeout to 6 minutes on all VTY lines.
SW1(config-line)# exec-timeout 6
n. Save the configuration to NVRAM.
SW1# copy running-config startup-config
Device Configs - Final
ROUTER RTA
! ==============================================================
!--- 16.4.6 Packet Tracer - Configure Secure Passwords and SSH
!--- ANSWER SCRIPT FOR ROUTER RTA
!--- Usage: on PCA open Desktop > Terminal (console to RTA), then paste this whole file at the Router> prompt. The passwords below are examples; the lab lets you choose your own. Every line beginning with "!" is a comment; IOS ignores it.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Step 1: Configure Basic Security on the Router.
! --------------------------------------------------------------

!--- Step 1c: Configure the hostname.
hostname RTA

!--- Step 1d: Configure the G0/0 IP address from the Addressing Table and enable the interface.
interface gigabitethernet 0/0
 ip address 172.16.1.1 255.255.255.0
 no shutdown
 exit

!--- Step 1e: Encrypt all plaintext passwords.
service password-encryption

!--- Step 1f: Require passwords of at least 10 characters (set this before the passwords below).
security passwords min-length 10

!--- Step 1g: Set a strong enable secret (13 characters, meets the 10-character minimum).
enable secret itexamanswers

!--- Step 1h: Disable DNS lookup so mistyped commands are not treated as host names.
no ip domain-lookup

!--- Step 1i: Set the domain name (case-sensitive for scoring in PT).
ip domain-name CCNA.com

!--- Step 1j: Create a local user with an encrypted (secret) password.
username jony secret itexamanswers.net

!--- Step 1k: Generate 1024-bit RSA keys (one line, no prompt). This enables SSH.
crypto key generate rsa general-keys modulus 1024

!--- Step 1l: Block logins for 180 seconds after 4 failed attempts within 120 seconds.
login block-for 180 attempts 4 within 120

!--- Steps 1m and 1n: VTY lines accept SSH only, authenticate with the local user, and time out after 6 minutes.
line vty 0 4
 transport input ssh
 login local
 exec-timeout 6
 exit

end

! --------------------------------------------------------------
!--- Step 1o: Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip ssh                  -> SSH Enabled - version 1.99, key size 1024
!---   show run | section line vty  -> transport input ssh, login local, exec-timeout 6 0
!---   From PCA: ssh -l jony 172.16.1.1 (password itexamanswers.net) -> RTA>
! ==============================================================
SWITCH SW1
! ==============================================================
!--- 16.4.6 Packet Tracer - Configure Secure Passwords and SSH
!--- ANSWER SCRIPT FOR SWITCH SW1
!--- Usage: click SW1 > CLI tab, then paste this whole file at the Switch> prompt. The passwords below are examples; the lab lets you choose your own. Every line beginning with "!" is a comment; IOS ignores it.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Step 2: Configure Basic Security on the Switch.
! --------------------------------------------------------------

!--- Step 2b: Configure the hostname.
hostname SW1

!--- Step 2c: Configure the VLAN 1 management address and enable the interface.
interface vlan 1
 ip address 172.16.1.2 255.255.255.0
 no shutdown
 exit

!--- Step 2d: Configure the default gateway (RTA G0/0) so the switch can be managed from other networks.
ip default-gateway 172.16.1.1

!--- Step 2e: Shut down every unused port. Only F0/1 and G0/1 are in use.
interface range fastethernet 0/2 - 24, gigabitethernet 0/2
 shutdown
 exit

!--- Step 2f: Encrypt all plaintext passwords.
service password-encryption

!--- Step 2g: Set a strong enable secret.
enable secret itexamanswers

!--- Step 2h: Disable DNS lookup.
no ip domain-lookup

!--- Step 2i: Set the domain name (case-sensitive for scoring in PT).
ip domain-name CCNA.com

!--- Step 2j: Create a local user with an encrypted (secret) password.
username jony secret itexamanswers.net

!--- Step 2k: Generate 1024-bit RSA keys (one line, no prompt). This enables SSH.
crypto key generate rsa general-keys modulus 1024

!--- Steps 2l and 2m: all 16 VTY lines accept SSH only, authenticate with the local user, and time out after 6 minutes.
line vty 0 15
 transport input ssh
 login local
 exec-timeout 6
 exit

end

! --------------------------------------------------------------
!--- Step 2n: Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip ssh              -> SSH Enabled, key size 1024
!---   show ip interface brief  -> Vlan1 172.16.1.2 up/up; F0/2-24 and G0/2 administratively down
!---   From PCA: ssh -l jony 172.16.1.2 (password itexamanswers.net) -> SW1>
! ==============================================================
PC PCA
Download Packet Tracer (.pka) file:


