How to find: Press "Ctrl + F" in the browser and fill in whatever wording is in the question to find that questio are two types of attacks used on DNS open resolvers? (Choose n/answer.
CCNA 3 v7: Enterprise Networking, Security, and Automation Course Final Exam Answers
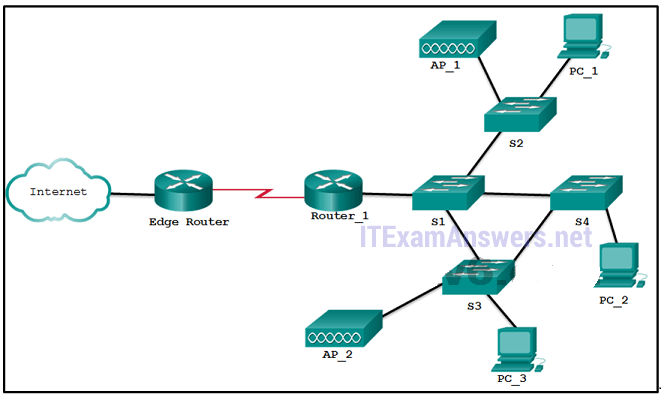
1. Which design feature will limit the size of a failure domain in an enterprise network?
the purchase of enterprise equipment that is designed for large traffic volume
the installation of redundant power supplies
the use of a collapsed core design
the use of the building switch block approach
Explanation: Topic 11.2.3
In order to best limit the of a failure domain, routers or multilayer switches can be deployed in pairs. The failure of a single device should not cause the network to go down. Installing redundant power supplies may protect a single device from a power failure, but if that device suffers from another type of problem, a redundant device would have been a better solution. Purchasing enterprise equipment that handles large flows of traffic will not provide extra reliability in times of an outage. If a collapsed core design is used, the core and distribution are collapsed into a single device, increasing the chance of a devastating outage.
2. Which two things should a network administrator modify on a router to perform password recovery? (Choose two.)
the system image file
the NVRAM file system
the configuration register value
the startup configuration file
system ROM
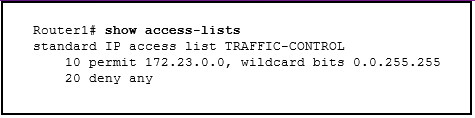
Explanation: Topic 10.6.8
To perform password recovery, the administrator must first change the configuration register value (typically to 0x2142) while in ROMMON mode. This setting instructs the router to ignore the startup configuration file during the boot process, allowing access to the device without a password. Once the router has loaded, the administrator copies the original configuration into RAM, sets a new password, and then modifies the startup configuration file by saving the new settings to ensure the recovery is permanent.
3. What type of network uses one common infrastructure to carry voice, data, and video signals?
borderless
converged
managed
switched
Explanation: Topic 11.1.2
A converged network has only one physical network to install and manage. This results in substantial savings over the installation and management of separate voice, video, and data networks.
4. What are three advantages of using private IP addresses and NAT? (Choose three.)
hides private LAN addressing from outside devices that are connected to the Internet
permits LAN expansion without additional public IP addresses
reduces CPU usage on customer routers
creates multiple public IP addresses
improves the performance of the router that is connected to the Internet
conserves registered public IP addresses
Explanation: Topic 6.3.1
Private IP addresses are designed to be exclusively used for internal networks and they cannot be used on the Internet. Thus they are not visible directly from the Internet and they can be used freely by network administrators for internal networks. In order for the internal hosts to access the Internet, NAT is used to translate between private and public IP addresses. NAT takes an internal private IP address and translates it to a global public IP address before the packet is forwarded.
5. Which two scenarios are examples of remote access VPNs? (Choose two.)
All users at a large branch office can access company resources through a single VPN connection.
A small branch office with three employees has a Cisco ASA that is used to create a VPN connection to the HQ.
A toy manufacturer has a permanent VPN connection to one of its parts suppliers.
A mobile sales agent is connecting to the company network via the Internet connection at a hotel.
An employee who is working from home uses VPN client software on a laptop in order to connect to the company network.
Explanation: Topic 8.2.1
Remote access VPNs connect individual users to another network via a VPN client that is installed on the user device. Site-to-site VPNs are “always on” connections that use VPN gateways to connect two sites together. Users at each site can access the network on the other site without having to use any special clients or configurations on their individual devices.
6. What are three benefits of cloud computing? (Choose three.)
It utilizes end-user clients to do a substantial amount of data preprocessing and storage.
It uses open-source software for distributed processing of large datasets.
It streamlines the IT operations of an organization by subscribing only to needed services.
It enables access to organizational data anywhere and at any time.
It turns raw data into meaningful information by discovering patterns and relationships.
It eliminates or reduces the need for onsite IT equipment, maintenance, and management.
Explanation: Topic 13.1.2
There are many benefits to using cloud computing, including these:
– Access to organizational data anywhere and at any time
– Streamlined IT operations in an organization by subscribing only to needed services
– Elimination or reduction of the need for onsite IT equipment, maintenance, and management
7. What is a characteristic of a single-area OSPF network?
All routers share a common forwarding database.
All routers have the same neighbor table.
All routers are in the backbone area.
All routers have the same routing table.
Explanation: Topic 1.1.4
In a single-area OSPF implementation, all participating routers are located within one administrative area. Best practice dictates that this single area should be Area 0, also known as the backbone area. This ensures that if the network scales to a multiarea design in the future, all other areas can connect directly to this required backbone. While routers in the same area share an identical Link-State Database (topology table), their neighbor tables and routing tables (forwarding databases) are unique to each individual router based on its specific location and adjacencies.
8. What is a WAN?
a network infrastructure that spans a limited physical area such as a city
a network infrastructure that provides access to other networks over a large geographic area
a network infrastructure that provides access in a small geographic area
a network infrastructure designed to provide data storage, retrieval, and replication
Explanation: Topic 7.1.1
A Wide Area Network (WAN) is a telecommunications network designed to span a relatively large geographical area, such as between cities, countries, or continents. Unlike a Local Area Network (LAN), which is restricted to a small area like a single building or campus, a WAN is used to interconnect remote users, networks, and sites that are geographically separated.
9. A network administrator has been tasked with creating a disaster recovery plan. As part of this plan, the administrator is looking for a backup site for all of the data on the company servers. What service or technology would support this requirement?
data center
virtualization
dedicated servers
software defined networking
Explanation: Topic 7.1.1
A data center is a dedicated facility used for the storage and processing of data, which can be managed by an in-house IT department or leased from an offsite provider. Because data centers provide the physical infrastructure for compute and storage needs, they serve as the primary backup site for disaster recovery plans, especially for smaller organizations that lease these services to reduce the cost of ownership. While virtualization is a technology used to improve disaster recovery, the data center is the actual service or facility that supports the requirement for a physical backup site.
10. Which type of OSPF packet is used by a router to discover neighbor routers and establish neighbor adjacency?
link-state update
hello
database description
link-state request
Explanation: Topic 1.2.4
The Hello packet (OSPF Type 1) is specifically used to discover neighbors and establish neighbor adjacencies between OSPF routers. These packets are sent out of OSPF-enabled interfaces to identify neighboring routers and to advertise parameters that both routers must agree upon before sharing routing information.
11. Which two statements are characteristics of a virus? (Choose two.)
A virus has an enabling vulnerability, a propagation mechanism, and a payload.
A virus can be dormant and then activate at a specific time or date.
A virus provides the attacker with sensitive data, such as passwords.
A virus replicates itself by independently exploiting vulnerabilities in networks.
A virus typically requires end-user activation.
Explanation: Topic 3.4.2
The type of end user interaction required to launch a virus is typically opening an application, opening a web page, or powering on the computer. Once activated, a virus may infect other files located on the computer or other computers on the same network.
12. Which public WAN access technology utilizes copper telephone lines to provide access to subscribers that are multiplexed into a single T3 link connection?
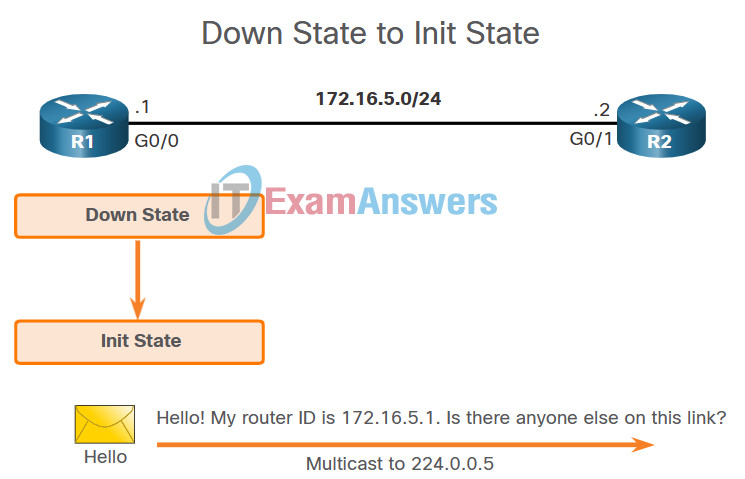
ISDN
DSL
cable
dialup
Explanation: Topic 7.5.3 Digital Subscriber Line (DSL) is a high-speed WAN technology that utilizes existing twisted-pair copper telephone lines. In a typical deployment, the provider uses a DSL Access Multiplexer (DSLAM) at the Central Office to concentrate and multiplex signals from multiple DSL subscribers into a single high-capacity backhaul connection, such as a T3 link or an optical fiber, to connect them to the internet.
13. A customer needs a metropolitan area WAN connection that provides high-speed, dedicated bandwidth between two sites. Which type of WAN connection would best fulfill this need?
packet-switched network
Ethernet WAN
circuit-switched network
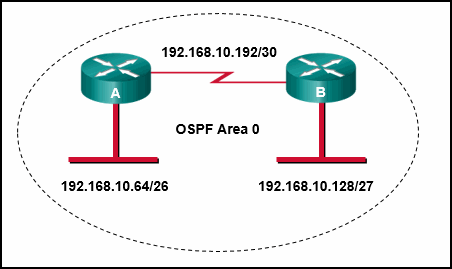
MPLS
Explanation: Topic 7.4.3
MPLS can use a variety of underlying technologies such as T- and E-Carriers, Carrier Ethernet, ATM, Frame Relay, and DSL, all of which support lower speeds than an Ethernet WAN. Neither a circuit-switched network, such as the public switched telephone network (PSTN) or Integrated Service Digital Network (ISDN), nor a packet-switched network, is considered high speed.
14. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use debuggers?
to detect installed tools within files and directories that provide threat actors remote access and control over a computer or network
to reverse engineer binary files when writing exploits and when analyzing malware
to obtain specially designed operating systems preloaded with tools optimized for hacking
to detect any evidence of a hack or malware in a computer or network
Explanation: Topic 3.3.3
Debuggers are penetration testing tools used by security professionals to reverse engineer binary files. This technique allows them to understand how a program functions at a low level, which is necessary for writing exploits during a penetration test or for analyzing malware to determine its behavior and impact. Examples of such tools include GDB, WinDbg, and IDA Pro.
15. Consider the following output for an ACL that has been applied to a router via the access-class in command. What can a network administrator determine from the output that is shown?
R1#
Standard IP access list 2
10 permit 192.168.10.0, wildcard bits 0.0.0.255 (2 matches)
20 deny any (1 match)
Two devices connected to the router have IP addresses of 192.168.10. x .
Two devices were able to use SSH or Telnet to gain access to the router.
Traffic from one device was not allowed to come into one router port and be routed outbound a different router port.
Traffic from two devices was allowed to enter one router port and be routed outbound to a different router port.
Explanation: Topic 5.3.1
The access-class command is used only on VTY ports. VTY ports support Telnet and/or SSH traffic. The match permit ACE is how many attempts were allowed using the VTY ports. The match deny ACE shows that a device from a network other than 192.168.10.0 was not allowed to access the router through the VTY ports.
16. What command would be used as part of configuring NAT or PAT to clear dynamic entries before the timeout has expired?
clear ip dhcp
clear ip nat translation
clear access-list counters
clear ip pat statistics
Explanation: Topic 6.5.5
By default, dynamic translation entries remain in the NAT table for 24 hours unless reconfigured. The clear ip nat translation privileged EXEC mode command is used to manually clear these dynamic entries from the table before the timeout has expired, which is specifically useful for clearing past translations during configuration testing or when modifying NAT pools. While clear ip nat statistics clears the hit/miss counters, it does not remove the actual address mappings from the translation table.
17. What are two characteristics of video traffic? (Choose two.)
Video traffic consumes less network resources than voice traffic consumes.
Video traffic latency should not exceed 400 ms.
Video traffic is more resilient to loss than voice traffic is.
Video traffic requires a minimum of 30 kbs of bandwidth.
Video traffic is unpredictable and inconsistent.
Explanation: Topic 9.2.4
Video traffic is characterized as unpredictable, inconsistent, and bursty because the number and size of packets vary depending on the content being transmitted (e.g., action sequences require more data than static scenes). To maintain an acceptable user experience and prevent degradation like blurriness or unsynchronized audio, the network must ensure that latency does not exceed 400 ms. Conversely, video is less resilient to loss than voice and requires significantly higher bandwidth (at least 384 Kbps).
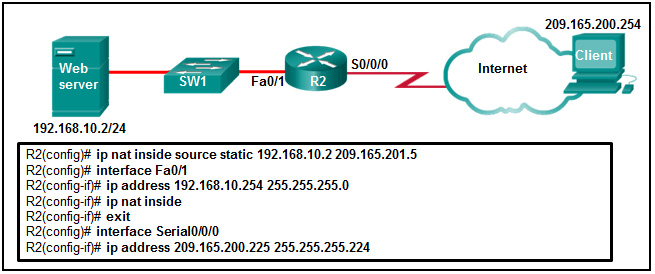
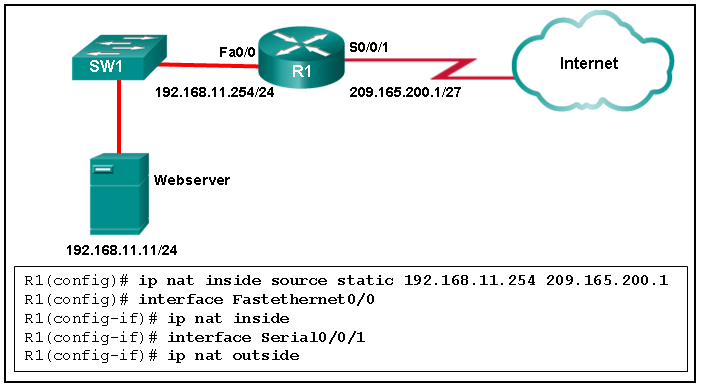
18. Refer to the exhibit. A technician is configuring R2 for static NAT to allow the client to access the web server. What is a possible reason that the client PC cannot access the web server?
The IP NAT statement is incorrect.
Interface Fa0/1 should be identified as the outside NAT interface.
Interface S0/0/0 should be identified as the outside NAT interface.
The configuration is missing a valid access control list.
Explanation: Topic 6.4.2
Interface S0/0/0 should be identified as the outside NAT interface. The command to do this would be R2(config-if)# ip nat outside.
19. In setting up a small office network, the network administrator decides to assign private IP addresses dynamically to workstations and mobile devices. Which feature must be enabled on the company router in order for office devices to access the internet?
UPnP
MAC filtering
NAT
QoS
Explanation: Topic 6.1.1
Network Address Translation (NAT) is the process used to convert private addresses to internet-routable addresses that allow office devices to access the internet.
20. A data center has recently updated a physical server to host multiple operating systems on a single CPU. The data center can now provide each customer with a separate web server without having to allocate an actual discrete server for each customer. What is the networking trend that is being implemented by the data center in this situation?
online collaboration
BYOD
virtualization
maintaining communication integrity
Explanation: Topic 13.2.3
Virtualization technology can run several different operating systems in parallel on a single CPU.
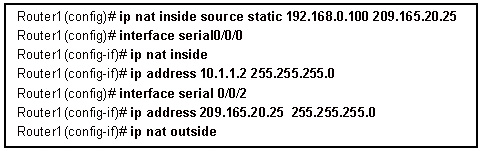
21. Refer to the exhibit. Which address or addresses represent the inside global address?
192.168.0.100
10.1.1.2
any address in the 10.1.1.0 network
209.165.20.25
Explanation: Topic 6.1.4
In NAT terminology, an inside global address is the address of an internal host as seen from the outside network, typically a globally routable IPv4 address. According to the static NAT configuration syntax ip nat inside source static [inside local address] [inside global address], the address 209.165.20.25 is explicitly defined as the global representation for the internal host 192.168.0.100. Additionally, this address is assigned to the router's outside interface (Serial 0/0/2), which is where translated traffic exits to reach external destinations.
22. Which two IPsec protocols are used to provide data integrity?
MD5
DH
AES
SHA
RSA
Explanation: Topic 8.3.5
The IPsec framework uses various protocols and algorithms to provide data confidentiality, data integrity, authentication, and secure key exchange. Two popular algorithms used to ensure that data is not intercepted and modified (data integrity) are MD5 and SHA. AES is an encryption protocol and provides data confidentiality. DH (Diffie-Hellman) is an algorithm used for key exchange. RSA is an algorithm used for authentication.
23. If an outside host does not have the Cisco AnyConnect client preinstalled, how would the host gain access to the client image?
The Cisco AnyConnect client is installed by default on most major operating systems.
The host initiates a clientless VPN connection using a compliant web browser to download the client.
The host initiates a clientless connection to a TFTP server to download the client.
The host initiates a clientless connection to an FTP server to download the client.
Explanation: Topic 8.2.1
If an outside host does not have the Cisco AnyConnect client preinstalled, the remote user must initiate a clientless SSL VPN connection via a compliant web browser, and then download and install the AnyConnect client on the remote host.
24. A company is considering updating the campus WAN connection. Which two WAN options are examples of the private WAN architecture? (Choose two.)
leased line
cable
digital subscriber line
Ethernet WAN
municipal Wi-Fi
Explanation: Topic 7.4.2
An organization can connect to a WAN through basic two options:
Private WAN infrastructure - such as dedicated point-to-point leased lines, PSTN, ISDN, Ethernet WAN, ATM, or Frame Relay
Public WAN infrastructure - such as digital subscriber line (DSL), cable, satellite access, municipal Wi-Fi, WiMAX, or wireless cellular including 3G/4G
25. Which type of QoS marking is applied to Ethernet frames?
IP precedence
DSCP
ToS
CoS
Explanation: Topic 9.5.5
The class of service (CoS) marking allows a Layer 2 Ethernet frame to be marked with eight levels of priority (values 0–7). This marking can be used by QoS-enabled network devices to provide preferential traffic treatment.
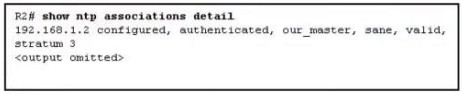
26. Refer to the exhibit. Routers R1 and R2 are connected via a serial link. One router is configured as the NTP master, and the other is an NTP client. Which two pieces of information can be obtained from the partial output of the show ntp associations detail command on R2? (Choose two.)
Both routers are configured to use NTPv2.
Router R1 is the master, and R2 is the client
The IP address of R2 is 192 168.1.2.
Router R2 is the master, and R1 is the client
The IP address of R1 is 192.168.1.2
Explanation: Topic 10.3.3
With the show NTP associations command, the IP address of the NTP master is given.
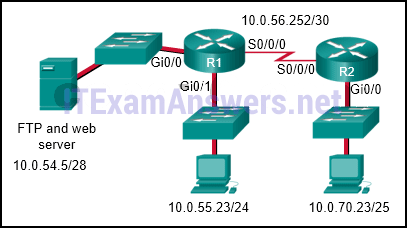
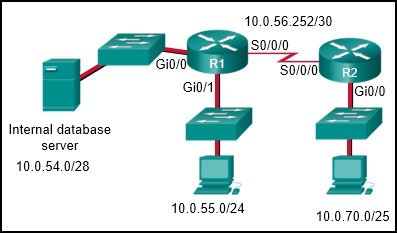
27. Refer to the exhibit. The network administrator that has the IP address of 10.0.70.23/25 needs to have access to the corporate FTP server (10.0.54.5/28). The FTP server is also a web server that is accessible to all internal employees on networks within the 10.x.x.x address. No other traffic should be allowed to this server. Which extended ACL would be used to filter this traffic, and how would this ACL be applied? (Choose two.)
R1(config)# interface s0/0/0
R1(config-if)# ip access-group 105 out
R2(config)# interface gi0/0
R2(config-if)# ip access-group 105 in
access-list 105 permit tcp host 10.0.70.23 host 10.0.54.5 eq 20
access-list 105 permit tcp host 10.0.70.23 host 10.0.54.5 eq 21
access-list 105 permit tcp 10.0.0.0 0.255.255.255 host 10.0.54.5 eq www
access-list 105 deny ip any host 10.0.54.5
access-list 105 permit ip any any
access-list 105 permit ip host 10.0.70.23 host 10.0.54.5
access-list 105 permit tcp any host 10.0.54.5 eq www
access-list 105 permit ip any any
R1(config)# interface gi0/0
R1(config-if)# ip access-group 105 out
Explanation: Topic 5.4.10
The first two lines of the ACL allow host 10.0.70.23 FTP access to the server that has the IP address of 10.0.54.5. The next line of the ACL allows HTTP access to the server from any host that has an IP address that starts with the number 10. The fourth line of the ACL denies any other type of traffic to the server from any source IP address. The last line of the ACL permits anything else in case there are other servers or devices added to the 10.0.54.0/28 network. Because traffic is being filtered from all other locations and for the 10.0.70.23 host device, the best place to put this ACL is closest to the server.
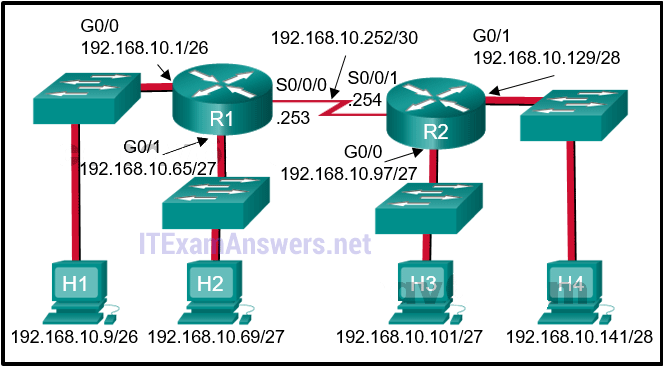
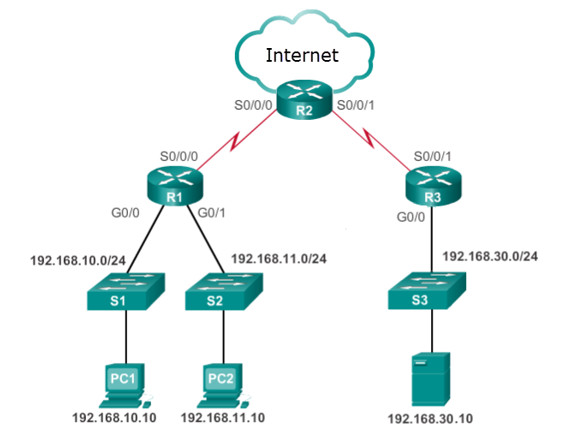
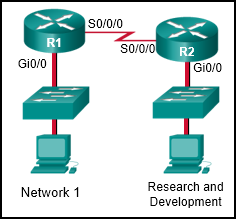
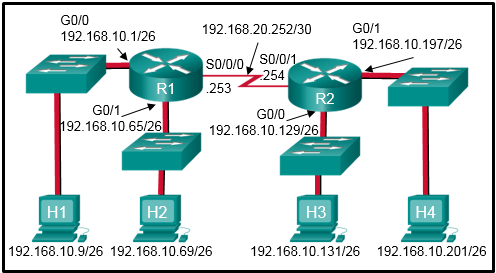
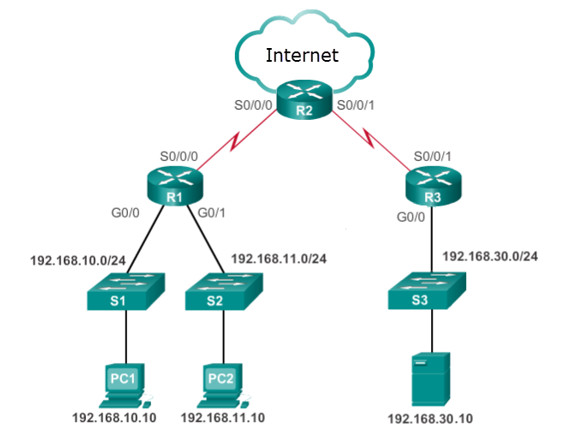
28. Refer to the exhibit. If the network administrator created a standard ACL that allows only devices that connect to the R2 G0/0 network access to the devices on the R1 G0/1 interface, how should the ACL be applied?
inbound on the R2 G0/0 interface
outbound on the R1 G0/1 interface
inbound on the R1 G0/1 interface
outbound on the R2 S0/0/1 interface
Explanation: Topic 4.4.4
Because standard access lists only filter on the source IP address, they are commonly placed closest to the destination network. In this example, the source packets will be coming from the R2 G0/0 network. The destination is the R1 G0/1 network. The proper ACL placement is outbound on the R1 G0/1 interface.
29. Which is a characteristic of a Type 2 hypervisor?
does not require management console software
has direct access to server hardware resources
best suited for enterprise environments
installs directly on hardware
Explanation: Topic 13.2.6
Type 2 hypervisors are hosted on an underlaying operating system and are best suited for consumer applications and those experimenting with virtualization. Unlike Type 1 hypervisors, Type 2 hypervisors do not require a management console and do not have direct access to hardware.
30. What are the two types of VPN connections? (Choose two.)
PPPoE
Frame Relay
site-to-site
remote access
leased line
Explanation: Topic 8.1.3
PPPoE, leased lines, and Frame Relay are types of WAN technology, not types of VPN connections.
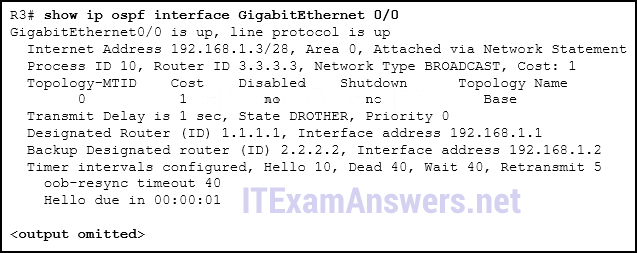
31. Refer to the exhibit. What three conclusions can be drawn from the displayed output? (Choose three.)
The DR can be reached through the GigabitEthernet 0/0 interface.
There have been 9 seconds since the last hello packet sent.
This interface is using the default priority.
The router ID values were not the criteria used to select the DR and the BDR.
The router ID on the DR router is 3.3.3.3
The BDR has three neighbors.
Explanation: Topic 2.3.4
The displayed output from the show ip ospf interface command provides the following insights:
Interface Reachability: The command output specifically describes the OSPF state and roles for the GigabitEthernet 0/0 interface, confirming that the Designated Router (ID 1.1.1.1) is the elected leader for this specific multiaccess segment.
Hello Timer: The default OSPF Hello interval for broadcast networks is 10 seconds. The output shows "Hello due in 00:00:01," which means 9 seconds have elapsed since the last Hello packet was transmitted.
Election Criteria: In an OSPF election where all priorities are equal, the router with the highest Router ID is elected DR. In this exhibit, R1 (ID 1.1.1.1) is the DR despite having a lower Router ID than R2 (ID 2.2.2.2) or the local router R3 (ID 3.3.3.3). Furthermore, R3 is a DROTHER because its priority is 0, which makes it ineligible for election regardless of its high Router ID. This confirms that Router ID values were not the primary criteria for the current election results.
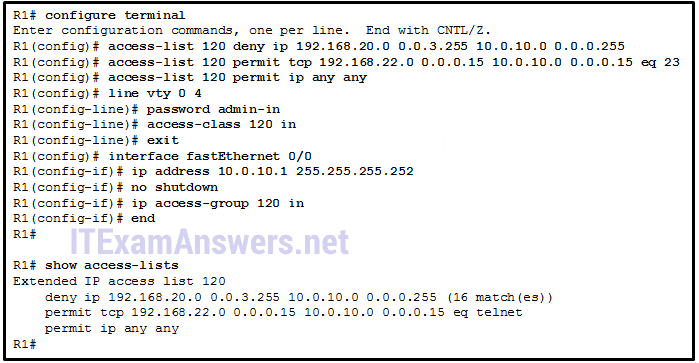
32. Refer to the exhibit. A network administrator is configuring an ACL to limit the connection to R1 vty lines to only the IT group workstations in the network 192.168.22.0/28. The administrator verifies the successful Telnet connections from a workstation with IP 192.168.22.5 to R1 before the ACL is applied. However, after the ACL is applied to the interface Fa0/0, Telnet connections are denied. What is the cause of the connection failure?
The enable secret password is not configured on R1.
The IT group network is included in the deny statement.
The permit ACE specifies a wrong port number.
The permit ACE should specify protocol ip instead of tcp.
The login command has not been entered for vty lines.
Explanation: Topic 12.4.4
The source IP range in the deny ACE is 192.168.20.0 0.0.3.255, which covers IP addresses from 192.168.20.0 to 192.168.23.255. The IT group network 192.168.22.0/28 is included in the 192.168.20/22 network. Therefore, the connection is denied. To fix it, the order of the deny and permit ACE should be switched.
33. What functionality does mGRE provide to the DMVPN technology?
It allows the creation of dynamically allocated tunnels through a permanent tunnel source at the hub and dynamically allocated tunnel destinations at the spokes.
It provides secure transport of private information over public networks, such as the Internet.
It is a Cisco software solution for building multiple VPNs in an easy, dynamic, and scalable manner.
It creates a distributed mapping database of public IP addresses for all VPN tunnel spokes.
Explanation: Topic 8.2.5
DMVPN is built on three protocols, NHRP, IPsec, and mGRE. NHRP is the distributed address mapping protocol for VPN tunnels. IPsec encrypts communications on VPN tunnels. The mGRE protocol allows the dynamic creation of multiple spoke tunnels from one permanent VPN hub.
34. What is used to pre-populate the adjacency table on Cisco devices that use CEF to process packets?
the FIB
the routing table
the ARP table
the DSP
Explanation: Topic 13.4.2
CEF uses the FIB and adjacency table to make fast forwarding decisions without control plane processing. The adjacency table is pre-populated by the ARP table and the FIB is pre-populated by the routing table.
35. What command would be used as part of configuring NAT or PAT to display information about NAT configuration parameters and the number of addresses in the pool?
show running-config
show ip nat statistics
show ip cache
show version
Explanation: Topic 6.5.5
The show ip nat statistics command is used to display a summary of NAT operations. It specifically provides information regarding NAT configuration parameters (such as designated inside and outside interfaces), the total number of active translations, and detailed data about address pools, including the total number of addresses in the pool and how many have been allocated. While show running-config can show the pool's configuration commands, only show ip nat statistics provides the real-time operational count of addresses within those pools.
36. What is a purpose of establishing a network baseline?
It provides a statistical average for network performance.
It creates a point of reference for future network evaluations.
It manages the performance of network devices.
It checks the security configuration of network devices.
Explanation: Topic 12.1.4
A baseline is used to establish normal network or system performance. It can be used to compare with future network or system performances in order to detect abnormal situations.
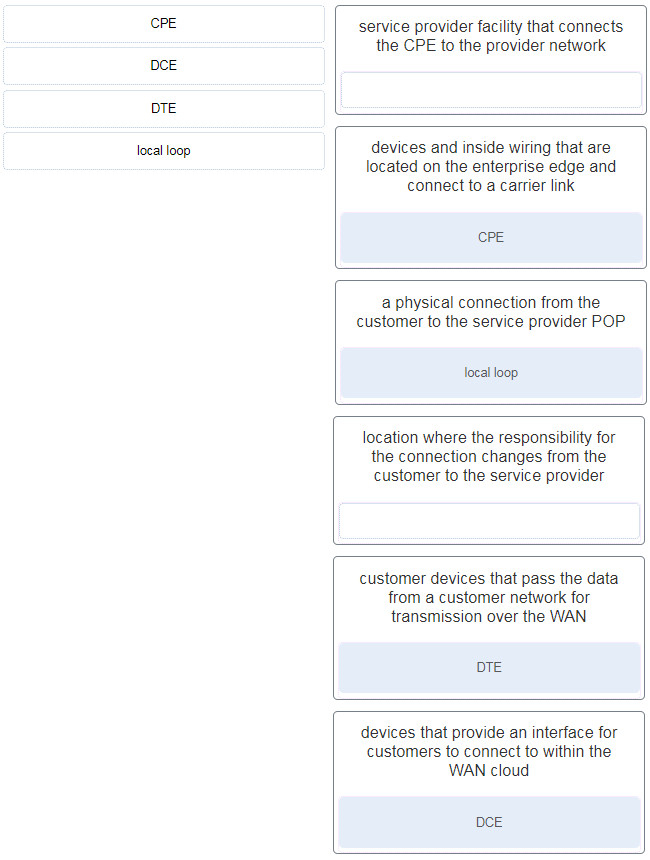
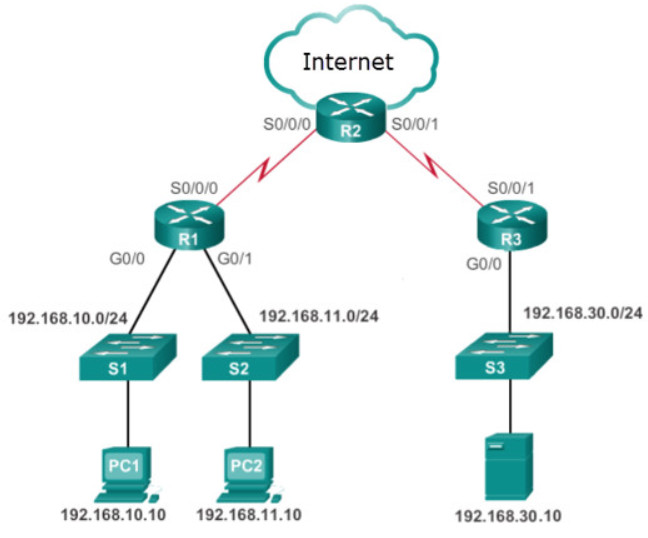
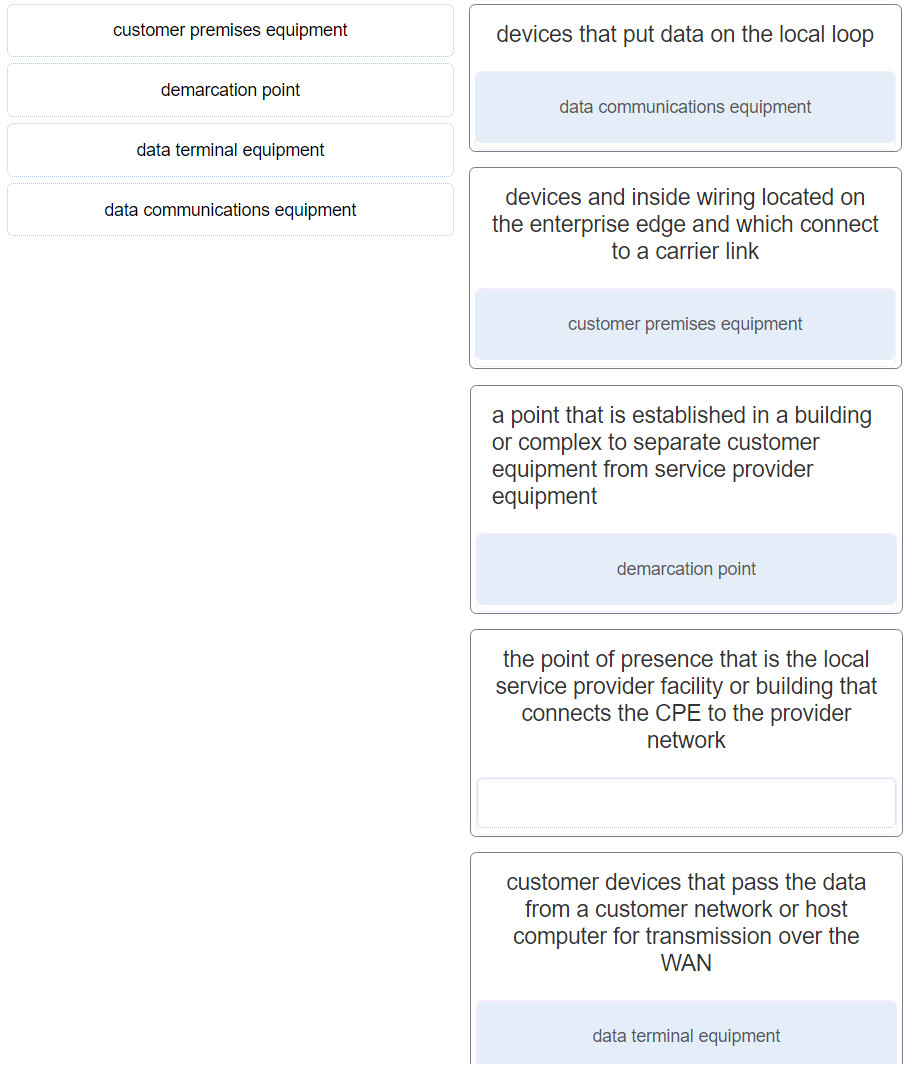
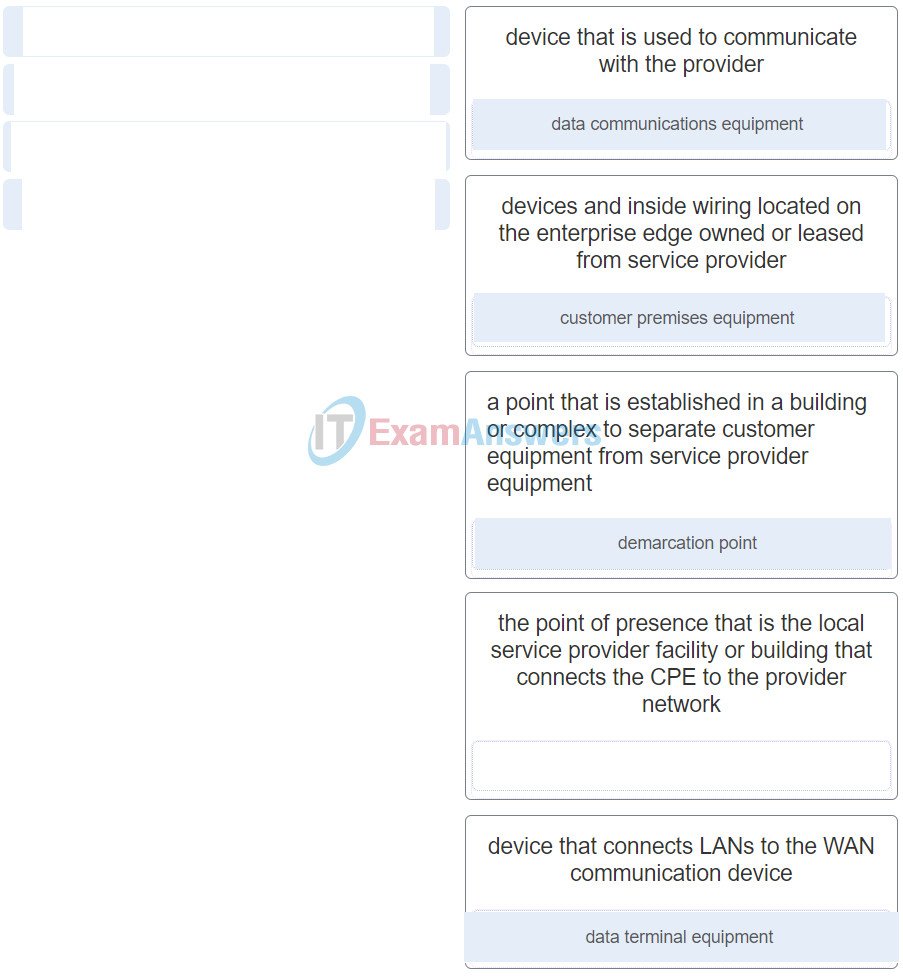
37. Match the type of WAN device or service to the description. (Not all options are used.)
CPE
devices and inside wiring that are located on the enterprise edge and connect to a carrier link
DCE
devices that provide an interface for customers to connect to within the WAN cloud
DTE
customer devices that pass the data from a customer network for transmission over the WAN
local loop
a physical connection from the customer to the service provider POP
Explanation: Topic 7.2.3
38. Which statement describes a characteristic of standard IPv4 ACLs?
They filter traffic based on source IP addresses only.
They can be created with a number but not with a name.
They are configured in the interface configuration mode.
They can be configured to filter traffic based on both source IP addresses and source ports.
Explanation: Topic 4.1.2
A standard IPv4 ACL can filter traffic based on source IP addresses only. Unlike an extended ACL, it cannot filter traffic based on Layer 4 ports. However, both standard and extended ACLs can be identified with either a number or a name, and both are configured in global configuration mode.
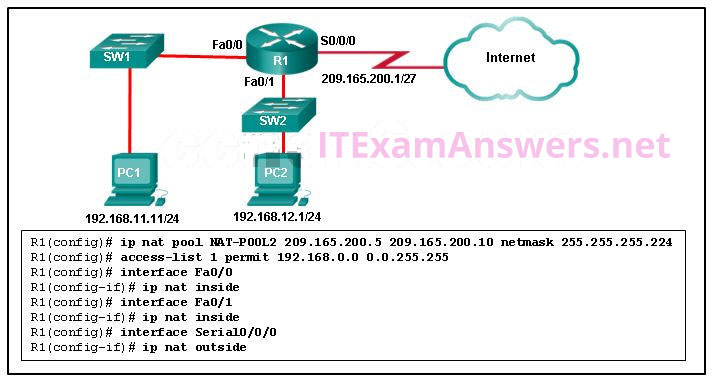
39. Refer to the exhibit. R1 is configured for NAT as displayed. What is wrong with the configuration?
NAT-POOL2 is not bound to ACL 1.
Interface Fa0/0 should be identified as an outside NAT interface.
The NAT pool is incorrect.
Access-list 1 is misconfigured.
Explanation: Topic 6.5.2
R1 has to have NAT-POOL2 bound to ACL 1. This is accomplished with the command R1(config)#ip nat inside source list 1 pool NAT-POOL2. This would enable the router to check for all interesting traffic and if it matches ACL 1 it would be translated by use of the addresses in NAT-POOL2.
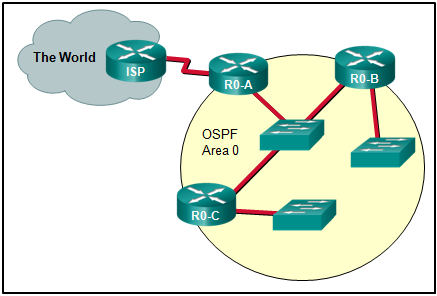
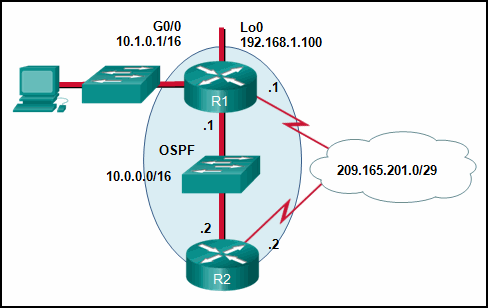
40. Refer to the exhibit. What method can be used to enable an OSPF router to advertise a default route to neighboring OSPF routers?
Use a static route pointing to the ISP and redistribute it.
Use the redistribute static command on R0-A.
Use the default-information originate command on ISP.
Use the default-information originate command on R0-A.
Explanation: Topic 2.5.1
To enable an OSPF router to advertise a default route to its neighbors, the edge router (known as the Autonomous System Boundary Router or ASBR) must be configured with a default static route and the default-information originate command. In this scenario, R0-A is the edge router connected to the ISP; therefore, entering this command on R0-A instructs it to become the source of the default route information and propagate that route in OSPF updates to R0-B and R0-C.
41. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use applications such as John the Ripper,THC Hydra, RainbowCrack, and Medusa?
to capture and analyze packets within traditional Ethernet LANs or WLANs
to probe and test the robustness of a firewall by using specially created forged packets
to make repeated guesses in order to crack a password
Explanation: Topic 3.3.3
Applications such as John the Ripper, THC Hydra, RainbowCrack, and Medusa are specifically categorized as password crackers. These tools are used during penetration tests to recover or discover critical system passwords by repeatedly making guesses or by bypassing data encryption. Identifying weak or compromised passwords is a vital part of a security assessment because they can provide threat actors with easy access to valuable corporate data.
42. What are two syntax rules for writing a JSON array? (Choose two.)
Each value in the array is separated by a comma.
The array can include only one value type.
A space must separate each value in the array.
A semicolon separates the key and list of values.
Values are enclosed in square brackets.
Explanation: Topic 14.2.6
A JSON array is a collection of ordered values within square brackets [ ]. The values in the array are separated by a comma. For example “users” : [“bob”, “alice”, “eve”].
43. What is a characteristic of a Trojan horse as it relates to network security?
An electronic dictionary is used to obtain a password to be used to infiltrate a key network device.
Malware is contained in a seemingly legitimate executable program.
Extreme quantities of data are sent to a particular network device interface.
Too much information is destined for a particular memory block, causing additional memory areas to be affecte
Explanation: Topic 3.4.2
A Trojan horse carries out malicious operations under the guise of a legitimate program. Denial of service attacks send extreme quantities of data to a particular host or network device interface. Password attacks use electronic dictionaries in an attempt to learn passwords. Buffer overflow attacks exploit memory buffers by sending too much information to a host to render the system inoperable.
44. An attacker is redirecting traffic to a false default gateway in an attempt to intercept the data traffic of a switched network. What type of attack could achieve this?
TCP SYN flood
DNS tunneling
DHCP spoofing
ARP cache poisoning
Explanation: Topic 3.8.7
In DHCP spoofing attacks, an attacker configures a fake DHCP server on the network to issue DHCP addresses to clients with the aim of forcing the clients to use a false default gateway, and other false services. DHCP snooping is a Cisco switch feature that can mitigate DHCP attacks. MAC address starvation and MAC address snooping are not recognized security attacks. MAC address spoofing is a network security threat.
45. A company is developing a security policy for secure communication. In the exchange of critical messages between a headquarters office and a branch office, a hash value should only be recalculated with a predetermined code, thus ensuring the validity of data source. Which aspect of secure communications is addressed?
data integrity
non-repudiation
origin authentication
data confidentiality
Explanation: Topic 3.10.5
Secure communications consists of four elements:
Data confidentiality - guarantees that only authorized users can read the message
Data integrity - guarantees that the message was not altered
Origin authentication - guarantees that the message is not a forgery and does actually come from whom it states
Data nonrepudiation – guarantees that the sender cannot repudiate, or refute, the validity of a message sent
46. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use packet sniffers?
to detect installed tools within files and directories that provide threat actors remote access and control over a computer or network
to detect any evidence of a hack or malware in a computer or network
to probe and test the robustness of a firewall by using specially created forged packets
to capture and analyze packets within traditional Ethernet LANs or WLANs
Explanation: Topic 3.3.3
Packet sniffers are specialized tools used by security professionals to capture, monitor, and analyze network data exchanges in real-time. These tools, such as Wireshark or Tcpdump, allow a penetration testing team to decode various protocol layers within recorded frames to identify potential security gaps or unencrypted sensitive information. While they provide a full view of the data inside a packet, they are primarily designed for capturing traffic rather than active tasks like probing firewalls with forged packets or reverse engineering binary files.
47. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 172.20.0.0 255.255.252.0. What wildcard mask would the administrator use in the OSPF network statement?
0.0.15.255
0.0.3.255
0.0.7.255
0.0.1.255
Explanation: Topic 2.2.2
The easiest method to calculate an OSPF wildcard mask is to subtract the network's subnet mask from 255.255.255.255. For the network 172.20.0.0 with a subnet mask of 255.255.252.0, the calculation is:
255.255.255.255
- 255.255.252. 0
----------------- 0. 0. 3.255.
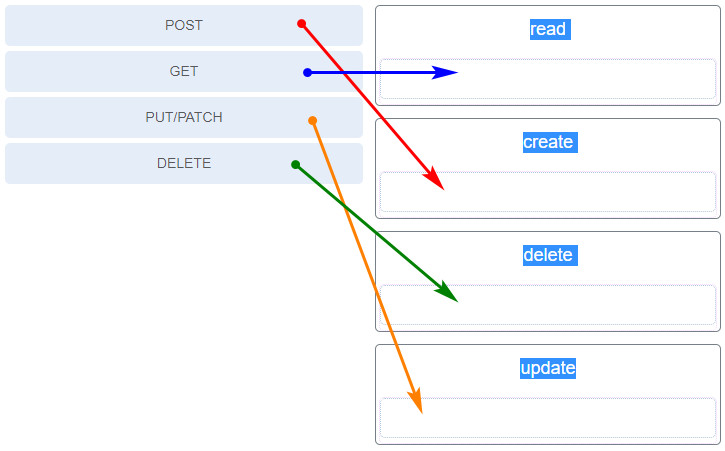
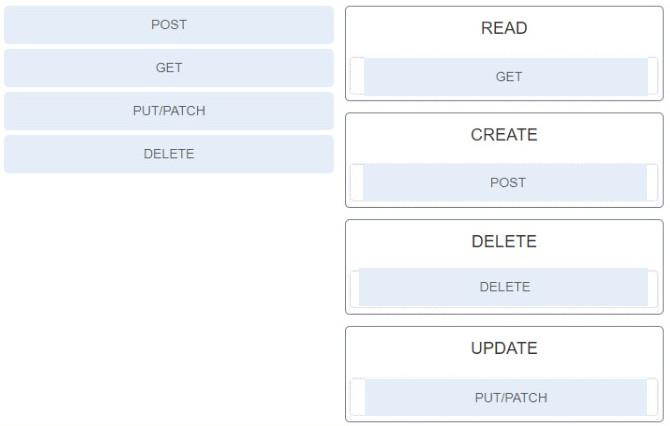
48. Match the HTTP method with the RESTful operation.
POST
Create
GET
Read
PUT/PATCH
Update/Replace?Modify
Delete
Delete
Explanation: Topic 14.4.3
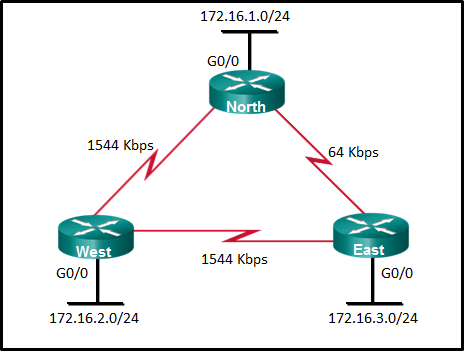
49. Refer to the exhibit. What is the OSPF cost to reach the West LAN 172.16.2.0/24 from East?
782
74
128
65
Explanation: Topic 2.4.3
The OSPF cost for a route is the accumulated value of all outgoing interfaces from the source router to the destination network. To reach the West LAN (172.16.2.0/24) from the East router, the packet must exit two interfaces:
The Serial interface on the East router connecting to West (1544 Kbps): By default, OSPF calculates the cost for a T1 link as 64.
The GigabitEthernet 0/0 interface on the West router leading to the LAN: The default OSPF cost for a Gigabit Ethernet interface is 1.
Adding these together (64+1), the total cumulative cost is 65.
50. What is one reason to use the ip ospf priority command when the OSPF routing protocol is in use?
to activate the OSPF neighboring process
to influence the DR/BDR election process
to provide a backdoor for connectivity during the convergence process
to streamline and speed up the convergence process
Explanation: Topic 2.3.8
The OSPF priority can be set to a number between 0 and 255. The higher the number set, the more likely the router becomes the DR. A priority 0 stops a router from participating in the election process and the router does not become a DR or a BDR.
51. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
If a packet with a source address of 172.18.20.14, a destination address of 172.18.20.40, and a protocol of 21 is received on the interface, is the packet permitted or denied?
permitted
Explanation: Topic 5.4.2
Source Address Match: The source wildcard mask of 0.0.0.31 combined with the network 172.18.20.0 defines a range from 172.18.20.0 to 172.18.20.31. The packet's source address, 172.18.20.14, falls within this permitted range.
Destination Address Match: The destination wildcard mask of 0.0.0.31 combined with 172.18.20.32 defines a range from 172.18.20.32 to 172.18.20.63. The packet's destination address, 172.18.20.40, falls within this permitted range.
Protocol and Port Match: The ACL specifies TCP and the operator eq ftp (port 21). The packet uses protocol 21 (FTP), satisfying the final criteria. Since all conditions (source, destination, protocol, and port) match the permit statement, the packet is allowed.
52. What is a characteristic of the two-tier spine-leaf topology of the Cisco ACI fabric architecture?
The spine and leaf switches are always linked through core switches.
The spine switches attach to the leaf switches and attach to each other for redundancy.
The leaf switches always attach to the spines and they are interlinked through a trunk line.
The leaf switches always attach to the spines, but they never attach to each other.
Explanation: Topic 13.5.4
In the two-tier spine-leaf topology used by Cisco ACI, the architecture follows a specific connection rule: every leaf switch must connect to every spine switch, but leaf switches never attach directly to one another. This design ensures that all devices connected to the fabric are exactly one hop away from each other, providing predictable and low-latency communication. Similarly, spine switches only connect to leaf switches and core switches, not to other spine switches.
53. Which two scenarios would result in a duplex mismatch? (Choose two.)
connecting a device with autonegotiation to another that is manually set to full-duplex
starting and stopping a router interface during a normal operation
connecting a device with an interface running at 100 Mbps to another with an interface running at 1000 Mbps
configuring dynamic routing incorrectly
manually setting the two connected devices to different duplex modes
Explanation: Topic 12.5.4
A duplex mismatch occurs when the two ends of an Ethernet link operate in different duplex modes. This happens if both ends are manually configured to different settings (one full and one half) or if one end is set to autonegotiate while the other is manually fixed at full-duplex. In the latter case, the autonegotiating end typically fails to detect the duplex and defaults to half-duplex, resulting in a mismatch that causes interface errors and late collisions.
54. A network technician is configuring SNMPv3 and has set a security level of auth . What is the effect of this setting?
authenticates a packet by a string match of the username or community string
authenticates a packet by using either the HMAC with MD5 method or the SHA method
authenticates a packet by using either the HMAC MD5 or 3.HMAC SHA algorithms and encrypts the packet with either the DES, 3DES or AES algorithms
authenticates a packet by using the SHA algorithm only
Explanation: Topic 10.4.4
For enabling SNMPv3 one of three security levels can be configured:
1) noAuth
2) auth
3) priv
The security level configured determines which security algorithms are performed on SNMP packets. The auth security level uses either HMAC with MD5 or SHA.
55. What are two types of attacks used on DNS open resolvers? (Choose two.)
amplification and reflection
resource utilization
fast flux
ARP poisoning
cushioning
Explanation: Topic 3.8.4
Three types of attacks used on DNS open resolvers are as follows:DNS cache poisoning – attacker sends spoofed falsified information to redirect users from legitimate sites to malicious sites
DNS amplification and reflection attacks – attacker sends an increased volume of attacks to mask the true source of the attack
DNS resource utilization attacks – a denial of service (DoS) attack that consumes server resources
56. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
If a packet with a source address of 192.168.101.45, a destination address of 64.100.40.4, and a protocol of 23 is received on the interface, is the packet permitted or denied?
If a packet with a source address of 192.168.100.219, a destination address of 64.100.40.10, and a protocol of 54 is received on the interface, is the packet permitted or denied?
denied
permitted
Explanation: Topic 5.4.2
Protocol Mismatch: The ACL is configured to permit UDP traffic, but Telnet (port 23) is a TCP protocol service.
Source Address Mismatch: The source address 192.168.101.45 does not match the range defined by 192.168.100.0 0.0.2.255. The wildcard 2 in the third octet (00000010) requires the last bit to be 0 (matching only 100 and 102), whereas 101 ends in 1.
Implicit Deny: Since the packet does not match the specific permit statement, it is discarded by the implicit deny any statement that exists at the end of every ACL.
57. Which type of resources are required for a Type 1 hypervisor?
a dedicated VLAN
a management console
a host operating system
a server running VMware Fusion
Explanation: Topic 13.3.2
Type 1 hypervisors, also known as "bare metal" hypervisors, are installed directly on the physical hardware rather than on a host operating system. Because they do not have a full graphical interface or local OS to create virtual machine instances, they require a management console to manage the hypervisor, consolidate servers, and handle operations like powering on or moving virtual machines between servers. VMware Fusion is an example of a Type 2 hypervisor, which does not require such a console.
58. In JSON, what is held within square brackets [ ]?
nested values
key/value pairs
an object
an array
Explanation: Topic 14.2.6
In JSON syntax, square brackets [ ] are used to hold arrays, which are defined as ordered lists of values. In contrast, curly braces { } are used to hold objects, which consist of one or more key/value pairs.
59. What are three components used in the query portion of a typical RESTful API request? (Choose three.)
resources
protocol
API server
format
key
parameters
Explanation: Topic 14.4.5
The query portion in a RESTful API request specifies the data format and information the client is requesting from the API service. Queries can include the following:
Format - JSON, YAML, XML, and other supported data format
Key - for authentication of the requesting source
Parameters - used to send information pertaining to the query request
60. A user reports that when the corporate web page URL is entered on a web browser, an error message indicates that the page cannot be displayed. The help-desk technician asks the user to enter the IP address of the web server to see if the page can be displayed. Which troubleshooting method is being used by the technician?
top-down
bottom-up
divide-and-conquer
substitution
Explanation: Topic 12.2.6
The technician is using the divide-and-conquer method by making an informed guess based on symptoms to select a specific layer to start the investigation. By asking the user to enter the IP address instead of the URL, the technician is attempting to determine if the issue is a name resolution (DNS) problem or a connectivity issue at a lower layer. If the web page displays using the IP address, the technician has successfully "divided" the problem and knows the layers below the Application layer are functioning correctly.
61. Which protocol provides authentication, integrity, and confidentiality services and is a type of VPN?
MD5
AES
IPsec
ESP
Explanation: Topic 8.3.2
IPsec services allow for authentication, integrity, access control, and confidentiality. With IPsec, the information exchanged between remote sites can be encrypted and verified. Both remote-access and site-to-site VPNs can be deployed using IPsec.
62. Which statement describes a characteristic of Cisco Catalyst 2960 switches?
They are best used as distribution layer switches.
New Cisco Catalyst 2960-C switches support PoE pass-through.
They are modular switches.
They do not support an active switched virtual interface (SVI) with IOS versions prior to 15.x.
Explanation: Topic 11.3.5
Cisco Catalyst 2960 switches support one active switched virtual interface (SVI) with IOS versions prior to 15.x. They are commonly used as access layer switches and they are fixed configuration switches.
63. Which component of the ACI architecture translates application policies into network programming?
the hypervisor
the Application Policy Infrastructure Controller
the Nexus 9000 switch
the Application Network Profile endpoints
Explanation: Topic 13.5.3
The Application Policy Infrastructure Controller (APIC) is the centralized software controller and "brains" of the Cisco ACI architecture. Its primary role is to provide centralized management and programmability, specifically by translating high-level application policies into the network programming required to configure the fabric. While the Application Network Profile defines the requirements, it is the APIC that performs the translation into actionable network configurations.
64. Which two pieces of information should be included in a logical topology diagram of a network? (Choose two.)
device type
cable specification
interface identifier
OS/IOS version
connection type
cable type and identifier
Explanation: Topic 12.1.2
The interface identifier and connection type should be included in a logical topology diagram because they indicate which interface is connected to other devices in the network with a specific type such as LAN, WAN, point-to-point, etc. The OS/IOS version, device type, cable type and identifier, and cable specification are typically included in a physical topology diagram.
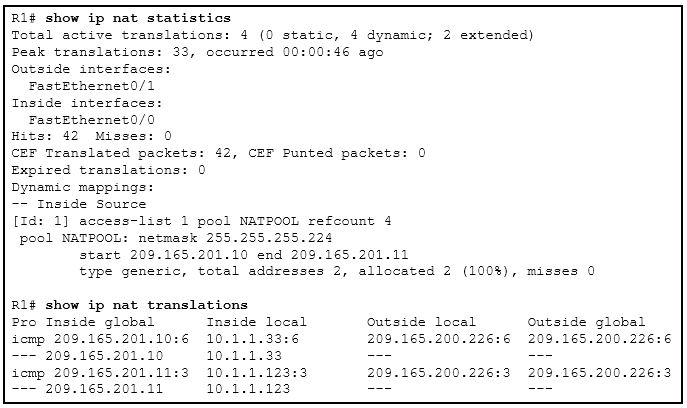
65. Refer to the exhibit. A PC at address 10.1.1.45 is unable to access the Internet. What is the most likely cause of the problem?
The NAT pool has been exhausted.
The wrong netmask was used on the NAT pool.
Access-list 1 has not been configured properly.
The inside and outside interfaces have been configured backwards.
Explanation: Topic 6.5.1
The output of show ip nat statistics shows that there are 2 total addresses and that 2 addresses have been allocated (100%). This indicates that the NAT pool is out of global addresses to give new clients. Based on the show ip nat translations, PCs at 10.1.1.33 and 10.1.1.123 have used the two available addresses to send ICMP messages to a host on the outside network.
66. What are two benefits of using SNMP traps? (Choose two.)
They eliminate the need for some periodic polling requests.
They reduce the load on network and agent resources.
They limit access for management systems only.
They can provide statistics on TCP/IP packets that flow through Cisco devices.
They can passively listen for exported NetFlow datagrams.
Explanation: Topic 10.4.3
SNMP traps are unsolicited messages sent by an agent to the SNMP manager to report an event immediately as it occurs. By notifying the manager only when significant events happen, traps eliminate the need for continuous, periodic polling, which in turn reduces the consumption of network bandwidth and processing resources on both the network and the managed devices (agents).
67. Which statement accurately describes a characteristic of IPsec?
IPsec works at the application layer and protects all application data.
IPsec is a framework of standards developed by Cisco that relies on OSI algorithms.
IPsec is a framework of proprietary standards that depend on Cisco specific algorithms.
IPsec works at the transport layer and protects data at the network layer.
IPsec is a framework of open standards that relies on existing algorithms.
Explanation: Topic 8.3.2
IPsec can secure a path between two network devices. IPsec can provide the following security functions:
Confidentiality - IPsec ensures confidentiality by using encryption.
Integrity - IPsec ensures that data arrives unchanged at the destination using a hash algorithm, such as MD5 or SHA.
Authentication - IPsec uses Internet Key Exchange (IKE) to authenticate users and devices that can carry out communication independently. IKE uses several types of authentication, including username and password, one-time password, biometrics, pre-shared keys (PSKs), and digital certificates.
Secure key exchange- IPsec uses the Diffie-Hellman (DH) algorithm to provide a public key exchange method for two peers to establish a shared secret key.
68. In a large enterprise network, which two functions are performed by routers at the distribution layer? (Choose two.)
connect users to the network
provide a high-speed network backbone
connect remote networks
provide Power over Ethernet to devices
provide data traffic security
Explanation: Topic 11.1.5
In a large enterprise network, the provision of a high-speed network backbone is a function of the core layer. Access layer switches connect users to the network and provide Power over Ethernet to devices. Distribution layer routers provide data traffic security and connections to other networks.
69. Which two statements describe the use of asymmetric algorithms? (Choose two.)
Public and private keys may be used interchangeably.
If a public key is used to encrypt the data, a public key must be used to decrypt the data.
If a private key is used to encrypt the data, a public key must be used to decrypt the data.
If a public key is used to encrypt the data, a private key must be used to decrypt the data.
If a private key is used to encrypt the data, a private key must be used to decrypt the data.
Explanation: Topic 3.10.8
Asymmetric algorithms use two keys: a public key and a private key. Both keys are capable of the encryption process, but the complementary matched key is required for decryption. If a public key encrypts the data, the matching private key decrypts the data. The opposite is also true. If a private key encrypts the data, the corresponding public key decrypts the data.
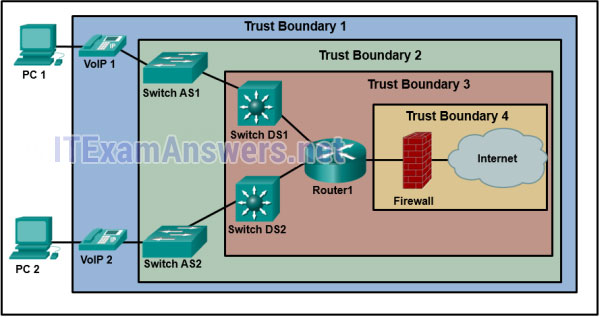
70. Refer to the exhibit. A network administrator has deployed QoS and has configured the network to mark traffic on the VoIP phones as well as the Layer 2 and Layer 3 switches. Where should initial marking occur to establish the trust boundary?
Trust Boundary 4
Trust Boundary 3
Trust Boundary 1
Trust Boundary 2
Explanation: Topic 9.5.10
Traffic should be classified and marked as close to its source as possible. The trust boundary identifies at which device marked traffic should be trusted. Traffic marked on VoIP phones would be considered trusted as it moves into the enterprise network.
71. What are two benefits of extending access layer connectivity to users through a wireless medium? (Choose two.)
reduced costs
decreased number of critical points of failure
increased flexibility
increased bandwidth availability
increased network management options
Explanation: Topic 11.2.5
Wireless connectivity at the access layer provides increased flexibility, reduced costs, and the ability to grow and adapt to changing business requirements. Utilizing wireless routers and access points can provide an increase in the number of central points of failure. Wireless routers and access points will not provide an increase in bandwidth availability.
72. What are two purposes of launching a reconnaissance attack on a network? (Choose two.)
to scan for accessibility
to retrieve and modify data
to gather information about the network and devices
to prevent other users from accessing the system
to escalate access privileges
Explanation: Topic 3.5.3
Gathering information about a network and scanning for access is a reconnaissance attack. Preventing other users from accessing a system is a denial of service attack. Attempting to retrieve and modify data, and attempting to escalate access privileges are types of access attacks.
73. A group of users on the same network are all complaining about their computers running slowly. After investigating, the technician determines that these computers are part of a zombie network. Which type of malware is used to control these computers?
botnet
spyware
virus
rootkit
Explanation: Topic 3.5.9
A botnet is a network of infected computers called a zombie network. The computers are controlled by a hacker and are used to attack other computers or to steal data.
74. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
If a packet with a source address of 10.1.1.201, a destination address of 192.31.7.45, and a protocol of 23 is received on the interface, is the packet permitted or denied?
permitted
denied
Explanation: Topic 5.4.2
Port/Service Mismatch: The ACL specifically permits TCP traffic where the destination port is DNS (port 53). However, the incoming packet is using protocol 23, which is the well-known port for Telnet.
Implicit Deny: Since the packet's port (23) does not match the port specified in the permit statement (53), the router moves past that entry. Because there are no other permit statements, the packet is discarded by the implicit deny any statement that is automatically applied to the end of every ACL.
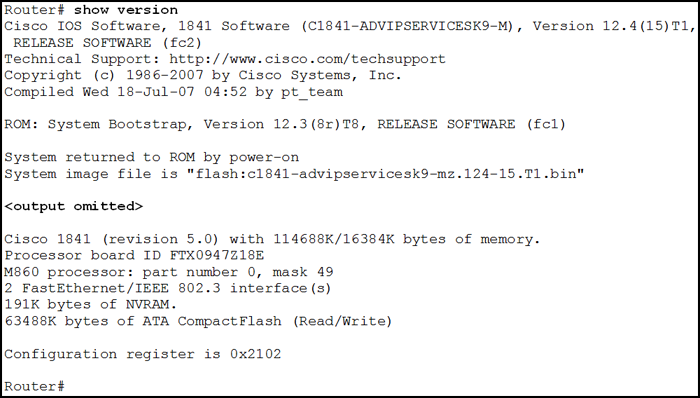
75. Refer to the exhibit. From which location did this router load the IOS?
flash memory
NVRAM?
RAM
ROM
a TFTP server?
Explanation: Topic 10.7.5
In the provided show version output, the line System image file is "flash:c1841-advipservicesk9-mz.124-15.Tl.bin" explicitly identifies the source of the Cisco IOS. The prefix flash: indicates that the router successfully located and loaded the operating system image from its internal flash memory during the boot process. Additionally, the configuration register value of 0x2102 confirms the router is set to follow standard boot procedures, which typically involve loading the first valid IOS image found in flash if no other specific boot instructions are present.
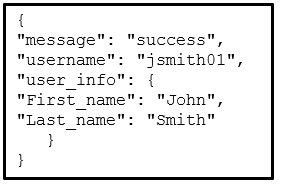
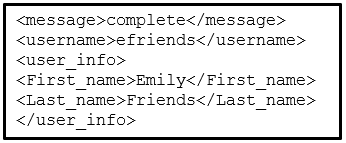
76. Refer to the exhibit. Which data format is used to represent the data for network automation applications?
XML
YAML
HTML
JSON
Explanation: Topic 14.2.5
The common data formats that are used in many applications including network automation and programmability are as follows:
JavaScript Object Notation (JSON) - In JSON, the data known as an object is one or more key/value pairs enclosed in braces { }. Keys must be strings within double quotation marks " ". Keys and values are separated by a colon.
eXtensible Markup Language (XML) - In XML, the data is enclosed within a related set of tags <tag>data</tag>.
YAML Ain’t Markup Language (YAML) - In YAML, the data known as an object is one or more key value pairs. Key value pairs are separated by a colon without the use of quotation marks. YAML uses indentation to define its structure, without the use of brackets or commas.
77. What QoS step must occur before packets can be marked?
classifying
shaping
queuing
policing
Explanation: Topic 9.5.4
Before a packet can be marked, it must first be classified. Classification is the process of analyzing network traffic flows to determine which specific class they belong to based on defined criteria. Once the traffic class is determined through classification, the packet can then be marked with a priority value in its header (such as DSCP or CoS) so that other QoS tools can identify and treat the traffic according to the established policy.
78. What is the main function of a hypervisor?
It is used to create and manage multiple VM instances on a host machine.
It is a device that filters and checks security credentials.
It is a device that synchronizes a group of sensors.
It is software used to coordinate and prepare data for analysis.
It is used by ISPs to monitor cloud computing resources.
Explanation: Topic 13.2.3
A hypervisor is a key component of virtualization. A hypervisor is often software-based and is used to create and manage multiple VM instances.
79. A company needs to interconnect several branch offices across a metropolitan area. The network engineer is seeking a solution that provides high-speed converged traffic, including voice, video, and data on the same network infrastructure. The company also wants easy integration to their existing LAN infrastructure in their office locations. Which technology should be recommended?
Frame Relay
Ethernet WAN
VSAT
ISDN
Explanation: Topic 7.4.3
Ethernet WAN uses many Ethernet standards and it connects easily to existing Ethernet LANs. It provides a switched, high-bandwidth Layer 2 network capable of managing data, voice, and video all on the same infrastructure. ISDN, while capable of supporting both voice and data, does not provide high bandwidth. VSAT uses satellite connectivity to establish a private WAN connection but with relatively low bandwidth. Use of VSAT, ISDN, and Frame Relay require specific network devices for the WAN connection and data conversion between LAN and WAN.
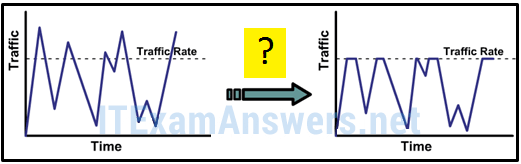
80. Refer to the exhibit. As traffic is forwarded out an egress interface with QoS treatment, which congestion avoidance technique is used?
traffic shaping
weighted random early detection
classification and marking
traffic policing
Explanation: Topic 9.5.12
Traffic shaping buffers excess packets in a queue and then forwards the traffic over increments of time, which creates a smoothed packet output rate. Traffic policing drops traffic when the amount of traffic reaches a configured maximum rate, which creates an output rate that appears as a saw-tooth with crests and troughs.
81. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
If a packet with a source address of 10.1.3.8, a destination address of 10.10.3.8, and a protocol of 53 is received on the interface, is the packet permitted or denied?
denied
permitted
Explanation: Topic 5.4.2
The packet is denied because it fails to match the specific criteria of the single permit entry in the ACL:
Source Address Mismatch: The ACL permits traffic from the source range 10.1.1.0 to 10.1.1.255. The packet's source address, 10.1.3.8, falls outside this permitted range.
Destination Address Mismatch: The ACL permits traffic destined for the specific host 10.1.3.8. The packet's destination address is 10.10.3.8, which does not match.
Implicit Deny: Because the packet does not match the explicit permit statement, it is discarded by the implicit deny any statement that is automatically applied to the end of every ACL.
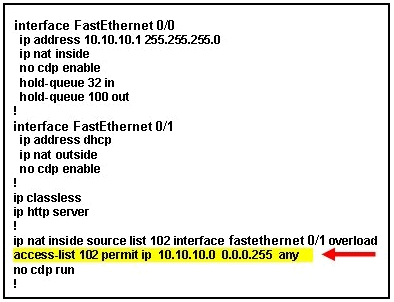
82. Refer to the exhibit. What is the purpose of the command marked with an arrow shown in the partial configuration output of a Cisco broadband router?
defines which addresses are allowed into the router
defines which addresses can be translated
defines which addresses are assigned to a NAT pool
defines which addresses are allowed out of the router
Explanation: Topic 6.5.2
In the provided configuration, access-list 102 is used in conjunction with the ip nat inside source command to identify the "inside local" traffic that is eligible for translation. Specifically, the statement access-list 102 permit ip 10.10.10.0 0.0.0.255 any identifies the internal network range, and the NAT command instructs the router to translate any source addresses matching that list to the public IP address of the FastEthernet 0/1 interface before forwarding the traffic to the outside network.
83. If a router has two interfaces and is routing both IPv4 and IPv6 traffic, how many ACLs could be created and applied to it?
12
4
8
16
6
Explanation: Topic 4.3.1
In calculating how many ACLs can be configured, use the rule of “three Ps”: one ACL per protocol, per direction, per interface. In this case, 2 interfaces x 2 protocols x 2 directions yields 8 possible ACLs.
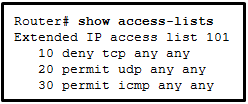
84. Refer to the exhibit. An administrator first configured an extended ACL as shown by the output of the show access-lists command. The administrator then edited this access-list by issuing the commands below.
Router(config)# ip access-list extended 101
Router(config-ext-nacl)# no 20
Router(config-ext-nacl)# 5 permit tcp any any eq 22
Router(config-ext-nacl)# 20 deny udp any any
Which two conclusions can be drawn from this new configuration? (Choose two.)
TFTP packets will be permitted.
Ping packets will be permitted.
Telnet packets will be permitted.
SSH packets will be permitted.
All TCP and UDP packets will be denied.
Explanation: Topic 5.2.3
After the editing, the final configuration is as follows:
Router# show access-lists
Extended IP access list 101
5 permit tcp any any eq ssh
10 deny tcp any any
20 deny udp any any
30 permit icmp any any
So, only SSH packets and ICMP packets will be permitted.
85. Which troubleshooting approach is more appropriate for a seasoned network administrator rather than a less-experienced network administrator?
a less-structured approach based on an educated guess
an approach comparing working and nonworking components to spot significant differences
a structured approach starting with the physical layer and moving up through the layers of the OSI model until the cause of the problem is identified
an approach that starts with the end-user applications and moves down through the layers of the OSI model until the cause of the problem has been identified
Explanation: Topic 12.2.6
The educated guess (also known as the "shoot-from-the-hip" approach) is more appropriate for seasoned technicians because they can rely on their extensive knowledge and experience to decisively isolate and solve network issues. While structured methods like bottom-up or top-down are safer for less-experienced administrators to avoid wasted time, an experienced admin can use intuition to skip steps and find the most probable cause quickly. For those without such experience, this approach often results in random and ineffective troubleshooting.
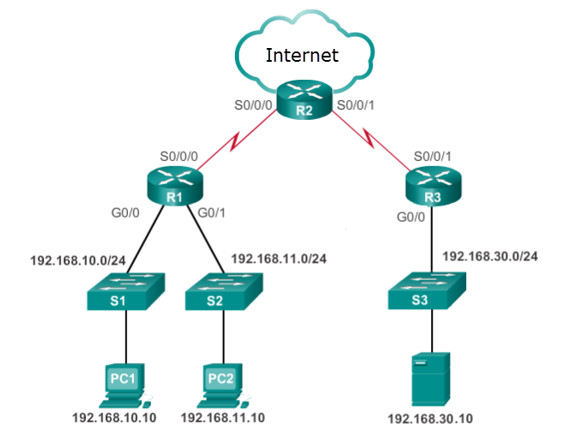
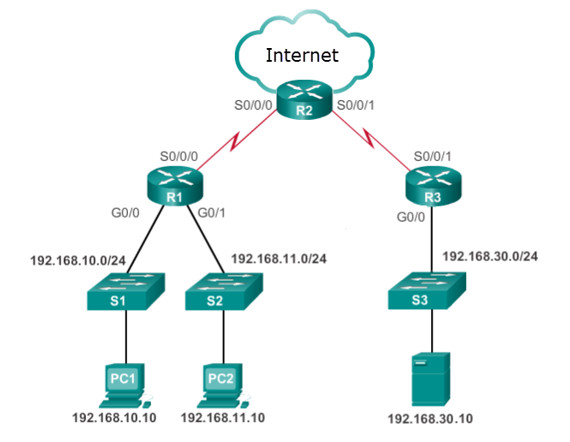
86. Refer to the exhibit. Many employees are wasting company time accessing social media on their work computers. The company wants to stop this access. What is the best ACL type and placement to use in this situation?
extended ACL outbound on R2 WAN interface towards the internet
standard ACL outbound on R2 WAN interface towards the internet
standard ACL outbound on R2 S0/0/0
extended ACLs inbound on R1 G0/0 and G0/1
Explanation: Topic 4.4.3
Type:Extended ACLs are required for this scenario because they can filter traffic based on destination addresses, protocols, and port numbers (such as specific social media sites or HTTP/HTTPS traffic), whereas standard ACLs only filter based on source addresses.
Placement: According to network design guidelines, extended ACLs should be located as close as possible to the source of the traffic being filtered. Placing these ACLs inbound on the R1 interfaces (G0/0 and G0/1) ensures that undesirable traffic is denied before it consumes any bandwidth or resources within the network infrastructure.
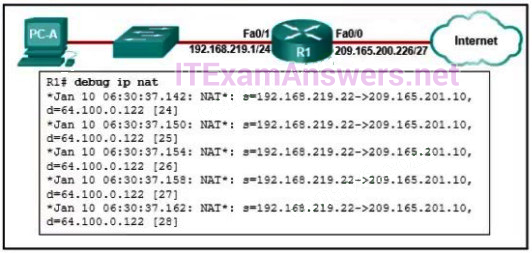
87. Refer to the exhibit. An administrator is trying to configure PAT on R1, but PC-A is unable to access the Internet. The administrator tries to ping a server on the Internet from PC-A and collects the debugs that are shown in the exhibit. Based on this output, what is most likely the cause of the problem?
The inside and outside NAT interlaces have been configured backwards
The inside global address is not on the same subnet as the ISP
The address on Fa0/0 should be 64.100.0.1.
The NAT source access list matches the wrong address range.
Explanation: Topic 6.1.4
The output of debug ip nat shows each packet that is translated by the router. The “s” is the source IP address of the packet and the “d” is the destination. The address after the arrow (“->”) shows the translated address. In this case, the translated address is on the 209.165.201.0 subnet but the ISP facing interface is in the 209.165.200.224/27 subnet. The ISP may drop the incoming packets, or might be unable to route the return packets back to the host because the address is in an unknown subnet.
88. Why is QoS an important issue in a converged network that combines voice, video, and data communications?
Data communications must be given the first priority.
Voice and video communications are more sensitive to latency.
Legacy equipment is unable to transmit voice and video without QoS.
Data communications are sensitive to jitter.
Explanation: Topic 9.2.2
Without any QoS mechanisms in place, time-sensitive packets, such as voice and video, will be dropped with the same frequency as email and web browsing traffic.
89. Which statement describes a VPN?
VPNs use logical connections to create public networks through the Internet.
VPNs use open source virtualization software to create the tunnel through the Internet.
VPNs use dedicated physical connections to transfer data between remote users.
VPNs use virtual connections to create a private network through a public network.
Explanation: Topic 8.1.1
A VPN is a private network that is created over a public network. Instead of using dedicated physical connections, a VPN uses virtual connections routed through a public network between two network devices.
90. In which OSPF state is the DR/BDR election conducted?
ExStart
Init
Two-Way
Exchange
Explanation: Topic 1.3.2
The DR and BDR election is conducted during the Two-Way state. In this state, communication between neighboring routers is confirmed as bidirectional. On multiaccess networks, such as Ethernet LANs, routers use this bidirectional communication to elect a Designated Router (DR) and a Backup Designated Router (BDR) before transitioning to the next state (ExStart) to begin synchronizing their databases.
91. Two corporations have just completed a merger. The network engineer has been asked to connect the two corporate networks without the expense of leased lines. Which solution would be the most cost effective method of providing a proper and secure connection between the two corporate networks?
Cisco Secure Mobility Clientless SSL VPN
Frame Relay
remote access VPN using IPsec
Cisco AnyConnect Secure Mobility Client with SSL
site-to-site VPN
Explanation: Topic 8.1.3
The site-to-site VPN is an extension of a classic WAN network that provides a static interconnection of entire networks. Frame Relay would be a better choice than leased lines, but would be more expensive than implementing site-to-site VPNs. The other options refer to remote access VPNs which are better suited for connecting users to the corporate network versus interconnecting two or more networks.
92. What is the final operational state that will form between an OSPF DR and a DROTHER once the routers reach convergence?
loading
established
full
two-way
Explanation: Topic 2.3.5
In OSPF multiaccess networks, a DROTHER forms a full adjacency with the Designated Router (DR) and Backup Designated Router (BDR) to synchronize link-state databases. While two DROTHERs remain in a Two-Way state to acknowledge each other's presence, the relationship between a DR and a DROTHER progresses through the Loading state until it reaches the Full state, indicating that their databases are identical and convergence is complete.
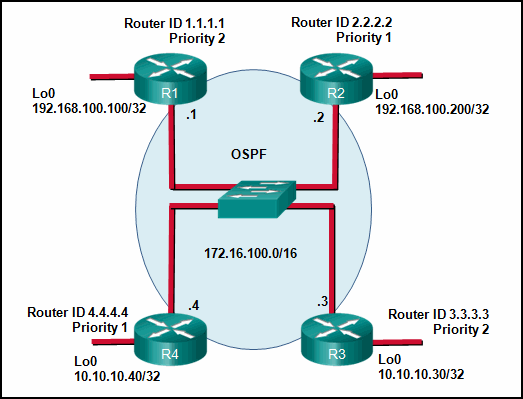
93. Refer to the exhibit. If the switch reboots and all routers have to re-establish OSPF adjacencies, which routers will become the new DR and BDR?
Router R3 will become the DR and router R1 will become the BDR.
Router R4 will become the DR and router R3 will become the BDR.
Router R1 will become the DR and router R2 will become the BDR.
Router R3 will become the DR and router R2 will become the BDR.
Explanation: Topic 2.3.6
OSPF elections of a DR are based on the following in order of precedence:
highest pritority from 1 -255 (0 = never a DR)
highest router ID
highest IP address of a loopback or active interface in the absence of a manually configured router ID. Loopback IP addresses take higher precedence than other interfaces.
In this case routers R3 and R1 have the highest router priority. Between the two, R3 has the higher router ID. Therefore, R3 will become the DR and R1 will become the BDR.
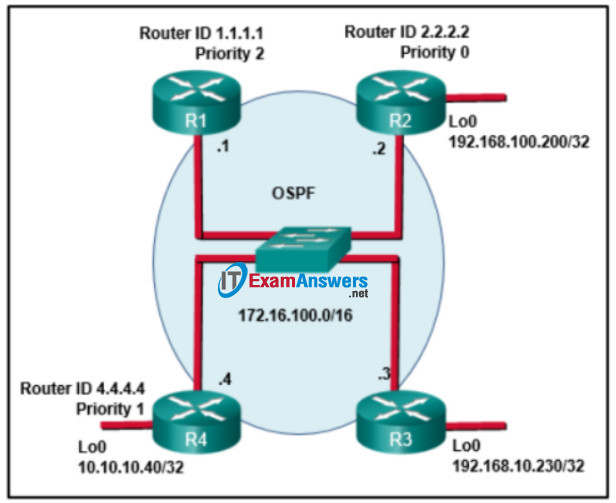
Case 2:
Enterprise Networking, Security, and Automation (Version 7.00) - ENSA Final Exam
Router R2 will become the DR and router R4 will become the BDR.
Router R1 will become the DR and router R3 will become the BDR.
Router R4 will become the DR and router R3 will become the BDR.
Router R3 will become the DR and router R2 will become the BDR.
Explanation: Topic 2.3.6
94. Which type of server would be used to keep a historical record of messages from monitored network devices?
DNS
print
DHCP
syslog
authentication
Explanation: Topic 10.5.1
A syslog server is used as a centralized location for logged messages from monitored network devices.
95. When QoS is implemented in a converged network, which two factors can be controlled to improve network performance for real-time traffic? (Choose two.)
packet addressing
delay
jitter
packet routing
link speed
Explanation: Topic 9.1.3
Delay is the latency between a sending and receiving device. Jitter is the variation in the delay of the received packets. Both delay and jitter need to be controlled in order to support real-time voice and video traffic.
96. In which step of gathering symptoms does the network engineer determine if the problem is at the core, distribution, or access layer of the network?
Determine ownership.
Determine the symptoms.
Narrow the scope.
Document the symptoms.
Gather information.
Explanation: Topic 12.2.2
In the “narrow the scope” step of gathering symptoms, a network engineer will determine if the network problem is at the core, distribution, or access layer of the network. Once this step is complete and the layer is identified, the network engineer can determine which pieces of equipment are the most likely cause.
97. What protocol sends periodic advertisements between connected Cisco devices in order to learn device name, IOS version, and the number and type of interfaces?
CDP
SNMP
NTP
LLDP
Explanation: Topic 10.1.1
Cisco Discovery Protocol (CDP) is a Cisco proprietary Layer 2 protocol that runs on all Cisco devices. It sends periodic advertisements to physically connected Cisco neighbors to share critical information, including the device name (hostname), the hardware platform, the IOS version, and the number and type of interfaces. While LLDP performs similar functions, it is a vendor-neutral protocol, whereas CDP is specifically designed for connected Cisco equipment.
98. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 192.168.0.0 255.255.252.0. What wildcard mask would the administrator use in the OSPF network statement?
0.0.0.127
0.0.0.31
0.0.3.255
0.0.0.63
Explanation: Topic 2.2.2
To determine the correct wildcard mask for an OSPF network statement, you subtract the subnet mask from 255.255.255.255. In this scenario, subtracting the subnet mask of 255.255.252.0 from 255.255.255.255 results in 0.0.3.255.
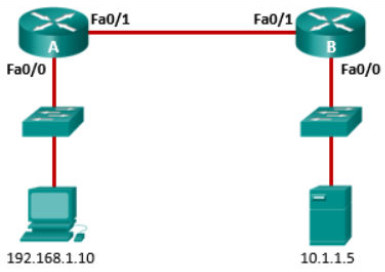
99. Refer to the exhibit. An administrator configures the following ACL in order to prevent devices on the 192.168.1.0 subnet from accessing the server at 10.1.1.5:
access-list 100 deny ip 192.168.1.0 0.0.0.255 host 10.1.1.5
access-list 100 permit ip any any
Where should the administrator place this ACL for the most efficient use of network resources?
inbound on router A Fa0/0
outbound on router B Fa0/0
outbound on router A Fa0/1
inbound on router B Fa0/1
Explanation: Topic 4.4.5
The configured ACL (100) is an Extended ACL because it filters traffic based on both source and destination IP addresses. According to standard design guidelines, Extended ACLs should be placed as close to the source of the traffic as possible. By applying this ACL inbound on Router A’s Fa0/0 interface, the unwanted traffic from the 192.168.1.0 subnet is discarded immediately upon entering the router, which prevents it from consuming bandwidth or processing resources across the point-to-point link and the rest of the network.
100. Which type of OSPFv2 packet is used to forward OSPF link change information?
link-state acknowledgment
link-state update
hello
database description
Explanation: Topic 1.2.3
The Type 4 Link-State Update (LSU) packet is specifically designed to announce new routing information and forward OSPF updates, such as link changes, to neighboring routers. While LSUs are used to reply to Link-State Requests (LSRs), they also serve as the primary vehicle for flooding Link-State Advertisements (LSAs) throughout an area when the network topology changes.
101. What protocol synchronizes with a private master clock or with a publicly available server on the internet?
MPLS
CBWFQ
TFTP
NTP
Explanation: Topic 10.3.1
Network Time Protocol (NTP) allows network devices to synchronize their software clocks with an NTP server to ensure accurate and consistent timestamping across the infrastructure. When implemented, the protocol can be configured to synchronize with a private master clock or with a publicly available NTP server on the internet. Consistent time settings are critical for correlating events in system logs and for effective network troubleshooting.
102. Which type of VPN allows multicast and broadcast traffic over a secure site-to-site VPN?
dynamic multipoint VPN
SSL VPN
IPsec virtual tunnel interface
GRE over IPsec
Explanation: Topic 8.2.4
Generic Routing Encapsulation (GRE) is a tunneling protocol that supports both multicast and broadcast traffic, which is essential for the operation of routing protocols over a VPN. Because standard IPsec tunnels are limited to unicast traffic, GRE over IPsec is used to encapsulate these non-unicast frames into GRE packets, which are then securely encrypted by IPsec for transport across the public network.
103. An OSPF router has three directly connected networks; 10.0.0.0/16, 10.1.0.0/16, and 10.2.0.0/16. Which OSPF network command would advertise only the 10.1.0.0 network to neighbors?
router(config-router)# network 10.1.0.0 0.0.255.255 area 0
router(config-router)# network 10.1.0.0 0.0.15.255 area 0
router(config-router)# network 10.1.0.0 255.255.255.0 area 0
router(config-router)# network 10.1.0.0 0.0.0.0 area 0
Explanation: Topic 2.2.2
To advertise only the 10.1.0.0/16 network the wildcard mask used in the network command must match the first 16-bits exactly. To match bits exactly, a wildcard mask uses a binary zero. This means that the first 16-bits of the wildcard mask must be zero. The low order 16-bits can all be set to 1.
104. Refer to the exhibit. Which sequence of commands should be used to configure router A for OSPF?
router ospf 1
network 192.168.10.64 0.0.0.63 area 0
network 192.168.10.192 0.0.0.3 area 0
Explanation: Topic 2.2.4
To configure OSPFv2, you must first enable the OSPF process using the router ospf [process-id] command. You then use the network statement to identify which interfaces participate in the routing process for a specific area.
The configuration requires two key components for each subnet:
Wildcard Mask: This is calculated by subtracting the subnet mask from 255.255.255.255.
For the /26 subnet (255.255.255.192), the wildcard is 0.0.0.63.
For the /30 WAN link (255.255.255.252), the wildcard is 0.0.0.3.
Area ID: Since the topology specifies the backbone area, both network statements must include area 0.
105. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 192.168.0.0 255.255.254.0. What wildcard mask would the administrator use in the OSPF network statement?
0.0.7.255
0.0.1.255
0.0.3.255
0.0.15.255
Explanation: Topic 2.2.2
The simplest method to calculate a wildcard mask is to subtract the network's subnet mask from a "quad-255" address (255.255.255.255). In this case, subtracting 255.255.254.0 from 255.255.255.255 results in 0.0.1.255. This mask tells the OSPF process to match the first 23 bits of the address exactly while ignoring the remaining bits.
106. How does virtualization help with disaster recovery within a data center?
improvement of business practices
supply of consistent air flow
support of live migration
guarantee of power
Explanation: Topic 13.2.4
Live migration allows moving of one virtual server to another virtual server that could be in a different location that is some distance from the original data center.
Case 2:
Less energy is consumed.
Server provisioning is faster.
Hardware at the recovery site does not have to be identical to production equipment.
Power is always provided.
Explanation: Topic 13.2.4
Improved disaster recovery - Virtualization offers advanced business continuity solutions. It provides hardware abstraction capability so that the recovery site no longer needs to have hardware that is identical to the hardware in the production environment. Most enterprise server virtualization platforms also have software that can help test and automate the failover before a disaster does happen.
107. How does virtualization help with disaster recovery within a data center?
Hardware does not have to be identical.
(Other case) Hardware at the recovery site does not have to be identical to production equipment.
Power is always provided.
Less energy is consumed.
Server provisioning is faster.
Explanation: Topic 13.2.4
Disaster recovery is how a company goes about accessing applications, data, and the hardware that might be affected during a disaster. Virtualization provides hardware independence which means the disaster recovery site does not have to have the exact equipment as the equipment in production. Server provisioning is relevant when a server is built for the first time. Although data centers do have backup generators, the entire data center is designed for disaster recovery. One particular data center could never guarantee that the data center itself would never be without power.
108. Refer to the exhibit. Which devices exist in the failure domain when switch S3 loses power?
S4 and PC_2
PC_3 and AP_2
AP_2 and AP_1
PC_3 and PC_2
S1 and S4
Explanation: Topic 11.2.3
A failure domain is the area of a network that is impacted when a critical device such as switch S3 has a failure or experiences problems.
109. Which set of access control entries would allow all users on the 192.168.10.0/24 network to access a web server that is located at 172.17.80.1, but would not allow them to use Telnet?
Explanation: Topic 5.4.2
For an extended ACL to meet these requirements the following need to be included in the access control entries:
identification number in the range 100-199 or 2000-2699
permit or deny parameter
protocol
source address and wildcard
destination address and wildcard
port number or name
110. Refer to the exhibit. A network administrator needs to add an ACE to the TRAFFIC-CONTROL ACL that will deny IP traffic from the subnet 172.23.16.0/20. Which ACE will meet this requirement?
5 deny 172.23.16.0 0.0.15.255
5 deny 172.23.16.0 0.0.255.255
15 deny 172.23.16.0 0.0.15.255
30 deny 172.23.16.0 0.0.15.255
Explanation: Topic 5.2.4
The only filtering criteria specified for a standard access list is the source IPv4 address. The wild card mask is written to identify what parts of the address to match, with a 0 bit, and what parts of the address should be ignored, which a 1 bit. The router will parse the ACE entries from lowest sequence number to highest. If an ACE must be added to an existing access list, the sequence number should be specified so that the ACE is in the correct place during the ACL evaluation process.
111. Which step in the link-state routing process is described by a router building a link-state database based on received LSAs?
executing the SPF algorithm
building the topology table
selecting the router ID
declaring a neighbor to be inaccessible
Explanation: Topic 1.1.3
In the generic link-state routing process, the third step is to build the Link-State Database (LSDB). After Link-State Advertisements (LSAs) are received from adjacent neighbors, OSPF-enabled routers use that information to build the topology table (LSDB), which contains information about all other routers in the network area and represents the overall network topology. Once this database is synchronized, the router can then execute the SPF algorithm to find the best paths.
112. What protocol uses agents, that reside on managed devices, to collect and store information about the device and its operation?
SYSLOG
TFTP
CBWFQ
SNMP
Explanation: Topic 10.4.2
In the generic link-state routing process, the third step is to build the Link-State Database (LSDB). After Link-State Advertisements (LSAs) are received from adjacent neighbors, OSPF-enabled routers use that information to build the topology table (LSDB), which contains information about all other routers in the network area and represents the overall network topology. Once this database is synchronized, the router can then execute the SPF algorithm to find the best paths.
113. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 10.27.27.0 255.255.255.0. What wildcard mask would the administrator use in the OSPF network statement?
0.0.0.63
0.0.0.255
0.0.0.31
0.0.0.15
Explanation: Topic 2.2.2
To calculate the wildcard mask for an OSPF network statement, you subtract the subnet mask from a "quad-255" address (255.255.255.255). For the subnet mask 255.255.255.0, the calculation is 255.255.255.255 minus 255.255.255.0, which equals 0.0.0.255. This mask tells the OSPF process to match the first three octets exactly while ignoring the last octet.
114. When will an OSPF-enabled router transition from the Down state to the Init state?
when an OSPF-enabled interface becomes active
as soon as the router starts
when the router receives a hello packet from a neighbor router
as soon as the DR/BDR election process is complete
Explanation: Topic 1.3.3
When OSPFv2 is enabled, the enabled Gigabit Ethernet 0/0 interface transitions from the Down state to the Init state. R1 starts sending Hello packets out all OSPF-enabled interfaces to discover OSPF neighbors to develop adjacencies with.
115. What type of traffic is described as having a high volume of data per packet?
data
video
voice
Explanation: Topic 9.2.4
Compared to voice traffic, video is described as having a higher volume of data per packet. While voice packets are typically small and predictable (approximately 200 bytes), video packets are significantly larger and vary in size based on the complexity and motion of the content being transmitted.
116. What protocol is a vendor-neutral Layer 2 protocol that advertises the identity and capabilities of the host device to other connected network devices?
LLDP
NTP
TFTP
SNMP
Explanation: Topic 10.2.1
Link Layer Discovery Protocol (LLDP) is a vendor-neutral Layer 2 neighbor discovery protocol similar to CDP. It is designed to work with network devices from different manufacturers, allowing them to advertise their identity and capabilities (such as device name, type, and management address) to other physically connected Layer 2 devices. This makes LLDP an essential tool for mapping network topologies in multi-vendor environments.
117. Which step in the link-state routing process is described by a router running an algorithm to determine the best path to each destination?
building the topology table
selecting the router ID
declaring a neighbor to be inaccessible
executing the SPF algorithm
Explanation: Topic 1.1.3
In the link-state routing process, executing the SPF algorithm is the step where a router runs the Dijkstra Shortest Path First (SPF) algorithm against its Link-State Database (topology table). This calculation creates an SPF tree, which determines the best (shortest) path to every destination network based on cumulative link costs. Once this algorithm finishes, the best routes are then offered to the routing table.
118. Refer to the exhibit. Which conclusion can be drawn from this OSPF multiaccess network?
If the DR stops producing Hello packets, a BDR will be elected, and then it promotes itself to assume the role of DR.
With an election of the DR, the number of adjacencies is reduced from 6 to 3.
When a DR is elected all other non-DR routers become DROTHER.
All DROTHER routers will send LSAs to the DR and BDR to multicast 224.0.0.5.
Explanation: Topic 1.3.5
On OSPF multiaccess networks, a DR is elected to be the collection and distribution point for LSAs sent and received. A BDR is also elected in case the DR fails. All other non-DR or BDR routers become DROTHER. Instead of flooding LSAs to all routers in the network, DROTHERs only send their LSAs to the DR and BDR using the multicast address 224.0.0.6. If there is no DR/BDR election, the number of required adjacencies is n(n-1)/2 = > 4(4-1)/2 = 6. With the election, this number is reduced to 3.
119. Refer to the exhibit. The network administrator has an IP address of 192.168.11.10 and needs access to manage R1. What is the best ACL type and placement to use in this situation?
extended ACL outbound on R2 WAN interface towards the internet
standard ACL inbound on R1 vty lines
extended ACLs inbound on R1 G0/0 and G0/1
extended ACL outbound on R2 S0/0/1
Explanation: Topic 5.3.1
Standard ACLs permit or deny packets based only on the source IPv4 address. Because all traffic types are permitted or denied, standard ACLs should be located as close to the destination as possible.
Extended ACLs permit or deny packets based on the source IPv4 address and destination IPv4 address, protocol type, source and destination TCP or UDP ports and more. Because the filtering of extended ACLs is so specific, extended ACLs should be located as close as possible to the source of the traffic to be filtered. Undesirable traffic is denied close to the source network without crossing the network infrastructure.
120. Which type of VPN connects using the Transport Layer Security (TLS) feature?
SSL VPN
IPsec virtual tunnel interface
GRE over IPsec
dynamic multipoint VPN
Explanation: Topic 8.2.2
When a client negotiates an SSL VPN connection with the VPN gateway, it connects using Transport Layer Security (TLS). TLS is the newer version of SSL and is sometimes expressed as SSL/TLS. The two terms are often used interchangeably.
121. Which group of APIs are used by an SDN controller to communicate with various applications?
eastbound APIs
westbound APIs
northbound APIs
southbound APIs
Explanation: Topic 13.4.4
The SDN controller uses northbound APIs to communicate with upstream applications (such as business or SDN applications) to help administrators shape traffic and deploy services. In contrast, southbound APIs are used by the controller to communicate with and define the behavior of downstream network elements like switches and routers.
122. A company has consolidated a number of servers and it is looking for a program or firmware to create and control virtual machines which have access to all the hardware of the consolidated servers. What service or technology would support this requirement?
Cisco ACI
software defined networking
Type-1 hypervisor
APIC-EM
Explanation: Topic 13.3.1
A Type-1 hypervisor, also known as a "bare metal" approach, is a program or firmware installed directly on the physical hardware of a server. This allows the hypervisor to create and control virtual machines (VMs) that have direct access to all hardware resources, such as CPUs, memory, and disk controllers. Because they lack the overhead of a host operating system, Type-1 hypervisors are highly efficient and are the standard choice for server consolidation in enterprise and data center environments.
123. What command would be used as part of configuring NAT or PAT to identify inside local addresses that are to be translated?
ip nat inside source list 24 interface serial 0/1/0 overload
ip nat inside source list 14 pool POOL-STAT overload
access-list 10 permit 172.19.89.0 0.0.0.255
ip nat inside source list ACCTNG pool POOL-STAT
Explanation: Topic 6.5.2
In the process of configuring NAT or PAT, a standard Access Control List (ACL) is used specifically to identify (permit) the range of internal private addresses—known as inside local addresses—that are eligible for translation. While the other commands listed (starting with ip nat inside source) are used to bind that identification to a global address pool or interface and execute the translation, it is the access-list statement itself that defines which packets the router will translate.
124. Anycompany has decided to reduce its environmental footprint by reducing energy costs, moving to a smaller facility, and promoting telecommuting, what service or technology would support requirement?
Cloud services
Data center
APIC-EM
Cisco ACI
Explanation: Topic 13.1.2 Cloud services directly support these requirements by eliminating or reducing the need for onsite IT equipment, which significantly lowers energy costs and physical plant requirements (allowing for a smaller facility). Furthermore, cloud computing enables employees to access organizational data and applications anywhere and at any time, which is essential for promoting telecommuting. The underlying virtualization technology also helps companies achieve a smaller carbon footprint by consolidating hardware and reducing power and cooling needs.
125. Refer to the exhibit. An administrator is trying to back up the current running configuration of the router to a USB drive, and enters the command copy usbflash0:/R1-config running-config on the router command line. After removing the USB drive and connecting it to a PC, the administrator discovers that the running configuration was not properly backed up to the R1-config file. What is the problem?
The file already exists on the USB drive and cannot be overwritten.
The drive was not properly formatted with the FAT16 file system.
There is no space left on the USB drive.
The USB drive is not recognized by the router.
The command that the administrator used was incorrect.
Explanation: Topic 10.6.7
The Cisco IOS copy command follows the syntax copy [source] [destination]. In this scenario, the administrator entered copy usbflash0:/R1-config running-config, which attempts to copy a file from the USB drive to the router's RAM (a restore operation). To properly back up the current configuration to the USB drive, the command should have been copy running-config usbflash0:/R1-config. The show file systems output confirms the USB drive was recognized, had write permissions (rw), and plenty of free space, so the only issue was the command syntax.
126. Which three types of VPNs are examples of enterprise-managed site-to-site VPNs? (Choose three.)
Layer 3 MPLS VPN
IPsec VPN
Cisco Dynamic Multipoint VPN
GRE over IPsec VPN
clientless SSL VPN
client-based IPsec VPN
Explanation: Topic 8.1.4
Enterprise-managed VPNs are created and managed by the organization using their own infrastructure to secure traffic across the internet. Within this category, IPsec VPNs, GRE over IPsec, and Cisco Dynamic Multipoint VPN (DMVPN) are specifically classified as site-to-site solutions used to connect remote branch offices to a main site. Conversely, Layer 3 MPLS is a service provider-managed solution, while clientless SSL and client-based IPsec are types of remote access VPNs intended for individual mobile users.
127. Refer to the exhibit. Employees on 192.168.11.0/24 work on critically sensitive information and are not allowed access off their network. What is the best ACL type and placement to use in this situation?
standard ACL inbound on R1 vty lines
extended ACL inbound on R1 G0/0
standard ACL inbound on R1 G0/1
extended ACL inbound on R3 S0/0/1
Explanation: Topic 4.4.3
A standard ACL is the best choice here because the security policy requires filtering traffic based solely on the source IP address (the 192.168.11.0/24 network). Placing the ACL inbound on the R1 G0/1 interface is most efficient because it discards unauthorized packets immediately upon entering the router. This "close to the source" placement prevents unwanted traffic from consuming any routing resources or bandwidth on the rest of the network.
128. In an OSPF network which two statements describe the link-state database (LSDB)? (Choose two.)
It can be viewed by using the show ip ospf database command.
A neighbor table is created based on the LSDB.
It contains a list of only the best routes to a particular network.
It contains a list of all neighbor routers to which a router has established bidirectional communication.
All routers within an area have an identical link-state database.
Explanation: Topic 1.1.2
The Link-state Database (LSDB) functions as the topology table for an OSPF area, containing comprehensive information about all other routers and links within that specific area. To ensure a consistent view of the network and accurate route calculations using the SPF algorithm, all routers within an area must maintain an identical LSDB. This database is stored in RAM and can be specifically inspected using the show ip ospf database command.
129. In an OSPF network which OSPF structure is used to create the neighbor table on a router?
adjacency database
link-state database
routing table
forwarding database
Explanation: Topic 1.1.2
The adjacency database is one of the three primary data structures used by OSPF. Its specific function is to create and maintain the neighbor table, which contains a unique list of all neighboring routers with which the router has established bidirectional communication. To view this table, administrators use the show ip ospf neighbor command.
130. What protocol is used in a system that consists of three elements--a manager, agents, and an information database?
MPLS
SYSLOG
SNMP
TFTP
Explanation: Topic 10.4.1
Simple Network Management Protocol (SNMP) is an application layer protocol that enables network administrators to monitor and manage network performance. An SNMP system is architecturally defined by three key elements: the SNMP manager (which runs management software), SNMP agents (software modules residing on managed devices), and the Management Information Base (MIB), which serves as the information database for storing device data and operational statistics.
131. What type of traffic is described as not resilient to loss?
data
video
voice
Explanation: Topic 9.2.4
Video traffic tends to be unpredictable, inconsistent, and bursty compared to voice traffic. Compared to voice, video is less resilient to loss and has a higher volume of data per packet.
132. Refer to the exhibit. Router R1 is configured with static NAT. Addressing on the router and the web server are correctly configured, but there is no connectivity between the web server and users on the Internet. What is a possible reason for this lack of connectivity?
Interface Fa0/0 should be configured with the command ip nat outside .
The inside global address is incorrect.
The router NAT configuration has an incorrect inside local address.
The NAT configuration on interface S0/0/1 is incorrect.
Explanation: Topic 6.4.2
To configure static NAT, the command syntax is ip nat inside source static [inside local address] [inside global address]. The inside local address should be the actual private IP address assigned to the internal device (the web server). In the exhibit description, the web server's IP is 192.168.11.11, but the command entered (192.168.11.254) mistakenly uses the IP address of the router's FastEthernet 0/0 interface. Because the mapping does not point to the server's real address, the NAT process will not function for the web server's traffic.
133. Which type of API would be used to allow authorized salespeople of an organization access to internal sales data from their mobile devices?
open
partner
public
private
Explanation: Topic 14.3.4
Private, or internal, APIs are used only within an organization and are for company access to data and services for internal use.
134. Refer to the exhibit. Which data format is used to represent the data for network automation applications?
XML
HTML
YAML
JSON
Explanation: Topic 14.2.8
Common data formats that are used in many applications including network automation and programmability include these:
JavaScript Object Notation (JSON) – In JSON, the data known as an object is one or more key/value pairs enclosed in braces { }. Keys must be strings within double quotation marks ” “. Keys and values are separated by a colon.
eXtensible Markup Language (XML) – In XML, the data is enclosed within a related set of tags data.
YAML Ain’t Markup Language (YAML) – In YAML, the data known as an object is one or more key value pairs. Key value pairs are separated by a colon without the use of quotation marks. YAML uses indentation to define its structure, without the use of brackets or commas.
135. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
If a packet with a source address of 198.133.219.100, a destination address of 198.133.219.170, and a protocol of 23 is received on the interface, is the packet permitted or denied?
denied
permitted
Explanation: Topic 4.1.3
Parameter Mismatch: The incoming packet fails to match the single Access Control Entry (ACE) on multiple fields. Specifically, its source address (198.133.219.100) and destination address (198.133.219.170) do not match the ACE's required source (192.168.100.32 0.0.0.7) and host destination (198.133.219.76).
Implicit Deny: According to the sources, when a packet does not match any defined ACE in a list, it is automatically discarded due to the implicit deny any statement that is present at the end of every ACL. Because this packet matches no permit criteria, it is denied.
136. Refer to the exhibit. If no router ID was manually configured, what would router R1 use as its OSPF router ID?
10.0.0.1
10.1.0.1
192.168.1.100
209.165.201.1
Explanation: Topic 2.1.4
Cisco routers determine the OSPF router ID based on a specific order of precedence. If an administrator does not explicitly configure a router ID using the router-id command, the router will automatically select the highest IPv4 address of any configured loopback interfaces. Because R1 has a loopback interface (Lo0) configured with the address 192.168.1.100, this address is chosen as the router ID, even if there are physical interfaces with active addresses. Physical interface addresses are only used as a last resort if no loopback interfaces exist.
137. What protocol is a vendor-neutral Layer 2 protocol that advertises the identity and capabilities of the host device to other connected network devices?
NTP
LLDP
SNMP
MPLS
Explanation: Topic 10.2.1 Link Layer Discovery Protocol (LLDP) is a vendor-neutral Layer 2 neighbor discovery protocol similar to CDP. It is designed to work across devices from different manufacturers, allowing them to advertise their identity and capabilities (such as device name and management address) to other physically connected network devices. This protocol is essential for mapping network topologies in multi-vendor environments.
138. Which type of VPN uses a hub-and-spoke configuration to establish a full mesh topology?
MPLS VPN
GRE over IPsec
IPsec virtual tunnel interface
dynamic multipoint VPN
Explanation: Topic 8.2.5 Dynamic Multipoint VPN (DMVPN) is a Cisco software solution designed to build multiple VPN tunnels in a dynamic and scalable manner. It specifically uses a hub-and-spoke configuration to establish what effectively becomes a full mesh topology; while spokes initially establish tunnels with a central hub, they can also obtain information from that hub to establish direct secure tunnels with each other as needed.
139. What is a characteristic of the REST API?
evolved into what became SOAP
used for exchanging XML structured information over HTTP or SMTP
considered slow, complex, and rigid
most widely used API for web services
Explanation: Topic 14.3.5
REST accounts for more than 80% of all API types used for web services, making it the most widely used web service API.
141. A student, doing a summer semester of study overseas, has taken hundreds of pictures on a smartphone and wants to back them up in case of loss. What service or technology would support this requirement?
Cisco ACI
cloud services
software defined networking
dedicated servers
Explanation: Topic 13.1.2
Cloud services provide off-premise, on-demand access to a shared pool of storage resources. This technology enables the student to access and back up their data anywhere and at any time, which is essential for someone studying overseas. Much like a physical storage unit for personal belongings, cloud computing serves as a digital storage solution for the "overflow" of data from a device like a smartphone.
142. Consider the following access list that allows IP phone configuration file transfers from a particular host to a TFTP server:
R1(config)# access-list 105 permit udp host 10.0.70.23 host 10.0.54.5 range 1024 5000
R1(config)# access-list 105 deny ip any any
R1(config)# interface gi0/0
R1(config-if)# ip access-group 105 out
Which method would allow the network administrator to modify the ACL and include FTP transfers from any source IP address?
R1(config)# interface gi0/0
R1(config-if)# no ip access-group 105 out
R1(config)# access-list 105 permit tcp any host 10.0.54.5 eq 20
R1(config)# access-list 105 permit tcp any host 10.0.54.5 eq 21
R1(config)# interface gi0/0
R1(config-if)# ip access-group 105 out
R1(config)# access-list 105 permit tcp any host 10.0.54.5 eq 20
R1(config)# access-list 105 permit tcp any host 10.0.54.5 eq 21
R1(config)# interface gi0/0
R1(config-if)# no ip access-group 105 out
R1(config)# no access-list 105
R1(config)# access-list 105 permit udp host 10.0.70.23 host 10.0.54.5 range 1024 5000
R1(config)# access-list 105 permit tcp any host 10.0.54.5 eq 20
R1(config)# access-list 105 permit tcp any host 10.0.54.5 eq 21
R1(config)# access-list 105 deny ip any any
R1(config)# interface gi0/0
R1(config-if)# ip access-group 105 out
R1(config)# access-list 105 permit udp host 10.0.70.23 host 10.0.54.5 range 1024 5000
R1(config)# access-list 105 permit tcp any host 10.0.54.5 eq 20
R1(config)# access-list 105 permit tcp any host 10.0.54.5 eq 21
R1(config)# access-list 105 deny ip any any
Explanation: Topic 5.2.2
When modifying a numbered ACL, new ACEs (Access Control Entries) are appended to the end of the list by default. Because the existing ACL already contains an explicit deny ip any any statement, simply adding new permit commands would place them after the deny statement, making them unreachable and ineffective. The most reliable method is to remove the ACL from the interface, delete it entirely with the no access-list command, and then recreate the entire sequence with the new entries placed before the final deny statement.
143. Which three statements are generally considered to be best practices in the placement of ACLs? (Choose three.)
Filter unwanted traffic before it travels onto a low-bandwidth link.
Place standard ACLs close to the destination IP address of the traffic.
Place standard ACLs close to the source IP address of the traffic.
Place extended ACLs close to the destination IP address of the traffic.
Place extended ACLs close to the source IP address of the traffic.
For every inbound ACL placed on an interface, there should be a matching outbound ACL.
Explanation: Topic 4.4.3
Extended ACLs should be placed as close as possible to the source IP address, so that traffic that needs to be filtered does not cross the network and use network resources. Because standard ACLs do not specify a destination address, they should be placed as close to the destination as possible. Placing a standard ACL close to the source may have the effect of filtering all traffic, and limiting services to other hosts. Filtering unwanted traffic before it enters low-bandwidth links preserves bandwidth and supports network functionality. Decisions on placing ACLs inbound or outbound are dependent on the requirements to be met.
144. Match the term to the web link http://www.buycarsfromus.com/2020models/ford/suv.html#Escape component. (Not all options are used.)
145. What command would be used as part of configuring NAT or PAT to display all static translations that have been configured?
show ip nat translations
show ip pat translations
show ip cache
show running-config
Explanation: Topic 6.5.5
The show ip nat translations command is used to display all active entries within the NAT translation table. According to the sources, this output specifically includes all static translations that have been configured, alongside any dynamic translations or PAT entries currently generated by network traffic. Because static mappings are permanent, they remain visible in this table regardless of whether there is active communication.
146. A network administrator modified an OSPF-enabled router to have a hello timer setting of 20 seconds. What is the new dead interval time setting by default?
40 seconds
60 seconds
80 seconds
100 seconds
Explanation: Topic 2.4.7
By default, Cisco IOS calculates the OSPF Dead interval as four times the Hello interval. When a network administrator modifies the Hello timer to 20 seconds, the router automatically adjusts the default Dead interval to 80 seconds (20 seconds * 4).
147. Which type of VPN is the preferred choice for support and ease of deployment for remote access?
SSL VPN
GRE over IPsec
dynamic multipoint VPN
IPsec virtual tunnel interface
Explanation: Topic 8.2.2
An SSL VPN is the preferred choice when support and ease of deployment are the primary considerations for remote access. While IPsec provides stronger security, SSL VPNs offer low connection complexity because they typically only require a web browser to establish a connection, making them easier to deploy across a wide range of devices without requiring specialized client software.
148. What type of traffic is described as predictable and smooth?
video
data
voice
Explanation: Topic 9.2.3
Voice traffic is specifically described as being predictable and smooth. It has known packet arrival times and a consistent bandwidth requirement, with packets typically arriving every 20 ms at a predictable size of 200 bytes. In contrast, video traffic is described as unpredictable and bursty, while general data traffic often has unpredictable bandwidth needs.
149. Which queuing mechanism has no provision for prioritizing or buffering but simply forwards packets in the order they arrive?
FIFO
LLQ
CBWFQ
WFQ
Explanation: Topic 9.3.3
FIFO (First-In, First-Out), also known as first-come, first-served, is the simplest queuing mechanism that buffers and forwards packets in the exact order they arrive. It has no concept of priority or traffic classes, meaning it makes no decisions to reorder packets based on importance; instead, it treats all packets equally within a single queue.
150. Refer to the exhibit. A network administrator has configured OSPFv2 on the two Cisco routers. The routers are unable to form a neighbor adjacency. What should be done to fix the problem on router R2?
Implement the command no passive-interface Serial0/1.
Implement the command network 192.168.2.6 0.0.0.0 area 0 on router R2.
Change the router-id of router R2 to 2.2.2.2.
Implement the command network 192.168.3.1 0.0.0.0 area 0 on router R2.
Explanation: Topic 2.2.9
OSPF-enabled routers must exchange Hello packets to discover neighbors and establish adjacencies. However, the passive-interface command suppresses these OSPF messages, preventing the router from sending and receiving routing updates on that specific interface. Because the show ip protocols output for R2 indicates that Serial0/1 (the interface connecting it to R1) is configured as a passive interface, R2 is not sending the necessary Hello packets to form an adjacency with R1. Removing this configuration on Serial0/1 will allow OSPF communication to resume on that link.
151. A network administrator is troubleshooting an OSPF problem that involves neighbor adjacency. What should the administrator do?
Make sure that the router priority is unique on each router.
Make sure that the DR/BDR election is complete.
Make sure that the router ID is included in the hello packet.
Make sure that the hello and dead interval timers are the same on all routers.
Explanation: Topic 2.6.1
For OSPF to establish a neighbor adjacency, certain parameters must match between neighboring routers. The Hello and Dead intervals are among these essential requirements; if these timers are not identical on the connected interfaces, the routers will fail to form an adjacency. Other requirements for adjacency include matching subnet masks, matching OSPF area IDs, and matching OSPF network types. While router IDs must be unique, the timers must be consistent across the link.
152. Refer to the exhibit. Internet privileges for an employee have been revoked because of abuse but the employee still needs access to company resources. What is the best ACL type and placement to use in this situation?
standard ACL inbound on R2 WAN interface connecting to the internet
standard ACL outbound on R2 WAN interface towards the internet
standard ACL inbound on R1 G0/0
standard ACL outbound on R1 G0/0
Explanation: Topic 4.4.3
- Standard ACLs permit or deny packets based only on the source IPv4 address. Because all traffic types are permitted or denied, standard ACLs should be located as close to the destination as possible.
- Extended ACLs permit or deny packets based on the source IPv4 address and destination IPv4 address, protocol type, source and destination TCP or UDP ports and more. Because the filtering of extended ACLs is so specific, extended ACLs should be located as close as possible to the source of the traffic to be filtered. Undesirable traffic is denied close to the source network without crossing the network infrastructure.
153. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
If a packet with a source address of 192.168.10.244, a destination address of 172.17.200.56, and a protocol of 80 is received on the interface, is the packet permitted or denied?
denied
permitted
Explanation: Topic 5.4.2
The packet is permitted because it successfully matches every field specified in the Access Control Entry (ACE):
Source Address: The packet's source (192.168.10.244) matches the network 192.168.10.0 with the wildcard mask 0.0.0.255.
Destination Address: The destination (172.17.200.56) matches the target network 172.17.200.0 with the wildcard mask 0.0.0.255.
Protocol and Port: The packet uses protocol 80, which is the numerical equivalent of the www keyword used in the configuration for TCP traffic.
154. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use applications such as Nmap, SuperScan, and Angry IP Scanner?
to detect installed tools within files and directories that provide threat actors remote access and control over a computer or network
to detect any evidence of a hack or malware in a computer or network
to reverse engineer binary files when writing exploits and when analyzing malware
to probe network devices, servers, and hosts for open TCP or UDP ports
Explanation: Topic 3.3.3
Applications such as Nmap, SuperScan, and Angry IP Scanner are classified as network scanning tools. During a penetration test, these tools are used to perform reconnaissance by probing network devices, servers, and hosts to identify active IP addresses and discover which TCP or UDP ports are open. This information helps security professionals determine which services are running and locate potential entry points into the network.
155. What command would be used as part of configuring NAT or PAT to display any dynamic PAT translations that have been created by traffic?
show ip pat translations
show ip cache
show running-config
show ip nat translations
Explanation: Topic 6.5.5
The show ip nat translations command is used to display all active entries within the NAT translation table. According to the sources, this command output includes all static translations that have been configured as well as any dynamic NAT or PAT translations that have been automatically created by network traffic. For PAT specifically, the table will show how unique source port numbers are used to differentiate between multiple internal hosts sharing the same public IP address.
156. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 172.16.91.0 255.255.255.192. What wildcard mask would the administrator use in the OSPF network statement?
0.0.31.255
0.0.0.63
0.0.15.255
0.0.7.255
Explanation: Topic 2.2.2
In OSPF, a wildcard mask is used to determine which bits of an IPv4 address must be matched to enable the protocol on an interface. The most efficient method to calculate this is to subtract the subnet mask from 255.255.255.255. For the network 172.16.91.0 with a subnet mask of 255.255.255.192, the calculation is:
255.255.255.255 - 255.255.255.192 = 0.0.0.63.
This wildcard mask instructs the router to match the first 26 bits of the network address and ignore the last 6 bits.
157. What type of traffic is described as requiring latency to be no more than 400 milliseconds (ms)?
video
data
voice
Explanation: Topic 9.2.4
Video traffic is described as requiring a one-way latency (delay) of no more than 400 milliseconds (ms) to maintain an acceptable user experience. In contrast, voice traffic is much more sensitive to delay and requires latency to be no more than 150 ms. General data traffic is typically classified as being relatively insensitive to both drops and delays.
158. Refer to the exhibit. Which two configurations would be used to create and apply a standard access list on R1, so that only the 10.0.70.0/25 network devices are allowed to access the internal database server? (Choose two.)
A.
R1(config)# interface GigabitEthernet0/0
R1(config-if)# ip access-group 5 out
B.
R1(config)# access-list 5 permit 10.0.54.0 0.0.1.255
C.
R1(config)# interface Serial0/0/0
R1(config-if)# ip access-group 5 in
D.
R1(config)# access-list 5 permit 10.0.70.0 0.0.0.127
E.
R1(config)# access-list 5 permit any
Explanation: Topic 4.4.3
Creating the ACL (D): Standard ACLs filter traffic based solely on the source IPv4 address. To permit only the 10.0.70.0/25 network, the correct wildcard mask is 0.0.0.127 (calculated by subtracting the subnet mask 255.255.255.128 from 255.255.255.255).
Applying the ACL (A): According to best practices, standard ACLs should be placed as close to the destination as possible. Since the internal database server is the destination and is connected to R1’s GigabitEthernet0/0 interface, the ACL should be applied outbound (out) on that interface to filter traffic just before it exits the router toward the server. Applying it elsewhere (like inbound on the serial interface) could unnecessarily block the 10.0.70.0/25 network from reaching other segments connected to R1, such as the 10.0.55.0/24 workstation.
159. A network administrator is writing a standard ACL that will deny any traffic from the 172.16.0.0/16 network, but permit all other traffic. Which two commands should be used? (Choose two.)
Explanation: Topic 5.1.2
To deny traffic from the 172.16.0.0/16 network, the access-list 95 deny 172.16.0.0 0.0.255.255 command is used. To permit all other traffic, the access-list 95 permit any statement is added.
160. Refer to the exhibit. The company has decided that no traffic initiating from any other existing or future network can be transmitted to the Research and Development network. Furthermore, no traffic that originates from the Research and Development network can be transmitted to any other existing or future networks in the company. The network administrator has decided that extended ACLs are better suited for these requirements. Based on the information given, what will the network administrator do?
One ACL will be placed on the R1 Gi0/0 interface and one ACL will be placed on the R2 Gi0/0 interface.
Only a numbered ACL will work for this situation.
One ACL will be placed on the R2 Gi0/0 interface and one ACL will be placed on the R2 S0/0/0 interface.
Two ACLs (one in each direction) will be placed on the R2 Gi0/0 interface.
Explanation: Topic 4.4.5
Extended ACLs should be placed as close to the source of the traffic as possible to filter undesirable traffic before it crosses the network infrastructure. To prevent traffic originating from the Research and Development network from reaching others, an ACL is placed inbound on R2's Gi0/0 interface to filter the traffic as it enters the router. To block traffic from all other existing or future networks from reaching Research and Development, a second ACL is applied outbound on the same Gi0/0 interface, ensuring any traffic destined for that network is dropped before exiting the router toward the destination. A single router interface can support one inbound and one outbound ACL per protocol.
161. What protocol uses smaller stratum numbers to indicate that the server is closer to the authorized time source than larger stratum numbers?
TFTP
SYSLOG
NTP
MPLS
Explanation: Topic 10.3.2
The Network Time Protocol (NTP) utilizes a hierarchical system of time sources where each level is known as a stratum. Smaller stratum numbers indicate that a server is closer to the authoritative time source (Stratum 0 high-precision devices) compared to larger stratum numbers. For example, Stratum 1 devices are directly connected to the primary time source, while Stratum 2 devices synchronize their time using packets from Stratum 1 servers.
162. Refer to the exhibit. If no router ID was manually configured, what would router Branch1 use as its OSPF router ID?
10.0.0.1
10.1.0.1
192.168.1.100
209.165.201.1
Explanation: Topic 2.1.4
In OSPFv2, a Cisco router uses a three-tier method to derive its router ID. The first choice is the manually configured router ID with the router-id command. If the router ID is not manually configured, the router will choose the highest IPv4 address of the configured loopback interfaces. Finally if no loopback interfaces are configured, the router chooses the highest active IPv4 address of its physical interfaces.
163. Match the HTTP method with the RESTful operation.
POST
create
GET
read
PUT/PATCH
update
DELETE
delete
Explanation: Topic 14.4.3
164. Refer to the exhibit. A web designer calls to report that the web server web-s1.cisco.com is not reachable through a web browser. The technician uses command line utilities to verify the problem and to begin the troubleshooting process. Which two things can be determined about the problem? (Choose two.)
The web server at 192.168.0.10 is reachable from the source host.
DNS cannot resolve the IP address for the server web-s1.cisco.com.
A router is down between the source host and the server web-s1.cisco.com.
There is a problem with the web server software on web-s1.cisco.com.
The default gateway between the source host and the server at 192.168.0.10 is down.
Explanation: Topic 12.5.12
The successful result of the ping to the IP address indicates that the network is operational and the web server is online. However, the fact that the ping to the domain name of the server fails indicates there is a DNS issue, namely that the host cannot resolve the domain name to its associated IP address.
165. What type of traffic is described as tending to be unpredictable, inconsistent, and bursty?
video
voice
data
Explanation: Topic 9.2.4
Video traffic is specifically described as tending to be unpredictable, inconsistent, and bursty. This is because the number and size of video packets vary significantly every 33 ms based on the complexity of the content; for example, rapidly changing action sequences require larger packets and higher volume compared to more static scenes. In contrast, voice traffic is defined as predictable and smooth.
166. Match the functions to the corresponding layers. (Not all options are used.)
Explanation: Topic 11.1.5
access layer
distribution layer
core layer
provides network access to the user
implements network access policy
provides high-speed backbone connectivity
represents the network edge
establishes Layer 3 routing boundaries
functions as an aggregator for all the campus blocks
167. What type of traffic is described as consisting of traffic that requires a higher priority if interactive?
voice
data
video
Explanation: Topic 9.2.5
While voice and video traffic are inherently sensitive to delay and always require high priority, data traffic priority is determined by specific factors. According to the sources, a network administrator must evaluate if data comes from an interactive application; if it is interactive and mission-critical, it should be prioritized to achieve a response time of 1 to 2 seconds. Non-interactive data, by contrast, is less sensitive to delay and can use leftover bandwidth.
168. Which type of VPN provides a flexible option to connect a central site with branch sites?
IPsec virtual tunnel interface
MPLS VPN
dynamic multipoint VPN
GRE over IPsec
Explanation: Topic 8.2.5
Dynamic Multipoint VPN (DMVPN) is a Cisco software solution that simplifies tunnel configuration and provides a flexible option to connect a central site with branch sites. It uses a hub-and-spoke configuration to establish what effectively becomes a full mesh topology, allowing branch (spoke) sites to communicate through a central (hub) site and dynamically establish direct tunnels with each other.
169. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use fuzzers?
to discover security vulnerabilities of a computer
to detect any evidence of a hack or malware in a computer or network
to reverse engineer binary files when writing exploits and when analyzing malware
to detect installed tools within files and directories that provide threat actors remote access and control over a computer or network
Explanation: Topic 3.3.3
Fuzzers are specialized penetration testing tools used to discover security vulnerabilities within a computer or application. They operate by providing large amounts of random or unexpected data as input to a system to identify potential weaknesses, crashes, or unintended behaviors that could be exploited by a threat actor. Examples of such tools mentioned in the sources include Skipfish, Wapiti, and W3af.
170. Refer to the exhibit. A network administrator has configured a standard ACL to permit only the two LAN networks attached to R1 to access the network that connects to R2 G0/1 interface, but not the G0/0 interface. When following the best practices, in what location should the standard ACL be applied?
R1 S0/0/0 outbound
R2 G0/0 outbound
R2 S0/0/1 outbound
R1 S0/0/0 inbound
R2 G0/1 inbound
Explanation: Topic 4.4.4
Standard ACLs should be placed as close to the destination as possible. This is because standard ACLs only filter based on the source IPv4 address; applying them too close to the source would block the traffic from reaching all other possible destinations. By applying the ACL outbound on R2's G0/0 interface, the administrator specifically prevents traffic from R1's LANs from entering that particular network while ensuring the packets can still successfully reach the network connected to R2's G0/1 interface.
171. Two OSPF-enabled routers are connected over a point-to-point link. During the ExStart state, which router will be chosen as the first one to send DBD packets?
the router with the highest router ID
the router with the lowest IP address on the connecting interface
the router with the highest IP address on the connecting interface
the router with the lowest router ID
Explanation: Topic 1.3.4
In the ExStart state, the two routers decide which router will send the DBD packets first. The router with the higher router ID will be the first router to send DBD packets during the Exchange state
172. Which step in the link-state routing process is described by a router sending Hello packets out all of the OSPF-enabled interfaces?
exchanging link-state advertisements
electing the designated router
injecting the default route
establishing neighbor adjacencies
Explanation: Topic 1.1.3
OSPF-enabled routers must recognize each other on the network before they can share information. An OSPF-enabled router sends Hello packets out all OSPF-enabled interfaces to determine if neighbors are present on those links. If a neighbor is present, the OSPF-enabled router attempts to establish a neighbor adjacency with that neighbor.
173. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use forensic tools?
to obtain specially designed operating systems preloaded with tools optimized for hacking
to detect any evidence of a hack or malware in a computer or network
to detect installed tools within files and directories that provide threat actors remote access and control over a computer or network
to reverse engineer binary files when writing exploits and when analyzing malware
Explanation: Topic 3.3.3
Forensic tools are used by security professionals to sniff out any trace of evidence existing in a computer. During a penetration test, these tools allow a team to identify residues of previous hacks or the presence of malware that may otherwise remain hidden within the system. Examples of such tools include Sleuth Kit, Helix, Maltego, and Encase.
174. Refer to the exhibit. A network administrator has configured OSPFv2 on the two Cisco routers but PC1 is unable to connect to PC2. What is the most likely problem?
Interface Fa0/0 has not been activated for OSPFv2 on router R2.
Interface Fa0/0 is configured as a passive-interface on router R2.
Interface S0/0 is configured as a passive-interface on router R2.
Interface s0/0 has not been activated for OSPFv2 on router R2.
Explanation: Topic 2.2.4
If a LAN network is not advertised using OSPFv2, a remote network will not be reachable. The output displays a successful neighbor adjacency between router R1 and R2 on the interface S0/0 of both routers.
175. ABCTech is investigating the use of automation for some of its products. In order to control and test these products, the programmers require Windows, Linux, and MAC OS on their computers. What service or technology would support this requirement?
dedicated servers
software defined networking
virtualization
Cisco ACI
Explanation: Topic 13.2.3
Virtualization is the technology that separates the operating system (OS) from the underlying hardware. This separation allows multiple operating systems—such as Windows, Linux, and MAC OS—to exist and run simultaneously on a single hardware platform. Specifically, Type 2 hypervisors can be installed on a programmer's computer to create virtual machine instances for each required OS, providing isolated environments for controlling and testing automated products.
176. A network engineer has noted that some expected network route entries are not displayed in the routing table. Which two commands will provide additional information about the state of router adjacencies, timer intervals, and the area ID? (Choose two.)
show ip protocols
show ip ospf neighbor
show running-configuration
show ip ospf interface
show ip route ospf
Explanation: Topic 2.6
The show ip ospf interface command will display routing table information that is already known. The show running-configuration and show ip protocols commands will display aspects of the OSPF configuration on the router but will not display adjacency state details or timer interval details.
177. Which type of VPN involves the forwarding of traffic over the backbone through the use of labels distributed among core routers?
MPLS VPN
GRE over IPsec
IPsec virtual tunnel interface
dynamic multipoint VPN
Explanation: Topic 8.2.7
Multiprotocol Label Switching (MPLS) is used by service providers in their core networks to forward traffic through the MPLS backbone. This process involves the use of labels that are previously distributed among the core routers to determine the next hop for a packet. This mechanism allows the provider to create secure, virtual paths between client sites that effectively segregate their traffic from other customers.
178. Which type of VPN involves a nonsecure tunneling protocol being encapsulated by IPsec?
SSL VPN
dynamic multipoint VPN
GRE over IPsec
IPsec virtual tunnel interface
Explanation: Topic 8.2.4
Generic Routing Encapsulation (GRE) is a non-secure tunneling protocol that can encapsulate various network layer protocols but lacks built-in encryption services. To secure the communication, a GRE packet is encapsulated into an IPsec packet, which provides the necessary encryption and authentication to protect the data as it travels across an untrusted network. This approach allows for the secure transport of multicast and routing protocol traffic, which standard IPsec VPNs cannot handle alone.
179. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use hacking operation systems?
to detect any evidence of a hack or malware in a computer or network
to obtain specially designed operating systems preloaded with tools optimized for hacking
to encode data, using algorithm schemes, to prevent unauthorized access to the encrypted data
to reverse engineer binary files when writing exploits and when analyzing malware
Explanation: Topic 3.3.3
Hacking operating systems are specially designed operating systems that come preloaded with tools optimized for hacking. These environments, such as Kali Linux, Knoppix, and BackBox Linux, provide security professionals with a comprehensive suite of integrated tools necessary to perform various stages of a penetration test efficiently. In contrast, forensic tools are used to detect evidence of hacks, and debuggers are used for reverse engineering.
180. What command would be used as part of configuring NAT or PAT to identify an interface as part of the external global network?
ip pat inside
access-list 10 permit 172.19.89.0 0.0.0.255
ip nat inside
ip nat outside
Explanation: Topic 6.4.2
To configure NAT or PAT, a network administrator must identify the role of each interface involved in the translation process. The ip nat outside command is used in interface configuration mode to designate an interface as being connected to the external global network, which is typically the public internet. Traffic exiting this interface will have its source address translated from a private (local) address to a public (global) address.
181. To avoid purchasing new hardware, a company wants to take advantage of idle system resources and consolidate the number of servers while allowing for multiple operating systems on a single hardware platform. What service or technology would support this requirement?
data center
cloud services
virtualization
dedicated servers
Explanation: Topic 13.2.3
Server virtualization takes advantage of idle resources and consolidates the number of required servers. This also allows for multiple operating systems to exist on a single hardware platform.
182. Which type of VPN routes packets through virtual tunnel interfaces for encryption and forwarding?
MPLS VPN
IPsec virtual tunnel interface
dynamic multipoint VPN
GRE over IPsec
Explanation: Topic 8.2.6
IPsec Virtual Tunnel Interface (VTI) simplifies VPN configuration by applying IPsec settings to a virtual interface rather than mapping them statically to a physical interface. In this mechanism, packets are routed directly to the VTI, which then encrypts and forwards the traffic to the physical exit interface. Because the VTI is seen as a routable interface, it natively supports both unicast and multicast encrypted traffic, including routing protocols, without the need for additional GRE encapsulation.
183. Which step in the link-state routing process is described by a router flooding link-state and cost information about each directly connected link?
building the topology table
selecting the router ID
exchanging link-state advertisements
injecting the default route
Explanation: Topic 1.1.3
According to the link-state routing process, once neighbor adjacencies are established, routers begin exchanging link-state advertisements (LSAs). During this step, each router floods information regarding the state and cost of its directly connected links to its neighbors. These neighbors then immediately forward the information to their own neighbors until all routers in the OSPF area possess identical link-state information.
184. What type of traffic is described as using either TCP or UDP depending on the need for error recovery?
video
voice
data
Explanation: Topic 9.2.5
Data traffic consists of applications that use either TCP or UDP based on their specific requirements. While real-time traffic like voice and video typically use UDP, data applications that have no tolerance for data loss (such as email and web pages) use TCP because it performs error recovery to ensure that any packets lost in transit are resent.
185. Refer to the exhibit. The company CEO demands that one ACL be created to permit email traffic to the internet and deny FTP access. What is the best ACL type and placement to use in this situation?
extended ACL outbound on R2 WAN interface towards the internet
standard ACL outbound on R2 S0/0/0
extended ACL inbound on R2 S0/0/0
standard ACL inbound on R2 WAN interface connecting to the internet
Explanation: Topic 4.4.3
ACL Type: An extended ACL is required because the CEO's demand involves filtering traffic based on specific applications (email and FTP), which necessitates inspecting Layer 4 protocol and port information. Standard ACLs are insufficient as they only filter based on the source IPv4 address.
Placement: To satisfy the requirement of using only one ACL to control traffic from multiple internal segments (R1's LANs and R3's Server), the ACL must be placed at a common exit point. Applying the ACL outbound on the R2 WAN interface ensures that all traffic from the entire organization is inspected and filtered before it enters the internet.
186. What command would be used as part of configuring NAT or PAT to define a pool of addresses for translation?
ip nat inside source static 172.19.89.13 198.133.219.65
ip nat inside source list 24 interface serial 0/1/0 overload
ip nat pool POOL-STAT 64.100.14.17 64.100.14.30 netmask 255.255.255.240
ip nat outside
Explanation: Topic 6.5.2
The ip nat pool command is used to define the pool of public IPv4 addresses that will be used for translation in dynamic NAT or PAT configurations. This command requires a pool name, a starting and ending IPv4 address, and either a netmask or prefix-length to specify the range of available global addresses. The other commands listed are used for static mapping, applying PAT to a specific interface, or identifying the NAT outside interface.
187. What is the name of the layer in the Cisco borderless switched network design that is considered to be the backbone used for high-speed connectivity and fault isolation?
data link
access
core
network
network access
Explanation: Topic 11.1.5
The three layers of the Cisco borderless switch network design are access, distribution, and core. The access layer switches are the ones used to connect end devices to the network. The distribution layer switches accept connections from access layer switches and provides switching, routing, and access policy functions. The core layer is called the backbone and core switches commonly have high-speed redundant connections.
188. An ACL is applied inbound on router interface. The ACL consists of a single entry:
access-list 210 permit tcp 172.18.20.0 0.0.0.47 any eq ftp
If a packet with a source address of 172.18.20.40, a destination address of 10.33.19.2, and a protocol of 21 is received on the interface, is the packet permitted or denied?
permitted
denied
Explanation: Topic 4.2.1
The packet is permitted because it satisfies all the criteria defined in the Access Control Entry (ACE):
Protocol and Port: The ACE specifies TCP and the port ftp (which corresponds to port 21). The packet uses protocol 21, creating a match.
Source Address: The ACE uses the network 172.18.20.0 with a wildcard mask of 0.0.0.47. In binary, the mask 47 is 00101111, meaning the router must match the bits in the 128, 64, and 16 positions (where the wildcard is 0). The packet source .40 in binary is 00101000. Since the bits in the 128, 64, and 16 positions are all 0 in both the ACE and the packet, the source address is a match.
Destination: The ACE specifies any, which matches the packet's destination address of 10.33.19.2.
Since a match is found on this permit statement, the router carries out the instruction and allows the packet to pass.
189. What type of traffic is described as consisting of traffic that gets a lower priority if it is not mission-critical?
video
data
voice
Explanation: Topic 9.2.5
The priority of data traffic is determined by whether the application is interactive or mission-critical. While voice and video traffic inherently require high priority, data traffic that is not mission-critical and not interactive is assigned a lower priority, essentially receiving only the leftover bandwidth after all other needs are met. In contrast, voice and video are always sensitive to delay and typically receive higher priority.
190. Which OSPF table is identical on all converged routers within the same OSPF area?
routing
neighbor
adjacency
topology
Explanation: Topic 1.1.2
The topology table, also known as the Link-state Database (LSDB), represents the network map by listing information about all other routers in the area. For OSPF to calculate accurate routes using the SPF algorithm, all converged routers within a specific area must maintain an identical LSDB. In contrast, the neighbor and routing tables are unique to each individual router.
191. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
access-list 100 permit tcp 192.168.10.0 0.0.0.255 any eq www .
If a packet with a source address of 192.168.10.45, a destination address of 10.10.3.27, and a protocol of 80 is received on the interface, is the packet permitted or denied?
permitted
denied
Explanation: Topic 5.4.4
The packet matches all criteria defined in the extended ACL entry. Specifically, the source address 192.168.10.45 falls within the range of the 192.168.10.0 0.0.0.255 subnet. The destination address matches the any keyword. Finally, protocol 80 is the standard port for www (HTTP), which uses the tcp protocol as specified in the entry. Since all conditions match, the packet is permitted.
192. What protocol allows the manager to poll agents to access information from the agent MIB?
CBWFQ
SYSLOG
TFTP
SNMP
Explanation: Topic 10.4.2
SNMP (Simple Network Management Protocol) is an application layer protocol that facilitates communication between network managers and agents. The SNMP manager uses the agent to poll and query the MIB (Management Information Base) for device data and operational statistics using "get" requests.
193. Match each component of a WAN connection to its description. (Not all options are used.) Case 2:
Explanation: Topic 7.2.3
194. What type of traffic is described as being able to tolerate a certain amount of latency, jitter, and loss without any noticeable effects?
voice
video
data
Explanation: Topic 9.2.3
Voice traffic is described as smooth and predictable but very sensitive to delays. It can tolerate a specific amount of latency (up to 150 ms), jitter (up to 30 ms), and packet loss (up to 1%) without users experiencing any noticeable effects on quality. While video traffic has similar tolerances, it is considered less resilient to loss than voice. In contrast, data traffic is typically insensitive to delay and jitter but cannot tolerate any loss.
195. What term describes adding a value to the packet header, as close to the source as possible, so that the packet matches a defined policy?
policing
traffic marking
weighted random early detection (WRED)
traffic shaping
tail drop
Explanation: Topic 9.5.4 Traffic marking is the process of adding a specific value to the packet header (such as CoS at Layer 2 or DSCP at Layer 3). This allows subsequent network devices to identify the traffic class and apply defined forwarding policies accordingly. For maximum efficiency, marking should be performed as close to the source as possible to establish a trust boundary.
196. Which three traffic-related factors would influence selecting a particular WAN link type? (Choose three.)
cost of the link
amount of traffic
distance between sites
reliability
security needs
type of traffic
Explanation: Topic 7.1.5
The traffic-related factors that influence selecting a particular WAN link type include the type of traffic, amount of traffic, quality requirements, and security requirements. Quality requirements include ensuring that traffic that cannot tolerate delay gets priority treatment as well as important business transactional traffic.
197. What command would be used as part of configuring NAT or PAT to link the inside local addresses to the pool of addresses available for PAT translation?
ip nat inside source list ACCTNG pool POOL-STAT
ip nat translation timeout 36000
ip nat inside source list 14 pool POOL-STAT overload
ip nat inside source static 172.19.89.13 198.133.219.65
Explanation: Topic 6.6.3
The traffic-related factors that influence selecting a particular WAN link type include the type of traffic, amount of traffic, quality requirements, and security requirements. Quality requirements include ensuring that traffic that cannot tolerate delay gets priority treatment as well as important business transactional traffic.
198. What protocol is a vendor-neutral Layer 2 discovery protocol that must be configured separately to transmit and receive information packets?
SNMP
MPLS
LLDP
NTP
Explanation: Topic 10.2.2
Link Layer Discovery Protocol (LLDP) is a vendor-neutral Layer 2 discovery protocol. Unlike Cisco proprietary protocols, LLDP requires separate configuration for an interface to transmit and receive information packets using specific commands like lldp transmit and lldp receive.
199. An ACL is applied inbound on a router interface. The ACL consists of a single entry: access-list 210 permit tcp 172.18.20.0 0.0.0.31 172.18.20.32 0.0.0.31 eq ftp .
If a packet with a source address of 172.18.20.55, a destination address of 172.18.20.3, and a protocol of 21 is received on the interface, is the packet permitted or denied?
permitted
denied
Explanation: Topic 4.2.1
The packet is denied because it fails to match the criteria of the single permit entry, triggering the implicit deny. Specifically, the source address 172.18.20.55 falls outside the permitted range of 172.18.20.0 to 172.18.20.31 (defined by wildcard 0.0.0.31). Additionally, the destination address 172.18.20.3 does not match the permitted range of 172.18.20.32 to 172.18.20.63. In ACL processing, if a packet does not match any explicit permit statement, it is automatically discarded.
200. Refer to the exhibit. Corporate policy demands that access to the server network be restricted to internal employees only. What is the best ACL type and placement to use in this situation?
Corporate policy demands that access to the server network be restricted to internal employees only. What is the best ACL type and placement to use in this situation
extended ACL outbound on R2 S0/0/1
standard ACL outbound on R2 S0/0/0
standard ACL inbound on R2 WAN interface connecting to the internet
extended ACL inbound on R2 S0/0/0
Explanation: Topic 4.4.3
ACL Type: An extended ACL is the best choice because it allows for filtering based on both the source address (identifying internal employees versus internet users) and the destination address (the specific server network).
Placement: According to the sources, outbound ACLs are most effective when a single filter must be applied to traffic arriving from multiple inbound interfaces. In this topology, traffic destined for the server network enters R2 through two different points: the internet WAN interface and the R1 serial interface (S0/0/0). Placing the ACL outbound on R2 S0/0/1 ensures that all traffic from both sources is filtered at this single "choke point" before it is sent to R3 and the server network.
201. A technician is working on a Layer 2 switch and notices that a %CDP-4-DUPLEX_MISMATCH message keeps appearing for port G0/5. What command should the technician issue on the switch to start the troubleshooting process?
show cdp neighbors
show ip interface brief
show interface g0/5
show cdp
Explanation: Topic 12.5.4
The %CDP-4-DUPLEX_MISMATCH message indicates that the local interface and its connected neighbor have conflicting duplex settings. To start troubleshooting, the technician must verify the operational status and configuration of the specific port mentioned in the error. The show interface g0/5 command provides detailed information, including whether the port is currently operating in full-duplex or half-duplex mode, allowing the technician to identify the mismatch.
202. Which virtual resource would be installed on a network server to provide direct access to hardware resources?
VMware Fusion
a management console
a dedicated VLAN
a Type 1 hypervisor
Explanation: Topic 13.3.1
Type 1 hypervisors, the hypervisor is installed directly on the server or networking hardware. Then, instances of an OS are installed on the hypervisor, as shown in the figure. Type 1 hypervisors have direct access to the hardware resources. Therefore, they are more efficient than hosted architectures. Type 1 hypervisors improve scalability, performance, and robustness.
203. Refer to the exhibit. A network administrator has configured a standard ACL to permit only the two LAN networks attached to R1 to access the network that connects to R2 G0/1 interface. When following the best practices, in what location should the standard ACL be applied?
Enterprise Networking, Security, and Automation ( Version 7.00) - ENSA Final Exam
R2 G0/1 inbound
R2 S0/0/1 outbound
R1 S0/0/0 outbound
R2 G0/1 outbound
R2 G0/0 outbound
Explanation: Topic 4.4.4
Following network best practices, standard ACLs should be placed as close to the destination as possible. In this topology, the destination is the network connected to interface G0/1 on R2. Applying the ACL outbound on R2 G0/1 ensures that traffic from the R1 LANs is permitted to that specific network without inadvertently blocking traffic destined for other networks, such as the LAN connected to R2 G0/0. Placing a standard ACL closer to the source (e.g., on R1) would block those source networks from reaching any other destination reachable through that interface.
204. Which OSPF database is identical on all converged routers within the same OSPF area?
neighbor
forwarding
link-state
adjacency
Explanation: Topic 1.1.2
Regardless of which OSPF area a router resides in, the adjacency database, routing table, and forwarding database are unique for each router. The link-state database lists information about all other routers within an area and is identical across all OSPF routers participating in that area.
205. What are two features to consider when creating a named ACL? (Choose two.)
Use alphanumeric characters if needed.
Use special characters, such as ! or * to show the importance of the ACL.
Modify the ACL using a text editor.
Be descriptive when creating the ACL name.
Use a space for ease of reading to separate the name from the description
Explanation: Topic 4.4.2
The following summarizes the rules to follow for named ACLs:
Assign a name to identify the purpose of the ACL.
Names can contain alphanumeric characters.
Names cannot contain spaces or punctuation.
It is suggested that the name be written in CAPITAL LETTERS.
Entries can be added or deleted within the ACL.
206. Match the RESTful API method to CRUD function.
Match the RESTful API method to CRUD function.
Explanation: Topic 14.4.3
207. What type of traffic is described as requiring at least 384 Kbps of bandwidth?
voice
data
video
Explanation: Topic 9.2.4
Video traffic is more demanding than voice traffic because of its higher volume of data per packet. It is specifically described as requiring at least 384 Kbps of bandwidth to maintain an acceptable user experience. In contrast, voice traffic requires a minimum of only 30 Kbps.
208. Which step in the link-state routing process is described by a router inserting best paths into the routing table?
declaring a neighbor to be inaccessible
executing the SPF algorithm
load balancing equal-cost paths
choosing the best route
Explanation: Topic 1.1.3
This is the final step in the generic link-state routing process. After the SPF algorithm creates the SPF tree, the router identifies the shortest paths to each destination and offers them to the IP routing table. These best paths are then inserted into the routing table unless a route to the same network with a lower administrative distance exists.
209. Anycompany has decided to reduce its environmental footprint by reducing energy costs, moving to a smaller facility, and promoting telecommuting. What service or technology would support this requirement?
data center
virtualization
cloud services
dedicated servers
Explanation: Topic 13.1.2 Cloud services support these requirements by providing off-premise, on-demand access to a shared pool of computing resources. By reducing or eliminating the need for onsite IT equipment, cloud services allow an organization to move to a smaller facility and reduce overhead related to the physical plant. This technology reduces energy costs and the overall environmental footprint by utilizing resources more efficiently and shifting infrastructure needs to the provider. Finally, it facilitates telecommuting by enabling secure access to organizational data from any location and at any time.
210. Which QoS technique smooths packet output rate?
policing
shaping
weighted random early detection
Integrated Services (IntServ)
marking
Explanation: Topic 9.5.12
Traffic shaping is a QoS mechanism that retains excess packets in a queue and schedules them for transmission over time. This process results in a smoothed packet output rate. Unlike policing, which drops excess traffic immediately, shaping requires a queue and sufficient memory to buffer and delay packets for later transmission.
211. Refer to the exhibit. The company has provided IP phones to employees on the 192.168.10.0/24 network and the voice traffic will need priority over data traffic. What is the best ACL type and placement to use in this situation?
extended ACL inbound on R1 G0/0
extended ACL outbound on R2 WAN interface towards the internet
extended ACL outbound on R2 S0/0/1
extended ACLs inbound on R1 G0/0 and G0/1
Explanation: Topic 4.4.3
Standard ACLs permit or deny packets based only on the source IPv4 address. Because all traffic types are permitted or denied, standard ACLs should be located as close to the destination as possible.
Extended ACLs permit or deny packets based on the source IPv4 address and destination IPv4 address, protocol type, source and destination TCP or UDP ports and more. Because the filtering of extended ACLs is so specific, extended ACLs should be located as close as possible to the source of the traffic to be filtered. Undesirable traffic is denied close to the source network without crossing the network infrastructure.
212. A network technician is configuring SNMPv3 and has set a security level of SNMPv3 authPriv. What is a feature of using this level?
authenticates a packet by using the SHA algorithm only
authenticates a packet by a string match of the username or community string
authenticates a packet by using either the HMAC with MD5 method or the SHA method
authenticates a packet by using either the HMAC MD5 or HMAC SHA algorithms and a username
Explanation: Topic 10.4.4
The SNMPv3 authPriv security level provides the highest level of protection by combining authentication and encryption. It uses the User-based Security Model (USM), which authenticates packets by using a username in conjunction with either the HMAC-MD5 or HMAC-SHA algorithms. Additionally, the authPriv level adds confidentiality by encrypting the data using algorithms like DES, 3DES, or AES.
The ITExamAnswers Editorial Team is a dedicated group of certified IT professionals and network engineers. We rigorously review, verify, and update all exam materials to ensure you receive the most accurate and reliable resources for your certification journey.