CCNAv7 Switching, Routing, and Wireless Essentials v7.0 (SRWE) Answers
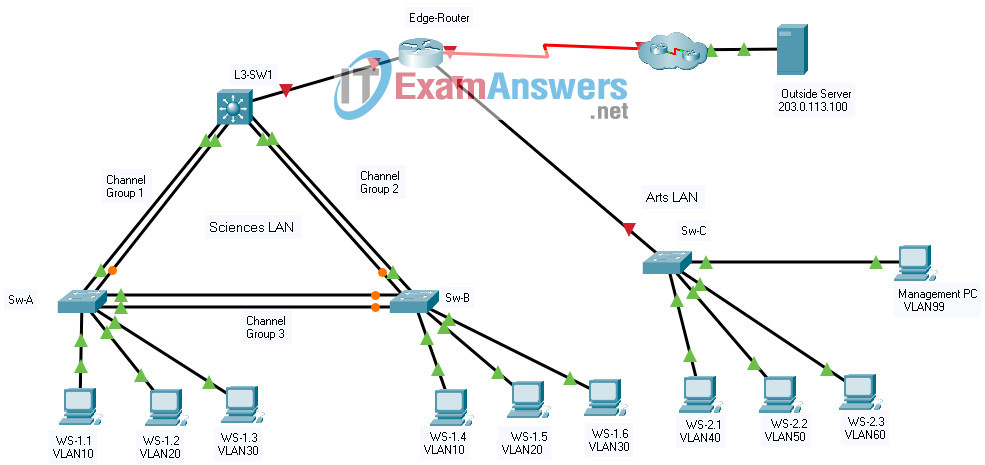
SRWE PT Practice Skills Assessment (PTSA) Part 1
SRWE PT Practice Skills Assessment (PTSA) Part 1
A few things to keep in mind while completing this activity:
- Do not use the browser Back button or close or reload any exam windows during the exam.
- Do not close Packet Tracer when you are done. It will close automatically.
- Click the Submit Assessment button in the browser window to submit your work.
Introduction
In this assessment you are configuring a network that is using EtherChannel and routing between VLANs. For the sake of time, you will not be asked to perform all configurations on all network devices as you may be required to do in a real network or other assessment. Instead, you will use the skills and knowledge that you have learned in the labs in this course to configure the router and switches in the topology. In addition to EtherChannel and inter-VLAN routing, this task involves creating VLANs and trunks, and performing basic router and switch configuration.
You are required to configure host default gateways; however host addresses are preconfigured.
You will practice and be assessed on the following skills:
- Configuration of initial settings on a router.
- Configuration of initial settings on a switch, including SVI and SSH.
- Configuration of VLANs.
- Configuration of switchport VLAN membership.
- EtherChannel configuration.
- Troubleshooting VLANs.
- Configuration of static trunking and DTP.
- Configuration of routing between VLANs on a Layer 3 switch.
- Configuration of router-on-a-stick inter-VLAN routing on a router.
- Configure default gateways on hosts.
Addressing Table
| Device | Interface | IP Address | Subnet Mask |
|---|---|---|---|
| Edge-Router | G0/0/0 | 192.168.0.1 | 255.255.255.0 |
| G0/0/1.40 | 192.168.40.1 | 255.255.255.0 | |
| G0/0/1.50 | 192.168.50.1 | 255.255.255.0 | |
| G0/0/1.60 | 192.168.60.1 | 255.255.255.0 | |
| G0/0/1.99 | 192.168.99.17 | 255.255.255.240 | |
| S0/1/0 | 209.165.201.2 | 255.255.255.252 | |
| L3-SW1 | G1/1/1 | 192.168.0.2 | 255.255.255.0 |
| VLAN10 | 192.168.10.1 | 255.255.255.0 | |
| VLAN20 | 192.168.20.1 | 255.255.255.0 | |
| VLAN30 | 192.168.30.1 | 255.255.255.0 | |
| Sw-C | VLAN99 | 192.168.99.18 | 255.255.255.240 |
| WS-1.1 | NIC | 192.168.10.10 | 255.255.255.0 |
| WS-1.2 | NIC | 192.168.20.20 | 255.255.255.0 |
| WS-1.3 | NIC | 192.168.30.30 | 255.255.255.0 |
| WS-1.4 | NIC | 192.168.10.11 | 255.255.255.0 |
| WS-1.5 | NIC | 192.168.20.21 | 255.255.255.0 |
| WS-1.6 | NIC | 192.168.30.31 | 255.255.255.0 |
| WS-2.1 | NIC | 192.168.40.40 | 255.255.255.0 |
| WS-2.2 | NIC | 192.168.50.50 | 255.255.255.0 |
| WS-2.3 | NIC | 192.168.60.60 | 255.255.255.0 |
| Management PC | NIC | 192.168.99.19 | 255.255.255.240 |
| Outside Server | NIC | 203.0.113.100 | 255.255.255.0 |
Background / Scenario
A corporation is planning to implement EtherChannel and a new VLAN design in order to make the network more efficient. You have been asked to work on a design and prototype of the new network. You have created the logical topology and now need to configure the devices in order to evaluate the design. You will configure VLANs and access port VLAN membership on access layer switches. You will also configure EtherChannel and trunking. Finally, you will configure a router and a Layer 3 switch to route between VLANs. Some addressing had already been configured.
Instructions
Part 1: Basic Router Configuration
Step 1: Configure router Edge-Router with required settings.
a. Open a command window on router Edge-Router and move to privileged EXEC mode.
Router> enable
b. Copy and paste the following configuration into the Edge-Router router CLI.
ip route 192.168.10.0 255.255.255.0 GigabitEthernet0/0/0

ip route 192.168.20.0 255.255.255.0 GigabitEthernet0/0/0

ip route 192.168.30.0 255.255.255.0 GigabitEthernet0/0/0
Be sure to press the <Enter> key after the last line to return to privileged EXEC mode prompt.
c. Configure the following settings on the router:
- The enable secret password.
Router(config)# enable secret class
- A console password.
Router(config)# line console 0
Router(config-line)# password cisco
Router(config-line)# login
- Remote access to the VTY lines.
Router(config)# line vty 0 4
Router(config-line)# password cisco
Router(config-line)# login
- A banner MOTD message.
Router(config)# banner motd #Authorized Access Only!#
- The device hostname according to the value in the addressing table.
Router(config)# hostname Edge-Router
- All clear text passwords should be encrypted.
Edge-Router(config)# service password-encryption
- Interface addressing on G0/0/0 and S0/1/0.
Edge-Router(config)# interface gigabitethernet 0/0/0
Edge-Router(config-if)# ip address 192.168.0.1 255.255.255.0
Edge-Router(config-if)# no shutdown
Edge-Router(config-if)# interface serial 0/1/0
Edge-Router(config-if)# ip address 209.165.201.2 255.255.255.252
Edge-Router(config-if)# no shutdown
- Interface descriptions on G0/0/0 and S0/1/0.
Edge-Router(config)# interface gigabitethernet 0/0/0
Edge-Router(config-if)# description Link to L3-SW1 G1/1/1
Edge-Router(config-if)# interface serial 0/1/0
Edge-Router(config-if)# description Link to ISP
Note: Be sure to make a record of the passwords that you create.
Part 2: Basic Switch Configuration
Step 1: Configure Remote Management Addressing
a. Configure SVI 99 on switch Sw-C with IP addressing according to the Addressing Table.
Sw-C(config)# interface vlan 99
Sw-C(config-if)# ip address 192.168.99.18 255.255.255.240
Sw-C(config-if)# no shutdown
b. The Sw-C switch SVI should be reachable from other networks.
Sw-C(config)# ip default-gateway 192.168.99.17
Step 2: Configure Secure Remote Access
On switch Sw-C, configure SSH as follows:
- Username: admin encrypted password: C1sco123!
Sw-C(config)# username admin privilege 15 secret C1sco123!
- Modulus bits 1024
Sw-C(config)# ip domain-name acad.pt
Sw-C(config)# crypto key generate rsa general-keys modulus 1024
- All VTY lines should accept SSH connections only.
Sw-C(config)# line vty 0 15
Sw-C(config-line)# transport input ssh
- Connections should require the previously configured username and password.
Sw-C(config)# line vty 0 15
Sw-C(config-line)# login local
- IP domain name: acad.pt
Sw-C(config)# ip domain-name acad.pt
The assessment also checks the enable secret password on Sw-C:
Sw-C(config)# enable secret class
Part 3: VLAN Configuration
Step 1: Configure VLANs according to the VLAN table.
Use the VLAN Table to create and name the VLANs on the appropriate switches.
VLAN Table
| VLAN | Name | IP Network | Subnet Mask | Devices |
|---|---|---|---|---|
| 10 | FL1 | 192.168.10.0 | 255.255.255.0 | L3-SW1, Sw-A, |
| Sw-B | ||||
| 20 | FL2 | 192.168.20.0 | 255.255.255.0 | L3-SW1, Sw-A, |
| Sw-B | ||||
| 30 | FL3 | 192.168.30.0 | 255.255.255.0 | L3-SW1, Sw-A, |
| Sw-B | ||||
| 40 | BDG4 | 192.168.40.0 | 255.255.255.0 | Sw-C |
| 50 | BDG5 | 192.168.50.0 | 255.255.255.0 | Sw-C |
| 60 | BDG6 | 192.168.60.0 | 255.255.255.0 | Sw-C |
| 99 | Management | 192.168.99.16 | 255.255.255.240 | Sw-C |
Note: In some exam IDs, L3-SW1 still has the default name (prompt Switch#). Set its hostname according to the Addressing Table first; the command is harmless if the switch is already named.
L3-SW1:
Switch(config)# hostname L3-SW1
L3-SW1(config)# vlan 10
L3-SW1(config-vlan)# name FL1
L3-SW1(config-vlan)# vlan 20
L3-SW1(config-vlan)# name FL2
L3-SW1(config-vlan)# vlan 30
L3-SW1(config-vlan)# name FL3
Sw-A:
Sw-A(config)# vlan 10
Sw-A(config-vlan)# name FL1
Sw-A(config-vlan)# vlan 20
Sw-A(config-vlan)# name FL2
Sw-A(config-vlan)# vlan 30
Sw-A(config-vlan)# name FL3
Sw-B:
Sw-B(config)# vlan 10
Sw-B(config-vlan)# name FL1
Sw-B(config-vlan)# vlan 20
Sw-B(config-vlan)# name FL2
Sw-B(config-vlan)# vlan 30
Sw-B(config-vlan)# name FL3
Sw-C:
Sw-C(config)# vlan 40
Sw-C(config-vlan)# name BDG4
Sw-C(config-vlan)# vlan 50
Sw-C(config-vlan)# name BDG5
Sw-C(config-vlan)# vlan 60
Sw-C(config-vlan)# name BDG6
Sw-C(config-vlan)# vlan 99
Sw-C(config-vlan)# name Management
Step 2: Assign switch ports to VLANs.
Assign VLAN membership to static access switchports according to the Port to VLAN Assignment table.
Port to VLAN Assignment Table
| Device | VLAN | VLAN Name | Port Assignments |
|---|---|---|---|
| Sw-A | 10 | FL1 | F0/7-10 |
| 20 | FL2 | F0/11-15 | |
| 30 | FL3 | F0/16-24 | |
| Sw-B | 10 | FL1 | F0/7-10 |
| 20 | FL2 | F0/11-15 | |
| 30 | FL3 | F0/16-24 | |
| Sw-C | 40 | BDG4 | F0/1-5 |
| 50 | BDG5 | F0/6-10 | |
| 60 | BDG6 | F0/11-15 | |
| 99 | Management Native | F0/24 |
Sw-A:
Sw-A(config)# interface range fastethernet 0/7 - 10
Sw-A(config-if-range)# switchport mode access
Sw-A(config-if-range)# switchport access vlan 10
Sw-A(config-if-range)# interface range fastethernet 0/11 - 15
Sw-A(config-if-range)# switchport mode access
Sw-A(config-if-range)# switchport access vlan 20
Sw-A(config-if-range)# interface range fastethernet 0/16 - 24
Sw-A(config-if-range)# switchport mode access
Sw-A(config-if-range)# switchport access vlan 30
Sw-B:
Sw-B(config)# interface range fastethernet 0/7 - 10
Sw-B(config-if-range)# switchport mode access
Sw-B(config-if-range)# switchport access vlan 10
Sw-B(config-if-range)# interface range fastethernet 0/11 - 15
Sw-B(config-if-range)# switchport mode access
Sw-B(config-if-range)# switchport access vlan 20
Sw-B(config-if-range)# interface range fastethernet 0/16 - 24
Sw-B(config-if-range)# switchport mode access
Sw-B(config-if-range)# switchport access vlan 30
Sw-C:
Sw-C(config)# interface range fastethernet 0/1 - 5
Sw-C(config-if-range)# switchport mode access
Sw-C(config-if-range)# switchport access vlan 40
Sw-C(config-if-range)# interface range fastethernet 0/6 - 10
Sw-C(config-if-range)# switchport mode access
Sw-C(config-if-range)# switchport access vlan 50
Sw-C(config-if-range)# interface range fastethernet 0/11 - 15
Sw-C(config-if-range)# switchport mode access
Sw-C(config-if-range)# switchport access vlan 60
Sw-C(config-if-range)# interface fastethernet 0/24
Sw-C(config-if)# switchport mode access
Sw-C(config-if)# switchport access vlan 99
Part 4: EtherChannel and Trunking Configuration
EtherChannel Port Assignments Table
| Channel Group | Devices in Groups | Ports in Group |
|---|---|---|
| 1 | L3-SW1 | G1/0/1, G1/0/2 |
| Sw-A | G0/1, G0/2 | |
| 2 | L3-SW1 | G1/0/3, G1/0/4 |
| Sw-B | G0/1, G0/2 | |
| 3 | Sw-A | F0/5, F0/6 |
| Sw-B | F0/5, F0/6 |
Step 1: Configure EtherChannels
Create EtherChannels according to the EtherChannel Port Assignments Table. Use the Cisco LACP protocol. Both sides of the channel should attempt to negotiate the link protocol.
L3-SW1:
L3-SW1(config)# interface range gigabitethernet 1/0/1 - 2
L3-SW1(config-if-range)# channel-group 1 mode active
L3-SW1(config-if-range)# interface range gigabitethernet 1/0/3 - 4
L3-SW1(config-if-range)# channel-group 2 mode active
Sw-A:
Sw-A(config)# interface range gigabitethernet 0/1 - 2
Sw-A(config-if-range)# channel-group 1 mode active
Sw-A(config-if-range)# interface range fastethernet 0/5 - 6
Sw-A(config-if-range)# channel-group 3 mode active
Sw-B:
Sw-B(config)# interface range gigabitethernet 0/1 - 2
Sw-B(config-if-range)# channel-group 2 mode active
Sw-B(config-if-range)# interface range fastethernet 0/5 - 6
Sw-B(config-if-range)# channel-group 3 mode active
Step 2: Configure Trunking on the EtherChannels
a. Configure the port channel interfaces as static trunks. Disable DTP negotiation on all trunks.
L3-SW1:
L3-SW1(config)# interface port-channel 1
L3-SW1(config-if)# switchport mode trunk
L3-SW1(config-if)# switchport nonegotiate
L3-SW1(config-if)# interface port-channel 2
L3-SW1(config-if)# switchport mode trunk
L3-SW1(config-if)# switchport nonegotiate
Sw-A:
Sw-A(config)# interface port-channel 1
Sw-A(config-if)# switchport mode trunk
Sw-A(config-if)# switchport nonegotiate
Sw-A(config-if)# interface port-channel 3
Sw-A(config-if)# switchport mode trunk
Sw-A(config-if)# switchport nonegotiate
Sw-B:
Sw-B(config)# interface port-channel 2
Sw-B(config-if)# switchport mode trunk
Sw-B(config-if)# switchport nonegotiate
Sw-B(config-if)# interface port-channel 3
Sw-B(config-if)# switchport mode trunk
Sw-B(config-if)# switchport nonegotiate
b. Troubleshoot any issues that prevent the formation of the EtherChannels.
The activity contains intentionally introduced errors on the member ports of channel group 2. This step is scored: the assessment checks the port mode of G0/2 on Sw-B, so it must be fixed to reach 100%. Use show etherchannel summary to find the problem: Po2 is down (SD) and its member ports are suspended (s). Then compare the configuration of the member ports: on L3-SW1, G1/0/4 is missing switchport mode trunk; on Sw-B, G0/2 is missing switchport mode trunk and is set to duplex half. To fix it, remove both member ports from channel group 2, give them the same settings, add them back and restart them.
Before the fix, Po2 is down on both switches and its member ports are suspended:
L3-SW1:
L3-SW1# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

1      Po1(SU)           LACP   Gig1/0/1(P) Gig1/0/2(P)
2 Po2(SD) LACP Gig1/0/3(s) Gig1/0/4(s) L3-SW1# show running-config | begin GigabitEthernet1/0/3
interface GigabitEthernet1/0/3
switchport mode trunk
switchport nonegotiate
channel-group 2 mode active
!
interface GigabitEthernet1/0/4
switchport nonegotiate
channel-group 2 mode active
!
<output omitted>Sw-B:
Sw-B# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

2      Po2(SD)           LACP   Gig0/1(s) Gig0/2(s)
3 Po3(SU) LACP Fa0/5(P) Fa0/6(P) Sw-B# show running-config | begin GigabitEthernet0/1
interface GigabitEthernet0/1
switchport mode trunk
switchport nonegotiate
channel-group 2 mode active
!
interface GigabitEthernet0/2
switchport nonegotiate
duplex half
channel-group 2 mode active
!
<output omitted>Fix the member ports of channel group 2 on both switches:
L3-SW1:
L3-SW1(config)# interface range gigabitethernet 1/0/3 - 4
L3-SW1(config-if-range)# no channel-group 2
L3-SW1(config-if-range)# switchport mode trunk
L3-SW1(config-if-range)# switchport nonegotiate
L3-SW1(config-if-range)# channel-group 2 mode active
L3-SW1(config-if-range)# shutdown
L3-SW1(config-if-range)# no shutdown
Sw-B:
Sw-B(config)# interface range gigabitethernet 0/1 - 2
Sw-B(config-if-range)# no channel-group 2
Sw-B(config-if-range)# switchport mode trunk
Sw-B(config-if-range)# switchport nonegotiate
Sw-B(config-if-range)# duplex auto
Sw-B(config-if-range)# channel-group 2 mode active
Sw-B(config-if-range)# shutdown
Sw-B(config-if-range)# no shutdown
If a member port of Po2 still shows (s) or (I) after both switches are fixed, restart the member ports on both switches once more, then wait for the ports to turn green (or click Fast Forward Time):
L3-SW1:
L3-SW1(config)# interface range gigabitethernet 1/0/3 - 4
L3-SW1(config-if-range)# shutdown
L3-SW1(config-if-range)# no shutdown
Sw-B:
Sw-B(config)# interface range gigabitethernet 0/1 - 2
Sw-B(config-if-range)# shutdown
Sw-B(config-if-range)# no shutdown
Verify that channel group 2 is now in use (SU) on both switches and that all member ports are bundled (P):
L3-SW1:
L3-SW1# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

1      Po1(SU)           LACP   Gig1/0/1(P) Gig1/0/2(P)
2      Po2(SU)           LACP   Gig1/0/3(P) Gig1/0/4(P)
Sw-B:
Sw-B# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

2      Po2(SU)           LACP   Gig0/1(P) Gig0/2(P)
3      Po3(SU)           LACP   Fa0/5(P) Fa0/6(P)
Note: Packet Tracer requires configuration of trunking and DTP mode on both portchannel interfaces and the component physical interfaces.
Step 3: Configure a static trunk uplink
a. On the Sw-C switch, configure the port that is connected to Edge-Router G0/0/1 as a static trunk.
Sw-C(config)# interface gigabitethernet 0/1
Sw-C(config-if)# switchport mode trunk
b. Configure the Management VLAN as the native VLAN.
Sw-C(config-if)# switchport trunk native vlan 99
c. Disable DTP on the port.
Sw-C(config-if)# switchport nonegotiate
Part 5: Configure Inter-VLAN Routing
Step 1: Configure inter-VLAN routing on the Layer 3 switch.
a. Configure Inter-VLAN routing on the L3-SW1 Layer 3 switch for all VLANs in the VLAN Table that are configured on L3-SW1.
L3-SW1(config)# ip routing
L3-SW1(config)# interface vlan 10
L3-SW1(config-if)# ip address 192.168.10.1 255.255.255.0
L3-SW1(config-if)# interface vlan 20
L3-SW1(config-if)# ip address 192.168.20.1 255.255.255.0
L3-SW1(config-if)# interface vlan 30
L3-SW1(config-if)# ip address 192.168.30.1 255.255.255.0
b. Configure the switchport on L3-SW1 that is connected to Edge-Router with an IP address as shown in the Addressing Table.
L3-SW1(config)# interface gigabitethernet 1/1/1
L3-SW1(config-if)# no switchport
L3-SW1(config-if)# ip address 192.168.0.2 255.255.255.0
Step 2: Configure router-on-a-stick inter-VLAN routing on a router.
a. Configure inter-VLAN routing on Edge-Router for all the VLANs that are configured on the Sw-C switch. Use the information in the Addressing Table.
Edge-Router(config)# interface gigabitethernet 0/0/1
Edge-Router(config-if)# no shutdown
Edge-Router(config-if)# interface gigabitethernet 0/0/1.40
Edge-Router(config-subif)# encapsulation dot1q 40
Edge-Router(config-subif)# ip address 192.168.40.1 255.255.255.0
Edge-Router(config-subif)# interface gigabitethernet 0/0/1.50
Edge-Router(config-subif)# encapsulation dot1q 50
Edge-Router(config-subif)# ip address 192.168.50.1 255.255.255.0
Edge-Router(config-subif)# interface gigabitethernet 0/0/1.60
Edge-Router(config-subif)# encapsulation dot1q 60
Edge-Router(config-subif)# ip address 192.168.60.1 255.255.255.0
Edge-Router(config-subif)# interface gigabitethernet 0/0/1.99
Edge-Router(config-subif)# encapsulation dot1q 99 native
Edge-Router(config-subif)# ip address 192.168.99.17 255.255.255.240
b. Be sure to configure descriptions of all interfaces.
Edge-Router(config)# interface gigabitethernet 0/0/1
Edge-Router(config-if)# description Trunk to Sw-C G0/1
Edge-Router(config-if)# interface gigabitethernet 0/0/1.40
Edge-Router(config-subif)# description Gateway for VLAN 40 (BDG4)
Edge-Router(config-subif)# interface gigabitethernet 0/0/1.50
Edge-Router(config-subif)# description Gateway for VLAN 50 (BDG5)
Edge-Router(config-subif)# interface gigabitethernet 0/0/1.60
Edge-Router(config-subif)# description Gateway for VLAN 60 (BDG6)
Edge-Router(config-subif)# interface gigabitethernet 0/0/1.99
Edge-Router(config-subif)# description Gateway for VLAN 99 (Management, native)
Step 3: Configure default gateways on hosts.
a. Configure default gateway addresses on all hosts on the LANs.
| Host | IP Address | Subnet Mask | Default Gateway |
|---|---|---|---|
| WS-1.1 | 192.168.10.10 | 255.255.255.0 | 192.168.10.1 |
| WS-1.2 | 192.168.20.20 | 255.255.255.0 | 192.168.20.1 |
| WS-1.3 | 192.168.30.30 | 255.255.255.0 | 192.168.30.1 |
| WS-1.4 | 192.168.10.11 | 255.255.255.0 | 192.168.10.1 |
| WS-1.5 | 192.168.20.21 | 255.255.255.0 | 192.168.20.1 |
| WS-1.6 | 192.168.30.31 | 255.255.255.0 | 192.168.30.1 |
| WS-2.1 | 192.168.40.40 | 255.255.255.0 | 192.168.40.1 |
| WS-2.2 | 192.168.50.50 | 255.255.255.0 | 192.168.50.1 |
| WS-2.3 | 192.168.60.60 | 255.255.255.0 | 192.168.60.1 |
| Management PC | 192.168.99.19 | 255.255.255.240 | 192.168.99.17 |
b. Verify connectivity between all hosts on both LANs with each other and the Outside Server.
c. Verify that a host can connect to the SVI of switch Sw-C over SSH.
C:\> ssh -l admin 192.168.99.18
Password:
Last Updated: January 2021
ID 200
Device Configs - Final
ROUTER Edge-Router
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 200
!--- ANSWER SCRIPT FOR ROUTER Edge-Router
!--- Usage: copy this whole file and paste it into the Edge-Router terminal (start at the Router> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1: Basic Router Configuration.
! --------------------------------------------------------------

!--- b. Static routes provided by the exam (paste as given).
ip route 192.168.10.0 255.255.255.0 GigabitEthernet0/0/0
ip route 192.168.20.0 255.255.255.0 GigabitEthernet0/0/0
ip route 192.168.30.0 255.255.255.0 GigabitEthernet0/0/0

!--- Optional: stop the router from treating mistyped commands as host names.
no ip domain lookup

!--- c. The enable secret password.
enable secret class

!--- c. A console password.
line console 0
 password cisco
 login
 exit

!--- c. Remote access to the VTY lines.
line vty 0 4
 password cisco
 login
 exit

!--- c. A banner MOTD message.
banner motd #Authorized Access Only!#

!--- c. The device hostname according to the value in the addressing table.
hostname Edge-Router

!--- c. All clear text passwords should be encrypted.
service password-encryption

!--- c. Interface addressing and description on G0/0/0.
interface gigabitethernet 0/0/0
 description Link to L3-SW1 G1/1/1
 ip address 192.168.0.1 255.255.255.0
 no shutdown
 exit

!--- c. Interface addressing and description on S0/1/0.
interface serial 0/1/0
 description Link to ISP
 ip address 209.165.201.2 255.255.255.252
 no shutdown
 exit

! --------------------------------------------------------------
!--- Part 5: Configure Inter-VLAN Routing.
! --------------------------------------------------------------

!--- Step 2a/b. Enable the physical trunk interface toward Sw-C, with description.
interface gigabitethernet 0/0/1
 description Trunk to Sw-C G0/1
 no shutdown
 exit

!--- Step 2a/b. Subinterface for VLAN 40, with description.
interface gigabitethernet 0/0/1.40
 description Gateway for VLAN 40 (BDG4)
 encapsulation dot1q 40
 ip address 192.168.40.1 255.255.255.0
 exit

!--- Step 2a/b. Subinterface for VLAN 50, with description.
interface gigabitethernet 0/0/1.50
 description Gateway for VLAN 50 (BDG5)
 encapsulation dot1q 50
 ip address 192.168.50.1 255.255.255.0
 exit

!--- Step 2a/b. Subinterface for VLAN 60, with description.
interface gigabitethernet 0/0/1.60
 description Gateway for VLAN 60 (BDG6)
 encapsulation dot1q 60
 ip address 192.168.60.1 255.255.255.0
 exit

!--- Step 2a/b. Subinterface for VLAN 99 (native VLAN), with description.
interface gigabitethernet 0/0/1.99
 description Gateway for VLAN 99 (Management, native)
 encapsulation dot1q 99 native
 ip address 192.168.99.17 255.255.255.240
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief     -> G0/0/0, S0/1/0, G0/0/1 and the four subinterfaces up/up
!---   show ip route               -> connected routes for VLANs 40, 50, 60, 99; static routes to 192.168.10.0, .20.0, .30.0
! ==============================================================
MULTILAYER SWITCH L3-SW1
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 200
!--- ANSWER SCRIPT FOR MULTILAYER SWITCH L3-SW1
!--- Usage: copy this whole file and paste it into the L3-SW1 terminal (start at the Switch> or L3-SW1> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Device name from the Addressing Table. In some exam IDs this switch still has the default name (Switch); the command is harmless if it is already named.
hostname L3-SW1

!--- Step 1. Create and name VLANs 10, 20 and 30.
vlan 10
 name FL1
 exit
vlan 20
 name FL2
 exit
vlan 30
 name FL3
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 1. Channel group 1 (G1/0/1-2, to Sw-A) and channel group 2 (G1/0/3-4, to Sw-B) with LACP active.
interface range gigabitethernet 1/0/1 - 2
 channel-group 1 mode active
 exit
interface range gigabitethernet 1/0/3 - 4
 channel-group 2 mode active
 exit

!--- Step 2a. Port channels as static trunks with DTP disabled.
interface port-channel 1
 switchport mode trunk
 switchport nonegotiate
 exit
interface port-channel 2
 switchport mode trunk
 switchport nonegotiate
 exit

!--- Step 2b. Troubleshoot Po2: G1/0/4 is preconfigured without "switchport mode trunk". Remove G1/0/3-4 from the channel, give both ports the same trunk settings, add them back and restart them.
interface range gigabitethernet 1/0/3 - 4
 no channel-group 2
 switchport mode trunk
 switchport nonegotiate
 channel-group 2 mode active
 shutdown
 no shutdown
 exit


! --------------------------------------------------------------
!--- Part 5: Configure Inter-VLAN Routing.
! --------------------------------------------------------------

!--- Step 1a. Enable routing and configure the SVIs for VLANs 10, 20 and 30.
ip routing
interface vlan 10
 ip address 192.168.10.1 255.255.255.0
 no shutdown
 exit
interface vlan 20
 ip address 192.168.20.1 255.255.255.0
 no shutdown
 exit
interface vlan 30
 ip address 192.168.30.1 255.255.255.0
 no shutdown
 exit

!--- Step 1b. G1/1/1 (to Edge-Router) as a routed port with the address from the Addressing Table.
interface gigabitethernet 1/1/1
 no switchport
 ip address 192.168.0.2 255.255.255.0
 no shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show etherchannel summary   -> Po1(SU) and Po2(SU), LACP, member ports (P)
!---   show interfaces trunk       -> Po1 and Po2 trunking, mode on (DTP off)
!---   show ip route               -> C routes for VLANs 10, 20, 30 and the G1/1/1 network
!--- Note: If a Po2 member port still shows (s) or (I) after both switches are configured, enter "shutdown" and "no shutdown" again on G1/0/3-4 of L3-SW1 and G0/1-2 of Sw-B, then wait for the ports to turn green.
! ==============================================================
SWITCH Sw-A
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 200
!--- ANSWER SCRIPT FOR SWITCH Sw-A
!--- Usage: copy this whole file and paste it into the Sw-A terminal (start at the Sw-A> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Step 1. Create and name VLANs 10, 20 and 30.
vlan 10
 name FL1
 exit
vlan 20
 name FL2
 exit
vlan 30
 name FL3
 exit

!--- Step 2. Static access ports per the Port to VLAN Assignment Table.
interface range fastethernet 0/7 - 10
 switchport mode access
 switchport access vlan 10
 exit
interface range fastethernet 0/11 - 15
 switchport mode access
 switchport access vlan 20
 exit
interface range fastethernet 0/16 - 24
 switchport mode access
 switchport access vlan 30
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 1. Channel group 1 (G0/1-2, to L3-SW1) and channel group 3 (F0/5-6, to Sw-B) with LACP active.
interface range gigabitethernet 0/1 - 2
 channel-group 1 mode active
 exit
interface range fastethernet 0/5 - 6
 channel-group 3 mode active
 exit

!--- Step 2a. Port channels as static trunks with DTP disabled.
interface port-channel 1
 switchport mode trunk
 switchport nonegotiate
 exit
interface port-channel 3
 switchport mode trunk
 switchport nonegotiate
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show etherchannel summary   -> Po1(SU) and Po3(SU), LACP, member ports (P)
!---   show interfaces trunk       -> Po1 and Po3 trunking, mode on (DTP off)
!---   show vlan brief             -> F0/7-10 in VLAN 10, F0/11-15 in VLAN 20, F0/16-24 in VLAN 30
! ==============================================================
SWITCH Sw-B
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 200
!--- ANSWER SCRIPT FOR SWITCH Sw-B
!--- Usage: copy this whole file and paste it into the Sw-B terminal (start at the Sw-B> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Step 1. Create and name VLANs 10, 20 and 30.
vlan 10
 name FL1
 exit
vlan 20
 name FL2
 exit
vlan 30
 name FL3
 exit

!--- Step 2. Static access ports per the Port to VLAN Assignment Table.
interface range fastethernet 0/7 - 10
 switchport mode access
 switchport access vlan 10
 exit
interface range fastethernet 0/11 - 15
 switchport mode access
 switchport access vlan 20
 exit
interface range fastethernet 0/16 - 24
 switchport mode access
 switchport access vlan 30
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 1. Channel group 2 (G0/1-2, to L3-SW1) and channel group 3 (F0/5-6, to Sw-A) with LACP active.
interface range gigabitethernet 0/1 - 2
 channel-group 2 mode active
 exit
interface range fastethernet 0/5 - 6
 channel-group 3 mode active
 exit

!--- Step 2a. Port channels as static trunks with DTP disabled.
interface port-channel 2
 switchport mode trunk
 switchport nonegotiate
 exit
interface port-channel 3
 switchport mode trunk
 switchport nonegotiate
 exit

!--- Step 2b. Troubleshoot Po2: G0/2 is preconfigured without "switchport mode trunk" and with duplex half (the assessment checks the port mode of G0/2). Remove G0/1-2 from the channel, give both ports the same settings, add them back and restart them.
interface range gigabitethernet 0/1 - 2
 no channel-group 2
 switchport mode trunk
 switchport nonegotiate
 duplex auto
 channel-group 2 mode active
 shutdown
 no shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show etherchannel summary   -> Po2(SU) and Po3(SU), LACP, member ports (P)
!---   show interfaces trunk       -> Po2 and Po3 trunking, mode on (DTP off)
!---   show vlan brief             -> F0/7-10 in VLAN 10, F0/11-15 in VLAN 20, F0/16-24 in VLAN 30
!--- Note: If a Po2 member port still shows (s) or (I) after both switches are configured, enter "shutdown" and "no shutdown" again on G1/0/3-4 of L3-SW1 and G0/1-2 of Sw-B, then wait for the ports to turn green.
! ==============================================================
SWITCH Sw-C
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 200
!--- ANSWER SCRIPT FOR SWITCH Sw-C
!--- Usage: copy this whole file and paste it into the Sw-C terminal (start at the Sw-C> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2: Basic Switch Configuration.
! --------------------------------------------------------------

!--- Step 1a. SVI 99 with the address from the Addressing Table.
interface vlan 99
 ip address 192.168.99.18 255.255.255.240
 no shutdown
 exit

!--- Step 1b. Default gateway so the SVI is reachable from other networks.
ip default-gateway 192.168.99.17

!--- Step 2. IP domain name (required before the RSA keys can be generated).
ip domain-name acad.pt

!--- Enable secret password (checked by the assessment).
enable secret class

!--- Step 2. Username admin with an encrypted password.
username admin privilege 15 secret C1sco123!

!--- Step 2. RSA keys with a 1024-bit modulus.
crypto key generate rsa general-keys modulus 1024

!--- Optional: use SSH version 2.
ip ssh version 2

!--- Step 2. All VTY lines accept SSH only and use the local username and password.
line vty 0 15
 transport input ssh
 login local
 exit

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Step 1. Create and name VLANs 40, 50, 60 and 99.
vlan 40
 name BDG4
 exit
vlan 50
 name BDG5
 exit
vlan 60
 name BDG6
 exit
vlan 99
 name Management
 exit

!--- Step 2. Static access ports per the Port to VLAN Assignment Table.
interface range fastethernet 0/1 - 5
 switchport mode access
 switchport access vlan 40
 exit
interface range fastethernet 0/6 - 10
 switchport mode access
 switchport access vlan 50
 exit
interface range fastethernet 0/11 - 15
 switchport mode access
 switchport access vlan 60
 exit
interface fastethernet 0/24
 switchport mode access
 switchport access vlan 99
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 3. G0/1 (to Edge-Router G0/0/1): static trunk, native VLAN 99, DTP disabled.
interface gigabitethernet 0/1
 switchport mode trunk
 switchport trunk native vlan 99
 switchport nonegotiate
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief     -> Vlan99 192.168.99.18 up/up (mask 255.255.255.240 in show running-config)
!---   show interfaces trunk       -> Gig0/1 trunking, mode on, native VLAN 99
!---   ping 192.168.99.17             -> Edge-Router G0/0/1.99 replies
!---   From the management host: ssh -l admin 192.168.99.18 (password C1sco123!) -> login succeeds
! ==============================================================
PC WS-1.1
PC WS-1.2
PC WS-1.3
PC WS-1.4
PC WS-1.5
PC WS-1.6
PC WS-2.1
PC WS-2.2
PC WS-2.3
MANAGEMENT PC
CCNAv7 Switching, Routing, and Wireless Essentials v7.0 (SRWE) Answers
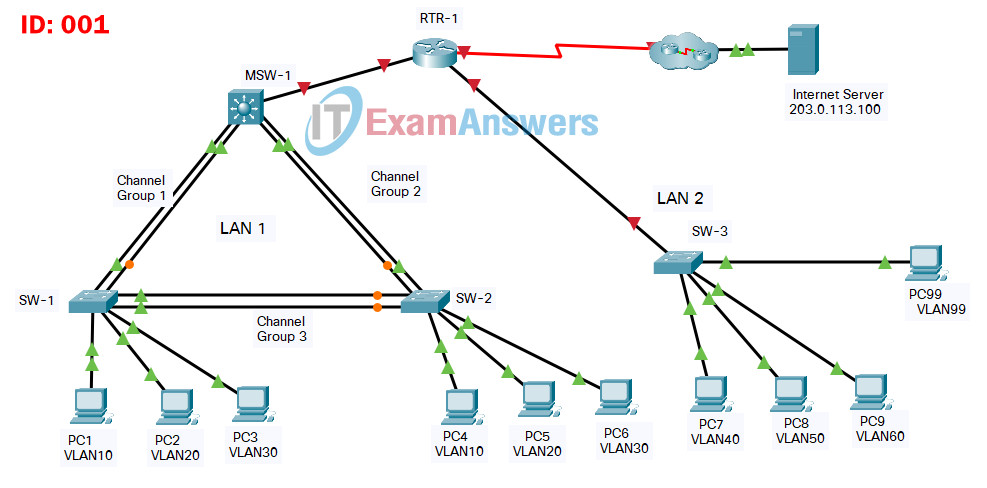
SRWE PT Practice Skills Assessment (PTSA) Part 1 ID 001
SRWE PT Practice Skills Assessment (PTSA) Part 1
A few things to keep in mind while completing this activity:
- Do not use the browser Back button or close or reload any exam windows during the exam.
- Do not close Packet Tracer when you are done. It will close automatically.
- Click the Submit Assessment button in the browser window to submit your work.
Introduction
In this assessment you are configuring a network that is using EtherChannel and routing between VLANs. For the sake of time, you will not be asked to perform all configurations on all network devices as you may be required to do in a real network or other assessment. Instead, you will use the skills and knowledge that you have learned in the labs in this course to configure the router and switches in the topology. In addition to EtherChannel and inter-VLAN routing, this task involves creating VLANs and trunks, and performing basic router and switch configuration.
You are required to configure host default gateways; however host addresses are preconfigured.
You will practice and be assessed on the following skills:
- Configuration of initial settings on a router.
- Configuration of initial settings on a switch, including SVI and SSH.
- Configuration of VLANs.
- Configuration of switchport VLAN membership.
- EtherChannel configuration.
- Troubleshooting VLANs.
- Configuration of static trunking and DTP.
- Configuration of routing between VLANs on a Layer 3 switch.
- Configuration of router-on-a-stick inter-VLAN routing on a router.
- Configure default gateways on hosts.
Addressing Table
| Device | Interface | IP Address | Subnet Mask |
|---|---|---|---|
| RTR-1 | G0/0/0 | 172.31.0.1 | 255.255.255.0 |
| G0/0/1.40 | 172.31.40.1 | 255.255.255.0 | |
| G0/0/1.50 | 172.31.50.1 | 255.255.255.0 | |
| G0/0/1.60 | 172.31.60.1 | 255.255.255.0 | |
| G0/0/1.99 | 172.31.99.17 | 255.255.255.240 | |
| S0/1/0 | 209.165.201.2 | 255.255.255.252 | |
| MSW-1 | G1/1/1 | 172.31.0.2 | 255.255.255.0 |
| VLAN10 | 172.31.10.1 | 255.255.255.0 | |
| VLAN20 | 172.31.20.1 | 255.255.255.0 | |
| VLAN30 | 172.31.30.1 | 255.255.255.0 | |
| SW-3 | VLAN99 | 172.31.99.18 | 255.255.255.240 |
| PC1 | NIC | 172.31.10.10 | 255.255.255.0 |
| PC2 | NIC | 172.31.20.20 | 255.255.255.0 |
| PC3 | NIC | 172.31.30.30 | 255.255.255.0 |
| PC4 | NIC | 172.31.10.11 | 255.255.255.0 |
| PC5 | NIC | 172.31.20.21 | 255.255.255.0 |
| PC6 | NIC | 172.31.30.31 | 255.255.255.0 |
| PC7 | NIC | 172.31.40.40 | 255.255.255.0 |
| PC8 | NIC | 172.31.50.50 | 255.255.255.0 |
| PC9 | NIC | 172.31.60.60 | 255.255.255.0 |
| PC99 | NIC | 172.31.99.19 | 255.255.255.240 |
| Internet Server | NIC | 203.0.113.100 | 255.255.255.0 |
Background / Scenario
A corporation is planning to implement EtherChannel and a new VLAN design in order to make the network more efficient. You have been asked to work on a design and prototype of the new network. You have created the logical topology and now need to configure the devices in order to evaluate the design. You will configure VLANs and access port VLAN membership on access layer switches. You will also configure EtherChannel and trunking. Finally, you will configure a router and a Layer 3 switch to route between VLANs. Some addressing had already been configured.
Instructions
Part 1: Basic Router Configuration
Step 1: Configure router RTR-1 with required settings.
a. Open a command window on router RTR-1 and move to privileged EXEC mode.
Router> enable
b. Copy and paste the following configuration into the RTR-1 router CLI.
ip route 172.31.10.0 255.255.255.0 GigabitEthernet0/0/0

ip route 172.31.20.0 255.255.255.0 GigabitEthernet0/0/0

ip route 172.31.30.0 255.255.255.0 GigabitEthernet0/0/0
Be sure to press the <Enter> key after the last line to return to privileged EXEC mode prompt.
c. Configure the following settings on the router:
- The enable secret password.
Router(config)# enable secret class
- A console password.
Router(config)# line console 0
Router(config-line)# password cisco
Router(config-line)# login
- Remote access to the VTY lines.
Router(config)# line vty 0 4
Router(config-line)# password cisco
Router(config-line)# login
- A banner MOTD message.
Router(config)# banner motd #Authorized Access Only!#
- The device hostname according to the value in the addressing table.
Router(config)# hostname RTR-1
- All clear text passwords should be encrypted.
RTR-1(config)# service password-encryption
- Interface addressing on G0/0/0 and S0/1/0.
RTR-1(config)# interface gigabitethernet 0/0/0
RTR-1(config-if)# ip address 172.31.0.1 255.255.255.0
RTR-1(config-if)# no shutdown
RTR-1(config-if)# interface serial 0/1/0
RTR-1(config-if)# ip address 209.165.201.2 255.255.255.252
RTR-1(config-if)# no shutdown
- Interface descriptions on G0/0/0 and S0/1/0.
RTR-1(config)# interface gigabitethernet 0/0/0
RTR-1(config-if)# description Link to MSW-1 G1/1/1
RTR-1(config-if)# interface serial 0/1/0
RTR-1(config-if)# description Link to ISP
Note: Be sure to make a record of the passwords that you create.
Part 2: Basic Switch Configuration
Step 1: Configure Remote Management Addressing
a. Configure SVI 99 on switch SW-3 with IP addressing according to the Addressing Table.
SW-3(config)# interface vlan 99
SW-3(config-if)# ip address 172.31.99.18 255.255.255.240
SW-3(config-if)# no shutdown
b. The SW-3 switch SVI should be reachable from other networks.
SW-3(config)# ip default-gateway 172.31.99.17
Step 2: Configure Secure Remote Access
On switch SW-3, configure SSH as follows:
- Username: admin encrypted password: C1sco123!
SW-3(config)# username admin privilege 15 secret C1sco123!
- Modulus bits 1024
SW-3(config)# ip domain-name acad.pt
SW-3(config)# crypto key generate rsa general-keys modulus 1024
- All VTY lines should accept SSH connections only.
SW-3(config)# line vty 0 15
SW-3(config-line)# transport input ssh
- Connections should require the previously configured username and password.
SW-3(config)# line vty 0 15
SW-3(config-line)# login local
- IP domain name: acad.pt
SW-3(config)# ip domain-name acad.pt
The assessment also checks the enable secret password on SW-3:
SW-3(config)# enable secret class
Part 3: VLAN Configuration
Step 1: Configure VLANs according to the VLAN table.
Use the VLAN Table to create and name the VLANs on the appropriate switches.
VLAN Table
| VLAN | Name | IP Network | Subnet Mask | Devices |
|---|---|---|---|---|
| 10 | FL1 | 172.31.10.0 | 255.255.255.0 | MSW-1, SW-1, |
| SW-2 | ||||
| 20 | FL2 | 172.31.20.0 | 255.255.255.0 | MSW-1, SW-1, |
| SW-2 | ||||
| 30 | FL3 | 172.31.30.0 | 255.255.255.0 | MSW-1, SW-1, |
| SW-2 | ||||
| 40 | BDG4 | 172.31.40.0 | 255.255.255.0 | SW-3 |
| 50 | BDG5 | 172.31.50.0 | 255.255.255.0 | SW-3 |
| 60 | BDG6 | 172.31.60.0 | 255.255.255.0 | SW-3 |
| 99 | Management | 172.31.99.16 | 255.255.255.240 | SW-3 |
Note: In some exam IDs, MSW-1 still has the default name (prompt Switch#). Set its hostname according to the Addressing Table first; the command is harmless if the switch is already named.
MSW-1:
Switch(config)# hostname MSW-1
MSW-1(config)# vlan 10
MSW-1(config-vlan)# name FL1
MSW-1(config-vlan)# vlan 20
MSW-1(config-vlan)# name FL2
MSW-1(config-vlan)# vlan 30
MSW-1(config-vlan)# name FL3
SW-1:
SW-1(config)# vlan 10
SW-1(config-vlan)# name FL1
SW-1(config-vlan)# vlan 20
SW-1(config-vlan)# name FL2
SW-1(config-vlan)# vlan 30
SW-1(config-vlan)# name FL3
SW-2:
SW-2(config)# vlan 10
SW-2(config-vlan)# name FL1
SW-2(config-vlan)# vlan 20
SW-2(config-vlan)# name FL2
SW-2(config-vlan)# vlan 30
SW-2(config-vlan)# name FL3
SW-3:
SW-3(config)# vlan 40
SW-3(config-vlan)# name BDG4
SW-3(config-vlan)# vlan 50
SW-3(config-vlan)# name BDG5
SW-3(config-vlan)# vlan 60
SW-3(config-vlan)# name BDG6
SW-3(config-vlan)# vlan 99
SW-3(config-vlan)# name Management
Step 2: Assign switch ports to VLANs.
Assign VLAN membership to static access switchports according to the Port to VLAN Assignment table.
Port to VLAN Assignment Table
| Device | VLAN | VLAN Name | Port Assignments |
|---|---|---|---|
| SW-1 | 10 | FL1 | F0/7-10 |
| 20 | FL2 | F0/11-15 | |
| 30 | FL3 | F0/16-24 | |
| SW-2 | 10 | FL1 | F0/7-10 |
| 20 | FL2 | F0/11-15 | |
| 30 | FL3 | F0/16-24 | |
| SW-3 | 40 | BDG4 | F0/1-5 |
| 50 | BDG5 | F0/6-10 | |
| 60 | BDG6 | F0/11-15 | |
| 99 | Management Native | F0/24 |
SW-1:
SW-1(config)# interface range fastethernet 0/7 - 10
SW-1(config-if-range)# switchport mode access
SW-1(config-if-range)# switchport access vlan 10
SW-1(config-if-range)# interface range fastethernet 0/11 - 15
SW-1(config-if-range)# switchport mode access
SW-1(config-if-range)# switchport access vlan 20
SW-1(config-if-range)# interface range fastethernet 0/16 - 24
SW-1(config-if-range)# switchport mode access
SW-1(config-if-range)# switchport access vlan 30
SW-2:
SW-2(config)# interface range fastethernet 0/7 - 10
SW-2(config-if-range)# switchport mode access
SW-2(config-if-range)# switchport access vlan 10
SW-2(config-if-range)# interface range fastethernet 0/11 - 15
SW-2(config-if-range)# switchport mode access
SW-2(config-if-range)# switchport access vlan 20
SW-2(config-if-range)# interface range fastethernet 0/16 - 24
SW-2(config-if-range)# switchport mode access
SW-2(config-if-range)# switchport access vlan 30
SW-3:
SW-3(config)# interface range fastethernet 0/1 - 5
SW-3(config-if-range)# switchport mode access
SW-3(config-if-range)# switchport access vlan 40
SW-3(config-if-range)# interface range fastethernet 0/6 - 10
SW-3(config-if-range)# switchport mode access
SW-3(config-if-range)# switchport access vlan 50
SW-3(config-if-range)# interface range fastethernet 0/11 - 15
SW-3(config-if-range)# switchport mode access
SW-3(config-if-range)# switchport access vlan 60
SW-3(config-if-range)# interface fastethernet 0/24
SW-3(config-if)# switchport mode access
SW-3(config-if)# switchport access vlan 99
Part 4: EtherChannel and Trunking Configuration
EtherChannel Port Assignments Table
| Channel Group | Devices in Groups | Ports in Group |
|---|---|---|
| 1 | MSW-1 | G1/0/1, G1/0/2 |
| SW-1 | G0/1, G0/2 | |
| 2 | MSW-1 | G1/0/3, G1/0/4 |
| SW-2 | G0/1, G0/2 | |
| 3 | SW-1 | F0/5, F0/6 |
| SW-2 | F0/5, F0/6 |
Step 1: Configure EtherChannels
Create EtherChannels according to the EtherChannel Port Assignments Table. Use the Cisco LACP protocol. Both sides of the channel should attempt to negotiate the link protocol.
MSW-1:
MSW-1(config)# interface range gigabitethernet 1/0/1 - 2
MSW-1(config-if-range)# channel-group 1 mode active
MSW-1(config-if-range)# interface range gigabitethernet 1/0/3 - 4
MSW-1(config-if-range)# channel-group 2 mode active
SW-1:
SW-1(config)# interface range gigabitethernet 0/1 - 2
SW-1(config-if-range)# channel-group 1 mode active
SW-1(config-if-range)# interface range fastethernet 0/5 - 6
SW-1(config-if-range)# channel-group 3 mode active
SW-2:
SW-2(config)# interface range gigabitethernet 0/1 - 2
SW-2(config-if-range)# channel-group 2 mode active
SW-2(config-if-range)# interface range fastethernet 0/5 - 6
SW-2(config-if-range)# channel-group 3 mode active
Step 2: Configure Trunking on the EtherChannels
a. Configure the port channel interfaces as static trunks. Disable DTP negotiation on all trunks.
MSW-1:
MSW-1(config)# interface port-channel 1
MSW-1(config-if)# switchport mode trunk
MSW-1(config-if)# switchport nonegotiate
MSW-1(config-if)# interface port-channel 2
MSW-1(config-if)# switchport mode trunk
MSW-1(config-if)# switchport nonegotiate
SW-1:
SW-1(config)# interface port-channel 1
SW-1(config-if)# switchport mode trunk
SW-1(config-if)# switchport nonegotiate
SW-1(config-if)# interface port-channel 3
SW-1(config-if)# switchport mode trunk
SW-1(config-if)# switchport nonegotiate
SW-2:
SW-2(config)# interface port-channel 2
SW-2(config-if)# switchport mode trunk
SW-2(config-if)# switchport nonegotiate
SW-2(config-if)# interface port-channel 3
SW-2(config-if)# switchport mode trunk
SW-2(config-if)# switchport nonegotiate
b. Troubleshoot any issues that prevent the formation of the EtherChannels.
The activity contains intentionally introduced errors on the member ports of channel group 2. This step is scored: the assessment checks the port mode of G0/2 on SW-2, so it must be fixed to reach 100%. Use show etherchannel summary to find the problem: Po2 is down (SD) and its member ports are suspended (s). Then compare the configuration of the member ports: on MSW-1, G1/0/4 is missing switchport mode trunk; on SW-2, G0/2 is missing switchport mode trunk and is set to duplex half. To fix it, remove both member ports from channel group 2, give them the same settings, add them back and restart them.
Before the fix, Po2 is down on both switches and its member ports are suspended:
MSW-1:
MSW-1# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

1      Po1(SU)           LACP   Gig1/0/1(P) Gig1/0/2(P)
2 Po2(SD) LACP Gig1/0/3(s) Gig1/0/4(s) MSW-1# show running-config | begin GigabitEthernet1/0/3
interface GigabitEthernet1/0/3
switchport mode trunk
switchport nonegotiate
channel-group 2 mode active
!
interface GigabitEthernet1/0/4
switchport nonegotiate
channel-group 2 mode active
!
<output omitted>SW-2:
SW-2# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

2      Po2(SD)           LACP   Gig0/1(s) Gig0/2(s)
3 Po3(SU) LACP Fa0/5(P) Fa0/6(P) SW-2# show running-config | begin GigabitEthernet0/1
interface GigabitEthernet0/1
switchport mode trunk
switchport nonegotiate
channel-group 2 mode active
!
interface GigabitEthernet0/2
switchport nonegotiate
duplex half
channel-group 2 mode active
!
<output omitted>Fix the member ports of channel group 2 on both switches:
MSW-1:
MSW-1(config)# interface range gigabitethernet 1/0/3 - 4
MSW-1(config-if-range)# no channel-group 2
MSW-1(config-if-range)# switchport mode trunk
MSW-1(config-if-range)# switchport nonegotiate
MSW-1(config-if-range)# channel-group 2 mode active
MSW-1(config-if-range)# shutdown
MSW-1(config-if-range)# no shutdown
SW-2:
SW-2(config)# interface range gigabitethernet 0/1 - 2
SW-2(config-if-range)# no channel-group 2
SW-2(config-if-range)# switchport mode trunk
SW-2(config-if-range)# switchport nonegotiate
SW-2(config-if-range)# duplex auto
SW-2(config-if-range)# channel-group 2 mode active
SW-2(config-if-range)# shutdown
SW-2(config-if-range)# no shutdown
If a member port of Po2 still shows (s) or (I) after both switches are fixed, restart the member ports on both switches once more, then wait for the ports to turn green (or click Fast Forward Time):
MSW-1:
MSW-1(config)# interface range gigabitethernet 1/0/3 - 4
MSW-1(config-if-range)# shutdown
MSW-1(config-if-range)# no shutdown
SW-2:
SW-2(config)# interface range gigabitethernet 0/1 - 2
SW-2(config-if-range)# shutdown
SW-2(config-if-range)# no shutdown
Verify that channel group 2 is now in use (SU) on both switches and that all member ports are bundled (P):
MSW-1:
MSW-1# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

1      Po1(SU)           LACP   Gig1/0/1(P) Gig1/0/2(P)
2      Po2(SU)           LACP   Gig1/0/3(P) Gig1/0/4(P)
SW-2:
SW-2# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

2      Po2(SU)           LACP   Gig0/1(P) Gig0/2(P)
3      Po3(SU)           LACP   Fa0/5(P) Fa0/6(P)
Note: Packet Tracer requires configuration of trunking and DTP mode on both portchannel interfaces and the component physical interfaces.
Step 3: Configure a static trunk uplink
a. On the SW-3 switch, configure the port that is connected to RTR-1 G0/0/1 as a static trunk.
SW-3(config)# interface gigabitethernet 0/1
SW-3(config-if)# switchport mode trunk
b. Configure the Management VLAN as the native VLAN.
SW-3(config-if)# switchport trunk native vlan 99
c. Disable DTP on the port.
SW-3(config-if)# switchport nonegotiate
Part 5: Configure Inter-VLAN Routing
Step 1: Configure inter-VLAN routing on the Layer 3 switch.
a. Configure Inter-VLAN routing on the MSW-1 Layer 3 switch for all VLANs in the VLAN Table that are configured on MSW-1.
MSW-1(config)# ip routing
MSW-1(config)# interface vlan 10
MSW-1(config-if)# ip address 172.31.10.1 255.255.255.0
MSW-1(config-if)# interface vlan 20
MSW-1(config-if)# ip address 172.31.20.1 255.255.255.0
MSW-1(config-if)# interface vlan 30
MSW-1(config-if)# ip address 172.31.30.1 255.255.255.0
b. Configure the switchport on MSW-1 that is connected to RTR-1 with an IP address as shown in the Addressing Table.
MSW-1(config)# interface gigabitethernet 1/1/1
MSW-1(config-if)# no switchport
MSW-1(config-if)# ip address 172.31.0.2 255.255.255.0
Step 2: Configure router-on-a-stick inter-VLAN routing on a router.
a. Configure inter-VLAN routing on RTR-1 for all the VLANs that are configured on the SW-3 switch. Use the information in the Addressing Table.
RTR-1(config)# interface gigabitethernet 0/0/1
RTR-1(config-if)# no shutdown
RTR-1(config-if)# interface gigabitethernet 0/0/1.40
RTR-1(config-subif)# encapsulation dot1q 40
RTR-1(config-subif)# ip address 172.31.40.1 255.255.255.0
RTR-1(config-subif)# interface gigabitethernet 0/0/1.50
RTR-1(config-subif)# encapsulation dot1q 50
RTR-1(config-subif)# ip address 172.31.50.1 255.255.255.0
RTR-1(config-subif)# interface gigabitethernet 0/0/1.60
RTR-1(config-subif)# encapsulation dot1q 60
RTR-1(config-subif)# ip address 172.31.60.1 255.255.255.0
RTR-1(config-subif)# interface gigabitethernet 0/0/1.99
RTR-1(config-subif)# encapsulation dot1q 99 native
RTR-1(config-subif)# ip address 172.31.99.17 255.255.255.240
b. Be sure to configure descriptions of all interfaces.
RTR-1(config)# interface gigabitethernet 0/0/1
RTR-1(config-if)# description Trunk to SW-3 G0/1
RTR-1(config-if)# interface gigabitethernet 0/0/1.40
RTR-1(config-subif)# description Gateway for VLAN 40 (BDG4)
RTR-1(config-subif)# interface gigabitethernet 0/0/1.50
RTR-1(config-subif)# description Gateway for VLAN 50 (BDG5)
RTR-1(config-subif)# interface gigabitethernet 0/0/1.60
RTR-1(config-subif)# description Gateway for VLAN 60 (BDG6)
RTR-1(config-subif)# interface gigabitethernet 0/0/1.99
RTR-1(config-subif)# description Gateway for VLAN 99 (Management, native)
Step 3: Configure default gateways on hosts.
a. Configure default gateway addresses on all hosts on the LANs.
| Host | IP Address | Subnet Mask | Default Gateway |
|---|---|---|---|
| PC1 | 172.31.10.10 | 255.255.255.0 | 172.31.10.1 |
| PC2 | 172.31.20.20 | 255.255.255.0 | 172.31.20.1 |
| PC3 | 172.31.30.30 | 255.255.255.0 | 172.31.30.1 |
| PC4 | 172.31.10.11 | 255.255.255.0 | 172.31.10.1 |
| PC5 | 172.31.20.21 | 255.255.255.0 | 172.31.20.1 |
| PC6 | 172.31.30.31 | 255.255.255.0 | 172.31.30.1 |
| PC7 | 172.31.40.40 | 255.255.255.0 | 172.31.40.1 |
| PC8 | 172.31.50.50 | 255.255.255.0 | 172.31.50.1 |
| PC9 | 172.31.60.60 | 255.255.255.0 | 172.31.60.1 |
| PC99 | 172.31.99.19 | 255.255.255.240 | 172.31.99.17 |
b. Verify connectivity between all hosts on both LANs with each other and the Internet Server.
c. Verify that a host can connect to the SVI of switch SW-3 over SSH.
C:\> ssh -l admin 172.31.99.18
Password:
Last Updated: January 2021
ID 001
Device Configs - Final
ROUTER RTR-1
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 001
!--- ANSWER SCRIPT FOR ROUTER RTR-1
!--- Usage: copy this whole file and paste it into the RTR-1 terminal (start at the Router> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1: Basic Router Configuration.
! --------------------------------------------------------------

!--- b. Static routes provided by the exam (paste as given).
ip route 172.31.10.0 255.255.255.0 GigabitEthernet0/0/0
ip route 172.31.20.0 255.255.255.0 GigabitEthernet0/0/0
ip route 172.31.30.0 255.255.255.0 GigabitEthernet0/0/0

!--- Optional: stop the router from treating mistyped commands as host names.
no ip domain lookup

!--- c. The enable secret password.
enable secret class

!--- c. A console password.
line console 0
 password cisco
 login
 exit

!--- c. Remote access to the VTY lines.
line vty 0 4
 password cisco
 login
 exit

!--- c. A banner MOTD message.
banner motd #Authorized Access Only!#

!--- c. The device hostname according to the value in the addressing table.
hostname RTR-1

!--- c. All clear text passwords should be encrypted.
service password-encryption

!--- c. Interface addressing and description on G0/0/0.
interface gigabitethernet 0/0/0
 description Link to MSW-1 G1/1/1
 ip address 172.31.0.1 255.255.255.0
 no shutdown
 exit

!--- c. Interface addressing and description on S0/1/0.
interface serial 0/1/0
 description Link to ISP
 ip address 209.165.201.2 255.255.255.252
 no shutdown
 exit

! --------------------------------------------------------------
!--- Part 5: Configure Inter-VLAN Routing.
! --------------------------------------------------------------

!--- Step 2a/b. Enable the physical trunk interface toward SW-3, with description.
interface gigabitethernet 0/0/1
 description Trunk to SW-3 G0/1
 no shutdown
 exit

!--- Step 2a/b. Subinterface for VLAN 40, with description.
interface gigabitethernet 0/0/1.40
 description Gateway for VLAN 40 (BDG4)
 encapsulation dot1q 40
 ip address 172.31.40.1 255.255.255.0
 exit

!--- Step 2a/b. Subinterface for VLAN 50, with description.
interface gigabitethernet 0/0/1.50
 description Gateway for VLAN 50 (BDG5)
 encapsulation dot1q 50
 ip address 172.31.50.1 255.255.255.0
 exit

!--- Step 2a/b. Subinterface for VLAN 60, with description.
interface gigabitethernet 0/0/1.60
 description Gateway for VLAN 60 (BDG6)
 encapsulation dot1q 60
 ip address 172.31.60.1 255.255.255.0
 exit

!--- Step 2a/b. Subinterface for VLAN 99 (native VLAN), with description.
interface gigabitethernet 0/0/1.99
 description Gateway for VLAN 99 (Management, native)
 encapsulation dot1q 99 native
 ip address 172.31.99.17 255.255.255.240
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief     -> G0/0/0, S0/1/0, G0/0/1 and the four subinterfaces up/up
!---   show ip route               -> connected routes for VLANs 40, 50, 60, 99; static routes to 172.31.10.0, .20.0, .30.0
! ==============================================================
MULTILAYER SWITCH MSW-1
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 001
!--- ANSWER SCRIPT FOR MULTILAYER SWITCH MSW-1
!--- Usage: copy this whole file and paste it into the MSW-1 terminal (start at the Switch> or MSW-1> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Device name from the Addressing Table. In some exam IDs this switch still has the default name (Switch); the command is harmless if it is already named.
hostname MSW-1

!--- Step 1. Create and name VLANs 10, 20 and 30.
vlan 10
 name FL1
 exit
vlan 20
 name FL2
 exit
vlan 30
 name FL3
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 1. Channel group 1 (G1/0/1-2, to SW-1) and channel group 2 (G1/0/3-4, to SW-2) with LACP active.
interface range gigabitethernet 1/0/1 - 2
 channel-group 1 mode active
 exit
interface range gigabitethernet 1/0/3 - 4
 channel-group 2 mode active
 exit

!--- Step 2a. Port channels as static trunks with DTP disabled.
interface port-channel 1
 switchport mode trunk
 switchport nonegotiate
 exit
interface port-channel 2
 switchport mode trunk
 switchport nonegotiate
 exit

!--- Step 2b. Troubleshoot Po2: G1/0/4 is preconfigured without "switchport mode trunk". Remove G1/0/3-4 from the channel, give both ports the same trunk settings, add them back and restart them.
interface range gigabitethernet 1/0/3 - 4
 no channel-group 2
 switchport mode trunk
 switchport nonegotiate
 channel-group 2 mode active
 shutdown
 no shutdown
 exit


! --------------------------------------------------------------
!--- Part 5: Configure Inter-VLAN Routing.
! --------------------------------------------------------------

!--- Step 1a. Enable routing and configure the SVIs for VLANs 10, 20 and 30.
ip routing
interface vlan 10
 ip address 172.31.10.1 255.255.255.0
 no shutdown
 exit
interface vlan 20
 ip address 172.31.20.1 255.255.255.0
 no shutdown
 exit
interface vlan 30
 ip address 172.31.30.1 255.255.255.0
 no shutdown
 exit

!--- Step 1b. G1/1/1 (to RTR-1) as a routed port with the address from the Addressing Table.
interface gigabitethernet 1/1/1
 no switchport
 ip address 172.31.0.2 255.255.255.0
 no shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show etherchannel summary   -> Po1(SU) and Po2(SU), LACP, member ports (P)
!---   show interfaces trunk       -> Po1 and Po2 trunking, mode on (DTP off)
!---   show ip route               -> C routes for VLANs 10, 20, 30 and the G1/1/1 network
!--- Note: If a Po2 member port still shows (s) or (I) after both switches are configured, enter "shutdown" and "no shutdown" again on G1/0/3-4 of MSW-1 and G0/1-2 of SW-2, then wait for the ports to turn green.
! ==============================================================
SWITCH SW-1
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 001
!--- ANSWER SCRIPT FOR SWITCH SW-1
!--- Usage: copy this whole file and paste it into the SW-1 terminal (start at the SW-1> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Step 1. Create and name VLANs 10, 20 and 30.
vlan 10
 name FL1
 exit
vlan 20
 name FL2
 exit
vlan 30
 name FL3
 exit

!--- Step 2. Static access ports per the Port to VLAN Assignment Table.
interface range fastethernet 0/7 - 10
 switchport mode access
 switchport access vlan 10
 exit
interface range fastethernet 0/11 - 15
 switchport mode access
 switchport access vlan 20
 exit
interface range fastethernet 0/16 - 24
 switchport mode access
 switchport access vlan 30
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 1. Channel group 1 (G0/1-2, to MSW-1) and channel group 3 (F0/5-6, to SW-2) with LACP active.
interface range gigabitethernet 0/1 - 2
 channel-group 1 mode active
 exit
interface range fastethernet 0/5 - 6
 channel-group 3 mode active
 exit

!--- Step 2a. Port channels as static trunks with DTP disabled.
interface port-channel 1
 switchport mode trunk
 switchport nonegotiate
 exit
interface port-channel 3
 switchport mode trunk
 switchport nonegotiate
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show etherchannel summary   -> Po1(SU) and Po3(SU), LACP, member ports (P)
!---   show interfaces trunk       -> Po1 and Po3 trunking, mode on (DTP off)
!---   show vlan brief             -> F0/7-10 in VLAN 10, F0/11-15 in VLAN 20, F0/16-24 in VLAN 30
! ==============================================================
SWITCH SW-2
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 001
!--- ANSWER SCRIPT FOR SWITCH SW-2
!--- Usage: copy this whole file and paste it into the SW-2 terminal (start at the SW-2> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Step 1. Create and name VLANs 10, 20 and 30.
vlan 10
 name FL1
 exit
vlan 20
 name FL2
 exit
vlan 30
 name FL3
 exit

!--- Step 2. Static access ports per the Port to VLAN Assignment Table.
interface range fastethernet 0/7 - 10
 switchport mode access
 switchport access vlan 10
 exit
interface range fastethernet 0/11 - 15
 switchport mode access
 switchport access vlan 20
 exit
interface range fastethernet 0/16 - 24
 switchport mode access
 switchport access vlan 30
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 1. Channel group 2 (G0/1-2, to MSW-1) and channel group 3 (F0/5-6, to SW-1) with LACP active.
interface range gigabitethernet 0/1 - 2
 channel-group 2 mode active
 exit
interface range fastethernet 0/5 - 6
 channel-group 3 mode active
 exit

!--- Step 2a. Port channels as static trunks with DTP disabled.
interface port-channel 2
 switchport mode trunk
 switchport nonegotiate
 exit
interface port-channel 3
 switchport mode trunk
 switchport nonegotiate
 exit

!--- Step 2b. Troubleshoot Po2: G0/2 is preconfigured without "switchport mode trunk" and with duplex half (the assessment checks the port mode of G0/2). Remove G0/1-2 from the channel, give both ports the same settings, add them back and restart them.
interface range gigabitethernet 0/1 - 2
 no channel-group 2
 switchport mode trunk
 switchport nonegotiate
 duplex auto
 channel-group 2 mode active
 shutdown
 no shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show etherchannel summary   -> Po2(SU) and Po3(SU), LACP, member ports (P)
!---   show interfaces trunk       -> Po2 and Po3 trunking, mode on (DTP off)
!---   show vlan brief             -> F0/7-10 in VLAN 10, F0/11-15 in VLAN 20, F0/16-24 in VLAN 30
!--- Note: If a Po2 member port still shows (s) or (I) after both switches are configured, enter "shutdown" and "no shutdown" again on G1/0/3-4 of MSW-1 and G0/1-2 of SW-2, then wait for the ports to turn green.
! ==============================================================
SWITCH SW-3
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 001
!--- ANSWER SCRIPT FOR SWITCH SW-3
!--- Usage: copy this whole file and paste it into the SW-3 terminal (start at the SW-3> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2: Basic Switch Configuration.
! --------------------------------------------------------------

!--- Step 1a. SVI 99 with the address from the Addressing Table.
interface vlan 99
 ip address 172.31.99.18 255.255.255.240
 no shutdown
 exit

!--- Step 1b. Default gateway so the SVI is reachable from other networks.
ip default-gateway 172.31.99.17

!--- Step 2. IP domain name (required before the RSA keys can be generated).
ip domain-name acad.pt

!--- Enable secret password (checked by the assessment).
enable secret class

!--- Step 2. Username admin with an encrypted password.
username admin privilege 15 secret C1sco123!

!--- Step 2. RSA keys with a 1024-bit modulus.
crypto key generate rsa general-keys modulus 1024

!--- Optional: use SSH version 2.
ip ssh version 2

!--- Step 2. All VTY lines accept SSH only and use the local username and password.
line vty 0 15
 transport input ssh
 login local
 exit

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Step 1. Create and name VLANs 40, 50, 60 and 99.
vlan 40
 name BDG4
 exit
vlan 50
 name BDG5
 exit
vlan 60
 name BDG6
 exit
vlan 99
 name Management
 exit

!--- Step 2. Static access ports per the Port to VLAN Assignment Table.
interface range fastethernet 0/1 - 5
 switchport mode access
 switchport access vlan 40
 exit
interface range fastethernet 0/6 - 10
 switchport mode access
 switchport access vlan 50
 exit
interface range fastethernet 0/11 - 15
 switchport mode access
 switchport access vlan 60
 exit
interface fastethernet 0/24
 switchport mode access
 switchport access vlan 99
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 3. G0/1 (to RTR-1 G0/0/1): static trunk, native VLAN 99, DTP disabled.
interface gigabitethernet 0/1
 switchport mode trunk
 switchport trunk native vlan 99
 switchport nonegotiate
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief     -> Vlan99 172.31.99.18 up/up (mask 255.255.255.240 in show running-config)
!---   show interfaces trunk       -> Gig0/1 trunking, mode on, native VLAN 99
!---   ping 172.31.99.17             -> RTR-1 G0/0/1.99 replies
!---   From the management host: ssh -l admin 172.31.99.18 (password C1sco123!) -> login succeeds
! ==============================================================
PC1
PC2
PC3
PC4
PC5
PC6
PC7
PC8
PC9
PC99
CCNAv7 Switching, Routing, and Wireless Essentials v7.0 (SRWE) Answers
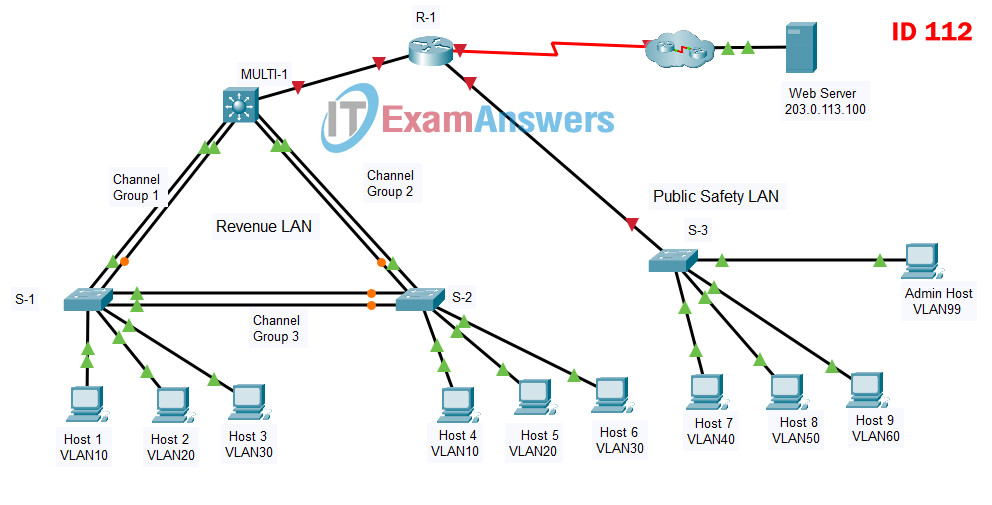
SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 112
SRWE PT Practice Skills Assessment (PTSA) Part 1
A few things to keep in mind while completing this activity:
- Do not use the browser Back button or close or reload any exam windows during the exam.
- Do not close Packet Tracer when you are done. It will close automatically.
- Click the Submit Assessment button in the browser window to submit your work.
Introduction
In this assessment you are configuring a network that is using EtherChannel and routing between VLANs. For the sake of time, you will not be asked to perform all configurations on all network devices as you may be required to do in a real network or other assessment. Instead, you will use the skills and knowledge that you have learned in the labs in this course to configure the router and switches in the topology. In addition to EtherChannel and inter-VLAN routing, this task involves creating VLANs and trunks, and performing basic router and switch configuration.
You are required to configure host default gateways; however host addresses are preconfigured.
You will practice and be assessed on the following skills:
- Configuration of initial settings on a router.
- Configuration of initial settings on a switch, including SVI and SSH.
- Configuration of VLANs.
- Configuration of switchport VLAN membership.
- EtherChannel configuration.
- Troubleshooting VLANs.
- Configuration of static trunking and DTP.
- Configuration of routing between VLANs on a Layer 3 switch.
- Configuration of router-on-a-stick inter-VLAN routing on a router.
- Configure default gateways on hosts.
Addressing Table
| Device | Interface | IP Address | Subnet Mask |
|---|---|---|---|
| R-1 | G0/0/0 | 10.0.0.1 | 255.255.255.0 |
| G0/0/1.40 | 10.0.40.1 | 255.255.255.0 | |
| G0/0/1.50 | 10.0.50.1 | 255.255.255.0 | |
| G0/0/1.60 | 10.0.60.1 | 255.255.255.0 | |
| G0/0/1.99 | 10.0.99.17 | 255.255.255.240 | |
| S0/1/0 | 209.165.201.2 | 255.255.255.252 | |
| MULTI-1 | G1/1/1 | 10.0.0.2 | 255.255.255.0 |
| VLAN10 | 10.0.10.1 | 255.255.255.0 | |
| VLAN20 | 10.0.20.1 | 255.255.255.0 | |
| VLAN30 | 10.0.30.1 | 255.255.255.0 | |
| S-3 | VLAN99 | 10.0.99.18 | 255.255.255.240 |
| Host 1 | NIC | 10.0.10.10 | 255.255.255.0 |
| Host 2 | NIC | 10.0.20.20 | 255.255.255.0 |
| Host 3 | NIC | 10.0.30.30 | 255.255.255.0 |
| Host 4 | NIC | 10.0.10.11 | 255.255.255.0 |
| Host 5 | NIC | 10.0.20.21 | 255.255.255.0 |
| Host 6 | NIC | 10.0.30.31 | 255.255.255.0 |
| Host 7 | NIC | 10.0.40.41 | 255.255.255.0 |
| Host 8 | NIC | 10.0.50.51 | 255.255.255.0 |
| Host 9 | NIC | 10.0.60.61 | 255.255.255.0 |
| Admin Host | NIC | 10.0.99.19 | 255.255.255.240 |
| Web Server | NIC | 203.0.113.100 | 255.255.255.0 |
Background / Scenario
A corporation is planning to implement EtherChannel and a new VLAN design in order to make the network more efficient. You have been asked to work on a design and prototype of the new network. You have created the logical topology and now need to configure the devices in order to evaluate the design. You will configure VLANs and access port VLAN membership on access layer switches. You will also configure EtherChannel and trunking. Finally, you will configure a router and a Layer 3 switch to route between VLANs. Some addressing had already been configured.
Instructions
Part 1: Basic Router Configuration
Step 1: Configure router R-1 with required settings.
a. Open a command window on router R-1 and move to privileged EXEC mode.
Router> enable
b. Copy and paste the following configuration into the R-1 router CLI.
ip route 10.0.10.0 255.255.255.0 GigabitEthernet0/0/0

ip route 10.0.20.0 255.255.255.0 GigabitEthernet0/0/0

ip route 10.0.30.0 255.255.255.0 GigabitEthernet0/0/0
Be sure to press the <Enter> key after the last line to return to privileged EXEC mode prompt.
c. Configure the following settings on the router:
- The enable secret password.
Router(config)# enable secret class
- A console password.
Router(config)# line console 0
Router(config-line)# password cisco
Router(config-line)# login
- Remote access to the VTY lines.
Router(config)# line vty 0 4
Router(config-line)# password cisco
Router(config-line)# login
- A banner MOTD message.
Router(config)# banner motd #Authorized Access Only!#
- The device hostname according to the value in the addressing table.
Router(config)# hostname R-1
- All clear text passwords should be encrypted.
R-1(config)# service password-encryption
- Interface addressing on G0/0/0 and S0/1/0.
R-1(config)# interface gigabitethernet 0/0/0
R-1(config-if)# ip address 10.0.0.1 255.255.255.0
R-1(config-if)# no shutdown
R-1(config-if)# interface serial 0/1/0
R-1(config-if)# ip address 209.165.201.2 255.255.255.252
R-1(config-if)# no shutdown
- Interface descriptions on G0/0/0 and S0/1/0.
R-1(config)# interface gigabitethernet 0/0/0
R-1(config-if)# description Link to MULTI-1 G1/1/1
R-1(config-if)# interface serial 0/1/0
R-1(config-if)# description Link to ISP
Note: Be sure to make a record of the passwords that you create.
Part 2: Basic Switch Configuration
Step 1: Configure Remote Management Addressing
a. Configure SVI 99 on switch S-3 with IP addressing according to the Addressing Table.
S-3(config)# interface vlan 99
S-3(config-if)# ip address 10.0.99.18 255.255.255.240
S-3(config-if)# no shutdown
b. The S-3 switch SVI should be reachable from other networks.
S-3(config)# ip default-gateway 10.0.99.17
Step 2: Configure Secure Remote Access
On switch S-3, configure SSH as follows:
- Username: admin encrypted password: C1sco123!
S-3(config)# username admin privilege 15 secret C1sco123!
- Modulus bits 1024
S-3(config)# ip domain-name acad.pt
S-3(config)# crypto key generate rsa general-keys modulus 1024
- All VTY lines should accept SSH connections only.
S-3(config)# line vty 0 15
S-3(config-line)# transport input ssh
- Connections should require the previously configured username and password.
S-3(config)# line vty 0 15
S-3(config-line)# login local
- IP domain name: acad.pt
S-3(config)# ip domain-name acad.pt
The assessment also checks the enable secret password on S-3:
S-3(config)# enable secret class
Part 3: VLAN Configuration
Step 1: Configure VLANs according to the VLAN table.
Use the VLAN Table to create and name the VLANs on the appropriate switches.
VLAN Table
| VLAN | Name | IP Network | Subnet Mask | Devices |
|---|---|---|---|---|
| 10 | SALES | 10.0.10.0 | 255.255.255.0 | MULTI-1, S-1, |
| S-2 | ||||
| 20 | ACCT | 10.0.20.0 | 255.255.255.0 | MULTI-1, S-1, |
| S-2 | ||||
| 30 | EXEC | 10.0.30.0 | 255.255.255.0 | MULTI-1, S-1, |
| S-2 | ||||
| 40 | FAC | 10.0.40.0 | 255.255.255.0 | S-3 |
| 50 | FAB1 | 10.0.50.0 | 255.255.255.0 | S-3 |
| 60 | FAB2 | 10.0.60.0 | 255.255.255.0 | S-3 |
| 99 | ADMIN | 10.0.99.16 | 255.255.255.240 | S-3 |
Note: In some exam IDs, MULTI-1 still has the default name (prompt Switch#). Set its hostname according to the Addressing Table first; the command is harmless if the switch is already named.
MULTI-1:
Switch(config)# hostname MULTI-1
MULTI-1(config)# vlan 10
MULTI-1(config-vlan)# name SALES
MULTI-1(config-vlan)# vlan 20
MULTI-1(config-vlan)# name ACCT
MULTI-1(config-vlan)# vlan 30
MULTI-1(config-vlan)# name EXEC
S-1:
S-1(config)# vlan 10
S-1(config-vlan)# name SALES
S-1(config-vlan)# vlan 20
S-1(config-vlan)# name ACCT
S-1(config-vlan)# vlan 30
S-1(config-vlan)# name EXEC
S-2:
S-2(config)# vlan 10
S-2(config-vlan)# name SALES
S-2(config-vlan)# vlan 20
S-2(config-vlan)# name ACCT
S-2(config-vlan)# vlan 30
S-2(config-vlan)# name EXEC
S-3:
S-3(config)# vlan 40
S-3(config-vlan)# name FAC
S-3(config-vlan)# vlan 50
S-3(config-vlan)# name FAB1
S-3(config-vlan)# vlan 60
S-3(config-vlan)# name FAB2
S-3(config-vlan)# vlan 99
S-3(config-vlan)# name ADMIN
Step 2: Assign switch ports to VLANs.
Assign VLAN membership to static access switchports according to the Port to VLAN Assignment table.
Port to VLAN Assignment Table
| Device | VLAN | VLAN Name | Port Assignments |
|---|---|---|---|
| S-1 | 10 | SALES | F0/7-10 |
| 20 | ACCT | F0/11-15 | |
| 30 | EXEC | F0/16-24 | |
| S-2 | 10 | SALES | F0/7-10 |
| 20 | ACCT | F0/11-15 | |
| 30 | EXEC | F0/16-24 | |
| S-3 | 40 | FAC | F0/1-5 |
| 50 | FAB1 | F0/6-10 | |
| 60 | FAB2 | F0/11-15 | |
| 99 | ADMIN Native | F0/24 |
S-1:
S-1(config)# interface range fastethernet 0/7 - 10
S-1(config-if-range)# switchport mode access
S-1(config-if-range)# switchport access vlan 10
S-1(config-if-range)# interface range fastethernet 0/11 - 15
S-1(config-if-range)# switchport mode access
S-1(config-if-range)# switchport access vlan 20
S-1(config-if-range)# interface range fastethernet 0/16 - 24
S-1(config-if-range)# switchport mode access
S-1(config-if-range)# switchport access vlan 30
S-2:
S-2(config)# interface range fastethernet 0/7 - 10
S-2(config-if-range)# switchport mode access
S-2(config-if-range)# switchport access vlan 10
S-2(config-if-range)# interface range fastethernet 0/11 - 15
S-2(config-if-range)# switchport mode access
S-2(config-if-range)# switchport access vlan 20
S-2(config-if-range)# interface range fastethernet 0/16 - 24
S-2(config-if-range)# switchport mode access
S-2(config-if-range)# switchport access vlan 30
S-3:
S-3(config)# interface range fastethernet 0/1 - 5
S-3(config-if-range)# switchport mode access
S-3(config-if-range)# switchport access vlan 40
S-3(config-if-range)# interface range fastethernet 0/6 - 10
S-3(config-if-range)# switchport mode access
S-3(config-if-range)# switchport access vlan 50
S-3(config-if-range)# interface range fastethernet 0/11 - 15
S-3(config-if-range)# switchport mode access
S-3(config-if-range)# switchport access vlan 60
S-3(config-if-range)# interface fastethernet 0/24
S-3(config-if)# switchport mode access
S-3(config-if)# switchport access vlan 99
Part 4: EtherChannel and Trunking Configuration
EtherChannel Port Assignments Table
| Channel Group | Devices in Groups | Ports in Group |
|---|---|---|
| 1 | MULTI-1 | G1/0/1, G1/0/2 |
| S-1 | G0/1, G0/2 | |
| 2 | MULTI-1 | G1/0/3, G1/0/4 |
| S-2 | G0/1, G0/2 | |
| 3 | S-1 | F0/5, F0/6 |
| S-2 | F0/5, F0/6 |
Step 1: Configure EtherChannels
Create EtherChannels according to the EtherChannel Port Assignments Table. Use the Cisco LACP protocol. Both sides of the channel should attempt to negotiate the link protocol.
MULTI-1:
MULTI-1(config)# interface range gigabitethernet 1/0/1 - 2
MULTI-1(config-if-range)# channel-group 1 mode active
MULTI-1(config-if-range)# interface range gigabitethernet 1/0/3 - 4
MULTI-1(config-if-range)# channel-group 2 mode active
S-1:
S-1(config)# interface range gigabitethernet 0/1 - 2
S-1(config-if-range)# channel-group 1 mode active
S-1(config-if-range)# interface range fastethernet 0/5 - 6
S-1(config-if-range)# channel-group 3 mode active
S-2:
S-2(config)# interface range gigabitethernet 0/1 - 2
S-2(config-if-range)# channel-group 2 mode active
S-2(config-if-range)# interface range fastethernet 0/5 - 6
S-2(config-if-range)# channel-group 3 mode active
Step 2: Configure Trunking on the EtherChannels
a. Configure the port channel interfaces as static trunks. Disable DTP negotiation on all trunks.
MULTI-1:
MULTI-1(config)# interface port-channel 1
MULTI-1(config-if)# switchport mode trunk
MULTI-1(config-if)# switchport nonegotiate
MULTI-1(config-if)# interface port-channel 2
MULTI-1(config-if)# switchport mode trunk
MULTI-1(config-if)# switchport nonegotiate
S-1:
S-1(config)# interface port-channel 1
S-1(config-if)# switchport mode trunk
S-1(config-if)# switchport nonegotiate
S-1(config-if)# interface port-channel 3
S-1(config-if)# switchport mode trunk
S-1(config-if)# switchport nonegotiate
S-2:
S-2(config)# interface port-channel 2
S-2(config-if)# switchport mode trunk
S-2(config-if)# switchport nonegotiate
S-2(config-if)# interface port-channel 3
S-2(config-if)# switchport mode trunk
S-2(config-if)# switchport nonegotiate
b. Troubleshoot any issues that prevent the formation of the EtherChannels.
The activity contains intentionally introduced errors on the member ports of channel group 2. This step is scored: the assessment checks the port mode of G0/2 on S-2, so it must be fixed to reach 100%. Use show etherchannel summary to find the problem: Po2 is down (SD) and its member ports are suspended (s). Then compare the configuration of the member ports: on MULTI-1, G1/0/4 is missing switchport mode trunk; on S-2, G0/2 is missing switchport mode trunk and is set to duplex half. To fix it, remove both member ports from channel group 2, give them the same settings, add them back and restart them.
Before the fix, Po2 is down on both switches and its member ports are suspended:
MULTI-1:
MULTI-1# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

1      Po1(SU)           LACP   Gig1/0/1(P) Gig1/0/2(P)
2 Po2(SD) LACP Gig1/0/3(s) Gig1/0/4(s) MULTI-1# show running-config | begin GigabitEthernet1/0/3
interface GigabitEthernet1/0/3
switchport mode trunk
switchport nonegotiate
channel-group 2 mode active
!
interface GigabitEthernet1/0/4
switchport nonegotiate
channel-group 2 mode active
!
<output omitted>S-2:
S-2# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

2      Po2(SD)           LACP   Gig0/1(s) Gig0/2(s)
3 Po3(SU) LACP Fa0/5(P) Fa0/6(P) S-2# show running-config | begin GigabitEthernet0/1
interface GigabitEthernet0/1
switchport mode trunk
switchport nonegotiate
channel-group 2 mode active
!
interface GigabitEthernet0/2
switchport nonegotiate
duplex half
channel-group 2 mode active
!
<output omitted>Fix the member ports of channel group 2 on both switches:
MULTI-1:
MULTI-1(config)# interface range gigabitethernet 1/0/3 - 4
MULTI-1(config-if-range)# no channel-group 2
MULTI-1(config-if-range)# switchport mode trunk
MULTI-1(config-if-range)# switchport nonegotiate
MULTI-1(config-if-range)# channel-group 2 mode active
MULTI-1(config-if-range)# shutdown
MULTI-1(config-if-range)# no shutdown
S-2:
S-2(config)# interface range gigabitethernet 0/1 - 2
S-2(config-if-range)# no channel-group 2
S-2(config-if-range)# switchport mode trunk
S-2(config-if-range)# switchport nonegotiate
S-2(config-if-range)# duplex auto
S-2(config-if-range)# channel-group 2 mode active
S-2(config-if-range)# shutdown
S-2(config-if-range)# no shutdown
If a member port of Po2 still shows (s) or (I) after both switches are fixed, restart the member ports on both switches once more, then wait for the ports to turn green (or click Fast Forward Time):
MULTI-1:
MULTI-1(config)# interface range gigabitethernet 1/0/3 - 4
MULTI-1(config-if-range)# shutdown
MULTI-1(config-if-range)# no shutdown
S-2:
S-2(config)# interface range gigabitethernet 0/1 - 2
S-2(config-if-range)# shutdown
S-2(config-if-range)# no shutdown
Verify that channel group 2 is now in use (SU) on both switches and that all member ports are bundled (P):
MULTI-1:
MULTI-1# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

1      Po1(SU)           LACP   Gig1/0/1(P) Gig1/0/2(P)
2      Po2(SU)           LACP   Gig1/0/3(P) Gig1/0/4(P)
S-2:
S-2# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+----------------------------------------------

2      Po2(SU)           LACP   Gig0/1(P) Gig0/2(P)
3      Po3(SU)           LACP   Fa0/5(P) Fa0/6(P)
Note: Packet Tracer requires configuration of trunking and DTP mode on both portchannel interfaces and the component physical interfaces.
Step 3: Configure a static trunk uplink
a. On the S-3 switch, configure the port that is connected to R-1 G0/0/1 as a static trunk.
S-3(config)# interface gigabitethernet 0/1
S-3(config-if)# switchport mode trunk
b. Configure the Management VLAN as the native VLAN.
S-3(config-if)# switchport trunk native vlan 99
c. Disable DTP on the port.
S-3(config-if)# switchport nonegotiate
Part 5: Configure Inter-VLAN Routing
Step 1: Configure inter-VLAN routing on the Layer 3 switch.
a. Configure Inter-VLAN routing on the MULTI-1 Layer 3 switch for all VLANs in the VLAN Table that are configured on MULTI-1.
MULTI-1(config)# ip routing
MULTI-1(config)# interface vlan 10
MULTI-1(config-if)# ip address 10.0.10.1 255.255.255.0
MULTI-1(config-if)# interface vlan 20
MULTI-1(config-if)# ip address 10.0.20.1 255.255.255.0
MULTI-1(config-if)# interface vlan 30
MULTI-1(config-if)# ip address 10.0.30.1 255.255.255.0
b. Configure the switchport on MULTI-1 that is connected to R-1 with an IP address as shown in the Addressing Table.
MULTI-1(config)# interface gigabitethernet 1/1/1
MULTI-1(config-if)# no switchport
MULTI-1(config-if)# ip address 10.0.0.2 255.255.255.0
Step 2: Configure router-on-a-stick inter-VLAN routing on a router.
a. Configure inter-VLAN routing on R-1 for all the VLANs that are configured on the S-3 switch. Use the information in the Addressing Table.
R-1(config)# interface gigabitethernet 0/0/1
R-1(config-if)# no shutdown
R-1(config-if)# interface gigabitethernet 0/0/1.40
R-1(config-subif)# encapsulation dot1q 40
R-1(config-subif)# ip address 10.0.40.1 255.255.255.0
R-1(config-subif)# interface gigabitethernet 0/0/1.50
R-1(config-subif)# encapsulation dot1q 50
R-1(config-subif)# ip address 10.0.50.1 255.255.255.0
R-1(config-subif)# interface gigabitethernet 0/0/1.60
R-1(config-subif)# encapsulation dot1q 60
R-1(config-subif)# ip address 10.0.60.1 255.255.255.0
R-1(config-subif)# interface gigabitethernet 0/0/1.99
R-1(config-subif)# encapsulation dot1q 99 native
R-1(config-subif)# ip address 10.0.99.17 255.255.255.240
b. Be sure to configure descriptions of all interfaces.
R-1(config)# interface gigabitethernet 0/0/1
R-1(config-if)# description Trunk to S-3 G0/1
R-1(config-if)# interface gigabitethernet 0/0/1.40
R-1(config-subif)# description Gateway for VLAN 40 (FAC)
R-1(config-subif)# interface gigabitethernet 0/0/1.50
R-1(config-subif)# description Gateway for VLAN 50 (FAB1)
R-1(config-subif)# interface gigabitethernet 0/0/1.60
R-1(config-subif)# description Gateway for VLAN 60 (FAB2)
R-1(config-subif)# interface gigabitethernet 0/0/1.99
R-1(config-subif)# description Gateway for VLAN 99 (ADMIN, native)
Step 3: Configure default gateways on hosts.
a. Configure default gateway addresses on all hosts on the LANs.
| Host | IP Address | Subnet Mask | Default Gateway |
|---|---|---|---|
| Host 1 | 10.0.10.10 | 255.255.255.0 | 10.0.10.1 |
| Host 2 | 10.0.20.20 | 255.255.255.0 | 10.0.20.1 |
| Host 3 | 10.0.30.30 | 255.255.255.0 | 10.0.30.1 |
| Host 4 | 10.0.10.11 | 255.255.255.0 | 10.0.10.1 |
| Host 5 | 10.0.20.21 | 255.255.255.0 | 10.0.20.1 |
| Host 6 | 10.0.30.31 | 255.255.255.0 | 10.0.30.1 |
| Host 7 | 10.0.40.41 | 255.255.255.0 | 10.0.40.1 |
| Host 8 | 10.0.50.51 | 255.255.255.0 | 10.0.50.1 |
| Host 9 | 10.0.60.61 | 255.255.255.0 | 10.0.60.1 |
| Admin Host | 10.0.99.19 | 255.255.255.240 | 10.0.99.17 |
b. Verify connectivity between all hosts on both LANs with each other and the Web Server.
c. Verify that a host can connect to the SVI of switch S-3 over SSH.
C:\> ssh -l admin 10.0.99.18
Password:
Last Updated: January 2021
ID 112
Device Configs - Final
ROUTER R-1
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 112
!--- ANSWER SCRIPT FOR ROUTER R-1
!--- Usage: copy this whole file and paste it into the R-1 terminal (start at the Router> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1: Basic Router Configuration.
! --------------------------------------------------------------

!--- b. Static routes provided by the exam (paste as given).
ip route 10.0.10.0 255.255.255.0 GigabitEthernet0/0/0
ip route 10.0.20.0 255.255.255.0 GigabitEthernet0/0/0
ip route 10.0.30.0 255.255.255.0 GigabitEthernet0/0/0

!--- Optional: stop the router from treating mistyped commands as host names.
no ip domain lookup

!--- c. The enable secret password.
enable secret class

!--- c. A console password.
line console 0
 password cisco
 login
 exit

!--- c. Remote access to the VTY lines.
line vty 0 4
 password cisco
 login
 exit

!--- c. A banner MOTD message.
banner motd #Authorized Access Only!#

!--- c. The device hostname according to the value in the addressing table.
hostname R-1

!--- c. All clear text passwords should be encrypted.
service password-encryption

!--- c. Interface addressing and description on G0/0/0.
interface gigabitethernet 0/0/0
 description Link to MULTI-1 G1/1/1
 ip address 10.0.0.1 255.255.255.0
 no shutdown
 exit

!--- c. Interface addressing and description on S0/1/0.
interface serial 0/1/0
 description Link to ISP
 ip address 209.165.201.2 255.255.255.252
 no shutdown
 exit

! --------------------------------------------------------------
!--- Part 5: Configure Inter-VLAN Routing.
! --------------------------------------------------------------

!--- Step 2a/b. Enable the physical trunk interface toward S-3, with description.
interface gigabitethernet 0/0/1
 description Trunk to S-3 G0/1
 no shutdown
 exit

!--- Step 2a/b. Subinterface for VLAN 40, with description.
interface gigabitethernet 0/0/1.40
 description Gateway for VLAN 40 (FAC)
 encapsulation dot1q 40
 ip address 10.0.40.1 255.255.255.0
 exit

!--- Step 2a/b. Subinterface for VLAN 50, with description.
interface gigabitethernet 0/0/1.50
 description Gateway for VLAN 50 (FAB1)
 encapsulation dot1q 50
 ip address 10.0.50.1 255.255.255.0
 exit

!--- Step 2a/b. Subinterface for VLAN 60, with description.
interface gigabitethernet 0/0/1.60
 description Gateway for VLAN 60 (FAB2)
 encapsulation dot1q 60
 ip address 10.0.60.1 255.255.255.0
 exit

!--- Step 2a/b. Subinterface for VLAN 99 (native VLAN), with description.
interface gigabitethernet 0/0/1.99
 description Gateway for VLAN 99 (ADMIN, native)
 encapsulation dot1q 99 native
 ip address 10.0.99.17 255.255.255.240
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief     -> G0/0/0, S0/1/0, G0/0/1 and the four subinterfaces up/up
!---   show ip route               -> connected routes for VLANs 40, 50, 60, 99; static routes to 10.0.10.0, .20.0, .30.0
! ==============================================================
MULTILAYER SWITCH MULTI-1
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 112
!--- ANSWER SCRIPT FOR MULTILAYER SWITCH MULTI-1
!--- Usage: copy this whole file and paste it into the MULTI-1 terminal (start at the Switch> or MULTI-1> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Device name from the Addressing Table. In some exam IDs this switch still has the default name (Switch); the command is harmless if it is already named.
hostname MULTI-1

!--- Step 1. Create and name VLANs 10, 20 and 30.
vlan 10
 name SALES
 exit
vlan 20
 name ACCT
 exit
vlan 30
 name EXEC
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 1. Channel group 1 (G1/0/1-2, to S-1) and channel group 2 (G1/0/3-4, to S-2) with LACP active.
interface range gigabitethernet 1/0/1 - 2
 channel-group 1 mode active
 exit
interface range gigabitethernet 1/0/3 - 4
 channel-group 2 mode active
 exit

!--- Step 2a. Port channels as static trunks with DTP disabled.
interface port-channel 1
 switchport mode trunk
 switchport nonegotiate
 exit
interface port-channel 2
 switchport mode trunk
 switchport nonegotiate
 exit

!--- Step 2b. Troubleshoot Po2: G1/0/4 is preconfigured without "switchport mode trunk". Remove G1/0/3-4 from the channel, give both ports the same trunk settings, add them back and restart them.
interface range gigabitethernet 1/0/3 - 4
 no channel-group 2
 switchport mode trunk
 switchport nonegotiate
 channel-group 2 mode active
 shutdown
 no shutdown
 exit


! --------------------------------------------------------------
!--- Part 5: Configure Inter-VLAN Routing.
! --------------------------------------------------------------

!--- Step 1a. Enable routing and configure the SVIs for VLANs 10, 20 and 30.
ip routing
interface vlan 10
 ip address 10.0.10.1 255.255.255.0
 no shutdown
 exit
interface vlan 20
 ip address 10.0.20.1 255.255.255.0
 no shutdown
 exit
interface vlan 30
 ip address 10.0.30.1 255.255.255.0
 no shutdown
 exit

!--- Step 1b. G1/1/1 (to R-1) as a routed port with the address from the Addressing Table.
interface gigabitethernet 1/1/1
 no switchport
 ip address 10.0.0.2 255.255.255.0
 no shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show etherchannel summary   -> Po1(SU) and Po2(SU), LACP, member ports (P)
!---   show interfaces trunk       -> Po1 and Po2 trunking, mode on (DTP off)
!---   show ip route               -> C routes for VLANs 10, 20, 30 and the G1/1/1 network
!--- Note: If a Po2 member port still shows (s) or (I) after both switches are configured, enter "shutdown" and "no shutdown" again on G1/0/3-4 of MULTI-1 and G0/1-2 of S-2, then wait for the ports to turn green.
! ==============================================================
SWITCH S-1
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 112
!--- ANSWER SCRIPT FOR SWITCH S-1
!--- Usage: copy this whole file and paste it into the S-1 terminal (start at the S-1> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Step 1. Create and name VLANs 10, 20 and 30.
vlan 10
 name SALES
 exit
vlan 20
 name ACCT
 exit
vlan 30
 name EXEC
 exit

!--- Step 2. Static access ports per the Port to VLAN Assignment Table.
interface range fastethernet 0/7 - 10
 switchport mode access
 switchport access vlan 10
 exit
interface range fastethernet 0/11 - 15
 switchport mode access
 switchport access vlan 20
 exit
interface range fastethernet 0/16 - 24
 switchport mode access
 switchport access vlan 30
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 1. Channel group 1 (G0/1-2, to MULTI-1) and channel group 3 (F0/5-6, to S-2) with LACP active.
interface range gigabitethernet 0/1 - 2
 channel-group 1 mode active
 exit
interface range fastethernet 0/5 - 6
 channel-group 3 mode active
 exit

!--- Step 2a. Port channels as static trunks with DTP disabled.
interface port-channel 1
 switchport mode trunk
 switchport nonegotiate
 exit
interface port-channel 3
 switchport mode trunk
 switchport nonegotiate
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show etherchannel summary   -> Po1(SU) and Po3(SU), LACP, member ports (P)
!---   show interfaces trunk       -> Po1 and Po3 trunking, mode on (DTP off)
!---   show vlan brief             -> F0/7-10 in VLAN 10, F0/11-15 in VLAN 20, F0/16-24 in VLAN 30
! ==============================================================
SWITCH S-2
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 112
!--- ANSWER SCRIPT FOR SWITCH S-2
!--- Usage: copy this whole file and paste it into the S-2 terminal (start at the S-2> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Step 1. Create and name VLANs 10, 20 and 30.
vlan 10
 name SALES
 exit
vlan 20
 name ACCT
 exit
vlan 30
 name EXEC
 exit

!--- Step 2. Static access ports per the Port to VLAN Assignment Table.
interface range fastethernet 0/7 - 10
 switchport mode access
 switchport access vlan 10
 exit
interface range fastethernet 0/11 - 15
 switchport mode access
 switchport access vlan 20
 exit
interface range fastethernet 0/16 - 24
 switchport mode access
 switchport access vlan 30
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 1. Channel group 2 (G0/1-2, to MULTI-1) and channel group 3 (F0/5-6, to S-1) with LACP active.
interface range gigabitethernet 0/1 - 2
 channel-group 2 mode active
 exit
interface range fastethernet 0/5 - 6
 channel-group 3 mode active
 exit

!--- Step 2a. Port channels as static trunks with DTP disabled.
interface port-channel 2
 switchport mode trunk
 switchport nonegotiate
 exit
interface port-channel 3
 switchport mode trunk
 switchport nonegotiate
 exit

!--- Step 2b. Troubleshoot Po2: G0/2 is preconfigured without "switchport mode trunk" and with duplex half (the assessment checks the port mode of G0/2). Remove G0/1-2 from the channel, give both ports the same settings, add them back and restart them.
interface range gigabitethernet 0/1 - 2
 no channel-group 2
 switchport mode trunk
 switchport nonegotiate
 duplex auto
 channel-group 2 mode active
 shutdown
 no shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show etherchannel summary   -> Po2(SU) and Po3(SU), LACP, member ports (P)
!---   show interfaces trunk       -> Po2 and Po3 trunking, mode on (DTP off)
!---   show vlan brief             -> F0/7-10 in VLAN 10, F0/11-15 in VLAN 20, F0/16-24 in VLAN 30
!--- Note: If a Po2 member port still shows (s) or (I) after both switches are configured, enter "shutdown" and "no shutdown" again on G1/0/3-4 of MULTI-1 and G0/1-2 of S-2, then wait for the ports to turn green.
! ==============================================================
SWITCH S-3
! ==============================================================
!--- SRWE PT Practice Skills Assessment (PTSA) Part 1 - ID 112
!--- ANSWER SCRIPT FOR SWITCH S-3
!--- Usage: copy this whole file and paste it into the S-3 terminal (start at the S-3> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- The hostname and VLAN names can change with each exam ID - check them against the tables in your exam before pasting.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2: Basic Switch Configuration.
! --------------------------------------------------------------

!--- Step 1a. SVI 99 with the address from the Addressing Table.
interface vlan 99
 ip address 10.0.99.18 255.255.255.240
 no shutdown
 exit

!--- Step 1b. Default gateway so the SVI is reachable from other networks.
ip default-gateway 10.0.99.17

!--- Step 2. IP domain name (required before the RSA keys can be generated).
ip domain-name acad.pt

!--- Enable secret password (checked by the assessment).
enable secret class

!--- Step 2. Username admin with an encrypted password.
username admin privilege 15 secret C1sco123!

!--- Step 2. RSA keys with a 1024-bit modulus.
crypto key generate rsa general-keys modulus 1024

!--- Optional: use SSH version 2.
ip ssh version 2

!--- Step 2. All VTY lines accept SSH only and use the local username and password.
line vty 0 15
 transport input ssh
 login local
 exit

! --------------------------------------------------------------
!--- Part 3: VLAN Configuration.
! --------------------------------------------------------------

!--- Step 1. Create and name VLANs 40, 50, 60 and 99.
vlan 40
 name FAC
 exit
vlan 50
 name FAB1
 exit
vlan 60
 name FAB2
 exit
vlan 99
 name ADMIN
 exit

!--- Step 2. Static access ports per the Port to VLAN Assignment Table.
interface range fastethernet 0/1 - 5
 switchport mode access
 switchport access vlan 40
 exit
interface range fastethernet 0/6 - 10
 switchport mode access
 switchport access vlan 50
 exit
interface range fastethernet 0/11 - 15
 switchport mode access
 switchport access vlan 60
 exit
interface fastethernet 0/24
 switchport mode access
 switchport access vlan 99
 exit

! --------------------------------------------------------------
!--- Part 4: EtherChannel and Trunking Configuration.
! --------------------------------------------------------------

!--- Step 3. G0/1 (to R-1 G0/0/1): static trunk, native VLAN 99, DTP disabled.
interface gigabitethernet 0/1
 switchport mode trunk
 switchport trunk native vlan 99
 switchport nonegotiate
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief     -> Vlan99 10.0.99.18 up/up (mask 255.255.255.240 in show running-config)
!---   show interfaces trunk       -> Gig0/1 trunking, mode on, native VLAN 99
!---   ping 10.0.99.17             -> R-1 G0/0/1.99 replies
!---   From the management host: ssh -l admin 10.0.99.18 (password C1sco123!) -> login succeeds
! ==============================================================
HOST 1
HOST 2
HOST 3
HOST 4
HOST 5
HOST 6
HOST 7
HOST 8
HOST 9
ADMIN HOST