12.6.1 Packet Tracer - Troubleshooting Challenge - Document the Network (Answers)

Same for:

  • 1.2.13 Packet Tracer - Troubleshooting Challenge - Document the Network
  • 37.2.13 Packet Tracer - Troubleshooting Challenge - Document the Network

12.6.1 Packet Tracer - Troubleshooting Challenge - Document the Network Answers

Topology
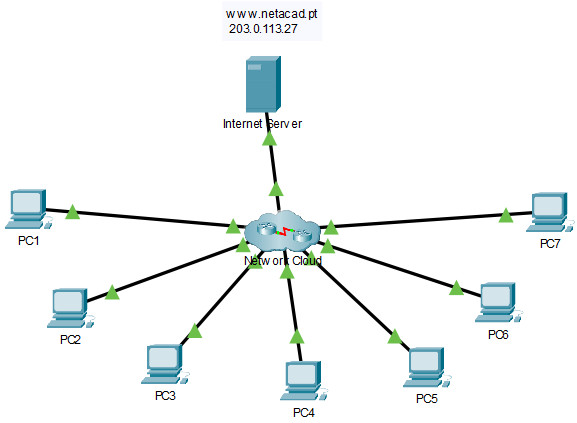
12.6.1 Packet Tracer - Troubleshooting Challenge - Document the Network topology

12.6.1 Packet Tracer - Troubleshooting Challenge - Document the Network

Table of Contents

Addressing Table

Device Interface Device Type
(router, switch, host)
IP Address Subnet Mask Default Gateway
PC1 NIC Host 192.168.1.153 255.255.255.0 192.168.1.1
PC2 NIC Host 192.168.3.50 255.255.255.0 192.168.3.1
PC3 NIC Host 192.168.4.115 255.255.255.0 192.168.4.1
PC4 NIC Host 192.168.5.83 255.255.255.128 192.168.5.1
PC5 NIC Host 192.168.5.227 255.255.255.128 192.168.5.129
PC6 NIC Host 192.168.2.48 255.255.255.224 192.168.2.33
PC7 NIC Host 192.168.2.67 255.255.255.224 192.168.2.65
Hub G0/0/0 router 192.0.2.1 255.255.255.252 N/A
Hub S0/1/0 router 192.168.0.1 255.255.255.252 N/A
Hub S0/1/1 router 192.168.0.5 255.255.255.252 N/A
Hub S0/2/0 router 192.168.0.9 255.255.255.252 N/A
Hub S0/2/1 router 192.168.0.13 255.255.255.252 N/A
Branch-1 G0/0/0 router 192.168.1.1 255.255.255.0 N/A
Branch-1 S0/1/0 router 192.168.0.2 255.255.255.252 N/A
Branch-2 G0/0/0.1 router 192.168.2.1 255.255.255.224 N/A
Branch-2 G0/0/0.32 router 192.168.2.33 255.255.255.224 N/A
Branch-2 G0/0/0.64 router 192.168.2.65 255.255.255.224 N/A
Branch-2 S0/1/0 router 192.168.0.6 255.255.255.252 N/A
Factory G0/0/0 router 192.168.3.1 255.255.255.0 N/A
Factory G0/0/1 router 192.168.4.1 255.255.255.0 N/A
Factory S0/1/0 router 192.168.0.14 255.255.255.252 N/A
HQ G0/0/0.1 router 192.168.6.1 255.255.255.0 N/A
HQ G0/0/0.5 router 192.168.5.1 255.255.255.128 N/A
HQ G0/0/0.10 router 192.168.5.129 255.255.255.128 N/A
HQ S0/1/0 router 192.168.0.10 255.255.255.252 N/A
SW-B1 VLAN 1 switch 192.168.1.252 255.255.255.0 192.168.1.1
SW-B2 VLAN 1 switch 192.168.2.17 255.255.255.224 192.168.2.1
SW-F1 VLAN 1 switch 192.168.3.252 255.255.255.0 192.168.3.1
SW-F2 VLAN 1 switch 192.168.4.252 255.255.255.0 192.168.4.1
SW-HQ1 VLAN 1 switch 192.168.6.252 255.255.255.0 192.168.6.1
SW-HQ2 VLAN 1 switch 192.168.6.253 255.255.255.0 192.168.6.1
SW-HQ3 VLAN 1 switch 192.168.6.254 255.255.255.0 192.168.6.1
DNS Server NIC host (server) 192.168.5.252 255.255.255.128 192.168.5.129
ISP G0/0/0 router 192.0.2.2 255.255.255.252 N/A
Internet Server NIC host (server) 203.0.113.27 N/A N/A

Objectives

In this lab, you will document a network that is unknown to you.

  • Test network connectivity.
  • Compile host addressing information.
  • Remotely access default gateway devices.
  • Document default gateway device configurations.
  • Discover devices on the network.
  • Draw the network topology.

Background / Scenario

Your employer has been hired to take over the administration of a corporate network because the previous network administrator has left the company. The network documentation is missing and needs to be recreated. Your job is to document the hosts and network devices including all the device addressing and logical interconnections. You will remotely access network devices and use network discovery to complete a device table and draw the network topology.

This is Part I of a two-part series of activities. You will use the documentation that you create in this activity to guide you as you troubleshoot the network in Part II, Packet Tracer - Troubleshooting Challenge - Using Documentation to Solve Issues.

As you investigate and document the network topology, make note of issues that you discover that do not adhere to the practices taught in the CCNA curriculum.

Instructions

Part 1: Test Connectivity

Ping between the PCs and the internet server to test the network. All PCs should be able to ping one another and the internet server.

C:\> ping 203.0.113.27

Pinging 203.0.113.27 with 32 bytes of data:

Reply from 203.0.113.27: bytes=32 time=7ms TTL=125
Reply from 203.0.113.27: bytes=32 time=6ms TTL=125
Reply from 203.0.113.27: bytes=32 time=1ms TTL=125
Reply from 203.0.113.27: bytes=32 time=6ms TTL=125

Ping statistics for 203.0.113.27:
    Packets: Sent = 4, Received = 4, Lost = 0 (0% loss),
Approximate round trip times in milli-seconds:
    Minimum = 1ms, Maximum = 7ms, Average = 5ms

What we learned:
PC1 can reach the Internet Server (203.0.113.27). The TTL value of 125 shows that the packets cross three routers: Branch-1, Hub, and the ISP router.

Part 2: Discover PC Configuration Information

Go to the command prompt of each PC and display the IP settings. Record this information in the documentation table.

C:\> ipconfig /all

FastEthernet0 Connection: (default port)

   Connection-specific DNS Suffix..:
   Physical Address................: 000C.CF0A.D737
   Link-local IPv6 Address.........: FE80::20C:CFFF:FE0A:D737
   IPv6 Address....................: ::
   IPv4 Address....................: 192.168.1.153
   Subnet Mask.....................: 255.255.255.0
   Default Gateway.................: ::
                                     192.168.1.1
   DHCP Servers....................: 0.0.0.0
   DHCPv6 IAID.....................:
   DHCPv6 Client DUID..............: 00-01-00-01-7E-32-AB-6D-00-0C-CF-0A-D7-37
   DNS Servers.....................: ::
                                     192.168.5.252

C:\> ipconfig /all

FastEthernet0 Connection: (default port)

   Connection-specific DNS Suffix..:
   Physical Address................: 0005.5E73.18D6
   Link-local IPv6 Address.........: FE80::205:5EFF:FE73:18D6
   IPv6 Address....................: ::
   IPv4 Address....................: 192.168.3.50
   Subnet Mask.....................: 255.255.255.0
   Default Gateway.................: ::
                                     192.168.3.1
   DHCP Servers....................: 0.0.0.0
   DHCPv6 IAID.....................:
   DHCPv6 Client DUID..............: 00-01-00-01-7E-32-AB-6D-00-05-5E-73-18-D6
   DNS Servers.....................: ::
                                     192.168.5.252

C:\> ipconfig /all

FastEthernet0 Connection: (default port)

   Connection-specific DNS Suffix..:
   Physical Address................: 0060.4770.6D7C
   Link-local IPv6 Address.........: FE80::260:47FF:FE70:6D7C
   IPv6 Address....................: ::
   IPv4 Address....................: 192.168.4.115
   Subnet Mask.....................: 255.255.255.0
   Default Gateway.................: ::
                                     192.168.4.1
   DHCP Servers....................: 0.0.0.0
   DHCPv6 IAID.....................:
   DHCPv6 Client DUID..............: 00-01-00-01-7E-32-AB-6D-00-60-47-70-6D-7C
   DNS Servers.....................: ::
                                     192.168.5.252

C:\> ipconfig /all

FastEthernet0 Connection: (default port)

   Connection-specific DNS Suffix..:
   Physical Address................: 000A.F350.C468
   Link-local IPv6 Address.........: FE80::20A:F3FF:FE50:C468
   IPv6 Address....................: ::
   IPv4 Address....................: 192.168.5.83
   Subnet Mask.....................: 255.255.255.128
   Default Gateway.................: ::
                                     192.168.5.1
   DHCP Servers....................: 0.0.0.0
   DHCPv6 IAID.....................:
   DHCPv6 Client DUID..............: 00-01-00-01-7E-32-AB-6D-00-0A-F3-50-C4-68
   DNS Servers.....................: ::
                                     192.168.5.252

C:\> ipconfig /all

FastEthernet0 Connection: (default port)

   Connection-specific DNS Suffix..:
   Physical Address................: 0000.0C1B.50E7
   Link-local IPv6 Address.........: FE80::200:CFF:FE1B:50E7
   IPv6 Address....................: ::
   IPv4 Address....................: 192.168.5.227
   Subnet Mask.....................: 255.255.255.128
   Default Gateway.................: ::
                                     192.168.5.129
   DHCP Servers....................: 0.0.0.0
   DHCPv6 IAID.....................:
   DHCPv6 Client DUID..............: 00-01-00-01-7E-32-AB-6D-00-00-0C-1B-50-E7
   DNS Servers.....................: ::
                                     192.168.5.252

C:\> ipconfig /all

FastEthernet0 Connection: (default port)

   Connection-specific DNS Suffix..:
   Physical Address................: 0006.2AB8.5971
   Link-local IPv6 Address.........: FE80::206:2AFF:FEB8:5971
   IPv6 Address....................: ::
   IPv4 Address....................: 192.168.2.48
   Subnet Mask.....................: 255.255.255.224
   Default Gateway.................: ::
                                     192.168.2.33
   DHCP Servers....................: 0.0.0.0
   DHCPv6 IAID.....................:
   DHCPv6 Client DUID..............: 00-01-00-01-7E-32-AB-6D-00-06-2A-B8-59-71
   DNS Servers.....................: ::
                                     192.168.5.252

C:\> ipconfig /all

FastEthernet0 Connection: (default port)

   Connection-specific DNS Suffix..:
   Physical Address................: 000B.BEEE.1678
   Link-local IPv6 Address.........: FE80::20B:BEFF:FEEE:1678
   IPv6 Address....................: ::
   IPv4 Address....................: 192.168.2.67
   Subnet Mask.....................: 255.255.255.224
   Default Gateway.................: ::
                                     192.168.2.65
   DHCP Servers....................: 0.0.0.0
   DHCPv6 IAID.....................:
   DHCPv6 Client DUID..............: 00-01-00-01-7E-32-AB-6D-00-0B-BE-EE-16-78
   DNS Servers.....................: ::
                                     192.168.5.252


What we learned:

  • All seven PCs use static IPv4 addressing (DHCP Servers: 0.0.0.0).
  • All PCs use the same DNS server: 192.168.5.252. This address belongs to the HQ 192.168.5.128/25 subnet (VLAN 10), so the DNS server is located at HQ.
  • Each default gateway is the router of that LAN. The gateways show that there are four LAN sites: Branch-1, Branch-2, Factory, and HQ.

PC IPv4 Address Subnet Mask Default Gateway Site / LAN
PC1 192.168.1.153 255.255.255.0 (/24) 192.168.1.1 Branch-1 LAN
PC2 192.168.3.50 255.255.255.0 (/24) 192.168.3.1 Factory LAN 1
PC3 192.168.4.115 255.255.255.0 (/24) 192.168.4.1 Factory LAN 2
PC4 192.168.5.83 255.255.255.128 (/25) 192.168.5.1 HQ VLAN 5
PC5 192.168.5.227 255.255.255.128 (/25) 192.168.5.129 HQ VLAN 10
PC6 192.168.2.48 255.255.255.224 (/27) 192.168.2.33 Branch-2 VLAN 32
PC7 192.168.2.67 255.255.255.224 (/27) 192.168.2.65 Branch-2 VLAN 64

Part 3: Discover Information about the Default Gateway Devices

Connect to each default gateway device using the Telnet protocol and record information about the interfaces that are in use in the table. The VTY password is cisco and privileged EXEC password is class.

C:\> telnet IP_address
Access Map

Use this table to reach every router and switch. The switches and the Hub router are reached from a Telnet session on a nearby router.

Device Telnet from IP Address VTY Password Enable Password
Branch-1 PC1 192.168.1.1 cisco class
Branch-2 PC6 (or any PC) 192.168.2.33 (or 192.168.0.6) cisco class
Factory PC2 192.168.3.1 cisco class
HQ PC4 192.168.5.1 cisco class
Hub Branch-1 (telnet session) 192.168.0.1 cisco class
SW-B1 PC1 192.168.1.252 cisco class
SW-B2 Branch-2 (telnet session) 192.168.2.17 cisco class
SW-F1 Factory (telnet session) 192.168.3.252 cisco class
SW-F2 Factory (telnet session) 192.168.4.252 cisco class
SW-HQ1 HQ (telnet session) 192.168.6.252 cisco class
SW-HQ2 HQ (telnet session) 192.168.6.253 cisco class
SW-HQ3 HQ (telnet session) 192.168.6.254 cisco class

C:\> telnet 192.168.1.1
Trying 192.168.1.1 ...Open


User Access Verification

Password: cisco
Branch-1> enable
Password: class
Branch-1#
Branch-1# show ip interface brief
Interface              IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0/0   192.168.1.1     YES manual up                    up
GigabitEthernet0/0/1   unassigned      YES unset  administratively down down
Serial0/1/0            192.168.0.2     YES manual up                    up
Serial0/1/1            unassigned      YES unset  administratively down down
Vlan1                  unassigned      YES unset  administratively down down

C:\> telnet 192.168.0.6
Trying 192.168.0.6 ...Open


User Access Verification

Password: cisco
Branch-2> enable
Password: class
Branch-2#
Branch-2# show ip interface brief
Interface              IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0/0   unassigned      YES manual up                    up
GigabitEthernet0/0/0.1 192.168.2.1     YES manual up                    up
GigabitEthernet0/0/0.32192.168.2.33    YES manual up                    up
GigabitEthernet0/0/0.64192.168.2.65    YES manual up                    up
GigabitEthernet0/0/1   unassigned      YES unset  administratively down down
Serial0/1/0            192.168.0.6     YES manual up                    up
Serial0/1/1            unassigned      YES unset  administratively down down
Vlan1                  unassigned      YES unset  administratively down down
Branch-2# show running-config | section interface GigabitEthernet0/0/0
interface GigabitEthernet0/0/0
 no ip address
 duplex auto
 speed auto
interface GigabitEthernet0/0/0.1
 encapsulation dot1Q 1 native
 ip address 192.168.2.1 255.255.255.224
interface GigabitEthernet0/0/0.32
 encapsulation dot1Q 32
 ip address 192.168.2.33 255.255.255.224
interface GigabitEthernet0/0/0.64
 encapsulation dot1Q 64
 ip address 192.168.2.65 255.255.255.224

C:\> telnet 192.168.3.1
Trying 192.168.3.1 ...Open


User Access Verification

Password: cisco
Factory> enable
Password: class
Factory#
Factory# show ip interface brief
Interface              IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0/0   192.168.3.1     YES manual up                    up
GigabitEthernet0/0/1   192.168.4.1     YES manual up                    up
Serial0/1/0            192.168.0.14    YES manual up                    up
Serial0/1/1            unassigned      YES unset  administratively down down
Vlan1                  unassigned      YES unset  administratively down down

C:\> telnet 192.168.5.1
Trying 192.168.5.1 ...Open


User Access Verification

Password: cisco
HQ> enable
Password: class
HQ#
HQ# show ip interface brief
Interface              IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0/0   unassigned      YES unset  up                    up
GigabitEthernet0/0/0.1 192.168.6.1     YES manual up                    up
GigabitEthernet0/0/0.5 192.168.5.1     YES manual up                    up
GigabitEthernet0/0/0.10192.168.5.129   YES manual up                    up
GigabitEthernet0/0/1   unassigned      YES unset  administratively down down
Serial0/1/0            192.168.0.10    YES manual up                    up
Serial0/1/1            unassigned      YES unset  administratively down down
Vlan1                  unassigned      YES unset  up                    down
HQ# show running-config | section interface GigabitEthernet0/0/0
interface GigabitEthernet0/0/0
 no ip address
 duplex auto
 speed auto
interface GigabitEthernet0/0/0.1
 encapsulation dot1Q 1 native
 ip address 192.168.6.1 255.255.255.0
interface GigabitEthernet0/0/0.5
 encapsulation dot1Q 5
 ip address 192.168.5.1 255.255.255.128
interface GigabitEthernet0/0/0.10
 encapsulation dot1Q 10
 ip address 192.168.5.129 255.255.255.128


What we learned:

  • Branch-1 and Factory route between physical LAN interfaces. Branch-2 and HQ use router-on-a-stick: the G0/0/0 interface is divided into 802.1Q subinterfaces, one for each VLAN, and VLAN 1 is the native VLAN.
  • Every gateway router has one active serial interface (S0/1/0) in a /30 subnet of 192.168.0.0/24. These are the WAN links to the rest of the network.

Router Interface IP Address / Prefix Connects to
Branch-1 G0/0/0 192.168.1.1/24 PC1 LAN
Branch-1 S0/1/0 192.168.0.2/30 WAN link
Branch-2 G0/0/0.1 (native VLAN 1) 192.168.2.1/27 Switch management (SW-B2)
Branch-2 G0/0/0.32 (VLAN 32) 192.168.2.33/27 PC6 LAN
Branch-2 G0/0/0.64 (VLAN 64) 192.168.2.65/27 PC7 LAN
Branch-2 S0/1/0 192.168.0.6/30 WAN link
Factory G0/0/0 192.168.3.1/24 PC2 LAN
Factory G0/0/1 192.168.4.1/24 PC3 LAN
Factory S0/1/0 192.168.0.14/30 WAN link
HQ G0/0/0.1 (native VLAN 1) 192.168.6.1/24 Switch management (SW-HQ1/2/3)
HQ G0/0/0.5 (VLAN 5) 192.168.5.1/25 PC4 LAN
HQ G0/0/0.10 (VLAN 10) 192.168.5.129/25 PC5 LAN and DNS server
HQ S0/1/0 192.168.0.10/30 WAN link

Part 4: Reconstruct the Network Topology

In this part of the activity, you will continue recording information about the devices in the network in the Addressing Table. In addition, you will start to diagram the network topology based on what you can discover about the device interconnections.

Step 1: Access Routing Tables on Each Gateway Device.

Use the routing tables in each router to learn more about the network. Make notes of your findings.

Branch-1# show ip route
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
       D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
       N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
       E1 - OSPF external type 1, E2 - OSPF external type 2, E - EGP
       i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area
       * - candidate default, U - per-user static route, o - ODR
       P - periodic downloaded static route

Gateway of last resort is 192.168.0.1 to network 0.0.0.0

      192.168.0.0/24 is variably subnetted, 5 subnets, 2 masks
C        192.168.0.0/30 is directly connected, Serial0/1/0
L        192.168.0.2/32 is directly connected, Serial0/1/0
O        192.168.0.4/30 [110/128] via 192.168.0.1, 00:09:57, Serial0/1/0
O        192.168.0.8/30 [110/128] via 192.168.0.1, 00:09:57, Serial0/1/0
O        192.168.0.12/30 [110/128] via 192.168.0.1, 00:09:57, Serial0/1/0
      192.168.1.0/24 is variably subnetted, 2 subnets, 2 masks
C        192.168.1.0/24 is directly connected, GigabitEthernet0/0/0
L        192.168.1.1/32 is directly connected, GigabitEthernet0/0/0
      192.168.2.0/27 is subnetted, 3 subnets
O        192.168.2.0/27 [110/129] via 192.168.0.1, 00:09:47, Serial0/1/0
O        192.168.2.32/27 [110/129] via 192.168.0.1, 00:09:47, Serial0/1/0
O        192.168.2.64/27 [110/129] via 192.168.0.1, 00:09:47, Serial0/1/0
O     192.168.3.0/24 [110/129] via 192.168.0.1, 00:09:47, Serial0/1/0
O     192.168.4.0/24 [110/129] via 192.168.0.1, 00:09:47, Serial0/1/0
      192.168.5.0/25 is subnetted, 2 subnets
O        192.168.5.0/25 [110/129] via 192.168.0.1, 00:09:47, Serial0/1/0
O        192.168.5.128/25 [110/129] via 192.168.0.1, 00:09:47, Serial0/1/0
O     192.168.6.0/24 [110/129] via 192.168.0.1, 00:09:47, Serial0/1/0
O*E2  0.0.0.0/0 [110/1] via 192.168.0.1, 00:09:57, Serial0/1/0
Branch-1# show ip protocols

Routing Protocol is "ospf 10"
  Outgoing update filter list for all interfaces is not set
  Incoming update filter list for all interfaces is not set
  Router ID 192.168.1.1
  Number of areas in this router is 1. 1 normal 0 stub 0 nssa
  Maximum path: 4
  Routing for Networks:
    192.168.1.0 0.0.0.255 area 0
    192.168.0.0 0.0.0.3 area 0
  Routing Information Sources:
    Gateway         Distance      Last Update
<output omitted>

Branch-1> telnet 192.168.0.1
Trying 192.168.0.1 ...Open

User Access Verification

Password: cisco
Hub> enable
Password: class
Hub#
Hub# show ip interface brief
Interface              IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0/0   192.0.2.1       YES manual up                    up
GigabitEthernet0/0/1   unassigned      YES unset  administratively down down
Serial0/1/0            192.168.0.1     YES manual up                    up
Serial0/1/1            192.168.0.5     YES manual up                    up
Serial0/2/0            192.168.0.9     YES manual up                    up
Serial0/2/1            192.168.0.13    YES manual up                    up
Vlan1                  unassigned      YES unset  administratively down down
Hub# show ip route
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
       D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
       N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
       E1 - OSPF external type 1, E2 - OSPF external type 2, E - EGP
       i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area
       * - candidate default, U - per-user static route, o - ODR
       P - periodic downloaded static route

Gateway of last resort is 192.0.2.2 to network 0.0.0.0

      192.0.2.0/24 is variably subnetted, 2 subnets, 2 masks
C        192.0.2.0/30 is directly connected, GigabitEthernet0/0/0
L        192.0.2.1/32 is directly connected, GigabitEthernet0/0/0
      192.168.0.0/24 is variably subnetted, 8 subnets, 2 masks
C        192.168.0.0/30 is directly connected, Serial0/1/0
L        192.168.0.1/32 is directly connected, Serial0/1/0
C        192.168.0.4/30 is directly connected, Serial0/1/1
L        192.168.0.5/32 is directly connected, Serial0/1/1
C        192.168.0.8/30 is directly connected, Serial0/2/0
L        192.168.0.9/32 is directly connected, Serial0/2/0
C        192.168.0.12/30 is directly connected, Serial0/2/1
L        192.168.0.13/32 is directly connected, Serial0/2/1
O     192.168.1.0/24 [110/65] via 192.168.0.2, 00:46:13, Serial0/1/0
      192.168.2.0/27 is subnetted, 3 subnets
O        192.168.2.0/27 [110/65] via 192.168.0.6, 00:46:13, Serial0/1/1
O        192.168.2.32/27 [110/65] via 192.168.0.6, 00:46:13, Serial0/1/1
O        192.168.2.64/27 [110/65] via 192.168.0.6, 00:46:13, Serial0/1/1
O     192.168.3.0/24 [110/65] via 192.168.0.14, 00:46:13, Serial0/2/1
O     192.168.4.0/24 [110/65] via 192.168.0.14, 00:46:13, Serial0/2/1
      192.168.5.0/25 is subnetted, 2 subnets
O        192.168.5.0/25 [110/65] via 192.168.0.10, 00:46:13, Serial0/2/0
O        192.168.5.128/25 [110/65] via 192.168.0.10, 00:46:13, Serial0/2/0
O     192.168.6.0/24 [110/65] via 192.168.0.10, 00:46:13, Serial0/2/0
S*    0.0.0.0/0 [1/0] via 192.0.2.2
Hub# show ip protocols

Routing Protocol is "ospf 10"
  Outgoing update filter list for all interfaces is not set
  Incoming update filter list for all interfaces is not set
  Router ID 192.168.0.13
  It is an autonomous system boundary router
  Redistributing External Routes from,
  Number of areas in this router is 1. 1 normal 0 stub 0 nssa
  Maximum path: 4
  Routing for Networks:
    192.168.0.0 0.0.0.3 area 0
    192.168.0.4 0.0.0.3 area 0
    192.168.0.8 0.0.0.3 area 0
    192.168.0.12 0.0.0.3 area 0
  Routing Information Sources:
    Gateway         Distance      Last Update
    192.168.0.13         110      00:16:28
    192.168.1.1          110      00:16:28
    192.168.2.65         110      00:16:27
    192.168.4.1          110      00:16:27
    192.168.6.1          110      00:16:27
  Distance: (default is 110)

Factory# show ip protocols

Routing Protocol is "ospf 10"
  Outgoing update filter list for all interfaces is not set
  Incoming update filter list for all interfaces is not set
  Router ID 192.168.4.1
  Number of areas in this router is 1. 1 normal 0 stub 0 nssa
  Maximum path: 4
  Routing for Networks:
    192.168.3.0 0.0.0.255 area 0
    192.168.4.0 0.0.0.255 area 0
    192.168.0.12 0.0.0.3 area 0
  Routing Information Sources:
    Gateway         Distance      Last Update
<output omitted>


What we learned:

  • Branch-1 learns every remote network through a single next hop, 192.168.0.1 (S0/1/0). The router at 192.168.0.1 is named Hub.
  • Hub has four serial interfaces, one /30 link to each site router: S0/1/0 to Branch-1 (192.168.0.2), S0/1/1 to Branch-2 (192.168.0.6), S0/2/0 to HQ (192.168.0.10), and S0/2/1 to Factory (192.168.0.14). This is a hub-and-spoke WAN.
  • Hub connects to the ISP on G0/0/0 (192.0.2.1/30) and has a static default route to 192.0.2.2. It sends this default route to the other routers through OSPF (O*E2 0.0.0.0/0 on Branch-1).
  • The site routers advertise their LAN networks in OSPF (for example 192.168.1.0/24 on Branch-1, 192.168.3.0/24 and 192.168.4.0/24 on Factory), but show ip protocols lists no passive interfaces. OSPF Hello packets are therefore sent out of the LAN interfaces toward the PCs.
  • All routers run OSPF process 10 in area 0. The OSPF router IDs are 192.168.0.13 (Hub), 192.168.1.1 (Branch-1), 192.168.2.65 (Branch-2), 192.168.4.1 (Factory), and 192.168.6.1 (HQ).
  • Remote networks in the routing tables: 192.168.1.0/24, 192.168.2.0/27, 192.168.2.32/27, 192.168.2.64/27, 192.168.3.0/24, 192.168.4.0/24, 192.168.5.0/25, 192.168.5.128/25, and 192.168.6.0/24.

Step 2: Discover Non-Gateway Devices.

Use a network discovery protocol to document neighboring devices. Record your findings in the addressing table. At this point you should also be able to begin documenting device interconnections.

Branch-1# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
SW-B1        Gig 0/0/0       132            S        2960          Gig 0/1
Hub          Ser 0/1/0       133            R        ISR4300       Ser 0/1/0

Branch-2# show cdp neighbors detail

Device ID: SW-B2
Entry address(es):
  IP address : 192.168.2.17
Platform: cisco 2960, Capabilities: Switch
Interface: GigabitEthernet0/0/0.1, Port ID (outgoing port): GigabitEthernet0/1
Holdtime: 159

Version :
Cisco IOS Software, C2960 Software (C2960-LANBASE-M), Version 12.2(25)FX, RELEASE
SOFTWARE (fc1)
Copyright (c) 1986-2005 by Cisco Systems, Inc.
Compiled Wed 12-Oct-05 22:05 by pt_team

advertisement version: 2
Duplex: full
-------------------------

Device ID: Hub
Entry address(es):
  IP address : 192.168.0.5
Platform: cisco ISR4300, Capabilities: Router
Interface: Serial0/1/0, Port ID (outgoing port): Serial0/1/1
Holdtime: 160

Version :
Cisco IOS XE Software, Version 03.13.04.S - Extended Support Release
Cisco IOS Software, ISR Software (X86_64_LINUX_IOSD-UNIVERSALK9-M), Version 15.5(3)S5,
RELEASE SOFTWARE (fc2)
Technical Support: http://www.cisco.com/techsupport
Copyright (c) 1986-2017 by Cisco Systems, Inc.
Compiled Mon 05-Oct-15 11:24 by mcpre

advertisement version: 2
Duplex: full

Factory# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
SW-F1        Gig 0/0/0       121            S        2960          Gig 0/1
SW-F2        Gig 0/0/1       121            S        2960          Gig 0/1
Hub          Ser 0/1/0       121            R        ISR4300       Ser 0/2/1

HQ# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
SW-HQ1       Gig 0/0/0.1     150            S        2960          Gig 0/1
Hub          Ser 0/1/0       150            R        ISR4300       Ser 0/2/0

Hub# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
ISP          Gig 0/0/0       131            R        ISR4300       Gig 0/0/0
HQ           Ser 0/2/0       139            R        ISR4300       Ser 0/1/0
Branch-1     Ser 0/1/0       140            R        ISR4300       Ser 0/1/0
Branch-2     Ser 0/1/1       141            R        ISR4300       Ser 0/1/0
Factory      Ser 0/2/1       142            R        ISR4300       Ser 0/1/0
Hub# show controllers serial 0/1/0
Interface Serial0/1/0
Hardware is PowerQUICC MPC860
DCE V.35, clock rate 2000000
<output omitted>


What we learned (topology, part 1):
CDP on the routers shows the physical links between the routers and the first switch at each site. Hub is the DCE end of the serial links (it provides the clock rate of 2000000). Hub connects to the ISP router through G0/0/0.

Device Interface Neighbor Neighbor Interface Network
Hub S0/1/0 Branch-1 S0/1/0 192.168.0.0/30
Hub S0/1/1 Branch-2 S0/1/0 192.168.0.4/30
Hub S0/2/0 HQ S0/1/0 192.168.0.8/30
Hub S0/2/1 Factory S0/1/0 192.168.0.12/30
Hub G0/0/0 ISP G0/0/0 192.0.2.0/30
Branch-1 G0/0/0 SW-B1 G0/1 192.168.1.0/24
Branch-2 G0/0/0 (trunk) SW-B2 G0/1 192.168.2.0/27, .32/27, .64/27
Factory G0/0/0 SW-F1 G0/1 192.168.3.0/24
Factory G0/0/1 SW-F2 G0/1 192.168.4.0/24
HQ G0/0/0 (trunk) SW-HQ1 G0/1 192.168.5.0/25, .128/25, 192.168.6.0/24

Part 5: Further Explore Device Configurations and Interconnections

Step 1: Access Device Configurations.

Connect to the other devices in the network. Gather information about the device configurations.

C:\> telnet 192.168.1.252
Trying 192.168.1.252 ...Open


User Access Verification

Password: cisco
SW-B1> enable
Password: class
SW-B1#
SW-B1# show running-config
Building configuration...

Current configuration : 1192 bytes
!
version 12.2
<output omitted>
hostname SW-B1
!
enable secret 5 $1$mERr$9cTjUIEqNGurQiFU.ZeCi1
!
<output omitted>
spanning-tree mode pvst
spanning-tree extend system-id
!
interface FastEthernet0/1
!
<output omitted>
interface GigabitEthernet0/2
!
interface Vlan1
 ip address 192.168.1.252 255.255.255.0
!
ip default-gateway 192.168.1.1
!
!
line con 0
!
line vty 0 4
 password cisco
 login
line vty 5 15
 login
!
end

Branch-2# telnet 192.168.2.17
Trying 192.168.2.17 ...Open


User Access Verification

Password: cisco
SW-B2> enable
Password: class
SW-B2#
SW-B2# show running-config | section Vlan1
interface Vlan1
 ip address 192.168.2.17 255.255.255.224

SW-B2# show running-config | include default-gateway
ip default-gateway 192.168.2.1
SW-B2# show vlan brief

VLAN Name                             Status    Ports
---- -------------------------------- --------- -------------------------------
1    default                          active    Fa0/21, Fa0/22, Fa0/23, Fa0/24
                                                Gig0/2
32   TEAM-1                           active    Fa0/1, Fa0/2, Fa0/3, Fa0/4
                                                Fa0/5, Fa0/6, Fa0/7, Fa0/8
                                                Fa0/9
64   TEAM-2                           active    Fa0/10, Fa0/11, Fa0/12, Fa0/13
                                                Fa0/14, Fa0/15, Fa0/16, Fa0/17
                                                Fa0/18, Fa0/19, Fa0/20

1002 fddi-default                     active
1003 token-ring-default               active
1004 fddinet-default                  active
1005 trnet-default                    active

Factory> telnet 192.168.3.252
Trying 192.168.3.252 ...Open


User Access Verification

Password: cisco
SW-F1> enable
Password: class
SW-F1#
SW-F1# show running-config | section Vlan1|default-gateway|line vty
interface Vlan1
 ip address 192.168.3.252 255.255.255.0
ip default-gateway 192.168.3.1
line vty 0 4
 password cisco
 login
line vty 5 15
 login

Factory> telnet 192.168.4.252
Trying 192.168.4.252 ...Open


User Access Verification

Password: cisco
SW-F2> enable
Password: class
SW-F2#
SW-F2# show running-config | section Vlan1|default-gateway|line vty
interface Vlan1
 ip address 192.168.4.252 255.255.255.0
ip default-gateway 192.168.4.1
line vty 0 4
 password cisco
 login
line vty 5 15
 login

HQ> telnet 192.168.6.252
Trying 192.168.6.252 ...Open


User Access Verification

Password: cisco
SW-HQ1> enable
Password: class
SW-HQ1#
SW-HQ1# show vlan brief

VLAN Name                             Status    Ports
---- -------------------------------- --------- -------------------------------
1    default                          active    Fa0/2, Fa0/3, Fa0/4, Fa0/5
                                                Fa0/6, Fa0/7, Fa0/8, Fa0/9
                                                Fa0/10, Fa0/11, Fa0/12, Fa0/13
                                                Fa0/14, Fa0/15, Fa0/16, Fa0/17
                                                Fa0/18, Fa0/21, Fa0/22, Gig0/2
5    acct                             active
10   admin                            active    Fa0/1
1002 fddi-default                     active
1003 token-ring-default               active
1004 fddinet-default                  active
1005 trnet-default                    active

HQ> telnet 192.168.6.253
Trying 192.168.6.253 ...Open


User Access Verification

Password: cisco
SW-HQ2> enable
Password: class
SW-HQ2#
SW-HQ2# show vlan brief

VLAN Name                             Status    Ports
---- -------------------------------- --------- -------------------------------
1    default                          active    Fa0/2, Fa0/3, Fa0/4, Fa0/5
                                                Fa0/6, Fa0/7, Fa0/8, Fa0/9
                                                Fa0/10, Fa0/11, Fa0/12, Fa0/13
                                                Fa0/14, Fa0/15, Fa0/16, Fa0/17
                                                Fa0/18, Fa0/23, Fa0/24, Gig0/1
                                                Gig0/2
5    acct                             active    Fa0/1
10   admin                            active
99   VLAN0099                         active
1002 fddi-default                     active
1003 token-ring-default               active
1004 fddinet-default                  active
1005 trnet-default                    active

HQ> telnet 192.168.6.254
Trying 192.168.6.254 ...Open


User Access Verification

Password: cisco
SW-HQ3> enable
Password: class
SW-HQ3#
SW-HQ3# show vlan brief

VLAN Name                             Status    Ports
---- -------------------------------- --------- -------------------------------
1    default                          active    Fa0/2, Fa0/3, Fa0/4, Fa0/5
                                                Fa0/6, Fa0/7, Fa0/8, Fa0/9
                                                Fa0/10, Fa0/11, Fa0/12, Fa0/13
                                                Fa0/14, Fa0/15, Fa0/16, Fa0/17
                                                Fa0/18, Fa0/19, Fa0/20, Gig0/1
                                                Gig0/2
5    acct                             active
10   admin                            active    Fa0/1
1002 fddi-default                     active
1003 token-ring-default               active
1004 fddinet-default                  active
1005 trnet-default                    active


What we learned:

  • All seven switches are managed through the default VLAN 1 SVI. Their default gateways are the native VLAN 1 address of the local router (Branch-2 G0/0/0.1 and HQ G0/0/0.1 use subinterfaces).
  • SW-B1, SW-F1, and SW-F2 have line vty 5 15 configured with login but without a password.
  • SW-B2 uses VLAN 32 and VLAN 64, which match the Branch-2 subinterfaces .32 and .64. The HQ switches use VLAN 5 (acct) and VLAN 10 (admin), which match the HQ subinterfaces .5 and .10.
  • The DNS server (192.168.5.252) is in VLAN 10, so it is connected to the VLAN 10 port of SW-HQ1. PC4 (VLAN 5) is connected to SW-HQ2 and PC5 (VLAN 10) is connected to SW-HQ3.
  • VLAN 99 exists only on SW-HQ2. It has no name and no ports.

Switch Management SVI IP Address / Prefix Default Gateway Site
SW-B1 VLAN 1 192.168.1.252/24 192.168.1.1 Branch-1
SW-B2 VLAN 1 192.168.2.17/27 192.168.2.1 Branch-2
SW-F1 VLAN 1 192.168.3.252/24 192.168.3.1 Factory
SW-F2 VLAN 1 192.168.4.252/24 192.168.4.1 Factory
SW-HQ1 VLAN 1 192.168.6.252/24 192.168.6.1 HQ
SW-HQ2 VLAN 1 192.168.6.253/24 192.168.6.1 HQ
SW-HQ3 VLAN 1 192.168.6.254/24 192.168.6.1 HQ
Switch VLAN Access Ports Connected Host / Subnet
SW-B2 VLAN 32 (TEAM-1) Fa0/1 - 9 PC6 (192.168.2.32/27)
SW-B2 VLAN 64 (TEAM-2) Fa0/10 - 20 PC7 (192.168.2.64/27)
SW-HQ1 VLAN 10 (admin) Fa0/1 DNS Server (192.168.5.128/25)
SW-HQ2 VLAN 5 (acct) Fa0/1 PC4 (192.168.5.0/25)
SW-HQ3 VLAN 10 (admin) Fa0/1 PC5 (192.168.5.128/25)
SW-HQ2 VLAN 99 (VLAN0099) none not used
Step 2: View Neighbor Information.

Use discovery protocols to increase your knowledge of the network devices and topologies.

SW-B1# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
Branch-1     Gig 0/1         131            R        ISR4300       Gig 0/0/0
SW-B1# show cdp neighbors detail

Device ID: Branch-1
Entry address(es):
  IP address : 192.168.1.1
Platform: cisco ISR4300, Capabilities: Router
Interface: GigabitEthernet0/1, Port ID (outgoing port): GigabitEthernet0/0/0
Holdtime: 136

Version :
Cisco IOS XE Software, Version 03.13.04.S - Extended Support Release
Cisco IOS Software, ISR Software (X86_64_LINUX_IOSD-UNIVERSALK9-M), Version 15.5(3)S5,
RELEASE SOFTWARE (fc2)
Technical Support: http://www.cisco.com/techsupport
Copyright (c) 1986-2017 by Cisco Systems, Inc.
Compiled Mon 05-Oct-15 11:24 by mcpre

advertisement version: 2
Duplex: full

SW-B2# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
Branch-2     Gig 0/1         155            R        ISR4300       Gig 0/0/0
Branch-2     Gig 0/1         155            R        ISR4300       Gig 0/0/0.1
Branch-2     Gig 0/1         155            R        ISR4300       Gig 0/0/0.32
Branch-2     Gig 0/1         155            R        ISR4300       Gig 0/0/0.64
SW-B2# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Gig0/1      on           802.1q         trunking      1

Port        Vlans allowed on trunk
Gig0/1      1-1005

Port        Vlans allowed and active in management domain
Gig0/1      1,32,64

Port        Vlans in spanning tree forwarding state and not pruned
Gig0/1      1,32,64

SW-F1# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
Factory      Gig 0/1         123            R        ISR4300       Gig 0/0/0

SW-F2# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
Factory      Gig 0/1         163            R        ISR4300       Gig 0/0/1

SW-HQ1# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
HQ           Gig 0/1         128            R        ISR4300       Gig 0/0/0
HQ           Gig 0/1         128            R        ISR4300       Gig 0/0/0.1
HQ           Gig 0/1         128            R        ISR4300       Gig 0/0/0.5
HQ           Gig 0/1         128            R        ISR4300       Gig 0/0/0.10
SW-HQ2       Por 1           120            S        2960          Fas 0/19
SW-HQ2       Por 1           120            S        2960          Fas 0/20
SW-HQ2       Por 1           120            S        2960          Por 1
SW-HQ3       Por 3           120            S        2960          Fas 0/24
SW-HQ3       Por 3           120            S        2960          Fas 0/23
SW-HQ3       Por 3           120            S        2960          Por 3
SW-HQ1# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Po1         on           802.1q         trunking      1
Po3         on           802.1q         trunking      1
Gig0/1      on           802.1q         trunking      1

Port        Vlans allowed on trunk
Po1         1-1005
Po3         1-1005
Gig0/1      1-1005

Port        Vlans allowed and active in management domain
Po1         1,5,10
Po3         1,5,10
Gig0/1      1,5,10

Port        Vlans in spanning tree forwarding state and not pruned
Po1         1,5,10
Po3         1,5,10
Gig0/1      1,5,10
SW-HQ1# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+-----------------------------------------------
1      Po1(SU)         LACP      Fa0/19(P)  Fa0/20(P)
3      Po3(SU)         LACP      Fa0/23(P)  Fa0/24(P)

SW-HQ2# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
SW-HQ3       Por 2           160            S        2960          Fas 0/22
SW-HQ3       Por 2           160            S        2960          Por 2
SW-HQ1       Por 1           160            S        2960          Fas 0/19
SW-HQ1       Por 1           160            S        2960          Fas 0/20
SW-HQ1       Por 1           160            S        2960          Por 1
SW-HQ3       Por 2           160            S        2960          Fas 0/21
SW-HQ2# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Po1         on           802.1q         trunking      1
Po2         on           802.1q         trunking      1

Port        Vlans allowed on trunk
Po1         1-1005
Po2         1-1005

Port        Vlans allowed and active in management domain
Po1         1,5,10,99
Po2         1,5,10,99

Port        Vlans in spanning tree forwarding state and not pruned
Po1         1,5,10,99
Po2         99
SW-HQ2# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+-----------------------------------------------
1      Po1(SU)         LACP      Fa0/19(P)  Fa0/20(P)
2      Po2(SU)         LACP      Fa0/21(P)  Fa0/22(P)
SW-HQ2# show spanning-tree
VLAN0001
  Spanning tree enabled protocol ieee
  Root ID    Priority    32769
             Address     0060.5C77.249C
             Cost        12
             Port        27(Port-channel1)
             Hello Time  2 sec  Max Age 20 sec  Forward Delay 15 sec

  Bridge ID  Priority    32769  (priority 32768 sys-id-ext 1)
             Address     00D0.FF4C.2E30
             Hello Time  2 sec  Max Age 20 sec  Forward Delay 15 sec
             Aging Time  20

Interface        Role Sts Cost      Prio.Nbr Type
---------------- ---- --- --------- -------- --------------------------------
Po1              Root FWD 12        128.27   P2p
Po2              Altn BLK 12        128.28   P2p

VLAN0005
  Spanning tree enabled protocol ieee
  Root ID    Priority    32773
             Address     0060.5C77.249C
             Cost        12
             Port        27(Port-channel1)
             Hello Time  2 sec  Max Age 20 sec  Forward Delay 15 sec

  Bridge ID  Priority    32773  (priority 32768 sys-id-ext 5)
             Address     00D0.FF4C.2E30
             Hello Time  2 sec  Max Age 20 sec  Forward Delay 15 sec
             Aging Time  20

Interface        Role Sts Cost      Prio.Nbr Type
---------------- ---- --- --------- -------- --------------------------------
Fa0/1            Desg FWD 19        128.1    P2p
Po1              Root FWD 12        128.27   P2p
Po2              Altn BLK 12        128.28   P2p

VLAN0010
  Spanning tree enabled protocol ieee
  Root ID    Priority    32778
             Address     0060.5C77.249C
             Cost        12
             Port        27(Port-channel1)
             Hello Time  2 sec  Max Age 20 sec  Forward Delay 15 sec

  Bridge ID  Priority    32778  (priority 32768 sys-id-ext 10)
             Address     00D0.FF4C.2E30
             Hello Time  2 sec  Max Age 20 sec  Forward Delay 15 sec
             Aging Time  20

Interface        Role Sts Cost      Prio.Nbr Type
---------------- ---- --- --------- -------- --------------------------------
Po1              Root FWD 12        128.27   P2p
Po2              Altn BLK 12        128.28   P2p

VLAN0099
  Spanning tree enabled protocol ieee
  Root ID    Priority    32867
             Address     00D0.FF4C.2E30
             This bridge is the root
             Hello Time  2 sec  Max Age 20 sec  Forward Delay 15 sec

  Bridge ID  Priority    32867  (priority 32768 sys-id-ext 99)
             Address     00D0.FF4C.2E30
             Hello Time  2 sec  Max Age 20 sec  Forward Delay 15 sec
             Aging Time  20

Interface        Role Sts Cost      Prio.Nbr Type
---------------- ---- --- --------- -------- --------------------------------
Po1              Desg FWD 12        128.27   P2p
Po2              Desg FWD 12        128.28   P2p

SW-HQ3# show cdp neighbors
Capability Codes: R - Router, T - Trans Bridge, B - Source Route Bridge
                  S - Switch, H - Host, I - IGMP, r - Repeater, P - Phone
Device ID    Local Intrfce   Holdtme    Capability   Platform      Port ID
SW-HQ1       Por 3           179            S        2960          Fas 0/23
SW-HQ1       Por 3           179            S        2960          Fas 0/24
SW-HQ2       Por 2           178            S        2960          Fas 0/22
SW-HQ2       Por 2           178            S        2960          Por 2
SW-HQ1       Por 3           179            S        2960          Por 3
SW-HQ2       Por 2           178            S        2960          Fas 0/21
SW-HQ3# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Po2         auto         n-802.1q       trunking      1
Po3         on           802.1q         trunking      1

Port        Vlans allowed on trunk
Po2         1-1005
Po3         1-1005

Port        Vlans allowed and active in management domain
Po2         1,5,10
Po3         1,5,10

Port        Vlans in spanning tree forwarding state and not pruned
Po2         1,5,10
Po3         1,5,10
SW-HQ3# show etherchannel summary
Flags:  D - down        P - in port-channel
        I - stand-alone s - suspended
        H - Hot-standby (LACP only)
        R - Layer3      S - Layer2
        U - in use      f - failed to allocate aggregator
        u - unsuitable for bundling
        w - waiting to be aggregated
        d - default port


Number of channel-groups in use: 2
Number of aggregators:           2

Group  Port-channel  Protocol    Ports
------+-------------+-----------+-----------------------------------------------
2      Po2(SU)         LACP      Fa0/21(P)  Fa0/22(P)
3      Po3(SU)         LACP      Fa0/23(P)  Fa0/24(P)


What we learned (topology, parts 2 and 3):

  • SW-B1, SW-F1, and SW-F2 each have only one neighbor: their router, on G0/1. They are single access switches.
  • SW-B2 connects to Branch-2 through an 802.1Q trunk on G0/1 (native VLAN 1). Branch-2 appears four times in the CDP table, once for the physical interface and once for each subinterface.
  • The three HQ switches are connected in a triangle with LACP EtherChannels: Po1 between SW-HQ1 and SW-HQ2 (Fa0/19 - 20), Po3 between SW-HQ1 and SW-HQ3 (Fa0/23 - 24), and Po2 between SW-HQ2 and SW-HQ3 (Fa0/21 - 22).
  • SW-HQ1 connects to the HQ router through a trunk on G0/1. All trunks use native VLAN 1. Po2 on SW-HQ3 is in auto mode, so the trunk is formed with DTP negotiation.
  • STP (legacy IEEE 802.1D, PVST) blocks Po2 on SW-HQ2 (Altn BLK) for VLANs 1, 5, and 10 to break the loop in the triangle. The root bridge is reached through Po1 (toward SW-HQ1).

Switch Interface Neighbor Neighbor Interface Link Type
SW-B1 G0/1 Branch-1 G0/0/0 access link
SW-B2 G0/1 Branch-2 G0/0/0 trunk, native VLAN 1
SW-F1 G0/1 Factory G0/0/0 access link
SW-F2 G0/1 Factory G0/0/1 access link
SW-HQ1 G0/1 HQ G0/0/0 trunk, native VLAN 1
SW-HQ1 Po1 (Fa0/19 - 20) SW-HQ2 Po1 (Fa0/19 - 20) LACP EtherChannel trunk
SW-HQ1 Po3 (Fa0/23 - 24) SW-HQ3 Po3 (Fa0/23 - 24) LACP EtherChannel trunk
SW-HQ2 Po2 (Fa0/21 - 22) SW-HQ3 Po2 (Fa0/21 - 22) LACP EtherChannel trunk, blocked by STP on SW-HQ2
Step 3: Connect to Other Devices.

Display configuration information for the other devices on the network. Record your findings in the device table.

By now you should know about all the devices and interface configurations in the network. All rows of the table should contain device information. Use your information to reconstruct as much of the network topology as you can.

What we learned (complete network):

  • WAN: Hub is the center of a hub-and-spoke network. It connects to Branch-1, Branch-2, HQ, and Factory over four serial /30 links (192.168.0.0/24) and to the ISP over G0/0/0 (192.0.2.0/30).
  • Branch-1: Branch-1 G0/0/0 - SW-B1 - PC1 (192.168.1.0/24).
  • Branch-2: router-on-a-stick on Branch-2 G0/0/0 - trunk - SW-B2 - PC6 (VLAN 32, 192.168.2.32/27) and PC7 (VLAN 64, 192.168.2.64/27).
  • Factory: Factory G0/0/0 - SW-F1 - PC2 (192.168.3.0/24) and Factory G0/0/1 - SW-F2 - PC3 (192.168.4.0/24).
  • HQ: router-on-a-stick on HQ G0/0/0 - trunk - SW-HQ1, which forms an EtherChannel triangle with SW-HQ2 and SW-HQ3. PC4 (VLAN 5) is on SW-HQ2, PC5 (VLAN 10) is on SW-HQ3, and the DNS server (VLAN 10) is on SW-HQ1.

Reflection

You may have noticed that some of the practices used to configure the network devices are out-of-date, inefficient, or not secure. Make a list of as many recommendations that you have regarding how the devices should be reconfigured to follow the practices that you have learned in the CCNA curriculum.

The list is a lengthy one. This question provides you with an opportunity to review many of the best practices that have been covered in the CCNA curriculum. Use student discussions to ensure that as many issues have been discussed as possible. Some issues are:

Security and Device Access
  • All devices use the same simple and well-known passwords. These should be changed, should vary between devices, and should be stronger. (see Access Map)
  • SSH is not in use in the network. (see Part 3)
  • On SW-B1, SW-F1, and SW-F2, the line vty 5 15 lines are configured with login but without a password, so Telnet sessions that use these lines cannot log in. All vty lines should be configured consistently, preferably for SSH only. (see Part 5, Step 1 - SW-B1, SW-F1, SW-F2)
  • Management access to all devices is not restricted using ACLs or AAA.
  • Port security is not in use.
  • 802.1x is not implemented.
  • IP Source Guard is not implemented.
  • CDP is on by default and should be turned off or restricted. (see Part 4, Step 2)
Switching and VLANs
Routing

Network Topology Diagram

Students’ drawings will differ in layout; however, the device interconnections should be consistent. The hidden topology is shown below.
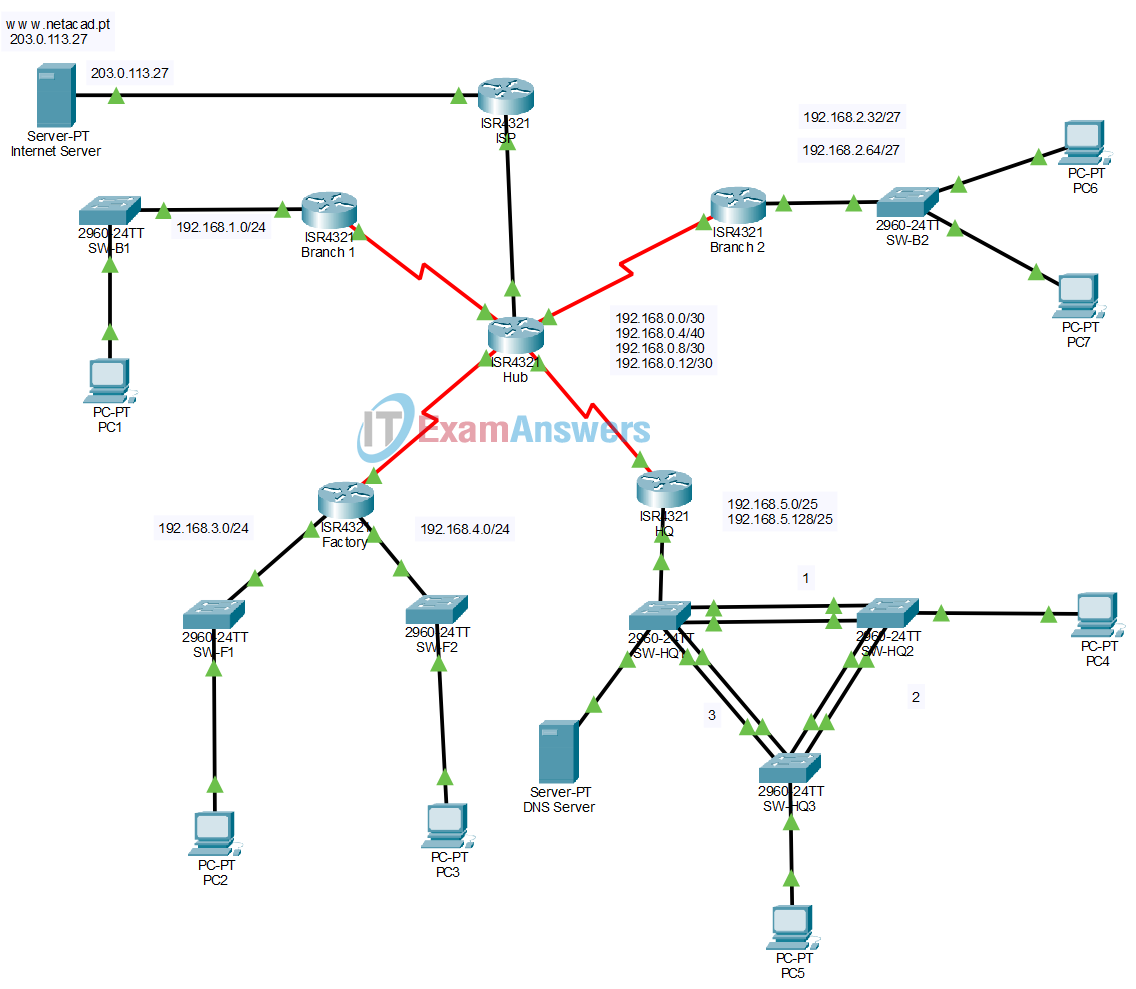
12.6.1 Packet Tracer - Troubleshooting Challenge - Document the Network hidden topology

Annotated Topology (built from the discovered information)
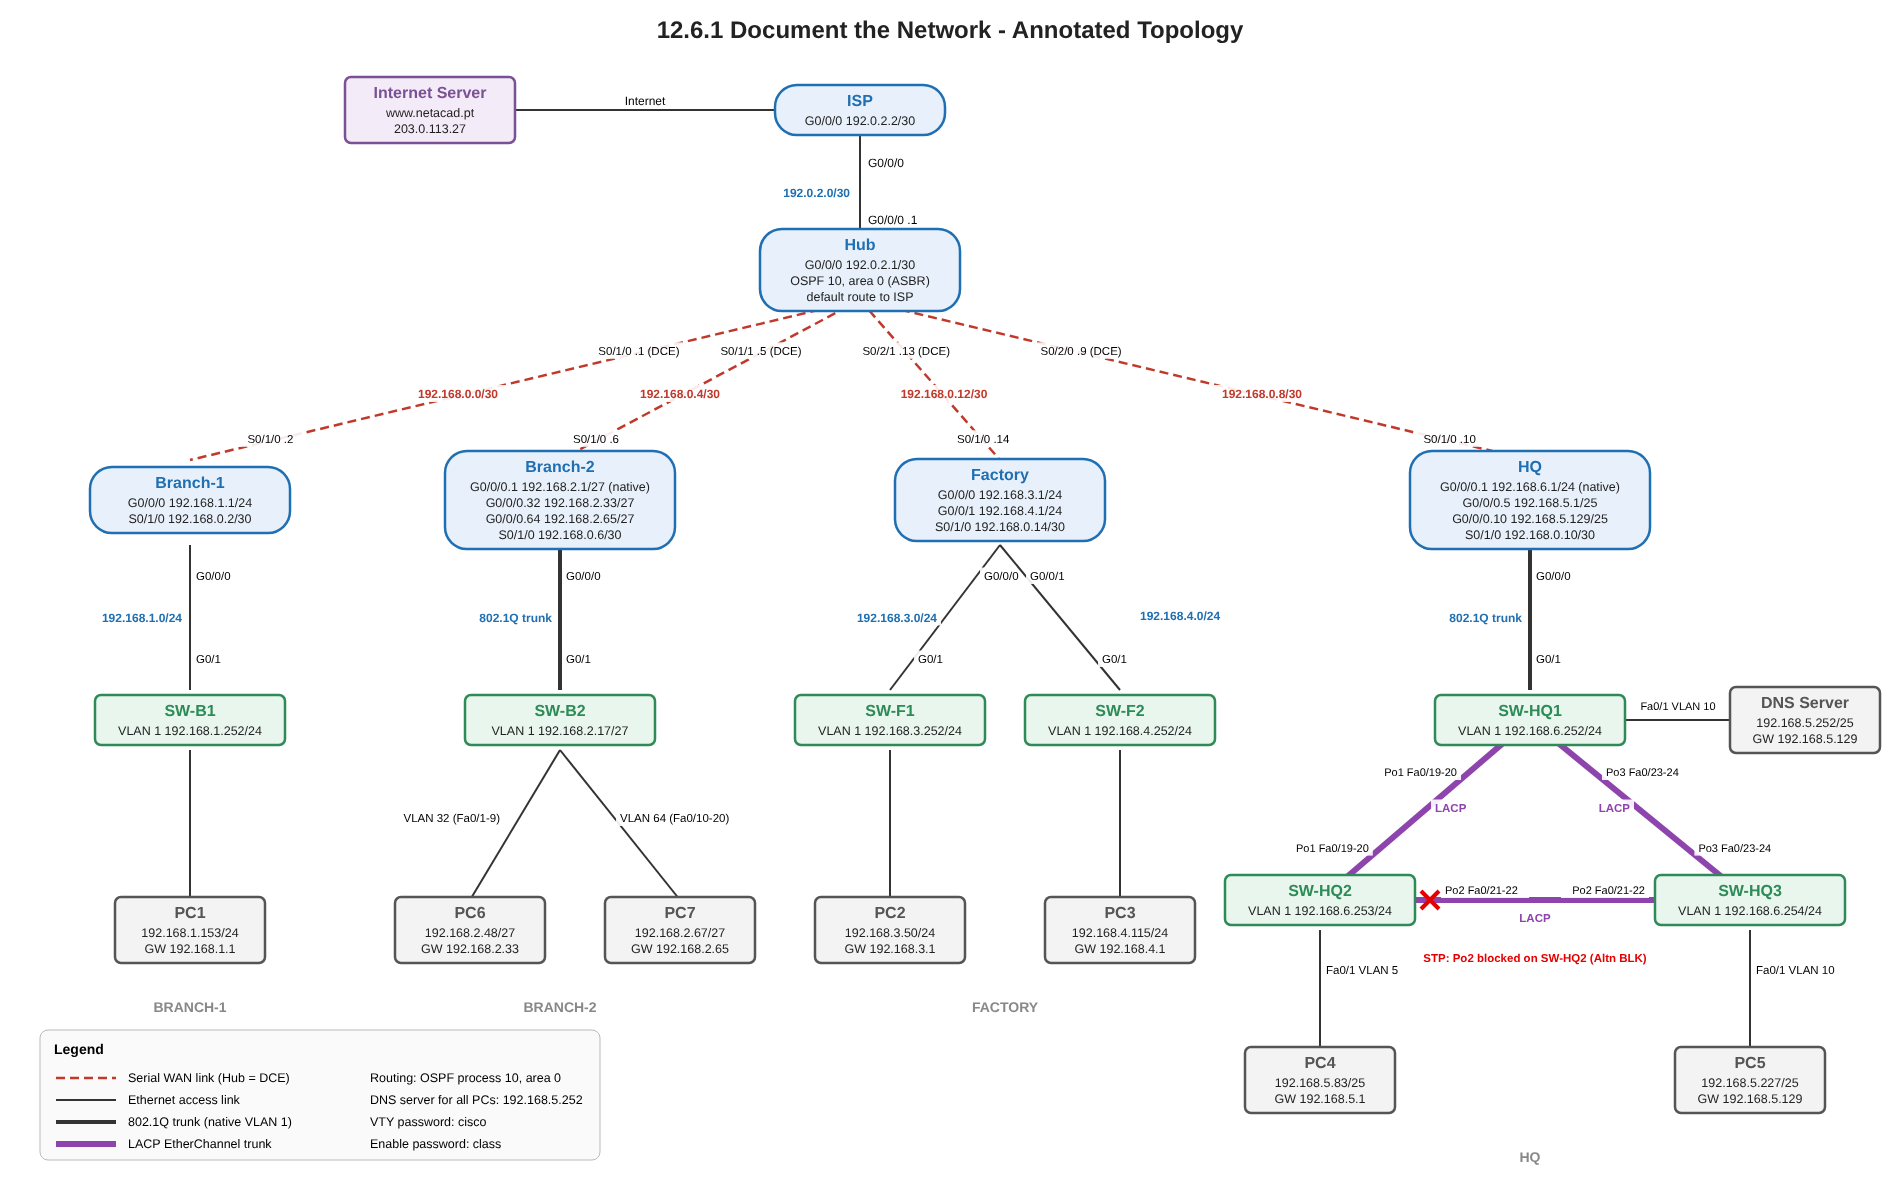
12.6.1 Packet Tracer - Troubleshooting Challenge - Document the Network annotated topology

Device Interconnections

Device Interface Neighbor Neighbor Interface Network / Notes
Hub G0/0/0 ISP G0/0/0 192.0.2.0/30
Hub S0/1/0 (DCE) Branch-1 S0/1/0 192.168.0.0/30
Hub S0/1/1 (DCE) Branch-2 S0/1/0 192.168.0.4/30
Hub S0/2/0 (DCE) HQ S0/1/0 192.168.0.8/30
Hub S0/2/1 (DCE) Factory S0/1/0 192.168.0.12/30
Branch-1 G0/0/0 SW-B1 G0/1 192.168.1.0/24
Branch-2 G0/0/0 (trunk) SW-B2 G0/1 VLAN 1, 32, 64
Factory G0/0/0 SW-F1 G0/1 192.168.3.0/24
Factory G0/0/1 SW-F2 G0/1 192.168.4.0/24
HQ G0/0/0 (trunk) SW-HQ1 G0/1 VLAN 1, 5, 10
SW-HQ1 Po1 (Fa0/19 - 20) SW-HQ2 Po1 (Fa0/19 - 20) LACP EtherChannel
SW-HQ1 Po3 (Fa0/23 - 24) SW-HQ3 Po3 (Fa0/23 - 24) LACP EtherChannel
SW-HQ2 Po2 (Fa0/21 - 22) SW-HQ3 Po2 (Fa0/21 - 22) LACP EtherChannel (STP blocked on SW-HQ2)
SW-HQ1 Fa0/1 DNS Server NIC VLAN 10, 192.168.5.252
SW-HQ2 Fa0/1 PC4 NIC VLAN 5
SW-HQ3 Fa0/1 PC5 NIC VLAN 10

Other items missing in the Topology documentation include the following:

  • VLANs and port memberships
  • DTE / DCE devices
  • DNS Server addresses
  • OSPFv2 Area
  • Physical interfaces and associated IP addresses
  • Physical switchports and associated VLAN / trunking
  • Each Switch Management VLAN and IP address
  • STP is being blocked on SW-HQ2 going to SW-HQ3
  • EtherChannel is using LACP (802.3ad)

Next step: Use the documentation that you created in this activity to find and fix the network problems in Part II: 12.6.2 Packet Tracer - Troubleshooting Challenge - Use Documentation to Solve Issues.

Download Packet Tracer (.pka) file:


Subscribe
Notify of
guest

5 Corrections & Clarifications