
2.7.2 Packet Tracer - Configure Single-Area OSPFv2 - Physical Mode Answers
Topology
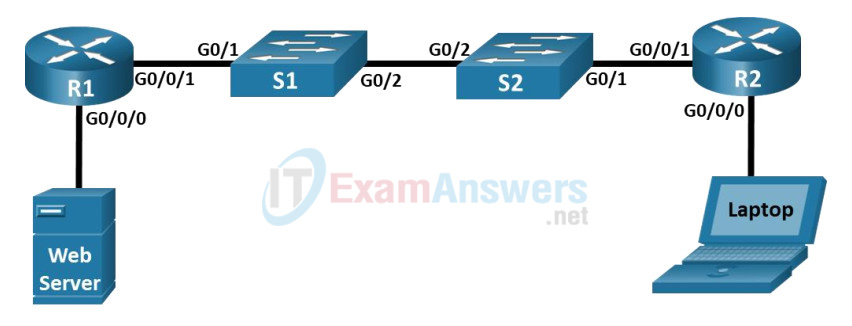
Addressing Table
| Device | Interface | IP Address | Subnet Mask | Default Gateway |
|---|---|---|---|---|
| R1 | G0/0/1 | 10.53.0.1 | 255.255.255.0 | n/a |
| G0/0/0 | 172.16.1.1 | 255.255.255.0 | n/a | |
| R2 | G0/0/1 | 10.53.0.2 | 255.255.255.0 | n/a |
| G0/0/0 | 192.168.1.1 | 255.255.255.0 | n/a | |
| Web Server | F0 | 172.16.1.10 | 255.255.255.0 | 172.16.1.1 |
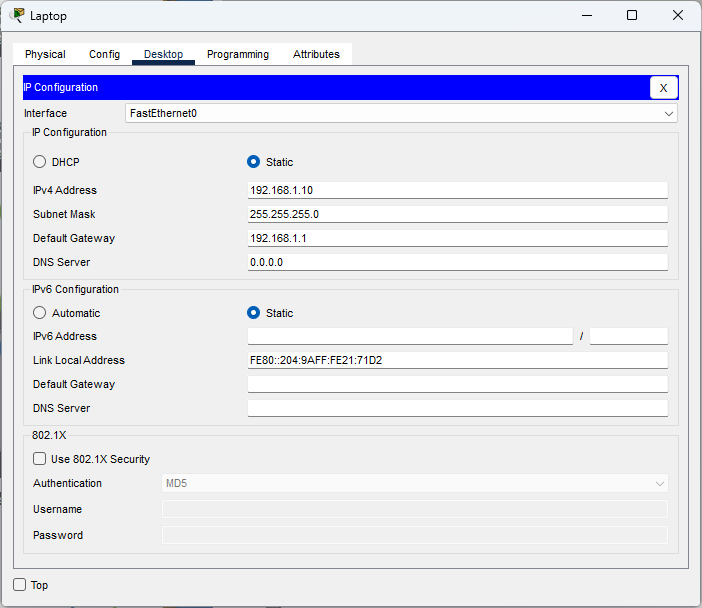
| Laptop | F0 | 192.168.1.10 | 255.255.255.0 | 192.168.1.1 |
Objectives
- Part 1: Build the Network and Configure Basic Device Settings
- Part 2: Configure and Verify Single-Area OSPFv2 for Basic Operation
- Part 3: Optimize and Verify the Single-Area OSPFv2 Configuration
Background / Scenario
You have been tasked with configuring a small company’s network using OSPFv2. R1 will share the default route information to R2. After the initial configuration, the organization has asked for the configuration to be optimized to reduce protocol traffic and ensure that R1 remains in control of routing.
Note: The equipment required for this activity is located in the wiring closet on the utility shelf.
Instructions
Part 1: Build the Network and Configure Basic Device Settings
Step 1: Cable the network as shown in the topology.
Place the required devices on the rack and the table. Power on the PCs and cable the devices according to the topology. To select the correct port on a switch, right-click and select Inspect Front. Use the Zoom tool, if necessary. Float your mouse over the ports to see the port numbers. Packet Tracer will score the correct cable and port connections.
a. There are several switches, routers, and other devices on the Shelf. Click and drag the routers R1 and R2 and the switches S1 and S2 to the Rack. Click and drag the Web Server to the Rack. Click and drag the Laptop to the Table.
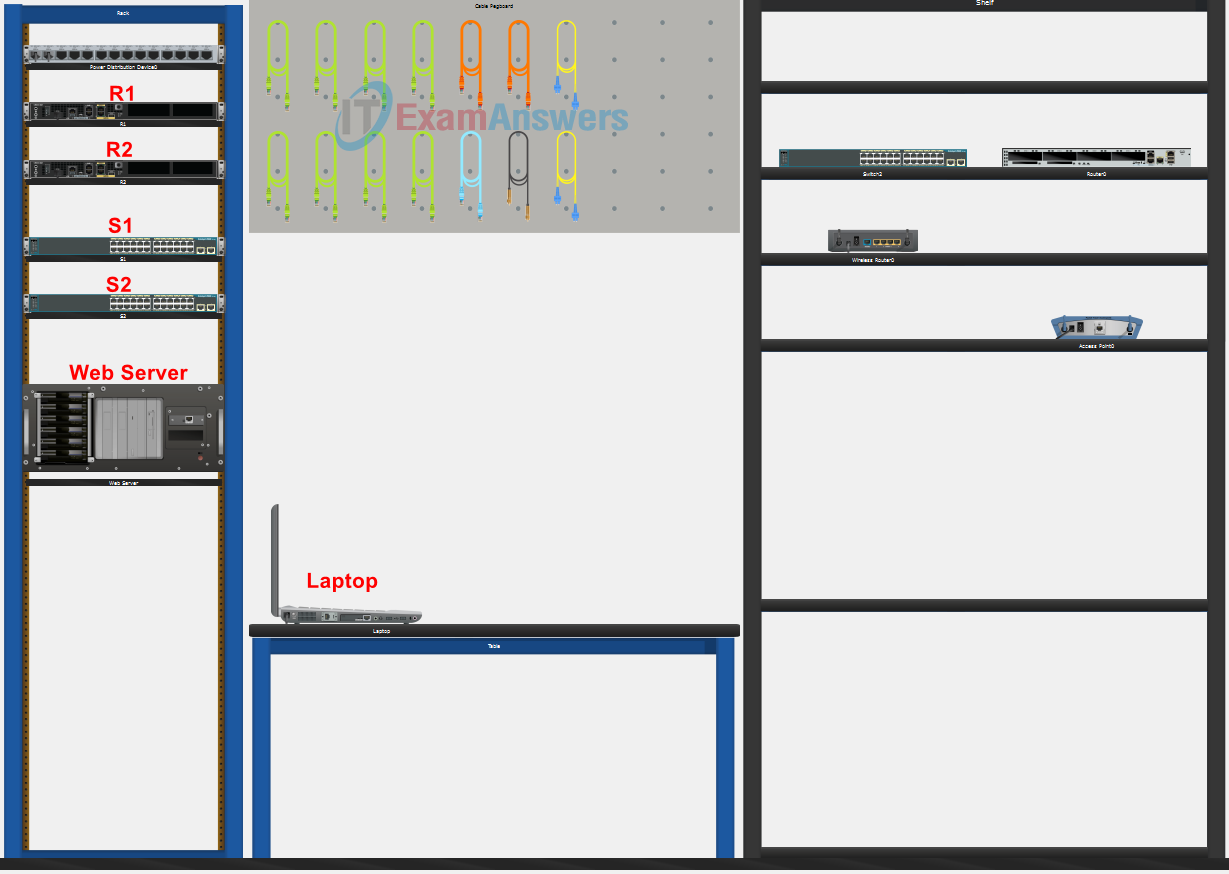
b. Power on the routers and the laptop.
c. On the Cable Pegboard, click a Copper Straight-Through cable. Click the GigabitEthernet0/1 port on S1 and then click the GigabitEthernet0/0/1 port on R1 to connect them.
d. On the Cable Pegboard, click a Copper Straight-Through cable. Click the GigabitEthernet0/1 port on S2 and then click the GigabitEthernet0/0/1 port on R2 to connect them.
e. On the Cable Pegboard, click a Copper Cross-Over cable. Click the GigabitEthernet0/2 port on S1 and then click the GigabitEthernet0/2 port on S2 to connect them. You should see the cable connecting the two ports.
f. On the Cable Pegboard, click a Copper Straight-Through cable. Click the GigabitEthernet0/0/0 port on R1 and then click the FastEthernet0 port on the Web Server to connect them.
g. On the Cable Pegboard, click a Copper Straight-Through cable. Click the GigabitEthernet0/0/0 port on R2 and then click the FastEthernet0 port on the Laptop to connect them.
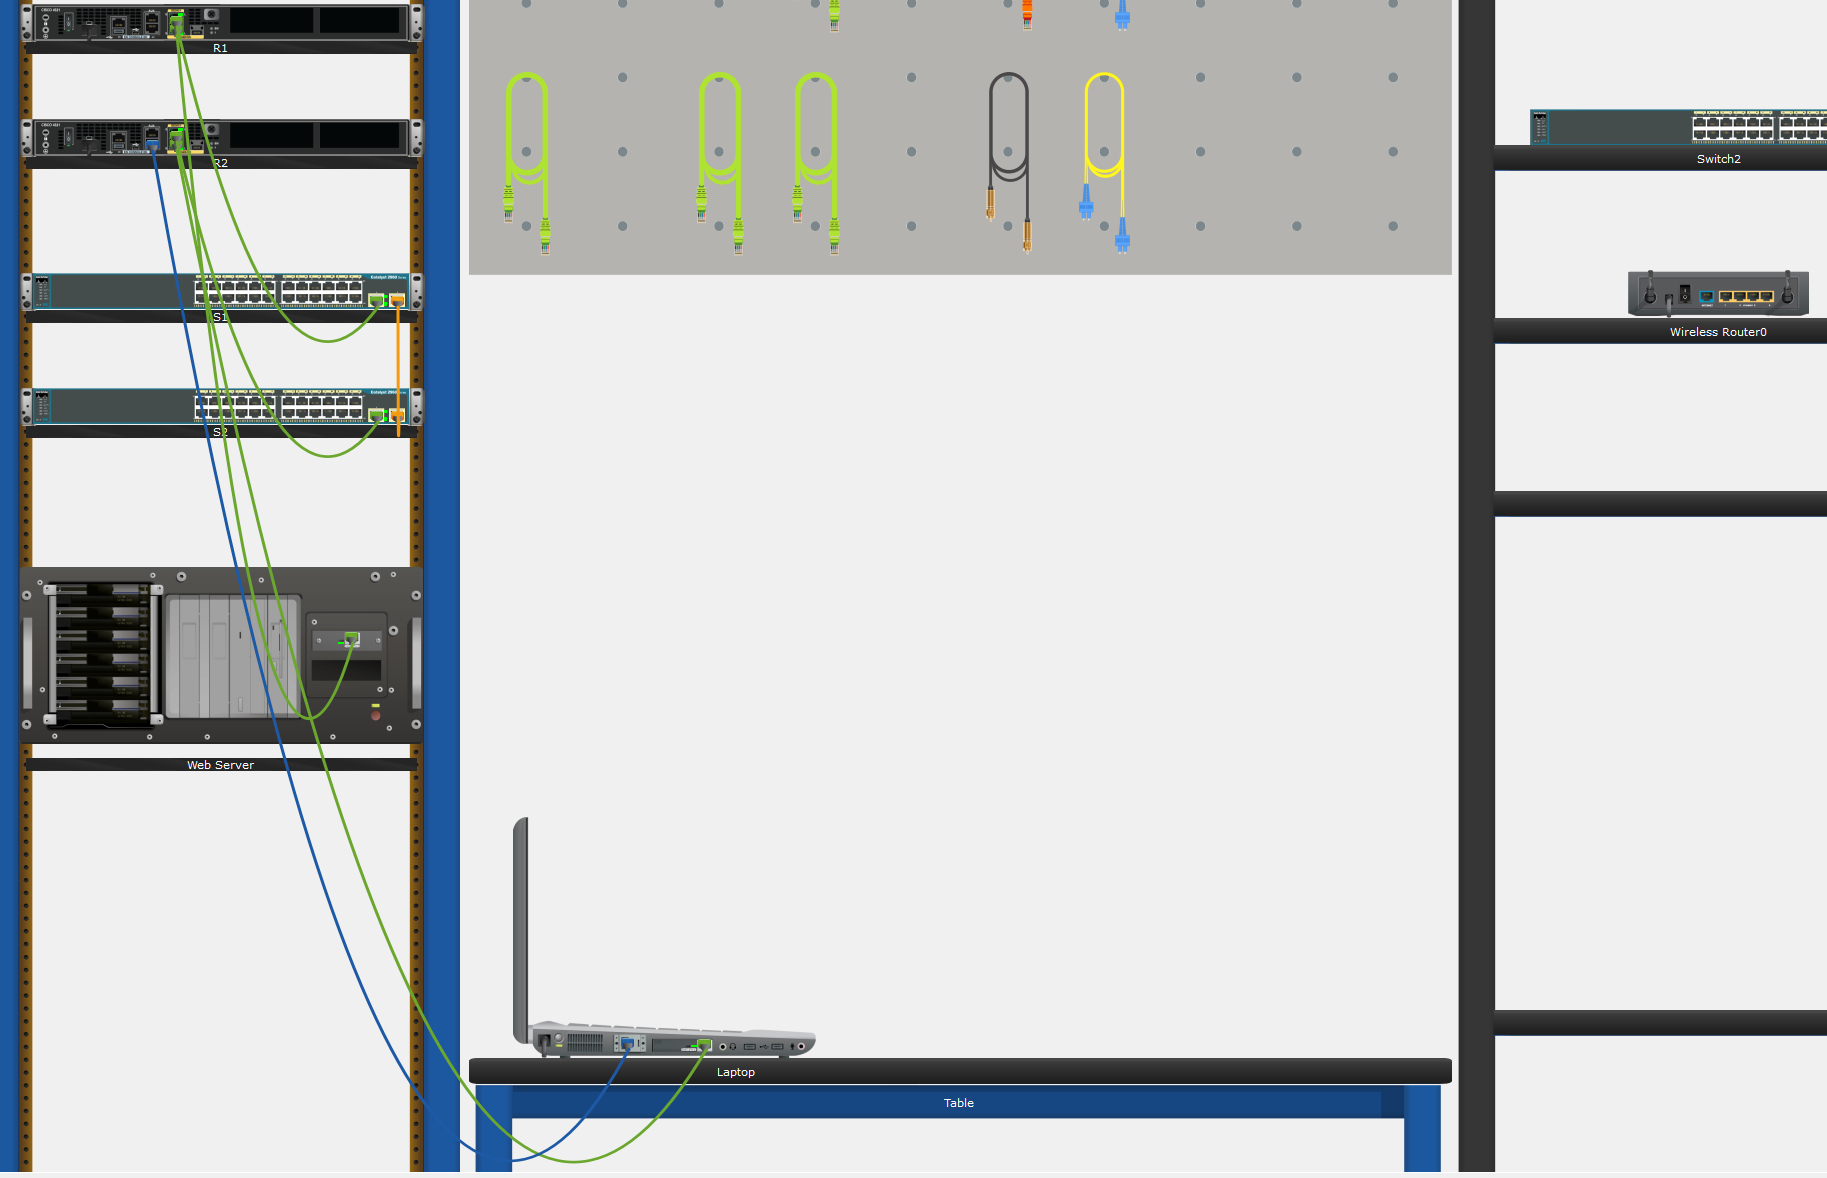
Visually inspect network connections. Initially, when you connect devices to a switch port, the link lights will be amber. After a minute or so, the link lights will turn green.
Step 2: Configure basic settings for the two routers and two switches.
a. On the Cable Pegboard, click a Console cable.
b. Connect the console cable between the device and the Laptop. For the switches, Inspect Rear to locate the Console port.
c. Assign a name to the device according to the Topology.
Router(config)# hostname R1
d. Disable DNS lookup to prevent the router from attempting to translate incorrectly entered commands as though they were host names.
R1(config)# no ip domain-lookup
e. Assign class as the privileged EXEC encrypted password.
R1(config)# enable secret class
f. Assign cisco as the console password and enable login.
R1(config)# line console 0
R1(config-line)# password cisco
R1(config-line)# login
g. Assign cisco as the vty password and enable login.
R1(config)# line vty 0 4
R1(config-line)# password cisco
R1(config-line)# login
h. Encrypt the plaintext passwords.
R1(config)# service password-encryption
i. Create a banner that warns anyone accessing the device that unauthorized access is prohibited.
R1(config)# banner motd $ Authorized Users Only! $
j. Save the running configuration to the startup configuration file.
R1# copy running-config startup-config
k. Click one end of the Console cable and drag it back to the Cable Pegboard.
l. Repeat Step 2 for each device until R2, S1, and S2 are also each configured with basic settings.
Router(config)# hostname R2

R2(config)# no ip domain-lookup

R2(config)# enable secret class

R2(config)# line console 0
R2(config-line)# password cisco
R2(config-line)# login
R2(config-line)# exit

R2(config)# line vty 0 4
R2(config-line)# password cisco
R2(config-line)# login
R2(config-line)# exit

R2(config)# service password-encryption

R2(config)# banner motd $ Authorized Users Only! $
Switch(config)# hostname S1

S1(config)# no ip domain-lookup

S1(config)# enable secret class

S1(config)# line console 0
S1(config-line)# password cisco
S1(config-line)# login
S1(config-line)# exit

S1(config)# line vty 0 15
S1(config-line)# password cisco
S1(config-line)# login
S1(config-line)# exit

S1(config)# service password-encryption

S1(config)# banner motd $ Authorized Users Only! $
Switch(config)# hostname S2

S2(config)# no ip domain-lookup

S2(config)# enable secret class

S2(config)# line console 0
S2(config-line)# password cisco
S2(config-line)# login
S2(config-line)# exit

S2(config)# line vty 0 15
S2(config-line)# password cisco
S2(config-line)# login
S2(config-line)# exit

S2(config)# service password-encryption

S2(config)# banner motd $ Authorized Users Only! $
Step 3: Configure settings for the server and the laptop.
Configure static IP address information on the Web Server and Laptop according to the Addressing Table.
a. Click Web Server > Desktop > IP Configuration. Enter the IPv4 address, subnet mask, and default gateway information for the Web Server according to the Addressing Table.
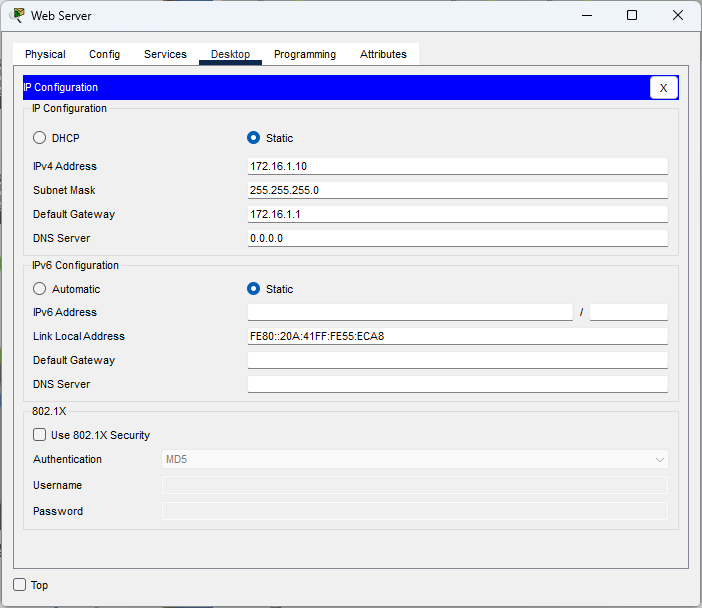
b. Close or minimize the Web Server window.
c. Repeat the previous steps to assign the IPv4 address information for the Laptop, as listed in the Addressing Table.
Part 2: Configure and Verify Single-Area OSPFv2 for Basic Operation
Step 1: Configure interface addresses and basic OSPFv2 on each router.
a. Connect a Console cable between R1 and the Laptop.
b. Configure interface addresses on each router as shown in the Addressing Table.
R1(config)# interface gigabitethernet 0/0/1
R1(config-if)# ip address 10.53.0.1 255.255.255.0
R1(config-if)# no shutdown
R1(config-if)# interface gigabitethernet 0/0/0
R1(config-if)# ip address 172.16.1.1 255.255.255.0
R1(config-if)# no shutdown
R2(config)# interface gigabitethernet 0/0/1
R2(config-if)# ip address 10.53.0.2 255.255.255.0
R2(config-if)# no shutdown
R2(config-if)# interface gigabitethernet 0/0/0
R2(config-if)# ip address 192.168.1.1 255.255.255.0
R2(config-if)# no shutdown
c. Enter OSPF router configuration mode using process ID 56.
R1(config)# router ospf 56
R2(config)# router ospf 56
d. Configure a static router ID for each router (1.1.1.1 for R1, 2.2.2.2 for R2).
R1(config-router)# router-id 1.1.1.1
R2(config-router)# router-id 2.2.2.2
e. Configure a network statement for the network between R1 and R2, placing it in area 0.
R1(config-router)# network 10.53.0.0 0.0.0.255 area 0
R2(config-router)# network 10.53.0.0 0.0.0.255 area 0
f. Configure a network statement for the other networks connected to R1 and R2 and place them in area 0. Note that the network command for the LAN connected to R1 will not be graded as this network is removed later in the activity.
R1(config-router)# network 172.16.1.0 0.0.0.255 area 0
R2(config-router)# network 192.168.1.0 0.0.0.255 area 0
g. Switch the console cable to R2 and repeat substeps b through f for R2. After configuring R1 and R2, you can simply use Telnet between them, if you wish, instead of moving the console cable each time.
h. Verify that OSPFv2 is operational between the routers. Issue the command to verify that R1 and R2 have formed an adjacency.
R1# show ip ospf neighbor

Neighbor ID     Pri   State           Dead Time   Address         Interface
2.2.2.2 1 FULL/DR 00:00:33 10.53.0.2 GigabitEthernet0/0/1R2# show ip ospf neighbor
Neighbor ID Pri State Dead Time Address Interface
1.1.1.1 1 FULL/BDR 00:00:37 10.53.0.1 GigabitEthernet0/0/1Which router is identified as the DR? Which is the BDR? What was the selection criteria?
Answers will vary. In this example, R2 is the DR and R1 is the BDR. Both G0/0/1 interfaces have the default priority of 1, so the router with the highest router ID (R2, 2.2.2.2) became the DR. If one router starts OSPF well before the other, it becomes the DR first and keeps the role, because the election is not preemptive.
i. On R1, issue the show ip route ospf command to verify that the R2 G0/0/0 network is present in the routing table.
R1# show ip route ospf
O    192.168.1.0 [110/2] via 10.53.0.2, 00:04:14, GigabitEthernet0/0/1
j. Click Laptop > Command Prompt, and then ping the Web Server at 172.16.1.10. After one or two timeouts, the ping should be successful. If not, troubleshoot your physical connections and configurations.
C:\> ping 172.16.1.10

Pinging 172.16.1.10 with 32 bytes of data:

Request timed out.
Reply from 172.16.1.10: bytes=32 time<1ms TTL=126
Reply from 172.16.1.10: bytes=32 time<1ms TTL=126
Reply from 172.16.1.10: bytes=32 time<1ms TTL=126

Ping statistics for 172.16.1.10:
    Packets: Sent = 4, Received = 3, Lost = 1 (25% loss),
Approximate round trip times in milli-seconds:
    Minimum = 0ms, Maximum = 0ms, Average = 0ms
Part 3: Optimize and Verify the Single-Area OSPFv2 Configuration
Step 1: Implement various optimizations on each router.
a. On R1, configure the interface G0/0/1 OSPF priority to 50 to ensure that R1 is the Designated Router.
R1(config)# interface gigabitethernet 0/0/1
R1(config-if)# ip ospf priority 50
b. Configure the OSPF timers on interface G0/0/1 of each router for a hello timer of 30 seconds and a dead timer of 120 seconds.
R1(config)# interface gigabitethernet 0/0/1
R1(config-if)# ip ospf hello-interval 30
R1(config-if)# ip ospf dead-interval 120
R2(config)# interface gigabitethernet 0/0/1
R2(config-if)# ip ospf hello-interval 30
R2(config-if)# ip ospf dead-interval 120
c. On R1, remove the OSPF network command for 172.16.1.0, and then configure a default static route that uses interface G0/0/0 as the exit interface. Finally, propagate the default route into OSPF. Note the console message after setting the default route.
R1(config)# router ospf 56
R1(config-router)# no network 172.16.1.0 0.0.0.255 area 0
R1(config)# ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/0
%Default route without gateway, if not a point-to-point interface, may impact performance
R1(config)# router ospf 56
R1(config-router)# default-information originate
d. Change the reference bandwidth on each router to 1Gbs. After this configuration, restart OSPF using the clear ip ospf process command. Note the console message after setting the new reference bandwidth.
R1(config)# router ospf 56
R1(config-router)# auto-cost reference-bandwidth 1000
%OSPF: Reference bandwidth is changed.
Please ensure reference bandwidth is consistent across all routers.
R1# clear ip ospf process
Reset ALL OSPF processes? [no]: yes
R2(config)# router ospf 56
R2(config-router)# auto-cost reference-bandwidth 1000
%OSPF: Reference bandwidth is changed.
Please ensure reference bandwidth is consistent across all routers.
R2# clear ip ospf process
Reset ALL OSPF processes? [no]: yes
Step 2: Verify OSPFv2 optimizations are in place.
a. Issue the show ip ospf interface g0/0/1 command on R1 and verify that the interface priority has been set to 50 and that the time intervals are Hello 30, Dead 120, and the default Network Type is Broadcast.
R1# show ip ospf interface gigabitethernet 0/0/1

GigabitEthernet0/0/1 is up, line protocol is up
  Internet address is 10.53.0.1/24, Area 0
  Process ID 56, Router ID 1.1.1.1, Network Type BROADCAST, Cost: 1
  Transmit Delay is 1 sec, State DR, Priority 50
  Designated Router (ID) 1.1.1.1, Interface address 10.53.0.1
  Backup Designated Router (ID) 2.2.2.2, Interface address 10.53.0.2
  Timer intervals configured, Hello 30, Dead 120, Wait 120, Retransmit 5
    Hello due in 00:00:19
  Index 1/1, flood queue length 0
  Next 0x0(0)/0x0(0)
  Last flood scan length is 1, maximum is 1
  Last flood scan time is 0 msec, maximum is 0 msec
  Neighbor Count is 1, Adjacent neighbor count is 1
    Adjacent with neighbor 2.2.2.2  (Backup Designated Router)
  Suppress hello for 0 neighbor(s)
b. On R1, issue the show ip route ospf command to verify that the R2 G0/0/0 network is present in the routing table. Note the difference in the metric between this output and the previous output.
R1# show ip route ospf
O    192.168.1.0 [110/11] via 10.53.0.2, 00:04:50, GigabitEthernet0/0/1
c. On R2, issue the show ip route ospf command. The only OSPF route information should be the default route that R1 is propagating.
R2# show ip route ospf
O*E2 0.0.0.0/0 [110/1] via 10.53.0.1, 00:01:58, GigabitEthernet0/0/1
d. From the Laptop, ping the Web Server again. The ping should be successful.
C:\> ping 172.16.1.10

Pinging 172.16.1.10 with 32 bytes of data:

Reply from 172.16.1.10: bytes=32 time<1ms TTL=126
Reply from 172.16.1.10: bytes=32 time<1ms TTL=126
Reply from 172.16.1.10: bytes=32 time<1ms TTL=126
Reply from 172.16.1.10: bytes=32 time<1ms TTL=126

Ping statistics for 172.16.1.10:
    Packets: Sent = 4, Received = 4, Lost = 0 (0% loss),
Approximate round trip times in milli-seconds:
    Minimum = 0ms, Maximum = 0ms, Average = 0ms
e. Compare the following two routes:
From R1:
R1# show ip route ospf
O    192.168.1.0 [110/11] via 10.53.0.2, 00:16:05, GigabitEthernet0/0/1
From R2:
R2# show ip route ospf
O*E2 0.0.0.0/0 [110/1] via 10.53.0.1, 00:14:28, GigabitEthernet0/0/1
Why is the OSPF cost for the default route different than the OSPF cost at R1 for the 192.168.1.0/24 network?
A default static route imported into OSPF is given the metric type of “E2” or External Type 2 by default. An “E2” by default, keeps the same OSPF cost across the entire OSPF network. In this case, the metric for the default route was 1, so it has a metric of 1 everywhere within the OSPF 56 network. The 192.168.1.0 /24 network is an internal OSPF route with a metric that is cumulative.
Device Configs - Final
ROUTER R1
! ==============================================================
!--- 2.7.2 Packet Tracer - Configure Single-Area OSPFv2 - Physical Mode
!--- ANSWER SCRIPT FOR ROUTER R1
!--- Usage: cable and power on the device, connect the console cable from the Laptop, and paste this whole file at the Router> prompt (answer no if the router asks to enter the initial configuration dialog). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1, Step 2: Configure basic settings.
! --------------------------------------------------------------

!--- c. Assign a name to the device.
hostname R1

!--- d. Disable DNS lookup.
no ip domain-lookup

!--- e. Privileged EXEC encrypted password: class.
enable secret class

!--- f. Console password cisco and enable login.
line console 0
 password cisco
 login
 exit

!--- g. VTY password cisco and enable login.
line vty 0 4
 password cisco
 login
 exit

!--- h. Encrypt the plaintext passwords.
service password-encryption

!--- i. Banner that warns unauthorized access is prohibited.
banner motd $ Authorized Users Only! $

! --------------------------------------------------------------
!--- Part 2, Step 1: Configure interface addresses and basic OSPFv2.
! --------------------------------------------------------------

!--- b. G0/0/1: 10.53.0.1/24.
interface gigabitethernet 0/0/1
 ip address 10.53.0.1 255.255.255.0
 no shutdown
 exit

!--- b. G0/0/0: 172.16.1.1/24.
interface gigabitethernet 0/0/0
 ip address 172.16.1.1 255.255.255.0
 no shutdown
 exit

!--- c-d. OSPF process 56 with router ID 1.1.1.1.
router ospf 56
 router-id 1.1.1.1
 exit

!--- e. Network between R1 and R2 in area 0.
router ospf 56
 network 10.53.0.0 0.0.0.255 area 0
 exit

! --------------------------------------------------------------
!--- Part 3, Step 1: Implement various optimizations on each router.
! --------------------------------------------------------------

!--- a. OSPF priority 50 on G0/0/1 so R1 is the Designated Router.
interface gigabitethernet 0/0/1
 ip ospf priority 50
 exit

!--- b. Hello 30 seconds and dead 120 seconds on G0/0/1.
interface gigabitethernet 0/0/1
 ip ospf hello-interval 30
 ip ospf dead-interval 120
 exit

!--- c. Default static route with G0/0/0 as the exit interface.
ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/0/0

!--- c. Propagate the default route into OSPF.
router ospf 56
 default-information originate
 exit

!--- d. Reference bandwidth 1 Gb/s (1000 Mbps).
router ospf 56
 auto-cost reference-bandwidth 1000
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip ospf interface gigabitethernet 0/0/1  -> State DR, Priority 50, Hello 30, Dead 120, Network Type BROADCAST
!---   show ip route ospf                            -> O 192.168.1.0/24 [110/11] via 10.53.0.2
!--- Note: the network 172.16.1.0 statement of Part 2 Step 1f is not graded and is removed again in
!--- Part 3 Step 1c, so this final script leaves it out. Step 1d (clear ip ospf process) is interactive;
!--- run it by hand after both scripts: R1# clear ip ospf process, then answer yes at
!--- "Reset ALL OSPF processes? [no]:". Paste R1 before R2 so R1 becomes the DR.
! ==============================================================
ROUTER R2
! ==============================================================
!--- 2.7.2 Packet Tracer - Configure Single-Area OSPFv2 - Physical Mode
!--- ANSWER SCRIPT FOR ROUTER R2
!--- Usage: cable and power on the device, connect the console cable from the Laptop, and paste this whole file at the Router> prompt (answer no if the router asks to enter the initial configuration dialog). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1, Step 2: Configure basic settings.
! --------------------------------------------------------------

!--- c. Assign a name to the device.
hostname R2

!--- d. Disable DNS lookup.
no ip domain-lookup

!--- e. Privileged EXEC encrypted password: class.
enable secret class

!--- f. Console password cisco and enable login.
line console 0
 password cisco
 login
 exit

!--- g. VTY password cisco and enable login.
line vty 0 4
 password cisco
 login
 exit

!--- h. Encrypt the plaintext passwords.
service password-encryption

!--- i. Banner that warns unauthorized access is prohibited.
banner motd $ Authorized Users Only! $

! --------------------------------------------------------------
!--- Part 2, Step 1: Configure interface addresses and basic OSPFv2.
! --------------------------------------------------------------

!--- b. G0/0/1: 10.53.0.2/24.
interface gigabitethernet 0/0/1
 ip address 10.53.0.2 255.255.255.0
 no shutdown
 exit

!--- b. G0/0/0: 192.168.1.1/24.
interface gigabitethernet 0/0/0
 ip address 192.168.1.1 255.255.255.0
 no shutdown
 exit

!--- c-d. OSPF process 56 with router ID 2.2.2.2.
router ospf 56
 router-id 2.2.2.2
 exit

!--- e. Network between R1 and R2 in area 0.
router ospf 56
 network 10.53.0.0 0.0.0.255 area 0
 exit

!--- f. R2 LAN 192.168.1.0/24 in area 0.
router ospf 56
 network 192.168.1.0 0.0.0.255 area 0
 exit

! --------------------------------------------------------------
!--- Part 3, Step 1: Implement various optimizations on each router.
! --------------------------------------------------------------

!--- b. Hello 30 seconds and dead 120 seconds on G0/0/1.
interface gigabitethernet 0/0/1
 ip ospf hello-interval 30
 ip ospf dead-interval 120
 exit

!--- d. Reference bandwidth 1 Gb/s (1000 Mbps).
router ospf 56
 auto-cost reference-bandwidth 1000
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip ospf neighbor  -> 1.1.1.1 FULL/DR on GigabitEthernet0/0/1
!---   show ip route ospf     -> O*E2 0.0.0.0/0 [110/1] via 10.53.0.1
!--- Note: Step 1d also asks for clear ip ospf process; run it by hand and answer yes.
! ==============================================================
SWITCH S1
! ==============================================================
!--- 2.7.2 Packet Tracer - Configure Single-Area OSPFv2 - Physical Mode
!--- ANSWER SCRIPT FOR SWITCH S1
!--- Usage: cable and power on the device, connect the console cable from the Laptop, and paste this whole file at the Switch> prompt. Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1, Step 2: Configure basic settings.
! --------------------------------------------------------------

!--- c. Assign a name to the device.
hostname S1

!--- d. Disable DNS lookup.
no ip domain-lookup

!--- e. Privileged EXEC encrypted password: class.
enable secret class

!--- f. Console password cisco and enable login.
line console 0
 password cisco
 login
 exit

!--- g. VTY password cisco and enable login.
line vty 0 15
 password cisco
 login
 exit

!--- h. Encrypt the plaintext passwords.
service password-encryption

!--- i. Banner that warns unauthorized access is prohibited.
banner motd $ Authorized Users Only! $

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show running-config  -> hostname, banner, console and vty login, encrypted passwords
! ==============================================================
SWITCH S2
! ==============================================================
!--- 2.7.2 Packet Tracer - Configure Single-Area OSPFv2 - Physical Mode
!--- ANSWER SCRIPT FOR SWITCH S2
!--- Usage: cable and power on the device, connect the console cable from the Laptop, and paste this whole file at the Switch> prompt. Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1, Step 2: Configure basic settings.
! --------------------------------------------------------------

!--- c. Assign a name to the device.
hostname S2

!--- d. Disable DNS lookup.
no ip domain-lookup

!--- e. Privileged EXEC encrypted password: class.
enable secret class

!--- f. Console password cisco and enable login.
line console 0
 password cisco
 login
 exit

!--- g. VTY password cisco and enable login.
line vty 0 15
 password cisco
 login
 exit

!--- h. Encrypt the plaintext passwords.
service password-encryption

!--- i. Banner that warns unauthorized access is prohibited.
banner motd $ Authorized Users Only! $

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show running-config  -> hostname, banner, console and vty login, encrypted passwords
! ==============================================================


