11.1.10 Packet Tracer - Implement Port Security Answers
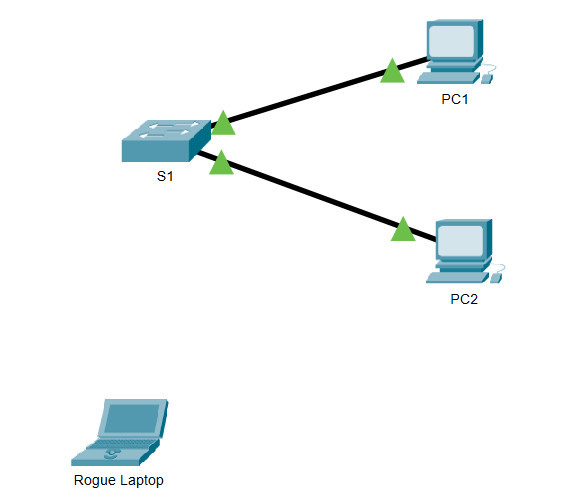
Topology
11.1.10 Packet Tracer – Implement Port Security
Addressing Table
| Device | Interface | IP Address | Subnet Mask |
|---|---|---|---|
| S1 | VLAN 1 | 10.10.10.2 | 255.255.255.0 |
| PC1 | NIC | 10.10.10.10 | 255.255.255.0 |
| PC2 | NIC | 10.10.10.11 | 255.255.255.0 |
| Rogue Laptop | NIC | 10.10.10.12 | 255.255.255.0 |
Objective
- Part 1: Configure Port Security
- Part 2: Verify Port Security
Background
In this activity, you will configure and verify port security on a switch. Port security allows you to restrict a port’s ingress traffic by limiting the MAC addresses that are allowed to send traffic into the port.
Instructions
Part 1: Configure Port Security
a. Access the command line for S1 and enable port security on Fast Ethernet ports 0/1 and 0/2.
S1(config)# interface range fastethernet 0/1 - 2
S1(config-if-range)# switchport port-security
b. Set the maximum so that only one device can access the Fast Ethernet ports 0/1 and 0/2.
S1(config-if-range)# switchport port-security maximum 1
c. Secure the ports so that the MAC address of a device is dynamically learned and added to the running configuration.
S1(config-if-range)# switchport port-security mac-address sticky
d. Set the violation mode so that the Fast Ethernet ports 0/1 and 0/2 are not disabled when a violation occurs, but a notification of the security violation is generated and packets from the unknown source are dropped.
S1(config-if-range)# switchport port-security violation restrict
e. Disable all the remaining unused ports. Use the range keyword to apply this configuration to all the ports simultaneously.
S1(config-if-range)# interface range fastethernet 0/3 - 24, gigabitethernet 0/1 - 2
S1(config-if-range)# shutdown
Part 2: Verify Port Security
a. From PC1, ping PC2.
C:\> ping 10.10.10.11
b. Verify that port security is enabled and the MAC addresses of PC1 and PC2 were added to the running configuration.
S1# show running-config | begin interface
interface FastEthernet0/1
 switchport mode access
 switchport port-security
 switchport port-security mac-address sticky
 switchport port-security violation restrict
 switchport port-security mac-address sticky 00E0.B027.2245
!
interface FastEthernet0/2
 switchport mode access
 switchport port-security
 switchport port-security mac-address sticky
 switchport port-security violation restrict
 switchport port-security mac-address sticky 0001.647C.697E
!
interface FastEthernet0/3
 shutdown
!
interface FastEthernet0/4
 shutdown
!
interface FastEthernet0/5
 shutdown
!
interface FastEthernet0/6
 shutdown
!
interface FastEthernet0/7
 shutdown
!
interface FastEthernet0/8
 shutdown
!
interface FastEthernet0/9
 shutdown
!
interface FastEthernet0/10
 shutdown
!
interface FastEthernet0/11
 shutdown
!
interface FastEthernet0/12
 shutdown
!
interface FastEthernet0/13
 shutdown
!
interface FastEthernet0/14
 shutdown
!
interface FastEthernet0/15
 shutdown
!
interface FastEthernet0/16
 shutdown
!
interface FastEthernet0/17
 shutdown
!
interface FastEthernet0/18
 shutdown
!
interface FastEthernet0/19
 shutdown
!
interface FastEthernet0/20
 shutdown
!
interface FastEthernet0/21
 shutdown
!
interface FastEthernet0/22
 shutdown
!
interface FastEthernet0/23
 shutdown
!
interface FastEthernet0/24
 shutdown
!
interface GigabitEthernet0/1
 shutdown
!
interface GigabitEthernet0/2
 shutdown
!
interface Vlan1
 ip address 10.10.10.2 255.255.255.0
!
!
!
!
!
!
line con 0
!
line vty 0 4
 login
line vty 5 15
 login
!
!
!
!
end
c. Use port-security show commands to display configuration information.
S1# show port-security
Secure Port MaxSecureAddr CurrentAddr SecurityViolation Security Action
               (Count)       (Count)        (Count)
--------------------------------------------------------------------
        Fa0/1        1          1                 0         Restrict
        Fa0/2        1          1                 0         Restrict
----------------------------------------------------------------------S1# show port-security address
Secure Mac Address Table
-----------------------------------------------------------------------------
Vlan Mac Address Type Ports Remaining Age
(mins)
---- ----------- ---- ----- -------------
1 00E0.B027.2245 SecureSticky Fa0/1 -
1 0001.647C.697E SecureSticky Fa0/2 -
-----------------------------------------------------------------------------
Total Addresses in System (excluding one mac per port) : 0
Max Addresses limit in System (excluding one mac per port) : 1024d. Attach Rogue Laptop to any unused switch port and notice that the link lights are red.
e. Enable the port and verify that Rogue Laptop can ping PC1 and PC2. After verification, shut down the port connected to Rogue Laptop.
f. Disconnect PC2 and connect Rogue Laptop to F0/2, which is the port to which PC2 was originally connected. Verify that Rogue Laptop is unable to ping PC1.
C:\> ping 10.10.10.10
g. Display the port security violations for the port to which Rogue Laptop is connected.
S1# show port-security interface fastethernet 0/2
Port Security              : Enabled
Port Status                : Secure-up
Violation Mode             : Restrict
Aging Time                 : 0 mins
Aging Type                 : Absolute
SecureStatic Address Aging : Disabled
Maximum MAC Addresses      : 1
Total MAC Addresses        : 1
Configured MAC Addresses   : 0
Sticky MAC Addresses       : 1
Last Source Address:Vlan   : 0002.4A42.C51C:1
Security Violation Count   : 19
How many violations have occurred?
Answers may vary. Every frame that the Rogue Laptop sends into F0/2 from its unknown MAC address is counted as a violation, so the count keeps increasing while the Rogue Laptop tries to ping PC1. In this activity, the Security Violation Count is 19.
h. Disconnect Rogue Laptop and reconnect PC2. Verify PC2 can ping PC1.
C:\> ping 10.10.10.10
Why is PC2 able to ping PC1, but the Rogue Laptop is not?
The port security that was enabled on the port only allowed the device, whose MAC was learned first, access to the port while preventing all other devices access.
Device Configs - Final
SWITCH S1
! ==============================================================
!--- 11.1.10 Packet Tracer - Implement Port Security
!--- ANSWER SCRIPT FOR SWITCH S1
!--- Usage: copy this whole file and paste it into the S1 terminal (start at the S1> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1: Configure Port Security.
! --------------------------------------------------------------

!--- a. Enable port security on F0/1 and F0/2.
interface range fastethernet 0/1 - 2
 switchport port-security
!--- b. Only one device (MAC address) may use each port.
 switchport port-security maximum 1
!--- c. Learn the MAC address dynamically and add it to the running configuration.
 switchport port-security mac-address sticky
!--- d. Violation mode restrict: drop unknown frames and log the violation, but keep the port up.
 switchport port-security violation restrict
 exit

!--- e. Disable all remaining unused ports.
interface range fastethernet 0/3 - 24, gigabitethernet 0/1 - 2
 shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show port-security            -> Fa0/1 and Fa0/2: MaxSecureAddr 1, Security Action Restrict
!---   show port-security address    -> SecureSticky MAC addresses of PC1 and PC2 (after PC1 pings PC2)
!---   show running-config | begin interface -> switchport port-security mac-address sticky <MAC> under Fa0/1 and Fa0/2
!--- Note: the sticky MAC addresses appear only after PC1 and PC2 send traffic; save again after the ping so they are kept in the startup configuration.
! ==============================================================