17.8.2 Packet Tracer – Skills Integration Challenge Answers
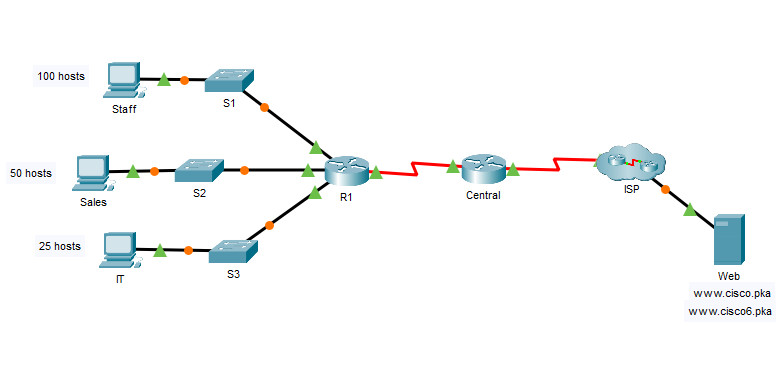
17.8.2 Packet Tracer - Skills Integration Challenge
Addressing Table
| Device | Interface | IP Address / Prefix | Default Gateway |
|---|---|---|---|
| R1 | G0/0 | 192.168.0.1 /25 | N/A |
| G0/0 | 2001:db8:acad::1/64 | N/A | |
| G0/0 | fe80::1 | N/A | |
| G0/1 | 192.168.0.129 /26 | N/A | |
| G0/1 | 2001:db8:acad:1::1/64 | N/A | |
| G0/1 | fe80::1 | N/A | |
| G0/2 | 192.168.0.193 /27 | N/A | |
| G0/2 | 2001:db8:acad:2::1/64 | N/A | |
| G0/2 | fe80::1 | N/A | |
| S0/0/1 | 172.16.1.2 /30 | N/A | |
| S0/0/1 | 2001:db8:2::1/64 | N/A | |
| S0/0/1 | fe80::1 | N/A | |
| Central | S0/0/0 | 209.165.200.226 /30 | N/A |
| S0/0/0 | 2001:db8:1::1/64 | N/A | |
| S0/0/0 | fe80::2 | N/A | |
| S0/0/1 | 172.16.1.1 /30 | N/A | |
| S0/0/1 | 2001:db8:2::2/64 | N/A | |
| S0/0/1 | fe80::2 | N/A | |
| S1 | VLAN 1 | 192.168.0.2 /25 | 192.168.0.1 |
| S2 | VLAN 1 | 192.168.0.130 /26 | 192.168.0.129 |
| S3 | VLAN 1 | 192.168.0.194 /27 | 192.168.0.193 |
| Staff | NIC | 192.168.0.3 /25 | 192.168.0.1 |
| NIC | 2001:db8:acad::2/64 | fe80::1 | |
| NIC | fe80::2 | fe80::1 | |
| Sales | NIC | 192.168.0.131 /26 | 192.168.0.129 |
| NIC | 2001:db8:acad:1::2/64 | fe80::1 | |
| NIC | fe80::2 | fe80::1 | |
| IT | NIC | 192.168.0.195 /27 | 192.168.0.193 |
| NIC | 2001:db8:acad:2::2/64 | fe80::1 | |
| NIC | fe80::2 | fe80::1 | |
| Web | NIC | 64.100.0.3 /29 | 64.100.0.1 |
| NIC | 2001:db8:cafe::3/64 | fe80::1 | |
| NIC | fe80::2 | fe80::1 |
Background / Scenario
The router Central, ISP cluster, and the Web server are completely configured. You must create a new IPv4 addressing scheme that will accommodate 4 subnets using the 192.168.0.0/24 network. The IT department requires 25 hosts. The Sales department needs 50 hosts. The subnet for the rest of the staff requires 100 hosts. A Guest subnet will be added in the future to accommodate 25 hosts. You must also finish the basic security settings and interface configurations on R1. Then, you will configure the SVI interface and basic security settings on switches S1, S2, and S3.
Instructions
IPv4 Addressing
- Use 192.168.0.0/24 to create subnets that meet the host requirements.
- Staff: 100 hosts
- Sales: 50 hosts
- IT: 25 hosts
- Guest network to be added later: 25 hosts
- Document the IPv4 addresses that have been assigned in the Addressing Table.
- Record the subnet for the Guest network: 192.168.0.224/27
PC Configurations
- Configure the assigned IPv4 address, subnet mask, and default gateway settings on the Staff, Sales, and IT PCs using your addressing scheme.
- Assign the IPv6 unicast and link local addresses and default gateways to the Staff, Sales, and IT networks according to the Addressing Table.
R1 Configurations
- Configure the device name according to the Addressing Table.
Router(config)# hostname R1
- Disable DNS lookup.
R1(config)# no ip domain-lookup
- Assign Ciscoenpa55 as the encrypted privileged EXEC mode password.
R1(config)# enable secret Ciscoenpa55
- Assign Ciscoconpa55 as the console password and enable login.
R1(config)# line console 0
R1(config-line)# password Ciscoconpa55
R1(config-line)# login
- Require that a minimum of 10 characters be used for all passwords.
R1(config)# security passwords min-length 10
- Encrypt all plaintext passwords.
R1(config)# service password-encryption
- Create a banner that warns anyone accessing the device that unauthorized access is prohibited.
R1(config)# banner motd #Unauthorized access is prohibited!#
- Configure and enable all the Gigabit Ethernet interfaces.
- Configure the IPv4 addresses according to your addressing scheme.
- Configure the IPv6 addresses according to the Addressing Table.
R1(config)# ipv6 unicast-routing
R1(config)# interface gigabitethernet 0/0
R1(config-if)# ip address 192.168.0.1 255.255.255.128
R1(config-if)# ipv6 address 2001:db8:acad::1/64
R1(config-if)# ipv6 address fe80::1 link-local
R1(config-if)# no shutdown
R1(config-if)# interface gigabitethernet 0/1
R1(config-if)# ip address 192.168.0.129 255.255.255.192
R1(config-if)# ipv6 address 2001:db8:acad:1::1/64
R1(config-if)# ipv6 address fe80::1 link-local
R1(config-if)# no shutdown
R1(config-if)# interface gigabitethernet 0/2
R1(config-if)# ip address 192.168.0.193 255.255.255.224
R1(config-if)# ipv6 address 2001:db8:acad:2::1/64
R1(config-if)# ipv6 address fe80::1 link-local
R1(config-if)# no shutdown
- Configure SSH on R1:
- Set the domain name to CCNA-lab.com
- Generate a 1024-bit RSA key.
- Configure the VTY lines for SSH access.
- Use the local user profiles for authentication.
- Create a user Admin1 with a privilege level of 15 and use the encrypted password of Admin1pa55.
R1(config)# ip domain-name CCNA-lab.com
R1(config)# crypto key generate rsa general-keys modulus 1024
R1(config)# line vty 0 4
R1(config-line)# transport input ssh
R1(config-line)# login local
R1(config-line)# exit
R1(config)# username Admin1 privilege 15 secret Admin1pa55
- Configure the console and VTY lines to log out after five minutes of inactivity.
R1(config)# line console 0
R1(config-line)# exec-timeout 5 0
R1(config-line)# line vty 0 4
R1(config-line)# exec-timeout 5 0
- Block anyone for three minutes who fails to log in after four attempts within a two-minute period.
R1(config)# login block-for 180 attempts 4 within 120
Switch Configuration
- Configure the device name according to the Addressing Table.
Switch(config)# hostname S1
Switch(config)# hostname S2
Switch(config)# hostname S3
- Configure the SVI interface with the IPv4 address and subnet mask according to your addressing scheme.
S1(config)# interface vlan 1
S1(config-if)# ip address 192.168.0.2 255.255.255.128
S1(config-if)# no shutdown
S2(config)# interface vlan 1
S2(config-if)# ip address 192.168.0.130 255.255.255.192
S2(config-if)# no shutdown
S3(config)# interface vlan 1
S3(config-if)# ip address 192.168.0.194 255.255.255.224
S3(config-if)# no shutdown
- Configure the default gateway.
S1(config)# ip default-gateway 192.168.0.1
S2(config)# ip default-gateway 192.168.0.129
S3(config)# ip default-gateway 192.168.0.193
- Disable DNS lookup.
S1(config)# no ip domain-lookup
S2(config)# no ip domain-lookup
S3(config)# no ip domain-lookup
- Assign Ciscoenpa55 as the encrypted privileged EXEC mode password.
S1(config)# enable secret Ciscoenpa55
S2(config)# enable secret Ciscoenpa55
S3(config)# enable secret Ciscoenpa55
- Assign Ciscoconpa55 as the console password and enable login.
S1(config)# line console 0
S1(config-line)# password Ciscoconpa55
S1(config-line)# login
S2(config)# line console 0
S2(config-line)# password Ciscoconpa55
S2(config-line)# login
S3(config)# line console 0
S3(config-line)# password Ciscoconpa55
S3(config-line)# login
- Configure the console and VTY lines to log out after five minutes of inactivity.
S1(config)# line console 0
S1(config-line)# exec-timeout 5 0
S1(config-line)# line vty 0 15
S1(config-line)# exec-timeout 5 0
S2(config)# line console 0
S2(config-line)# exec-timeout 5 0
S2(config-line)# line vty 0 15
S2(config-line)# exec-timeout 5 0
S3(config)# line console 0
S3(config-line)# exec-timeout 5 0
S3(config-line)# line vty 0 15
S3(config-line)# exec-timeout 5 0
- Encrypt all plaintext passwords.
S1(config)# service password-encryption
S2(config)# service password-encryption
S3(config)# service password-encryption
Connectivity Requirements
- Use the web browser on the Staff, Sales, and IT PCs to navigate to www.cisco.pka.
- Use the web browser on the Staff, Sales, and IT PCs to navigate to www.cisco6.pka.
- All PCs should be able to ping all the other devices.
Device Configs - Final
ROUTER R1
! ==============================================================
!--- 17.8.2 Packet Tracer - Skills Integration Challenge
!--- ANSWER SCRIPT FOR ROUTER R1
!--- Usage: copy this whole file and paste it into the ROUTER R1 terminal (start at the Router> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Basic security settings
! --------------------------------------------------------------

!--- Encrypt all plaintext passwords (set first so every password below is stored encrypted).
service password-encryption

!--- Require a minimum of 10 characters for all passwords (set BEFORE the passwords below).
security passwords min-length 10

!--- Assign the device name.
hostname R1

!--- Disable DNS lookup.
no ip domain-lookup

!--- Encrypted privileged EXEC password: Ciscoenpa55.
enable secret Ciscoenpa55

!--- Block anyone for 3 minutes (180 s) who fails 4 login attempts within 2 minutes (120 s).
login block-for 180 attempts 4 within 120

!--- Banner warning against unauthorized access. (The answer key leaves a placeholder 'Any text' here - replace it with a real warning.)
banner motd #Unauthorized access is prohibited!#

!--- Enable IPv6 routing so R1 forwards IPv6 between the LANs.
ipv6 unicast-routing

! --------------------------------------------------------------
!--- SSH configuration
! --------------------------------------------------------------

!--- Set the domain name (required before RSA keys can be generated).
ip domain-name CCNA-lab.com

!--- Create the SSH admin account with privilege level 15 and password Admin1pa55.
username Admin1 privilege 15 secret Admin1pa55

!--- Generate the 1024-bit RSA key. This one-line form supplies the modulus, so there is no interactive prompt to answer.
crypto key generate rsa general-keys modulus 1024

! --------------------------------------------------------------
!--- Console and VTY lines (log out after 5 minutes of inactivity)
! --------------------------------------------------------------

!--- Console: password Ciscoconpa55, require login, 5-minute idle timeout.
line console 0
 password Ciscoconpa55
 login
 exec-timeout 5 0
 exit

!--- VTY: SSH only, authenticate with the local user database, 5-minute idle timeout.
line vty 0 4
 login local
 transport input ssh
 exec-timeout 5 0
 exit

! --------------------------------------------------------------
!--- Interfaces - IPv4 per the new subnetting scheme + IPv6 per the Addressing Table
! --------------------------------------------------------------

!--- G0/0 - Staff LAN: 192.168.0.0/25 (100 hosts), first host as the gateway.
interface gigabitethernet 0/0
 ip address 192.168.0.1 255.255.255.128
 ipv6 address 2001:db8:acad::1/64
 ipv6 address fe80::1 link-local
 no shutdown
 exit

!--- G0/1 - Sales LAN: 192.168.0.128/26 (50 hosts), first host as the gateway.
interface gigabitethernet 0/1
 ip address 192.168.0.129 255.255.255.192
 ipv6 address 2001:db8:acad:1::1/64
 ipv6 address fe80::1 link-local
 no shutdown
 exit

!--- G0/2 - IT LAN: 192.168.0.192/27 (25 hosts), first host as the gateway.
interface gigabitethernet 0/2
 ip address 192.168.0.193 255.255.255.224
 ipv6 address 2001:db8:acad:2::1/64
 ipv6 address fe80::1 link-local
 no shutdown
 exit

!--- S0/0/1 - WAN link to the Central router (already listed in the answer key; re-applying is harmless).
interface serial 0/0/1
 ip address 172.16.1.2 255.255.255.252
 ipv6 address 2001:db8:2::1/64
 ipv6 address fe80::1 link-local
 no shutdown
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief    -> all Gigabit interfaces up/up
!---   show ipv6 interface brief  -> GUA + fe80::1 on each interface
!---   show ip route              -> three connected LAN subnets
!---   show ip ssh                -> SSH enabled, RSA key present
! ==============================================================
SWITCH S1
! ==============================================================
!--- 17.8.2 Packet Tracer - Skills Integration Challenge
!--- ANSWER SCRIPT FOR SWITCH S1
!--- Usage: copy this whole file and paste it into the SWITCH S1 terminal (start at the Switch> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Basic security settings
! --------------------------------------------------------------

!--- Encrypt all plaintext passwords (set first so every password below is stored encrypted).
service password-encryption

!--- Assign the device name.
hostname S1

!--- Disable DNS lookup.
no ip domain-lookup

!--- Encrypted privileged EXEC password: Ciscoenpa55.
enable secret Ciscoenpa55

! --------------------------------------------------------------
!--- Console and VTY lines (log out after 5 minutes of inactivity)
! --------------------------------------------------------------

!--- Console: password Ciscoconpa55, require login, 5-minute idle timeout.
line console 0
 password Ciscoconpa55
 login
 exec-timeout 5 0
 exit

!--- VTY lines: 5-minute idle timeout and require login (per the answer key).
line vty 0 4
 login
 exec-timeout 5 0
 exit
line vty 5 15
 login
 exec-timeout 5 0
 exit

! --------------------------------------------------------------
!--- Management interface
! --------------------------------------------------------------

!--- VLAN 1 SVI on the Staff LAN, second host of the subnet.
interface vlan 1
 ip address 192.168.0.2 255.255.255.128
 no shutdown
 exit

!--- Default gateway (the R1 interface on this LAN).
ip default-gateway 192.168.0.1

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief  -> VLAN 1 up/up with its IP
!---   ping 192.168.0.1         -> reach the default gateway
! ==============================================================
SWITCH S2
! ==============================================================
!--- 17.8.2 Packet Tracer - Skills Integration Challenge
!--- ANSWER SCRIPT FOR SWITCH S2
!--- Usage: copy this whole file and paste it into the SWITCH S2 terminal (start at the Switch> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Basic security settings
! --------------------------------------------------------------

!--- Encrypt all plaintext passwords (set first so every password below is stored encrypted).
service password-encryption

!--- Assign the device name.
hostname S2

!--- Disable DNS lookup.
no ip domain-lookup

!--- Encrypted privileged EXEC password: Ciscoenpa55.
enable secret Ciscoenpa55

! --------------------------------------------------------------
!--- Console and VTY lines (log out after 5 minutes of inactivity)
! --------------------------------------------------------------

!--- Console: password Ciscoconpa55, require login, 5-minute idle timeout.
line console 0
 password Ciscoconpa55
 login
 exec-timeout 5 0
 exit

!--- VTY lines: 5-minute idle timeout and require login (per the answer key).
line vty 0 4
 login
 exec-timeout 5 0
 exit
line vty 5 15
 login
 exec-timeout 5 0
 exit

! --------------------------------------------------------------
!--- Management interface
! --------------------------------------------------------------

!--- VLAN 1 SVI on the Sales LAN, second host of the subnet.
interface vlan 1
 ip address 192.168.0.130 255.255.255.192
 no shutdown
 exit

!--- Default gateway (the R1 interface on this LAN).
ip default-gateway 192.168.0.129

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief  -> VLAN 1 up/up with its IP
!---   ping 192.168.0.129       -> reach the default gateway
! ==============================================================
SWITCH S3
! ==============================================================
!--- 17.8.2 Packet Tracer - Skills Integration Challenge
!--- ANSWER SCRIPT FOR SWITCH S3
!--- Usage: copy this whole file and paste it into the SWITCH S3 terminal (start at the Switch> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Basic security settings
! --------------------------------------------------------------

!--- Encrypt all plaintext passwords (set first so every password below is stored encrypted).
service password-encryption

!--- Assign the device name.
hostname S3

!--- Disable DNS lookup.
no ip domain-lookup

!--- Encrypted privileged EXEC password: Ciscoenpa55.
enable secret Ciscoenpa55

! --------------------------------------------------------------
!--- Console and VTY lines (log out after 5 minutes of inactivity)
! --------------------------------------------------------------

!--- Console: password Ciscoconpa55, require login, 5-minute idle timeout.
line console 0
 password Ciscoconpa55
 login
 exec-timeout 5 0
 exit

!--- VTY lines: 5-minute idle timeout and require login (per the answer key).
line vty 0 4
 login
 exec-timeout 5 0
 exit
line vty 5 15
 login
 exec-timeout 5 0
 exit

! --------------------------------------------------------------
!--- Management interface
! --------------------------------------------------------------

!--- VLAN 1 SVI on the IT LAN, second host of the subnet.
interface vlan 1
 ip address 192.168.0.194 255.255.255.224
 no shutdown
 exit

!--- Default gateway (the R1 interface on this LAN).
ip default-gateway 192.168.0.193

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief  -> VLAN 1 up/up with its IP
!---   ping 192.168.0.193       -> reach the default gateway
! ==============================================================
PC Staff
StaffPC
IPv4
IP Address192.168.0.3
Subnet Mask255.255.255.128
Default Gateway192.168.0.1
IPv6
IPv6 Address2001:db8:acad::2/64
Link-Local Addressfe80::2
IPv6 Gatewayfe80::1
PC Sales
SalesPC
IPv4
IP Address192.168.0.131
Subnet Mask255.255.255.192
Default Gateway192.168.0.129
IPv6
IPv6 Address2001:db8:acad:1::2/64
Link-Local Addressfe80::2
IPv6 Gatewayfe80::1
PC IT
ITPC
IPv4
IP Address192.168.0.195
Subnet Mask255.255.255.224
Default Gateway192.168.0.193
IPv6
IPv6 Address2001:db8:acad:2::2/64
Link-Local Addressfe80::2
IPv6 Gatewayfe80::1


