5.5.1 Packet Tracer - IPv4 ACL Implementation Challenge Answers
Topology
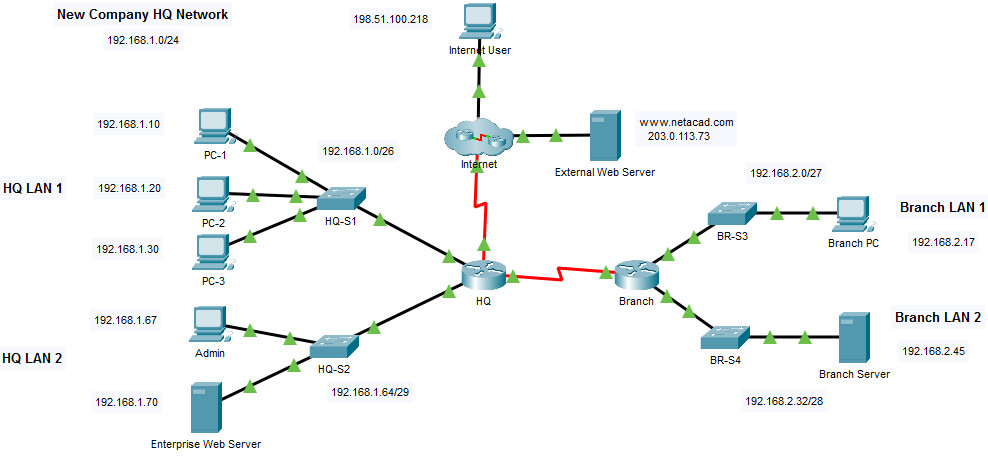
5.5.1 Packet Tracer - IPv4 ACL Implementation Challenge
Addressing Table
| Device | Interface | IP Address |
|---|---|---|
| HQ | G0/0/0 | 192.168.1.1/26 |
| G0/0/1 | 192.168.1.65/29 | |
| S0/1/0 | 192.0.2.1/30 | |
| S0/1/1 | 192.168.3.1/30 | |
| Branch | G0/0/0 | 192.168.2.1/27 |
| G0/0/1 | 192.168.2.33/28 | |
| S0/1/1 | 192.168.3.2/30 | |
| PC-1 | NIC | 192.168.1.10/26 |
| PC-2 | NIC | 192.168.1.20/26 |
| PC-3 | NIC | 192.168.1.30/26 |
| Admin | NIC | 192.168.1.67/29 |
| Enterprise Web Server | NIC | 192.168.1.70/29 |
| Branch PC | NIC | 192.168.2.17/27 |
| Branch Server | NIC | 192.168.2.45/28 |
| Internet User | NIC | 198.51.100.218/24 |
| External Web Server | NIC | 203.0.113.73/24 |
Objectives
- Configure a router with standard named ACLs.
- Configure a router with extended named ACLs.
- Configure a router with extended ACLs to meet specific communication requirements.
- Configure an ACL to control access to network device terminal lines.
- Configure the appropriate router interfaces with ACLs in the appropriate direction.
- Verify the operation of the configured ACLs.
Background / Scenario
In this activity you will configure extended, standard named, and extended named ACLs to meet specified communication requirements.
Instructions
Step 1: Verify Connectivity in the New Company Network
First, test connectivity on the network as it is before configuring the ACLs. All hosts should be able to ping all other hosts.
Step 2: Configure Standard and Extended ACLs per Requirements.
Configure ACLs to meet the following requirements:
Important guidelines:
- Do not use explicit deny any statements at the end of your ACLs.
- Use shorthand (host and any) whenever possible.
- Write your ACL statements to address the requirements in the order that they are specified here.
- Place your ACLs in the most efficient location and direction.
ACL 1 Requirements
- Create ACL 101.
- Explicitly block FTP access to the Enterprise Web Server from the internet.
HQ(config)# access-list 101 deny tcp any host 192.168.1.70 eq ftp
- No ICMP traffic from the internet should be allowed to any hosts on HQ LAN 1.
HQ(config)# access-list 101 deny icmp any 192.168.1.0 0.0.0.63
- Allow all other traffic.
HQ(config)# access-list 101 permit ip any any
HQ(config)# interface serial 0/1/0
HQ(config-if)# ip access-group 101 in
ACL 2 Requirements
- Use ACL number 111.
- No hosts on HQ LAN 1 should be able to access the Branch Server.
HQ(config)# access-list 111 deny ip any host 192.168.2.45
- All other traffic should be permitted.
HQ(config)# access-list 111 permit ip any any
HQ(config)# interface gigabitethernet 0/0/0
HQ(config-if)# ip access-group 111 in
ACL 3 Requirements
- Create a named standard ACL. Use the name vty_block. The name of your ACL must match this name exactly.
HQ(config)# ip access-list standard vty_block
- Only addresses from the HQ LAN 2 network should be able to access the VTY lines of the HQ router.
HQ(config-std-nacl)# permit 192.168.1.64 0.0.0.7
HQ(config)# line vty 0 4
HQ(config-line)# access-class vty_block in
ACL 4 Requirements
- Create a named extended ACL called branch_to_hq. The name of your ACL must match this name exactly.
Branch(config)# ip access-list extended branch_to_hq
- No hosts on either of the Branch LANs should be allowed to access HQ LAN 1. Use one access list statement for each of the Branch LANs.
Branch(config-ext-nacl)# deny ip 192.168.2.0 0.0.0.31 192.168.1.0 0.0.0.63
Branch(config-ext-nacl)# deny ip 192.168.2.32 0.0.0.15 192.168.1.0 0.0.0.63
- All other traffic should be allowed.
Branch(config-ext-nacl)# permit ip any any
Branch(config)# interface serial 0/1/1
Branch(config-if)# ip access-group branch_to_hq out
Step 3: Verify ACL Operation.
a. Perform the following connectivity tests between devices in the topology. Note whether or not they are successful.
Note: Use the show ip access-lists command to verify ACL operation. Use the clear access-list counters command to reset the match counters.
Send a ping request from Branch PC to the Enterprise Web Server. Was it successful? Explain.
C:\> ping 192.168.1.70

Pinging 192.168.1.70 with 32 bytes of data:

Reply from 192.168.1.70: bytes=32 time=17ms TTL=126
Reply from 192.168.1.70: bytes=32 time=17ms TTL=126
Reply from 192.168.1.70: bytes=32 time=15ms TTL=126
Reply from 192.168.1.70: bytes=32 time=6ms TTL=126

Ping statistics for 192.168.1.70:
    Packets: Sent = 4, Received = 4, Lost = 0 (0% loss),
Approximate round trip times in milli-seconds:
    Minimum = 6ms, Maximum = 17ms, Average = 13ms
The ping was successful because it was permitted by the ACL.
Which ACL statement permitted or denied the ping between these two devices? List the access list name or number, the router on which it was applied, and the specific line that the traffic matched.
Branch# show ip access-lists
Extended IP access list branch_to_hq
    10 deny ip 192.168.2.0 0.0.0.31 192.168.1.0 0.0.0.63
    20 deny ip 192.168.2.32 0.0.0.15 192.168.1.0 0.0.0.63
    30 permit ip any any (15 match(es))
The last line (line 30, permit ip any any) in the branch_to_hq ACL on the Branch router permitted this traffic.
Attempt to ping from PC-1 on the HQ LAN 1 to the Branch Server. Was it successful? Explain.
C:\> ping 192.168.2.45

Pinging 192.168.2.45 with 32 bytes of data:

Reply from 192.168.1.1: Destination host unreachable.
Reply from 192.168.1.1: Destination host unreachable.
Reply from 192.168.1.1: Destination host unreachable.
Reply from 192.168.1.1: Destination host unreachable.

Ping statistics for 192.168.2.45:
    Packets: Sent = 4, Received = 0, Lost = 4 (100% loss),
The ping was not successful because the traffic was blocked by an access list.
Which ACL statement permitted or denied the ping between these two devices?
Statement 10 in access list 111 on the HQ router denies all traffic to the branch server.
Open a web browser on the External Web Server and attempt to bring up a web page stored on the Enterprise Web Server. Is it successful? Explain.
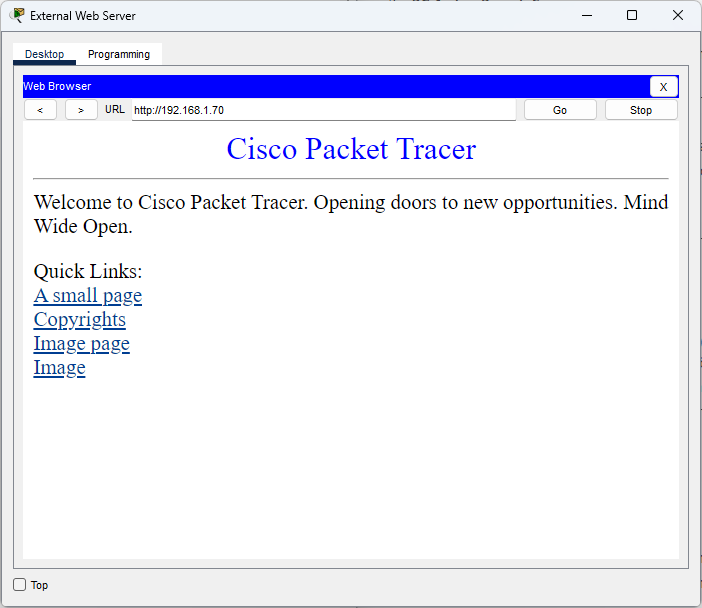
Yes, the External Web Server can access a web page on the Enterprise Web Server. HTTP traffic is not blocked to the Enterprise Web Server.
Which ACL statement permitted or denied the traffic between these two devices?
HQ# show ip access-lists
Extended IP access list 101
    10 deny tcp any host 192.168.1.70 eq ftp
    20 deny icmp any 192.168.1.0 0.0.0.63
    30 permit ip any any (16 match(es))
Extended IP access list 111
    10 deny ip any host 192.168.2.45 (4 match(es))
    20 permit ip any any
Standard IP access list vty_block
    10 permit 192.168.1.64 0.0.0.7
Line 30 (permit ip any any) in access list 101 on the HQ router permitted this traffic.
b. Test connections to an internal server from the internet.
From the command line on the Internet User PC, attempt to make an FTP connection to the Branch Server. Is the FTP connection successful?
C:\> ftp 192.168.2.45
Trying to connect...192.168.2.45
Connected to 192.168.2.45
220- Welcome to PT Ftp server
Username:cisco
331- Username ok, need password
Password:*****
230- Logged in
(passive mode On)
ftp> quit

221- Service closing control connection.
Yes, the FTP connection from the internet User PC to the Branch Server is successful.
Which access list should be modified to prevent users from the Internet from making FTP connections to the Branch Server?
The access list 101 on the HQ router needs to be modified to deny this traffic.
Which statement(s) should be added to the access list to deny this traffic?
The statement “deny tcp any host 192.168.2.45 eq 21” or “deny tcp any host 192.168.2.45 range 20 21” needs to be added to the access list 101.
Device Configs - Final
ROUTER HQ
! ==============================================================
!--- 5.5.1 Packet Tracer - IPv4 ACL Implementation Challenge
!--- ANSWER SCRIPT FOR ROUTER HQ
!--- Usage: open the HQ CLI tab and paste this whole file at the HQ> prompt. Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Step 2: Configure Standard and Extended ACLs per Requirements.
! --------------------------------------------------------------

!--- ACL 1: block FTP to the Enterprise Web Server and ICMP to HQ LAN 1 from the internet.
access-list 101 deny tcp any host 192.168.1.70 eq ftp
access-list 101 deny icmp any 192.168.1.0 0.0.0.63
access-list 101 permit ip any any

!--- Apply ACL 101 inbound on the internet-facing interface S0/1/0.
interface serial 0/1/0
 ip access-group 101 in
 exit

!--- ACL 2: no HQ LAN 1 host may access the Branch Server.
access-list 111 deny ip any host 192.168.2.45
access-list 111 permit ip any any

!--- Apply ACL 111 inbound on G0/0/0 (HQ LAN 1).
interface gigabitethernet 0/0/0
 ip access-group 111 in
 exit

!--- ACL 3: named standard ACL vty_block, only HQ LAN 2 (192.168.1.64/29) may reach the VTY lines.
ip access-list standard vty_block
 permit 192.168.1.64 0.0.0.7
 exit

line vty 0 4
 access-class vty_block in
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip access-lists  -> 101 (3 lines), 111 (2 lines), vty_block (1 line)
!---   ping 192.168.2.45 from PC-1                 -> fails (ACL 111 line 10)
!---   web 192.168.1.70 from External Web Server   -> succeeds (ACL 101 line 30)
!--- Note: Step 3b asks which line to add to block internet FTP to the Branch Server:
!--- deny tcp any host 192.168.2.45 eq 21 in ACL 101 (before permit ip any any). Not part of the graded config.
! ==============================================================
ROUTER Branch
! ==============================================================
!--- 5.5.1 Packet Tracer - IPv4 ACL Implementation Challenge
!--- ANSWER SCRIPT FOR ROUTER Branch
!--- Usage: open the Branch CLI tab and paste this whole file at the Branch> prompt. Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Step 2: Configure Standard and Extended ACLs per Requirements.
! --------------------------------------------------------------

!--- ACL 4: named extended ACL branch_to_hq, neither Branch LAN may access HQ LAN 1.
ip access-list extended branch_to_hq
 deny ip 192.168.2.0 0.0.0.31 192.168.1.0 0.0.0.63
 deny ip 192.168.2.32 0.0.0.15 192.168.1.0 0.0.0.63
 permit ip any any
 exit

!--- Apply branch_to_hq outbound on S0/1/1 (toward HQ).
interface serial 0/1/1
 ip access-group branch_to_hq out
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip access-lists                  -> branch_to_hq lines 10, 20, 30
!---   ping 192.168.1.70 from Branch PC      -> succeeds (line 30)
!---   ping 192.168.1.10 from Branch PC      -> fails (line 10)
! ==============================================================


