
5.5.2 Packet Tracer - Configure and Verify Extended IPv4 ACLs - Physical Mode Answers
Topology
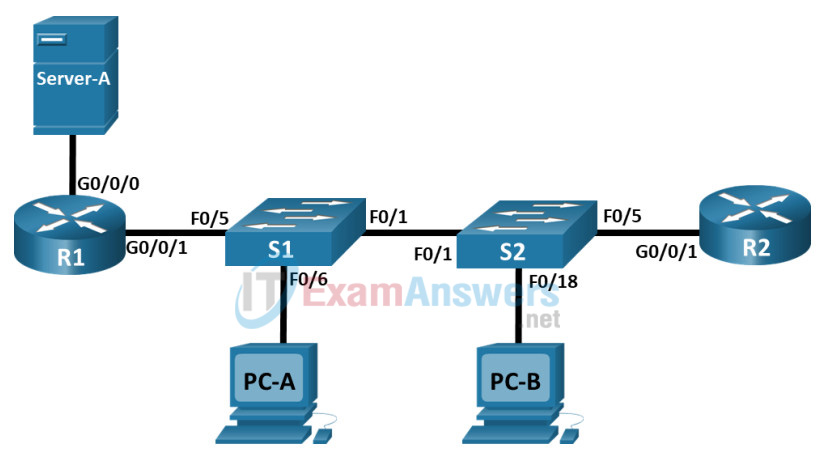
Addressing Table
| Device | Interface | IP Address | Subnet Mask | Default Gateway |
|---|---|---|---|---|
| R1 | G0/0/1 | N/A | N/A | N/A |
| G0/0/1.20 | 10.20.0.1 | 255.255.255.0 | ||
| G0/0/1.30 | 10.30.0.1 | 255.255.255.0 | ||
| G0/0/1.40 | 10.40.0.1 | 255.255.255.0 | ||
| G0/0/1.1000 | N/A | N/A | ||
| G0/0/0 | 172.16.1.1 | 255.255.255.0 | ||
| R2 | G0/0/1 | 10.20.0.4 | 255.255.255.0 | N/A |
| S1 | VLAN 20 | 10.20.0.2 | 255.255.255.0 | 10.20.0.1 |
| S2 | VLAN 20 | 10.20.0.3 | 255.255.255.0 | 10.20.0.1 |
| PC-A | NIC | 10.30.0.10 | 255.255.255.0 | 10.30.0.1 |
| PC-B | NIC | 10.40.0.10 | 255.255.255.0 | 10.40.0.1 |
| Server-A | NIC | 172.16.1.2 | 255.255.255.0 | 172.16.1.1 |
VLAN Table
| VLAN | Name | Interface Assigned |
|---|---|---|
| 20 | Management | S2: F0/5 |
| 30 | Operations | S1: F0/6 |
| 40 | Sales | S2: F0/18 |
| 999 | ParkingLot | S1: F0/2-4, F0/7-24, G0/1-2 S2: F0/2-4, F0/6-17, F0/19-24, G0/1-2 |
| 1000 | Native | N/A |
Objectives
- Part 1: Build the Network and Configure Basic Device Settings
- Part 2: Configure VLANs on the Switches
- Part 3: Configure Trunking
- Part 4: Configure Routing
- Part 5: Configure Remote Access
- Part 6: Verify Connectivity
- Part 7: Configure and Verify Extended Access Control Lists
Background / Scenario
In this Packet Tracer Physical Mode (PTPM) activity, you have been tasked with configuring access control lists (ACLs) on a small company’s network. ACLs are one of the simplest and most direct means of controlling Layer 3 traffic. R1 will be hosting an internet connection and sharing the default route information to R2. After initial configuration is complete, the company has some specific traffic security requirements that you will be responsible for implementing.
Note: There are over 100 items scored in this activity. Therefore, Packet Tracer will display the number of items currently correct instead of the percentage score.
Instructions
Part 1: Build the Network and Configure Basic Device Settings
Step 1: Cable the network as shown in the topology.
a. Cable and power on the devices as shown in the topology diagram. Use a console cable to connect a PC to each switch or router as you configure them. To access a switch or router, you must connect a console cable between the PCs and the device you wish to configure. We recommend connecting PC-A to R1 and PC-B to R2.
b. Then, when configuring the switches, connect PC-A to S1 and PC-B to S2. After you have connected the console cable, click the PC > Desktop tab > Terminal, and then click OK, to access the command line.
When changing a console cable to a new device, such as between a router and a switch, it is easier to click the end of the console cable and drag it back to the Cable Pegboard than it is to try to connect the cable directly to another device. After attaching a console cable to a different device, you must close and reopen the Terminal window to establish a new connection.
Step 2: Configure basic settings for each router.
a. Assign a device name to the router.
R1:
Router(config)# hostname R1
R2:
Router(config)# hostname R2
b. Disable DNS lookup to prevent the router from attempting to translate incorrectly entered commands as though they were host names.
R1:
R1(config)# no ip domain lookup
R2:
R2(config)# no ip domain lookup
c. Assign class as the privileged EXEC encrypted password.
R1:
R1(config)# enable secret class
R2:
R2(config)# enable secret class
d. Assign cisco as the console password and enable login.
R1:
R1(config)# line console 0
R1(config-line)# password cisco
R1(config-line)# login
R2:
R2(config)# line console 0
R2(config-line)# password cisco
R2(config-line)# login
e. Assign cisco as the vty password. You will enable login later in this activity.
R1:
R1(config)# line vty 0 4
R1(config-line)# password cisco
R2:
R2(config)# line vty 0 4
R2(config-line)# password cisco
f. Encrypt the plaintext passwords.
R1:
R1(config)# service password-encryption
R2:
R2(config)# service password-encryption
g. Create a banner that warns anyone accessing the device that unauthorized access is prohibited.
R1:
R1(config)# banner motd $ Authorized Users Only! $
R2:
R2(config)# banner motd $ Authorized Users Only! $
h. Save the running configuration to the startup configuration file.
R1:
R1# copy running-config startup-config
R2:
R2# copy running-config startup-config
Step 3: Configure basic settings for each switch.
a. Assign a device name to the switch.
S1:
Switch(config)# hostname S1
S2:
Switch(config)# hostname S2
b. Disable DNS lookup to prevent the switch from attempting to translate incorrectly entered commands as though they were host names.
S1:
S1(config)# no ip domain-lookup
S2:
S2(config)# no ip domain-lookup
c. Assign class as the privileged EXEC encrypted password.
S1:
S1(config)# enable secret class
S2:
S2(config)# enable secret class
d. Assign cisco as the console password and enable login.
S1:
S1(config)# line console 0
S1(config-line)# password cisco
S1(config-line)# login
S2:
S2(config)# line console 0
S2(config-line)# password cisco
S2(config-line)# login
e. Assign cisco as the vty password. You will enable login later in this activity.
S1:
S1(config)# line vty 0 15
S1(config-line)# password cisco
S2:
S2(config)# line vty 0 15
S2(config-line)# password cisco
f. Encrypt the plaintext passwords.
S1:
S1(config)# service password-encryption
S2:
S2(config)# service password-encryption
g. Create a banner that warns anyone accessing the device that unauthorized access is prohibited.
S1:
S1(config)# banner motd $ Authorized Users Only! $
S2:
S2(config)# banner motd $ Authorized Users Only! $
h. Save the running configuration to the startup configuration file.
S1:
S1# copy running-config startup-config
S2:
S2# copy running-config startup-config
Part 2: Configure VLANs on the Switches
Step 1: Create VLANs on both switches.
a. Create and name the required VLANs on each switch from the VLAN table.
S1:
S1(config)# vlan 20
S1(config-vlan)# name Management
S1(config-vlan)# vlan 30
S1(config-vlan)# name Operations
S1(config-vlan)# vlan 40
S1(config-vlan)# name Sales
S1(config-vlan)# vlan 999
S1(config-vlan)# name ParkingLot
S1(config-vlan)# vlan 1000
S1(config-vlan)# name Native
S2:
S2(config)# vlan 20
S2(config-vlan)# name Management
S2(config-vlan)# vlan 30
S2(config-vlan)# name Operations
S2(config-vlan)# vlan 40
S2(config-vlan)# name Sales
S2(config-vlan)# vlan 999
S2(config-vlan)# name ParkingLot
S2(config-vlan)# vlan 1000
S2(config-vlan)# name Native
b. Configure the management interface and default gateway on each switch using the IP address information in the Addressing Table.
S1:
S1(config)# interface vlan 20
S1(config-if)# ip address 10.20.0.2 255.255.255.0
S1(config-if)# no shutdown
S1(config)# ip default-gateway 10.20.0.1
S2:
S2(config)# interface vlan 20
S2(config-if)# ip address 10.20.0.3 255.255.255.0
S2(config-if)# no shutdown
S2(config)# ip default-gateway 10.20.0.1
c. Assign all unused ports on the switch to the Parking Lot VLAN. Configure them for static access mode, and administratively deactivate them.
Note: The interface range command helps to accomplish this task with as few commands as necessary.
S1:
S1(config)# interface range fastethernet 0/2 - 4, fastethernet 0/7 - 24, gigabitethernet 0/1 - 2
S1(config-if-range)# switchport mode access
S1(config-if-range)# switchport access vlan 999
S1(config-if-range)# shutdown
S2:
S2(config)# interface range fastethernet 0/2 - 4, fastethernet 0/6 - 17, fastethernet 0/19 - 24, gigabitethernet 0/1 - 2
S2(config-if-range)# switchport mode access
S2(config-if-range)# switchport access vlan 999
S2(config-if-range)# shutdown
Step 2: Assign VLANs to the correct switch interfaces.
a. Assign used ports to the appropriate VLAN (specified in the VLAN table) and configure them for static access mode.
S1:
S1(config)# interface fastethernet 0/6
S1(config-if)# switchport mode access
S1(config-if)# switchport access vlan 30
S2:
S2(config)# interface fastethernet 0/5
S2(config-if)# switchport mode access
S2(config-if)# switchport access vlan 20
S2(config-if)# interface fastethernet 0/18
S2(config-if)# switchport mode access
S2(config-if)# switchport access vlan 40
b. Issue the show vlan brief command and verify that the VLANs are assigned to the correct interfaces.
S1:
S1# show vlan brief

VLAN Name                             Status    Ports
---- -------------------------------- --------- -------------------------------
1    default                          active    Fa0/1, Fa0/5
20   Management                       active
30   Operations                       active    Fa0/6
40   Sales                            active
999  ParkingLot                       active    Fa0/2, Fa0/3, Fa0/4, Fa0/7
                                                Fa0/8, Fa0/9, Fa0/10, Fa0/11
                                                Fa0/12, Fa0/13, Fa0/14, Fa0/15
                                                Fa0/16, Fa0/17, Fa0/18, Fa0/19
                                                Fa0/20, Fa0/21, Fa0/22, Fa0/23
                                                Fa0/24, Gig0/1, Gig0/2
1000 Native                           active
1002 fddi-default                     active
1003 token-ring-default               active
1004 fddinet-default                  active
1005 trnet-default                    active
S2:
S2# show vlan brief

VLAN Name                             Status    Ports
---- -------------------------------- --------- -------------------------------
1    default                          active    Fa0/1
20   Management                       active    Fa0/5
30   Operations                       active
40   Sales                            active    Fa0/18
999  ParkingLot                       active    Fa0/2, Fa0/3, Fa0/4, Fa0/6
                                                Fa0/7, Fa0/8, Fa0/9, Fa0/10
                                                Fa0/11, Fa0/12, Fa0/13, Fa0/14
                                                Fa0/15, Fa0/16, Fa0/17, Fa0/19
                                                Fa0/20, Fa0/21, Fa0/22, Fa0/23
                                                Fa0/24, Gig0/1, Gig0/2
1000 Native                           active
1002 fddi-default                     active
1003 token-ring-default               active
1004 fddinet-default                  active
1005 trnet-default                    active
Part 3: Configure Trunking
Step 1: Manually configure trunk interface F0/1.
a. Change the switchport mode on interface F0/1 to force trunking. Make sure to do this on both switches.
S1:
S1(config)# interface fastethernet 0/1
S1(config-if)# switchport mode trunk
S2:
S2(config)# interface fastethernet 0/1
S2(config-if)# switchport mode trunk
b. As a part of the trunk configuration, set the native vlan to 1000 on both switches. You may see error messages temporarily while the two interfaces are configured for different Native VLANs.
S1:
S1(config-if)# switchport trunk native vlan 1000
S2:
S2(config-if)# switchport trunk native vlan 1000
c. As another part of trunk configuration, specify that VLANs 20, 30, 40, and 1000 are allowed to cross the trunk.
S1:
S1(config-if)# switchport trunk allowed vlan 20,30,40,1000
S2:
S2(config-if)# switchport trunk allowed vlan 20,30,40,1000
d. Issue the show interfaces trunk command to verify trunking ports, the Native VLAN and allowed VLANs across the trunk.
S1:
S1# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Fa0/1       on           802.1q         trunking      1000

Port        Vlans allowed on trunk
Fa0/1       20,30,40,1000

Port        Vlans allowed and active in management domain
Fa0/1       20,30,40,1000

Port        Vlans in spanning tree forwarding state and not pruned
Fa0/1       20,30,40,1000
S2:
S2# show interfaces trunk
Port        Mode         Encapsulation  Status        Native vlan
Fa0/1       on           802.1q         trunking      1000

Port        Vlans allowed on trunk
Fa0/1       20,30,40,1000

Port        Vlans allowed and active in management domain
Fa0/1       20,30,40,1000

Port        Vlans in spanning tree forwarding state and not pruned
Fa0/1       20,30,40,1000
Step 2: Manually configure S1’s trunk interface F0/5.
a. Configure S1’s interface F0/5 with the same trunk parameters as F0/1. This is the trunk to R1.
S1(config)# interface fastethernet 0/5
S1(config-if)# switchport mode trunk
S1(config-if)# switchport trunk native vlan 1000
S1(config-if)# switchport trunk allowed vlan 20,30,40,1000
b. Save the running configuration to the startup configuration file.
S1# copy running-config startup-config
Part 4: Configure Routing
Step 1: Configure Inter-VLAN Routing on R1.
a. Activate interface G0/0/1 on the router.
R1(config)# interface gigabitethernet 0/0/1
R1(config-if)# no shutdown
b. Configure sub-interfaces for each VLAN as specified in the Addressing Table. All sub-interfaces use 802.1Q encapsulation. Ensure the sub-interface for the Native VLAN does not have an IP address assigned. Include a description for each sub-interface.
R1(config)# interface gigabitethernet 0/0/1.20
R1(config-subif)# description Management Network
R1(config-subif)# encapsulation dot1Q 20
R1(config-subif)# ip address 10.20.0.1 255.255.255.0
R1(config-subif)# interface gigabitethernet 0/0/1.30
R1(config-subif)# encapsulation dot1Q 30
R1(config-subif)# description Operations Network
R1(config-subif)# ip address 10.30.0.1 255.255.255.0
R1(config-subif)# interface gigabitethernet 0/0/1.40
R1(config-subif)# encapsulation dot1Q 40
R1(config-subif)# description Sales Network
R1(config-subif)# ip address 10.40.0.1 255.255.255.0
R1(config-subif)# interface gigabitethernet 0/0/1.1000
R1(config-subif)# encapsulation dot1Q 1000 native
R1(config-subif)# description Native VLAN
c. Configure interface G0/0/0 on R1 with addressing from the Addressing Table.
R1(config)# interface gigabitethernet 0/0/0
R1(config-if)# ip address 172.16.1.1 255.255.255.0
R1(config-if)# no shutdown
d. Use the show ip interface brief command to verify that the sub-interfaces are operational.
R1# show ip interface brief
Interface              IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0/0   172.16.1.1      YES manual up                    up
GigabitEthernet0/0/1   unassigned      YES unset  up                    up
GigabitEthernet0/0/1.2010.20.0.1       YES manual up                    up
GigabitEthernet0/0/1.3010.30.0.1       YES manual up                    up
GigabitEthernet0/0/1.4010.40.0.1       YES manual up                    up
GigabitEthernet0/0/1.1000unassigned      YES unset  up                    up
Step 2: Configure the R2 interface g0/0/1 using the Addressing table and a default route with the next hop 10.20.0.1.
R2(config)# interface gigabitethernet 0/0/1
R2(config-if)# ip address 10.20.0.4 255.255.255.0
R2(config-if)# no shutdown
R2(config)# ip route 0.0.0.0 0.0.0.0 10.20.0.1
Part 5: Configure Remote Access
Step 1: Configure all network devices for basic SSH support.
a. Create a local user with the username SSHadmin and $cisco123! as the encrypted password.
R1:
R1(config)# username SSHadmin secret $cisco123!
R2:
R2(config)# username SSHadmin secret $cisco123!
S1:
S1(config)# username SSHadmin secret $cisco123!
S2:
S2(config)# username SSHadmin secret $cisco123!
b. Use ccna-lab.com as the domain name.
R1:
R1(config)# ip domain name ccna-lab.com
R2:
R2(config)# ip domain name ccna-lab.com
S1:
S1(config)# ip domain name ccna-lab.com
S2:
S2(config)# ip domain name ccna-lab.com
c. Generate crypto keys using a 1024-bit modulus.
R1:
R1(config)# crypto key generate rsa general-keys modulus 1024
R2:
R2(config)# crypto key generate rsa general-keys modulus 1024
S1:
S1(config)# crypto key generate rsa general-keys modulus 1024
S2:
S2(config)# crypto key generate rsa general-keys modulus 1024
d. Configure the first five vty lines on each device to support SSH connections only and to authenticate to the local user database.
R1:
R1(config)# line vty 0 4
R1(config-line)# transport input ssh
R1(config-line)# login local
R2:
R2(config)# line vty 0 4
R2(config-line)# transport input ssh
R2(config-line)# login local
S1:
S1(config)# line vty 0 15
S1(config-line)# transport input ssh
S1(config-line)# login local
S2:
S2(config)# line vty 0 15
S2(config-line)# transport input ssh
S2(config-line)# login local
Part 6: Verify Connectivity
Step 1: Configure PC hosts.
Refer to the Addressing Table for PC host address information.
Step 2: Complete the following tests. All should be successful.
Note: If you click Check Results, you will see that the five highlighted Connectivity Tests show as incorrect. This is because you have not implemented ACLs yet. After ACLs are implemented, these five highlighted Connectivity Tests should successfully fail.
| From | Protocol | Destination | Result |
|---|---|---|---|
| PC-A | Ping | 10.40.0.10 | Success |
| PC-A | Ping | 10.20.0.1 | Success |
| PC-B | Ping | 10.30.0.10 | Success |
| PC-B | Ping | 10.20.0.1 | Success |
| PC-B | Ping | 172.16.1.1 | Success |
| PC-B | HTTPS | 172.16.1.2 | Success |
| PC-A | HTTPS | 172.16.1.2 | Success |
| PC-B | SSH | 10.20.0.4 | Success |
| PC-B | SSH | 172.16.1.1 | Success |
Part 7: Configure and Verify Extended Access Control Lists
When basic connectivity is verified, the company requires the following security policies to be implemented:
Policy 1: The Sales Network is not allowed to SSH to the Management Network (but other SSH is allowed).
Policy 2: The Sales Network is not allowed to access server-A using any web protocol (HTTP/HTTPS). All other web traffic is allowed.
Policy 3: The Sales Network is not allowed to send ICMP echo requests to the Operations or Management Networks. ICMP echo requests to other destinations are allowed.
Policy 4: The Operations network is not allowed to send ICMP echo requests to the Sales Network. ICMP echo requests to other destinations are allowed.
Step 1: Develop and apply extended access lists that will meet the security policy statements.
R1(config)# access-list 101 remark ACL 101 fulfills policies 1, 2, and 3
R1(config)# access-list 101 deny tcp 10.40.0.0 0.0.0.255 10.20.0.0 0.0.0.255 eq 22
R1(config)# access-list 101 deny tcp 10.40.0.0 0.0.0.255 172.16.1.2 0.0.0.0 eq 80
R1(config)# access-list 101 deny tcp 10.40.0.0 0.0.0.255 172.16.1.2 0.0.0.0 eq 443
R1(config)# access-list 101 deny icmp 10.40.0.0 0.0.0.255 10.20.0.0 0.0.0.255 echo
R1(config)# access-list 101 deny icmp 10.40.0.0 0.0.0.255 10.30.0.0 0.0.0.255 echo
R1(config)# access-list 101 permit ip any any
R1(config)# interface gigabitethernet 0/0/1.40
R1(config-subif)# ip access-group 101 in
R1(config)# access-list 102 remark ACL 102 fulfills policy 4
R1(config)# access-list 102 deny icmp 10.30.0.0 0.0.0.255 10.40.0.0 0.0.0.255 echo
R1(config)# access-list 102 permit ip any any
R1(config)# interface gigabitethernet 0/0/1.30
R1(config-subif)# ip access-group 102 in
Step 2: Verify that security policies are being enforced by the deployed access lists.
Run the following tests. The expected results are shown in the table:
Note: Click Check Results to force Packet Tracer to run all the Connectivity Tests again.
| From | Protocol | Destination | Result |
|---|---|---|---|
| PC-A | Ping | 10.40.0.10 | Fail |
| PC-A | Ping | 10.20.0.1 | Success |
| PC-B | Ping | 10.30.0.10 | Fail |
| PC-B | Ping | 10.20.0.1 | Fail |
| PC-B | Ping | 172.16.1.1 | Success |
| PC-B | HTTPS | 172.16.1.2 | Fail |
| PC-A | HTTPS | 172.16.1.2 | Success |
| PC-B | SSH | 10.20.0.4 | Fail |
| PC-B | SSH | 172.16.1.1 | Success |
Device Configs - Final
ROUTER R1
! ==============================================================
!--- 5.5.2 Packet Tracer - Configure and Verify Extended IPv4 ACLs - Physical Mode
!--- ANSWER SCRIPT FOR ROUTER R1
!--- Usage: cable and power on the device, connect the console cable from a PC, and paste this whole file at the Router> prompt (answer no if the router asks to enter the initial configuration dialog). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1, Step 2: Configure basic settings for each router.
! --------------------------------------------------------------

!--- a. Device name.
hostname R1

!--- b. Disable DNS lookup.
no ip domain lookup

!--- c. Privileged EXEC encrypted password: class.
enable secret class

!--- d. Console password cisco and enable login.
line console 0
 password cisco
 login
 exit

!--- e. VTY password cisco (login is enabled in Part 5).
line vty 0 4
 password cisco
 exit

!--- f. Encrypt the plaintext passwords.
service password-encryption

!--- g. Banner that warns unauthorized access is prohibited.
banner motd $ Authorized Users Only! $

! --------------------------------------------------------------
!--- Part 4, Step 1: Configure Inter-VLAN Routing on R1.
! --------------------------------------------------------------

!--- a. Activate G0/0/1 (trunk to S1).
interface gigabitethernet 0/0/1
 no shutdown
 exit

!--- b. Sub-interfaces with 802.1Q and a description; no IP address on the native VLAN.
interface gigabitethernet 0/0/1.20
 description Management Network
 encapsulation dot1Q 20
 ip address 10.20.0.1 255.255.255.0
 exit

interface gigabitethernet 0/0/1.30
 description Operations Network
 encapsulation dot1Q 30
 ip address 10.30.0.1 255.255.255.0
 exit

interface gigabitethernet 0/0/1.40
 description Sales Network
 encapsulation dot1Q 40
 ip address 10.40.0.1 255.255.255.0
 exit

interface gigabitethernet 0/0/1.1000
 description Native VLAN
 encapsulation dot1Q 1000 native
 exit

!--- c. G0/0/0 to Server-A.
interface gigabitethernet 0/0/0
 ip address 172.16.1.1 255.255.255.0
 no shutdown
 exit

! --------------------------------------------------------------
!--- Part 5, Step 1: Configure all network devices for basic SSH support.
! --------------------------------------------------------------

!--- a. Local user SSHadmin with encrypted password $cisco123!.
username SSHadmin secret $cisco123!

!--- b. Domain name ccna-lab.com.
ip domain name ccna-lab.com

!--- c. RSA keys with a 1024-bit modulus.
crypto key generate rsa general-keys modulus 1024

!--- d. First five vty lines: SSH only, local user database.
line vty 0 4
 transport input ssh
 login local
 exit

! --------------------------------------------------------------
!--- Part 7, Step 1: Develop and apply extended access lists.
! --------------------------------------------------------------

!--- ACL 101 (Sales network): policies 1, 2 and 3.
access-list 101 remark ACL 101 fulfills policies 1, 2, and 3
!--- Policy 1: no SSH from Sales to the Management network.
access-list 101 deny tcp 10.40.0.0 0.0.0.255 10.20.0.0 0.0.0.255 eq 22
!--- Policy 2: no HTTP/HTTPS from Sales to Server-A.
access-list 101 deny tcp 10.40.0.0 0.0.0.255 172.16.1.2 0.0.0.0 eq 80
access-list 101 deny tcp 10.40.0.0 0.0.0.255 172.16.1.2 0.0.0.0 eq 443
!--- Policy 3: no ICMP echo from Sales to the Management and Operations networks.
access-list 101 deny icmp 10.40.0.0 0.0.0.255 10.20.0.0 0.0.0.255 echo
access-list 101 deny icmp 10.40.0.0 0.0.0.255 10.30.0.0 0.0.0.255 echo
access-list 101 permit ip any any

!--- Apply ACL 101 inbound on the Sales sub-interface.
interface gigabitethernet 0/0/1.40
 ip access-group 101 in
 exit

!--- ACL 102 (Operations network), policy 4: no ICMP echo to the Sales network.
access-list 102 remark ACL 102 fulfills policy 4
access-list 102 deny icmp 10.30.0.0 0.0.0.255 10.40.0.0 0.0.0.255 echo
access-list 102 permit ip any any

!--- Apply ACL 102 inbound on the Operations sub-interface.
interface gigabitethernet 0/0/1.30
 ip access-group 102 in
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief                           -> G0/0/0 and all G0/0/1 sub-interfaces up/up
!---   show access-lists                                 -> ACL 101 (6 lines) and ACL 102 (2 lines)
!---   PC-B: ping 10.30.0.10 / 10.20.0.1, https and ssh  -> fail (ACL 101); ping and ssh 172.16.1.1 succeed
!---   PC-A: ping 10.40.0.10                             -> fails (ACL 102); ping 10.20.0.1 and https 172.16.1.2 succeed
! ==============================================================
ROUTER R2
! ==============================================================
!--- 5.5.2 Packet Tracer - Configure and Verify Extended IPv4 ACLs - Physical Mode
!--- ANSWER SCRIPT FOR ROUTER R2
!--- Usage: cable and power on the device, connect the console cable from a PC, and paste this whole file at the Router> prompt (answer no if the router asks to enter the initial configuration dialog). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1, Step 2: Configure basic settings for each router.
! --------------------------------------------------------------

!--- a. Device name.
hostname R2

!--- b. Disable DNS lookup.
no ip domain lookup

!--- c. Privileged EXEC encrypted password: class.
enable secret class

!--- d. Console password cisco and enable login.
line console 0
 password cisco
 login
 exit

!--- e. VTY password cisco (login is enabled in Part 5).
line vty 0 4
 password cisco
 exit

!--- f. Encrypt the plaintext passwords.
service password-encryption

!--- g. Banner that warns unauthorized access is prohibited.
banner motd $ Authorized Users Only! $

! --------------------------------------------------------------
!--- Part 4, Step 2: Configure R2 G0/0/1 and a default route.
! --------------------------------------------------------------

!--- G0/0/1: 10.20.0.4/24 (Management VLAN).
interface gigabitethernet 0/0/1
 ip address 10.20.0.4 255.255.255.0
 no shutdown
 exit

!--- Default route with next hop 10.20.0.1.
ip route 0.0.0.0 0.0.0.0 10.20.0.1

! --------------------------------------------------------------
!--- Part 5, Step 1: Configure all network devices for basic SSH support.
! --------------------------------------------------------------

!--- a. Local user SSHadmin with encrypted password $cisco123!.
username SSHadmin secret $cisco123!

!--- b. Domain name ccna-lab.com.
ip domain name ccna-lab.com

!--- c. RSA keys with a 1024-bit modulus.
crypto key generate rsa general-keys modulus 1024

!--- d. First five vty lines: SSH only, local user database.
line vty 0 4
 transport input ssh
 login local
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip route   -> S* 0.0.0.0/0 [1/0] via 10.20.0.1
!---   ping 10.20.0.1  -> succeeds
! ==============================================================
SWITCH S1
! ==============================================================
!--- 5.5.2 Packet Tracer - Configure and Verify Extended IPv4 ACLs - Physical Mode
!--- ANSWER SCRIPT FOR SWITCH S1
!--- Usage: cable and power on the device, connect the console cable from a PC, and paste this whole file at the Switch> prompt. Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1, Step 3: Configure basic settings for each switch.
! --------------------------------------------------------------

!--- a. Device name.
hostname S1

!--- b. Disable DNS lookup.
no ip domain-lookup

!--- c. Privileged EXEC encrypted password: class.
enable secret class

!--- d. Console password cisco and enable login.
line console 0
 password cisco
 login
 exit

!--- e. VTY password cisco (login is enabled in Part 5).
line vty 0 15
 password cisco
 exit

!--- f. Encrypt the plaintext passwords.
service password-encryption

!--- g. Banner that warns unauthorized access is prohibited.
banner motd $ Authorized Users Only! $

! --------------------------------------------------------------
!--- Part 2, Step 1: Create VLANs on both switches.
! --------------------------------------------------------------

!--- a. VLANs from the VLAN table.
vlan 20
 name Management
 exit
vlan 30
 name Operations
 exit
vlan 40
 name Sales
 exit
vlan 999
 name ParkingLot
 exit
vlan 1000
 name Native
 exit

!--- b. Management interface VLAN 20 and default gateway.
interface vlan 20
 ip address 10.20.0.2 255.255.255.0
 no shutdown
 exit
ip default-gateway 10.20.0.1

!--- c. Unused ports: Parking Lot VLAN 999, static access, shut down.
interface range fastethernet 0/2 - 4, fastethernet 0/7 - 24, gigabitethernet 0/1 - 2
 switchport mode access
 switchport access vlan 999
 shutdown
 exit

! --------------------------------------------------------------
!--- Part 2, Step 2: Assign VLANs to the correct switch interfaces.
! --------------------------------------------------------------

!--- a. F0/6 (PC-A): access port in VLAN 30.
interface fastethernet 0/6
 switchport mode access
 switchport access vlan 30
 exit

! --------------------------------------------------------------
!--- Part 3: Configure Trunking.
! --------------------------------------------------------------

!--- Step 1. F0/1 trunk: native VLAN 1000, allowed VLANs 20, 30, 40 and 1000.
interface fastethernet 0/1
 switchport mode trunk
 switchport trunk native vlan 1000
 switchport trunk allowed vlan 20,30,40,1000
 exit

!--- Step 2. F0/5 trunk to R1 with the same parameters.
interface fastethernet 0/5
 switchport mode trunk
 switchport trunk native vlan 1000
 switchport trunk allowed vlan 20,30,40,1000
 exit

! --------------------------------------------------------------
!--- Part 5, Step 1: Configure all network devices for basic SSH support.
! --------------------------------------------------------------

!--- a. Local user SSHadmin with encrypted password $cisco123!.
username SSHadmin secret $cisco123!

!--- b. Domain name ccna-lab.com.
ip domain name ccna-lab.com

!--- c. RSA keys with a 1024-bit modulus.
crypto key generate rsa general-keys modulus 1024

!--- d. VTY lines 0-15: SSH only, local user database.
line vty 0 15
 transport input ssh
 login local
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show vlan brief        -> Fa0/6 in VLAN 30, unused ports in VLAN 999
!---   show interfaces trunk  -> Fa0/1 and Fa0/5 trunking, native 1000, allowed 20,30,40,1000
! ==============================================================
SWITCH S2
! ==============================================================
!--- 5.5.2 Packet Tracer - Configure and Verify Extended IPv4 ACLs - Physical Mode
!--- ANSWER SCRIPT FOR SWITCH S2
!--- Usage: cable and power on the device, connect the console cable from a PC, and paste this whole file at the Switch> prompt. Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 1, Step 3: Configure basic settings for each switch.
! --------------------------------------------------------------

!--- a. Device name.
hostname S2

!--- b. Disable DNS lookup.
no ip domain-lookup

!--- c. Privileged EXEC encrypted password: class.
enable secret class

!--- d. Console password cisco and enable login.
line console 0
 password cisco
 login
 exit

!--- e. VTY password cisco (login is enabled in Part 5).
line vty 0 15
 password cisco
 exit

!--- f. Encrypt the plaintext passwords.
service password-encryption

!--- g. Banner that warns unauthorized access is prohibited.
banner motd $ Authorized Users Only! $

! --------------------------------------------------------------
!--- Part 2, Step 1: Create VLANs on both switches.
! --------------------------------------------------------------

!--- a. VLANs from the VLAN table.
vlan 20
 name Management
 exit
vlan 30
 name Operations
 exit
vlan 40
 name Sales
 exit
vlan 999
 name ParkingLot
 exit
vlan 1000
 name Native
 exit

!--- b. Management interface VLAN 20 and default gateway.
interface vlan 20
 ip address 10.20.0.3 255.255.255.0
 no shutdown
 exit
ip default-gateway 10.20.0.1

!--- c. Unused ports: Parking Lot VLAN 999, static access, shut down.
interface range fastethernet 0/2 - 4, fastethernet 0/6 - 17, fastethernet 0/19 - 24, gigabitethernet 0/1 - 2
 switchport mode access
 switchport access vlan 999
 shutdown
 exit

! --------------------------------------------------------------
!--- Part 2, Step 2: Assign VLANs to the correct switch interfaces.
! --------------------------------------------------------------

!--- a. F0/5 (R2): access port in VLAN 20; F0/18 (PC-B): access port in VLAN 40.
interface fastethernet 0/5
 switchport mode access
 switchport access vlan 20
 exit
interface fastethernet 0/18
 switchport mode access
 switchport access vlan 40
 exit

! --------------------------------------------------------------
!--- Part 3: Configure Trunking.
! --------------------------------------------------------------

!--- Step 1. F0/1 trunk: native VLAN 1000, allowed VLANs 20, 30, 40 and 1000.
interface fastethernet 0/1
 switchport mode trunk
 switchport trunk native vlan 1000
 switchport trunk allowed vlan 20,30,40,1000
 exit

! --------------------------------------------------------------
!--- Part 5, Step 1: Configure all network devices for basic SSH support.
! --------------------------------------------------------------

!--- a. Local user SSHadmin with encrypted password $cisco123!.
username SSHadmin secret $cisco123!

!--- b. Domain name ccna-lab.com.
ip domain name ccna-lab.com

!--- c. RSA keys with a 1024-bit modulus.
crypto key generate rsa general-keys modulus 1024

!--- d. VTY lines 0-15: SSH only, local user database.
line vty 0 15
 transport input ssh
 login local
 exit

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show vlan brief        -> Fa0/5 in VLAN 20, Fa0/18 in VLAN 40, unused ports in VLAN 999
!---   show interfaces trunk  -> Fa0/1 trunking, native 1000, allowed 20,30,40,1000
! ==============================================================


