
1.6.1 Packet Tracer - Implement a Small Network (Instructor Version)
Instructor Note: Red font color or gray highlights indicate text that appears in the instructor copy only.
This activity requires some knowledge of how to build topologies in Packet Tracer. You may want to quickly train students on how to do the following:
- Select specific device models and drag devices to the work area, specifically 1941 routers and 2960 switches.
- Select an Ethernet-straight through cable.
- Connect devices with a Copper straight-through cable to specific device ports.
- Change device display names by clicking on the device name in the topology and typing a new name. Whenever this is done, the device name is required to match the device name in the instructions exactly.
Addressing Table
| Device | Interface | Address | Subnet Mask | Default Gateway |
|---|---|---|---|---|
| RTA | G0/0 | 10.10.10.1 | 255.255.255.0 | N/A |
| G0/1 | 10.10.20.1 | 255.255.255.0 | N/A | |
| SW1 | VLAN1 | 10.10.10.2 | 255.255.255.0 | 10.10.10.1 |
| SW2 | VLAN1 | 10.10.20.2 | 255.255.255.0 | 10.10.20.1 |
| PC-1 | NIC | Any available address in network | 255.255.255.0 | 10.10.10.1 |
| PC-2 | NIC | Any available address in network | 255.255.255.0 | 10.10.20.1 |
Objectives
- Part 1: Create the Network Topology
- Part 2: Configure Devices and Verify Connectivity
Instructions
Part 1: Create the Network Topology
Step 1: Obtain the required devices.
a. Click the Network Devices icon in the bottom tool bar.
b. Click the router icon in the submenu.
c. Locate the 1941 router icon. Click and drag the icon for the 1941 router into the topology area.
d. Click the switch entry in the submenu.
e. Locate the 2960 switch icon. Click and drag the icon for the 2960 switch into the topology area.
f. Repeat the step above so that there are two 2960 switches in the topology area.
g. Click the End Devices icon.
h. Locate the PC icon. Drag two PCs to the topology area.
i. Arrange the devices into a layout that you can work with by clicking and dragging.
Step 2: Name the devices.
The devices have default names that you will need to change. You will name the devices as shown in the Addressing Table. You are changing the display names of the devices. This is the text label that appears below each device. Your display names must match the information in the Addressing Table exactly. If a display name does not match, you will not be scored for your device configuration.
a. Click the device display name that is below the device icon. A text field should appear with a flashing insertion point. If the configuration window for the device appears, close it and try again, clicking a little further away from the device icon.
b. Replace the current display name with the appropriate display name from the Addressing Table.
c. Repeat until all devices are named.
Step 3: Connect the devices.
a. Click the orange lightning bolt connections icon in the bottom toolbar.
b. Locate the Copper Straight-Through cable icon. It looks like a solid black diagonal line.
c. To connect the device, click the Copper Straight-Through cable icon and then click the first device that you want to connect. Select the correct port and then click the second device. Select the correct port and the devices will be connected.
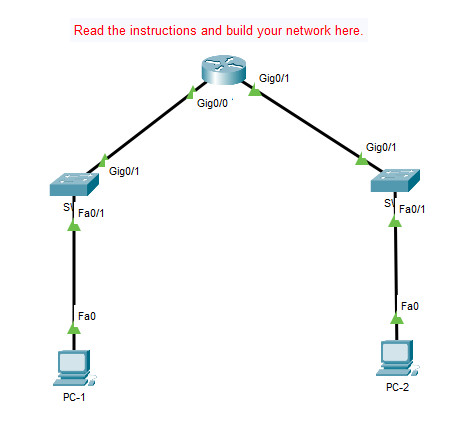
d. Connect the devices as specified in the table below.
| From Device | Port | To Device | Port |
|---|---|---|---|
| RTA | G0/0 | SW1 | G0/1 |
| G0/1 | SW2 | G0/1 | |
| SW1 | F0/1 | PC-1 | Fastethernet0 |
| SW2 | F0/1 | PC-2 | Fastethernet0 |
Part 2: Configure Devices
Record the PC addressing and gateway addresses in the addressing table. You can use any available address in the network for PC-1 and PC-2.
Step 1: Configure the router.
a. Configure basic settings.
- Hostname as shown in the Addressing Table.
- Configure Ciscoenpa55 as the encrypted password.
- Configure Ciscolinepa55 as the password on the lines.
- All lines should accept connections.
- Configure an appropriate message of the day banner.
Router>enable
Router#config terminal

Router(config)#hostname RTA

RTA(config)#enable secret Ciscoenpa55

RTA(config)#line console 0
RTA(config-line)#password Ciscolinepa55
RTA(config-line)#login
RTA(config-line)#exit

RTA(config)#line vty 0 4
RTA(config-line)#password Ciscolinepa55
RTA(config-line)#login
RTA(config-line)#exit

RTA(config)#banner motd $Unauthorized Access is Prohibited$
b. Configure interface settings.
- Addressing.
- Descriptions on the interfaces.
- Save your configuration.
RTA(config)#interface g0/0
RTA(config-if)#ip address 10.10.10.1 255.255.255.0
RTA(config-if)#description Connected to SW1 port G0/1
RTA(config-if)#no shutdown
RTA(config-if)#exit

RTA(config)#interface g0/1
RTA(config-if)#ip address 10.10.20.1 255.255.255.0
RTA(config-if)#description Connected to SW2 port G0/1
RTA(config-if)#no shutdown
RTA(config-if)#end

RTA#copy running-config startup-config
Step 2: Configure switch SW1 and SW2.
a. Configure the default management interface so that it will accept connections over the network from local and remote hosts. Use the values in the addressing table.
b. Configure an encrypted password using the value in step 1a above.
c. Configure all lines to accept connections using the password from step 1a above.
d. Configure the switches so that they can send data to hosts on remote networks.
e. Save your configuration.
Step 3: Configure the hosts.
Configure addressing on the hosts. If your configurations are complete, you should be able to ping all devices in the topology.
Device Configs - Final
ROUTER RTA
! ==============================================================
!--- 1.6.1 Packet Tracer - Implement a Small Network
!--- ANSWER SCRIPT FOR ROUTER RTA
!--- Usage: copy this whole file and paste it into the ROUTER RTA terminal (start at the Router> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- IMPORTANT: set the device DISPLAY NAME in the topology to match the Addressing Table exactly, or Packet Tracer will not score the device.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2, Step 1a: Basic settings
! --------------------------------------------------------------

!--- Hostname as shown in the Addressing Table.
hostname RTA

!--- Encrypted privileged EXEC password: Ciscoenpa55. "enable secret" stores the password as an MD5 hash, so it is encrypted by design.
enable secret Ciscoenpa55

!--- Console line: password Ciscolinepa55 and accept connections.
line console 0
 password Ciscolinepa55
 login
 exit

!--- VTY lines: password Ciscolinepa55 and accept connections. A 1941 router has vty 0 4 by default, so this covers all of its lines.
line vty 0 4
 password Ciscolinepa55
 login
 exit

!--- Message of the day banner warning against unauthorized access.
banner motd $Unauthorized Access is Prohibited$

! --------------------------------------------------------------
!--- Part 2, Step 1b: Interface settings (addressing + descriptions)
! --------------------------------------------------------------

!--- G0/0 - LAN toward SW1. The description is corrected: the connection table says this link lands on SW1 port G0/1 (the instructor config says 'G1/1', a port that does not exist on a 2960).
interface g0/0
 description Connected to SW1 port G0/1
 ip address 10.10.10.1 255.255.255.0
 no shutdown
 exit

!--- G0/1 - LAN toward SW2, same correction applied.
interface g0/1
 description Connected to SW2 port G0/1
 ip address 10.10.20.1 255.255.255.0
 no shutdown
 exit

end

! --------------------------------------------------------------
!--- Part 2, Step 1b3: Save the configuration. (Press Enter when prompted.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief  -> G0/0 and G0/1 up/up
!---   show ip route            -> both connected LANs
! ==============================================================
SWITCH SW1
! ==============================================================
!--- 1.6.1 Packet Tracer - Implement a Small Network
!--- ANSWER SCRIPT FOR SWITCH SW1
!--- Usage: copy this whole file and paste it into the SWITCH SW1 terminal (start at the Switch> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- IMPORTANT: set the device DISPLAY NAME in the topology to match the Addressing Table exactly, or Packet Tracer will not score the device.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2, Step 2: Configure switch SW1
! --------------------------------------------------------------

!--- Hostname as shown in the Addressing Table.
hostname SW1

!--- Step 2a: default management interface (VLAN 1) so the switch accepts connections from local AND remote hosts.
interface vlan 1
 ip address 10.10.10.2 255.255.255.0
 no shutdown
 exit

!--- Step 2d: default gateway (RTA G0/0) - this is what lets the switch send data to hosts on REMOTE networks.
ip default-gateway 10.10.10.1

!--- Step 2b: encrypted privileged EXEC password.
enable secret Ciscoenpa55

!--- Step 2c: ALL lines accept connections with the password Ciscolinepa55. A 2960 has vty 0 15, so all sixteen lines must be covered - the instructor config leaves vty 5-15 without a password (SW2) or omits them entirely (SW1), which makes those lines refuse connections.
line console 0
 password Ciscolinepa55
 login
 exit
line vty 0 15
 password Ciscolinepa55
 login
 exit

!--- Message of the day banner (not required by the switch steps, but included for consistency with RTA).
banner motd $Unauthorized Access is Prohibited$

end

! --------------------------------------------------------------
!--- Step 2e: Save the configuration. (Press Enter when prompted.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief  -> VLAN 1 up/up with 10.10.10.2
!---   ping 10.10.10.1          -> reach the default gateway
! ==============================================================
SWITCH SW2
! ==============================================================
!--- 1.6.1 Packet Tracer - Implement a Small Network
!--- ANSWER SCRIPT FOR SWITCH SW2
!--- Usage: copy this whole file and paste it into the SWITCH SW2 terminal (start at the Switch> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- IMPORTANT: set the device DISPLAY NAME in the topology to match the Addressing Table exactly, or Packet Tracer will not score the device.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2, Step 2: Configure switch SW2
! --------------------------------------------------------------

!--- Hostname as shown in the Addressing Table.
hostname SW2

!--- Step 2a: default management interface (VLAN 1) so the switch accepts connections from local AND remote hosts.
interface vlan 1
 ip address 10.10.20.2 255.255.255.0
 no shutdown
 exit

!--- Step 2d: default gateway (RTA G0/1) - this is what lets the switch send data to hosts on REMOTE networks.
ip default-gateway 10.10.20.1

!--- Step 2b: encrypted privileged EXEC password.
enable secret Ciscoenpa55

!--- Step 2c: ALL lines accept connections with the password Ciscolinepa55. A 2960 has vty 0 15, so all sixteen lines must be covered - the instructor config leaves vty 5-15 without a password (SW2) or omits them entirely (SW1), which makes those lines refuse connections.
line console 0
 password Ciscolinepa55
 login
 exit
line vty 0 15
 password Ciscolinepa55
 login
 exit

!--- Message of the day banner (not required by the switch steps, but included for consistency with RTA).
banner motd $Unauthorized Access is Prohibited$

end

! --------------------------------------------------------------
!--- Step 2e: Save the configuration. (Press Enter when prompted.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief  -> VLAN 1 up/up with 10.10.20.2
!---   ping 10.10.20.1          -> reach the default gateway
! ==============================================================


