Month: June 2019
Objectives Part 1: Creating Hashes with OpenSSL Part 2: Verifying Hashes Background / Scenario Hash functions are mathematical algorithms designed to take data as input and generate a fixed-size, unique string of characters, also known as the hash. Designed to be fast, hash functions are very hard to …
Objectives Part 1: Examine a Telnet Session with Wireshark Part 2: Examine an SSH Session with Wireshark Background / Scenario In this lab, you will configure a router to accept SSH connectivity and use Wireshark to capture and view Telnet and SSH sessions. This will demonstrate the importance …
Objectives Part 1: Create and Encrypt Files Part 2: Recover Encrypted Zip File Passwords Background / Scenario What if you work for a large corporation that had a corporate policy regarding removable media? Specifically, it states that only encrypted zipped documents can be copied to portable USB flash …
Objectives Part 1: Encrypting Messages with OpenSSL Part 2: Decrypting Messages with OpenSSL Background / Scenario OpenSSL is an open source project that provides a robust, commercial-grade, and full-featured toolkit for the Transport Layer Security (TLS) and Secure Sockets Layer (SSL) protocols. It is also a general-purpose cryptography …
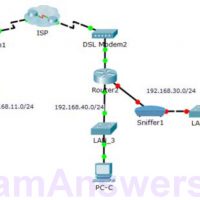
Topology Addressing Table Device Private IP Address Public IP Address FTP_Server 192.168.30.253 209.165.200.227 SYSLOG_SERVER 192.168.11.254 209.165.200.229 Router2 N/A 209.165.200.226 Objectives Part 1: Create FTP traffic. Part 2: Investigate the FTP Traffic Part 3: View Syslog Messages Background In this activity, you will use Packet Tracer to sniff and …
Objectives Part 1: Reading Log Files with Cat, More, and Less Part 2: Log Files and Syslog Part 3: Log Files and Journalctl Background / Scenario Log files are an important tool for troubleshooting and monitoring. Different application generates different log files, each one containing its own set …
Objectives In this lab, you will view a PCAP file from a previous attack against a SQL database. Background / Scenario SQL injection attacks allow malicious hackers to type SQL statements in a web site and receive a response from the database. This allows attackers to tamper with …
Objectives Part 1: Capture DNS Traffic Part 2: Explore DNS Query Traffic Part 3: Explore DNS Response Traffic Background / Scenario Wireshark is an open source packet capture and analysis tool. Wireshark gives a detailed breakdown of the network protocol stack. Wireshark allows you to filter traffic for …
Objectives Identify the processes running on a computer, the protocol they are using, and their local and remote port addresses. Background / Scenario For a hacker to establish a connection to a remote computer, a port must be listening on that device. This may be due to infection …
Objectives Research and identify social engineering attacks Background / Scenario Social engineering is an attack with the goal of getting a victim to enter personal or sensitive information, this type of attack can be performed by an attacker utilizing a keylogger, phishing email, or an in-person method. This …