Month: July 2019
Objectives Apply your knowledge of security incident handling procedures to formulate questions about given incident scenarios. Background / Scenario Computer security incident response has become a vital part of any organization. The process for handling a security incident can be complicated and involve many different groups. An organization …
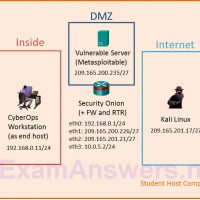
Topology Objectives In this lab, you will review logs during an exploitation of a documented vulnerability to determine the compromised hosts and file. Part 1: Prepare the Virtual Environment Part 2: Reconnaissance Part 3: Exploitation Part 4: Infiltration Part 5: Review the Logs Background / Scenario The 5-tuple …
Topology Objectives In this lab, you will review logs during an exploitation of documented HTTP and DNS vulnerabilities. Part 1: Prepare the Virtual Environment Part 2: Investigate an SQL Injection Attack Part 3: Data Exfiltration Using DNS Background / Scenario MySQL is a popular database used by numerous …
Objectives Part 1: Prepare the Virtual Environment Part 2: Analyze Pre-Captured Logs and Traffic Captures Background / Scenario Looking at logs is very important but it is also important to understand how network transactions happen at the packet level. In this lab, you will analyze the traffic in …
Objectives In this lab, you will learn how to use regular expressions to search for desired strings of information. Background / Scenario A regular expression (regex) is a pattern of symbols that describes data to be matched in a query or other operation. Regular expressions are constructed similarly …
Objectives Part 1: Normalize Timestamps in a Log File Part 2: Normalize Timestamps in an Apache Log File Part 3: Log File Preparation in Security Onion Background / Scenario This lab will prepare students to learn where log files are located and how to manipulate and view log …
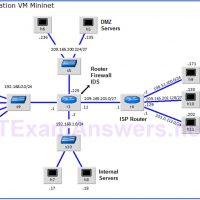
Topology Objectives Part 1: Preparing the Virtual Environment Part 2: Firewall and IDS Logs Part 3: Terminate and Clear Mininet Process Background / Scenario In a secure production network, network alerts are generated by various types of devices such as security appliances, firewalls, IPS devices, routers, switches, servers, …
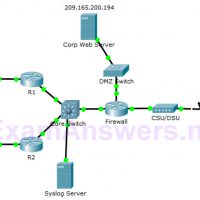
Topology Objectives Part 1: Use syslog to capture log files from multiple network devices Part 2: Observe AAA user access logging Part 3: Observe NetFlow information Background / Scenario In this activity, you will use Packet Tracer to view network data generated by syslog, AAA, and NetFlow. Part …
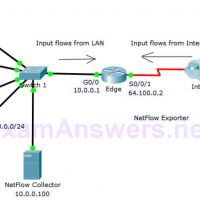
Topology Objectives Part 1: Observe NetFlow Flow Records - One Direction Part 2: Observe NetFlow Records for a Session that Enters and Leaves the Collector Background In this activity, you will use Packet Tracer to create network traffic and observe the corresponding NetFlow flow records in a NetFlow …
Topology Objectives In this lab, you will set up a virtual network environment by connecting multiple virtual machines in Virtualbox. Background / Scenario A virtual network security sandbox or multi-VM lab environment is useful for security analysis and testing. This multi-VM environment is a requirement for more advanced …