
Endpoint Security: My Knowledge Check Answers
1. Which Windows version was the first to introduce a 64-bit Windows operating system?
- Windows NT
- Windows XP
- Windows 7
- Windows 10
2. Employees in an organization report that the network access is slow. Further investigation reveals that one employee downloaded a third-party scanning program for the printer. What type of malware may have been introduced?
- Worm
- Trojan horse
- Spam
- Phishing
3. Which two options are window managers for Linux? (Choose two.)
- File Explorer
- Gnome
- Kali
- KDE
- PenTesting
4. On a Windows host, which tool can be used to create and maintain block lists and allow lists?
- Task Manager
- Group Policy Editor
- Computer Management
- Local Users and Groups
5. Users in a company have complained about network performance. After investigation, the IT staff has determined that an attacker has used a specific technique that affects the TCP three-way handshake. What is the name of this type of network attack?
- SYN flood
- DDoS
- DNS poisoning
- session hijacking
6. Which parameter is commonly used to identify a wireless network name when a home wireless AP is being configured?
- ad hoc
- BESS
- ESS
- SSID
7. What would be the target of an SQL injection attack?
- database
- DHCP
- DNS
8. Which of the following are foundational principles of the cybersecurity domain? (Choose three.)
- Security
- Integrity
- Policy
- Encryption
- Availability
- Confidentiality
9. A social media site is describing a security breach in a sensitive branch of a national bank. In the post, it refers to a vulnerability. What statement describes that term?
- The potential damage to the organization that is caused by the threat.
- The actions that are taken to protect assets by mitigating a threat or reducing risk.
- The likelihood that a particular threat will exploit a vulnerability of an asset and result in an undesirable consequence.
- A weakness in a system or its design that could be exploited by a threat.
10. Why is Kali Linux a popular choice in testing the network security of an organization?
- It is an open source Linux security distribution containing many penetration tools.
- It can be used to intercept and log network traffic.
- It can be used to test weaknesses by using only malicious software.
- It is a network scanning tool that prioritizes security risks.
11. What type of attack targets an SQL database using the input field of a user?
- XML injection
- Cross-site scripting
- SQL injection
- buffer overflow
12. A security specialist is asked for advice on a security measure to prevent unauthorized hosts from accessing the home network of employees. Which measure would be most effective?
- Implement intrusion detection systems.
- Implement a firewall.
- Implement a VLAN.
- Implement RAID.
13. Refer to the exhibit. An IT security manager is planning security updates on this particular network. Which type of network is displayed in the exhibit and is being considered for updates?
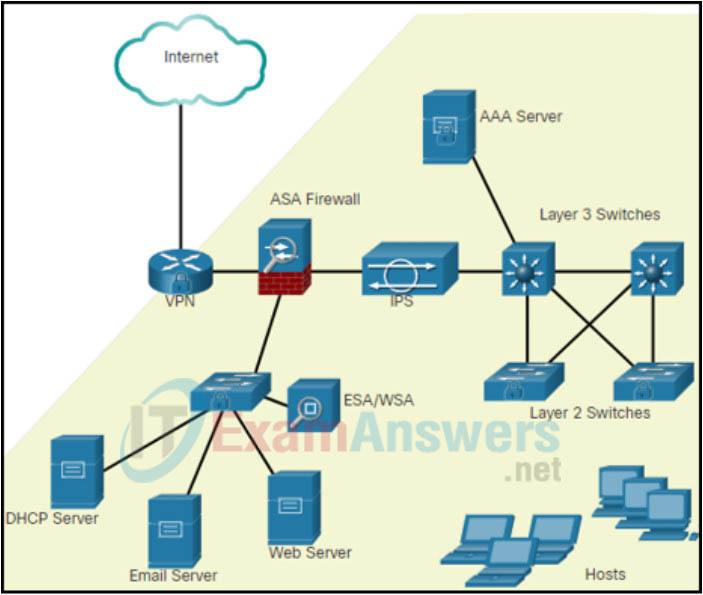
- WAN
- CAN
- data center
- SOHO
14. Which two commands could be used to check if DNS name resolution is working properly on a Windows PC? (Choose two.)
- nslookup cisco.com
- net cisco.com
- ping cisco.com
- nbtstat cisco.com
- ipconfig /flushdns
15. What are three benefits of using symbolic links over hard links in Linux? (Choose three.)
- Symbolic links can be exported.
- They can be encrypted.
- They can be compressed.
- They can link to a directory.
- They can show the location of the original file.
- They can link to a file in a different file system.
16. Match the Apple system security feature to its purpose.
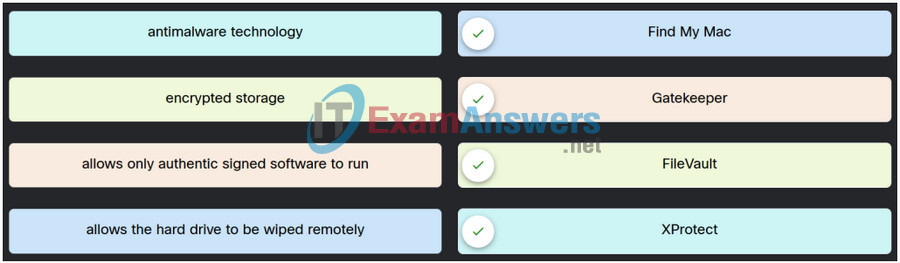
17. A cyber criminal sends a series of maliciously formatted packets to the database server. The server cannot parse the packets and the event causes the server to crash. What is the type of attack the cyber criminal launches?
- packet Injection
- SQL injection
- DoS
- man-in-the-middle
18. Which field in the IPv4 header is used to prevent a packet from traversing a network endlessly?
- Time-to-Live
- Sequence Number
- Acknowledgment Number
- Differentiated Services
19. What is required in order to connect a Wi-Fi enabled laptop to a WPA secured wireless network?
- a security encryption key
- a MAC address
- a username and password
- an updated wireless driver
20. Which network service allows administrators to monitor and manage network devices?
- NTP
- SNMP
- syslog
- NetFlow
21. When considering network security, what is the most valuable asset of an organization?
- customers
- data
- financial resources
- personnel
22. What is the primary means for mitigating virus and Trojan horse attacks?
- antivirus software
- encryption
- antisniffer software
- blocking ICMP echo and echo-replies
23. Which language is used to query a relational database?
- Python
- C++
- Java
- SQL
24. What does the term vulnerability mean?
- a weakness that makes a target susceptible to an attack
- a computer that contains sensitive information
- a method of attack to exploit a target
- a known target or victim machine
- a potential threat that a hacker creates
25. What is an IPS signature?
- It is the timestamp that is applied to logged security events and alarms.
- It is the authorization that is required to implement a security policy.
- It is a set of rules used to detect typical intrusive activity.
- It is a security script that is used to detect unknown threats.
26. Why would a rootkit be used by a hacker?
- to do reconnaissance
- to try to guess a password
- to gain access to a device without being detected
- to reverse engineer binary files
27. Which Windows tool can be used by a cybersecurity administrator to secure stand-alone computers that are not part of an active directory domain?
- Local Security Policy
- Windows Defender
- Windows Firewall
- PowerShell
28. Which file system is the primary file system used by Apple in current Macintosh computers?
- ext2
- ext3
- CDFS
- HFS
- APFS
29. Which device in a LAN infrastructure is susceptible to MAC address-table overflow and spoofing attacks?
- server
- switch
- workstation
- firewall
30. At a local college, students are allowed to connect to the wireless network without using a password. Which mode is the access point using?
- network
- open
- passive
- shared-key
31. What is the term used when a malicious party sends a fraudulent email disguised as being from a legitimate, trusted source?
- phishing
- vishing
- backdoor
- trojan
32. Which term describes a field in the IPv4 packet header used to detect corruption in the IPv4 header?
- header checksum
- version
- destination IPv4 address
- protocol
33. What is a nontechnical method that a cybercriminal would use to gather sensitive information from an organization?
- man-in-the-middle
- ransomeware
- social engineering
- pharming
34. Match the type of cyberattackers to the description. (Not all options are used.)
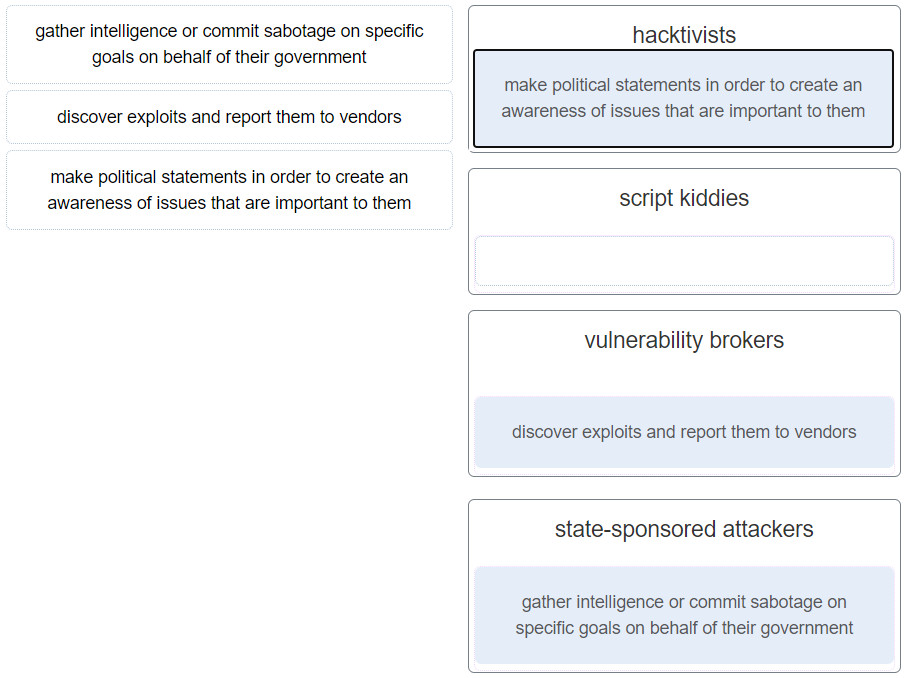
35. What is the purpose of a personal firewall on a computer?
- to protect the hardware against fire hazard
- to filter the traffic that is moving in and out of the PC
- to protect the computer from viruses and malware
- to increase the speed of the Internet connection
36. What technology was created to replace the BIOS program on modern personal computer motherboards?
- UEFI
- RAM
- CMOS
- MBR
37. Which protocol provides authentication, integrity, and confidentiality services and is a type of VPN?
- AES
- ESP
- IPsec
- MD5
38. A new PC is taken out of the box, started up and connected to the Internet. Patches were downloaded and installed. Antivirus was updated. In order to further harden the operating system what can be done?
- Turn off the firewall.
- Remove the administrator account.
- Remove unnecessary programs and services.
- Install a hardware firewall.
- Give the computer a nonroutable address.
39. A cybercriminal sends a series of maliciously formatted packets to a database server, which causes the server to crash. What do you call this type of attack?
- Packet injection
- SQL injection
- DoS
- Man-in-the-middle
40. Which Linux command can be used to display the name of the current working directory?
- ps
- pwd
- chmod
- sudo
41. A user creates a file with .ps1 extension in Windows. What type of file is it?
- PowerShell script
- PowerShell cmdlet
- PowerShell function
- PowerShell documentation
42. What principle prevents the disclosure of information to unauthorized people, resources, and processes?
- confidentiality
- integrity
- availability
- nonrepudiation
- accounting
43. What is a daemon?
- a background process that runs without the need for user interaction
- a record to keep track of important events
- a type of security attack
- an application that monitors and analyzes suspicious activity
44. Which technology is used to secure, monitor, and manage mobile devices?
- MDM
- VPN
- rootkit
- ASA firewall
45. What kind of ICMP message can be used by threat actors to map an internal IP network?
- ICMP echo request
- ICMP router discovery
- ICMP mask reply
- ICMP redirects
46. Match typical Linux log files to the function.
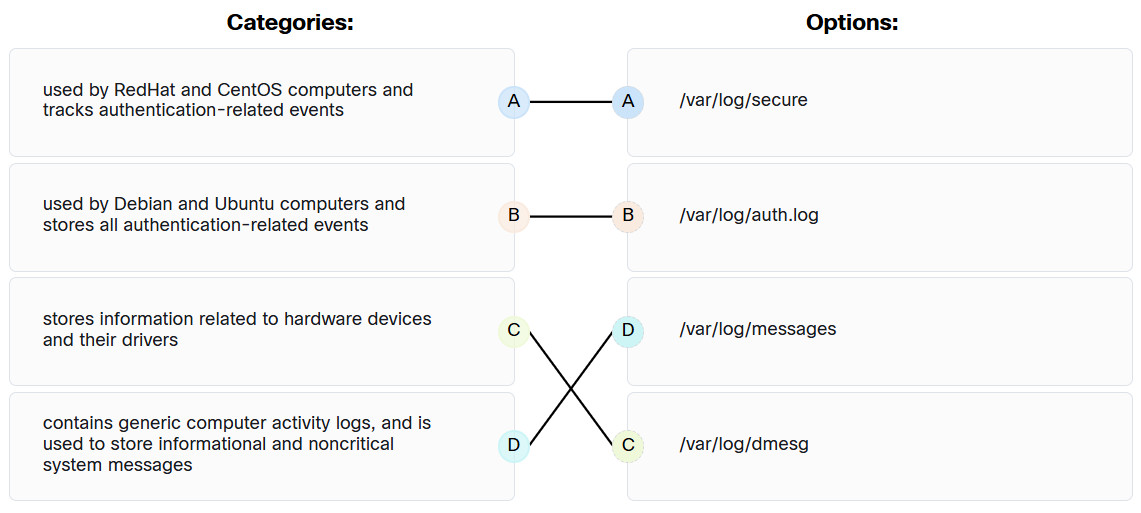
47. Which statement describes the term iptables?
- It is a DNS daemon in Linux.
- It is a DHCP application in Windows.
- It is a rule-based firewall application in Linux.
- It is a file used by a DHCP server to store current active IP addresses.
48. Which wireless encryption method is the most secure?
- WPA
- WEP
- WPA2 with TKIP
- WPA2 with AES
49. Which statement describes the term attack surface?
- It is the network interface where attacks originate.
- It is the group of hosts that experiences the same attack.
- It is the total number of attacks toward an organization within a day.
- It is the total sum of vulnerabilities in a system that is accessible to an attacker.
50. A secretary receives a phone call from someone claiming that their manager is about to give an important presentation but the presentation files are corrupted. The caller sternly asks that the secretary email the presentation right away to a personal email address. The caller also states that the secretary is being held personally responsible for the success of this presentation. What type of social engineering tactic is the caller using?
- Trusted partners
- Familiarity
- Intimidation
- Urgency
51. How much RAM is addressable by a 32-bit version of Windows?
- 4 GB
- 8 GB
- 16 GB
- 32 GB
52. A threat actor uses a program to launch an attack by sending a flood of UDP packets to a server on the network. The program sweeps through all of the known ports trying to find closed ports. It causes the server to reply with an ICMP port unreachable message and is similar to a DoS attack. Which two programs could be used by the threat actor to launch the attack? (Choose two.)
- ping
- Smurf
- WireShark
- UDP Unicorn
- Low Orbit Ion Cannon
53. Which antimalware software approach can recognize various characteristics of known malware files to detect a threat?
- routing-based
- behavior-based
- signature-based
- heuristics-based
54. Which wireless parameter refers to the frequency bands used to transmit data to a wireless access point?
- SSID
- channel settings
- security mode
- scanning mode
55. What is the motivation of a white hat attacker?
- taking advantage of any vulnerability for illegal personal gain
- fine tuning network devices to improve their performance and efficiency
- studying operating systems of various platforms to develop a new system
- discovering weaknesses of networks and systems to improve the security level of these systems
56. What is the reason for disabling SSID broadcasting and changing the default SSID on a wireless access point?
- Anyone with the default SSID can gain access to the access point and change the configuration.
- Disabling SSID broadcasting frees up radio frequency bandwidth and increases the data throughput of the access point.
- The access point stops broadcasting its own MAC address, thus preventing unauthorized wireless clients from connecting to the network.
- Wireless clients must then have the SSID manually configured to connect to the wireless network.
57. Which statement describes a VPN?
- VPNs use dedicated physical connections to transfer data between remote users.
- VPNs use logical connections to create public networks through the Internet.
- VPNs use open source virtualization software to create the tunnel through the Internet.
- VPNs use virtual connections to create a private network through a public network.
58. Consider the result of the ls -l command in the Linux output below. What are the file permissions assigned to the sales user for the analyst.txt file?
ls –l analyst.txt
-rwxrw-r-- sales staff 1028 May 28 15:50 analyst.txt
- write only
- read, write, execute
- read, write
- read only
59. In Windows Firewall, when is the Domain profile applied?
- when the host accesses the Internet
- when the host checks emails from an enterprise email server
- when the host is connected to a trusted network such as an internal business network
- when the host is connected to an isolated network from the Internet by another security device
60. What are three states of data during which data is vulnerable? (Choose three.)
- stored data
- purged data
- data in-transit
- data encrypted
- data decrypted
- data in-process
61. What does a rootkit modify?
- operating system
- programs
- screen savers
- notepad
- microsoft Word
62. Which security technology is commonly used by a teleworker when accessing resources on the main corporate office network?
- IPS
- VPN
- SecureX
- biometric access
63. Which of the following statements describes a distributed denial of service (DDoS) attack?
- An attacker sends an enormous quantity of data that a server cannot handle
- An attacker monitors network traffic to learn authentication credentials
- One computer accepts data packets based on the MAC address of another computer
- A botnet of zombies, coordinated by an attacker, overwhelms a server with DoS attacks
64. Match the network-based anti-malware solution to the function. (Not all options are used.)
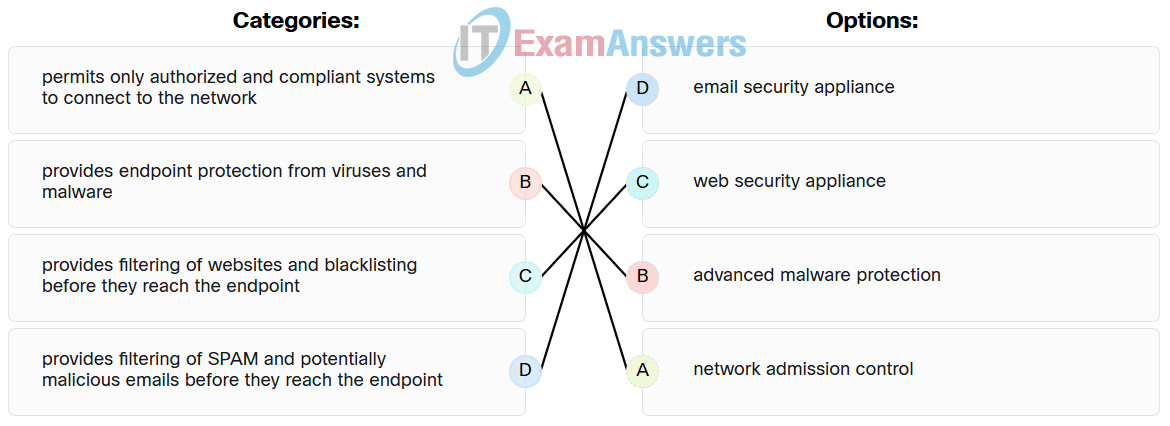
65. What is the result of a DHCP starvation attack?
- Legitimate clients are unable to lease IP addresses.
- Clients receive IP address assignments from a rogue DHCP server.
- The attacker provides incorrect DNS and default gateway information to clients.
- The IP addresses assigned to legitimate clients are hijacked.
66. Which two attacks target web servers through exploiting possible vulnerabilities of input functions used by an application? (Choose two.)
- SQL injection
- port scanning
- port redirection
- trust exploitation
- cross-site scripting
67. A client device has initiated a secure HTTP request to a web browser. Which well-known port address number is associated with the destination address?
- 404
- 80
- 443
- 110
68. What occurs when a rogue access point is added to a WLAN?
- Authorized access points can transmit excess traffic to rogue access points to help alleviate congestion.
- Unauthorized users can gain access to internal servers, thus causing a security hole.
- All traffic that uses the same channel as the rogue access point will be encrypted.
- All traffic that uses the same channel as the rogue access point will be required to authenticate.
69. What is the first line of defense to protect a device from improper access control?
- encryption
- end user license agreement (EULA)
- passwords
- shredding
70. What would be displayed if the netstat -abno command was entered on a Windows PC?
- a local routing table
- only active TCP connections in an ESTABLISHED state
- only active UDP connections in an LISTENING state
- all active TCP and UDP connections, their current state, and their associated process ID (PID)
71. What three tasks are accomplished by a comprehensive security policy? (Choose three.)
- sets rules for expected behavior
- defines legal consequences of violations
- gives security staff the backing of management
- vagueness
- useful for management
- is not legally binding
72. What is the purpose of the cd∖ command?
- changes directory to the root directory
- changes directory to the next highest directory
- changes directory to the previous directory
- changes directory to the next lower directory
73. As described by the SANS Institute, which attack surface includes the exploitation of vulnerabilities in wired and wireless protocols used by IoT devices?
- human attack surface
- Internet attack surface
- network attack surface
- software attack surface
74. Which term is used for bulk advertising emails flooded to as many end users as possible?
- Phishing
- Brute force
- Spam
- Adware
75. A flood of packets with invalid source IP addresses requests a connection on the network. The server busily tries to respond, resulting in valid requests being ignored. What type of attack has occurred?
- UDP flood
- TCP session hijacking
- TCP reset
- TCP SYN flood
76. Which type of network attack involves randomly opening many Telnet requests to a router and results in a valid network administrator not being able to access the device?
- spoofing
- man-in-the-middle
- SYN flooding
- DNS poisoning
77. Which two options can limit the information discovered from port scanning? (Choose two.)
- authentication
- encryption
- firewall
- intrusion prevention system
- passwords
78. What would be a reason for a computer user to use the Task Manager Performance tab?
- to increase the performance of the CPU
- to view the processes that are running and end a process if needed
- to view the services that are currently running on the PC
- to check the CPU usage of the PC
79. Which type of networks poses increasing challenges to cybersecurity specialists due to the growth of BYOD on campus?
- sneaker net
- wireless networks
- wired networks
- virtual networks
80. Which method can be used to harden a device?
- Allow users to re-use old passwords.
- Allow USB auto-detection.
- Force periodic password changes.
- Allow default services to remain enabled.
81. Which technology is used by Cisco Advanced Malware Protection (AMP) in defending and protecting against known and emerging threats?
- network admission control
- website filtering and block listing
- network profiling
- threat intelligence
82. Which user can override file permissions on a Linux computer?
- any user that has 'group' permission to the file
- root user
- any user that has 'other' permission to the file
- only the creator of the file
83. What do you call an impersonation attack that takes advantage of a trusted relationship between two systems?
- Sniffing
- Spamming
- Spoofing
- Man-in-the-middle
84. Which device can control and manage a large number of corporate APs?
- LWAP
- router
- switch
- WLC
85. Which HIDS is an open-source based product?
- Tripwire
- OSSEC
- Cisco AMP
- AlienVault USM
86. An attacker is using a laptop as a rogue access point to capture all network traffic from a targeted user. Which type of attack is this?
- trust exploitation
- buffer overflow
- man in the middle
- port redirection
87. A threat actor wants to interrupt a normal TCP communication between two hosts by sending a spoofed packet to both endpoints. Which TCP option bit would the threat actor set in the spoofed packet?
- ACK
- FIN
- RST
- SYN
88. Employees in an organization report that they cannot access the customer database on the main server. Further investigation reveals that the database file is now encrypted. Shortly afterward, the organization receives a threatening email demanding payment for the decryption of the database file. What type of attack has the organization experienced?
- DoS attack
- Man-in-the-middle attack
- Ransomware
- Trojan horse
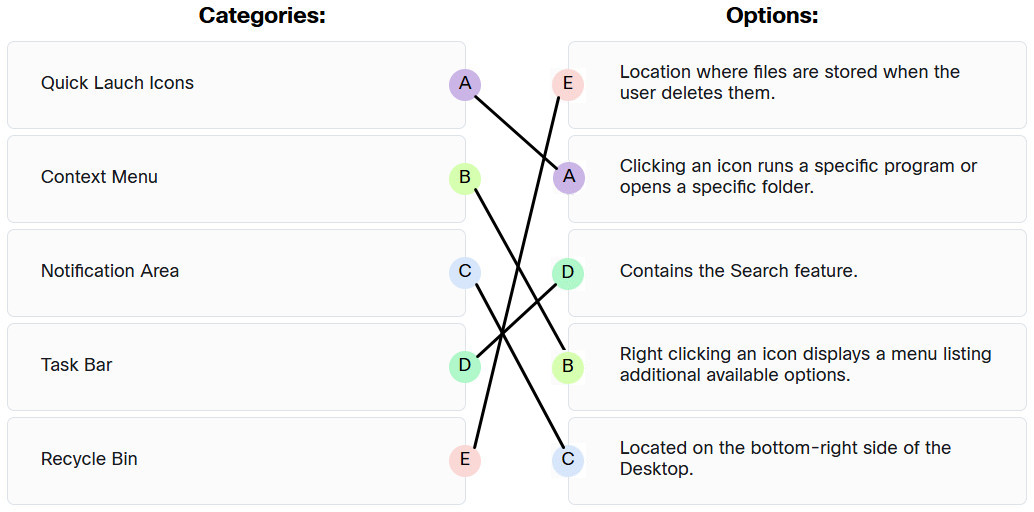
89. Match the Windows GUI term to the characteristic.
90. What three best practices can help defend against social engineering attacks? (Choose three.)
- Enable a policy that states that the IT department should supply information over the phone only to managers.
- Add more security guards.
- Resist the urge to click on enticing web links.
- Deploy well-designed firewall appliances.
- Educate employees regarding policies.
- Do not provide password resets in a chat window.
91. Which Linux command would create a symbolic link for a file named file1.txt?
- ln file1.txt symbol1.txt
- ln -s file1.txt symbol1.txt
- ln -b file1.txt symbol1.txt
- ln - P file1.txt symbol1.txt
92. Which type of DNS attack involves the cybercriminal compromising a parent domain and creating multiple subdomains to be used during the attacks?
- shadowing
- amplification and reflection
- tunneling
- cache poisoning
93. Which device in a LAN infrastructure is susceptible to MAC address-table overflow and spoofing attacks?
- firewall
- workstation
- server
- switch
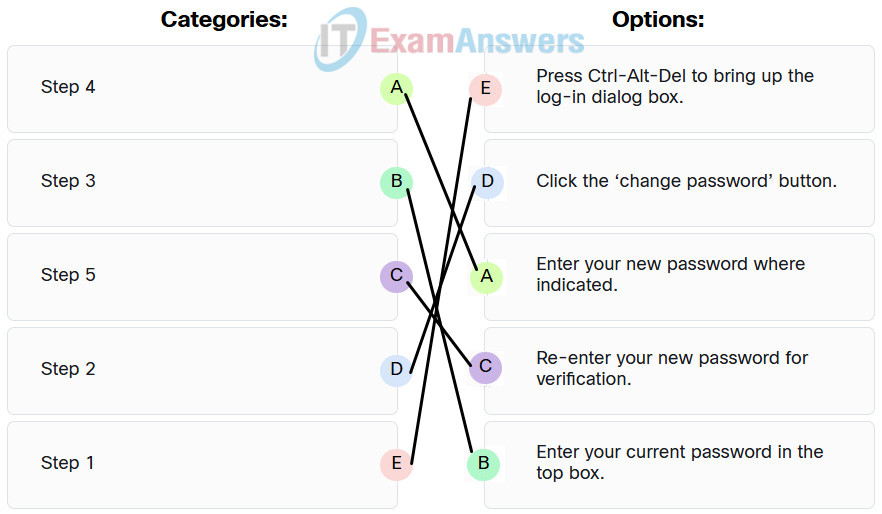
94. Match the step number to the description in a change password procedure on a Windows host.
95. What is a characteristic of the WLAN passive discover mode?
- The client must know the name of the SSID to begin the discover process.
- The client begins the discover process by sending a probe request.
- The beaconing feature on the AP is disabled.
- The AP periodically sends beacon frames containing the SSID.
96. Which field in an IPv6 packet is used by the router to determine if a packet has expired and should be dropped?
- TTL
- Hop Limit
- Address Unreachable
- No Route to Destination
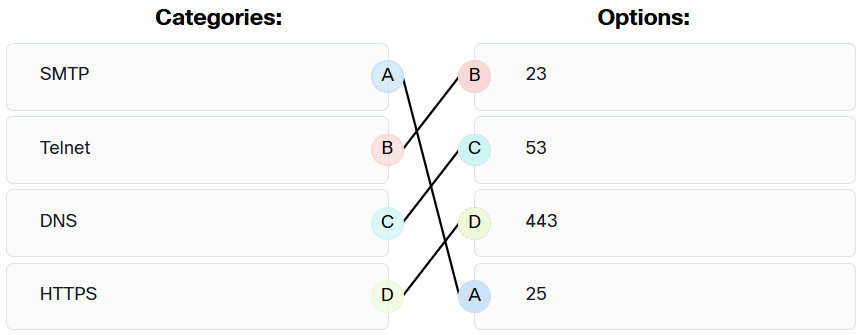
97. Match the commonly used ports on a Linux server with the corresponding service. (Not all options are used.)
98. What is an example of a local exploit?
- Port scanning is used to determine if the Telnet service is running on a remote server.
- A threat actor performs a brute force attack on an enterprise edge router to gain illegal access.
- A buffer overflow attack is launched against an online shopping website and causes the server crash.
- A threat actor tries to gain the user password of a remote host by using a keyboard capture software installed on it by a Trojan.
99. What are two drawbacks to using HIPS? (Choose two.)
- With HIPS, the success or failure of an attack cannot be readily determined.
- With HIPS, the network administrator must verify support for all the different operating systems used in the network.
- HIPS has difficulty constructing an accurate network picture or coordinating events that occur across the entire network.
- If the network traffic stream is encrypted, HIPS is unable to access unencrypted forms of the traffic.
- HIPS installations are vulnerable to fragmentation attacks or variable TTL attacks
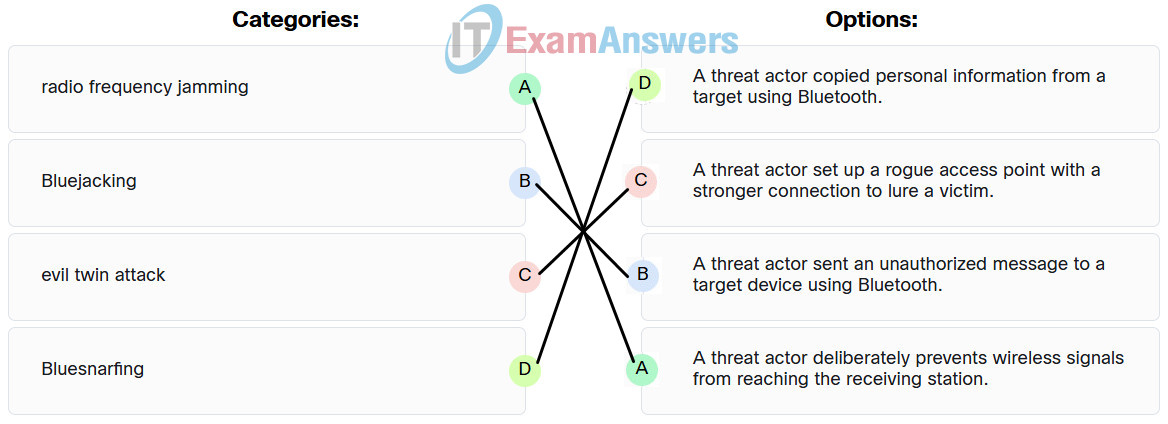
100. Match the wireless and mobile device attack to the scenario.
101. A system administrator issues the apt-get upgrade command on a Linux operating system. What is the purpose of this command?
- Every application installed will update itself to the latest version.
- Operating system updates are downloaded and will be installed.
- The remote repository of applications and dependencies will be updated to the latest version.
- A specific application named upgrade will be installed.
102. For security reasons a network administrator needs to ensure that local computers cannot ping each other. Which settings can accomplish this task?
- smartcard settings
- firewall settings
- MAC address settings
- file system settings
103. Which statement describes the policy-based intrusion detection approach?
- It compares the signatures of incoming traffic to a known intrusion database.
- It compares the operations of a host against well-defined security rules.
- It compares the antimalware definitions to a central repository for the latest updates.
- It compares the behaviors of a host to an established baseline to identify potential intrusion.
104. City Center Hospital provides WLAN connectivity to its employees. The security policy requires that communication between employee mobile devices and the access points must be encrypted. What is the purpose of this requirement?
- to ensure that users who connect to an AP are employees of the hospital
- to prevent a computer virus on a mobile device from infecting other devices
- to prevent the contents of intercepted messages from being read
- to block denial of service attacks originating on the Internet
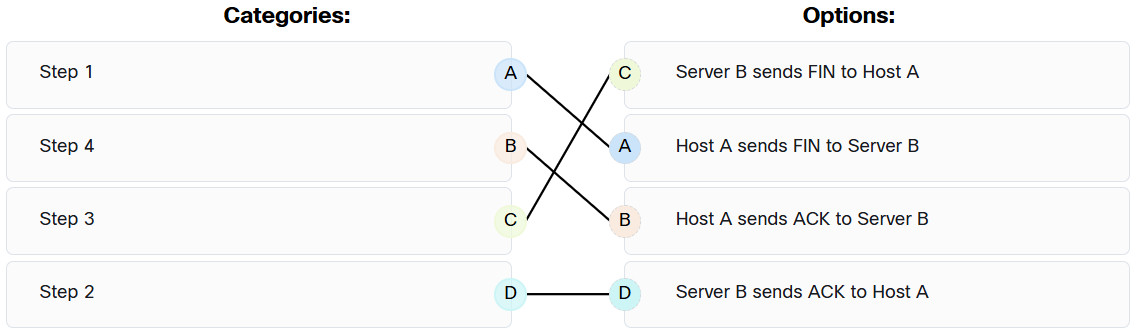
105. After host A receives a web page from server B, host A terminates the connection with server B. Match each option to its correct step in the normal termination proccess for a TCP connection.
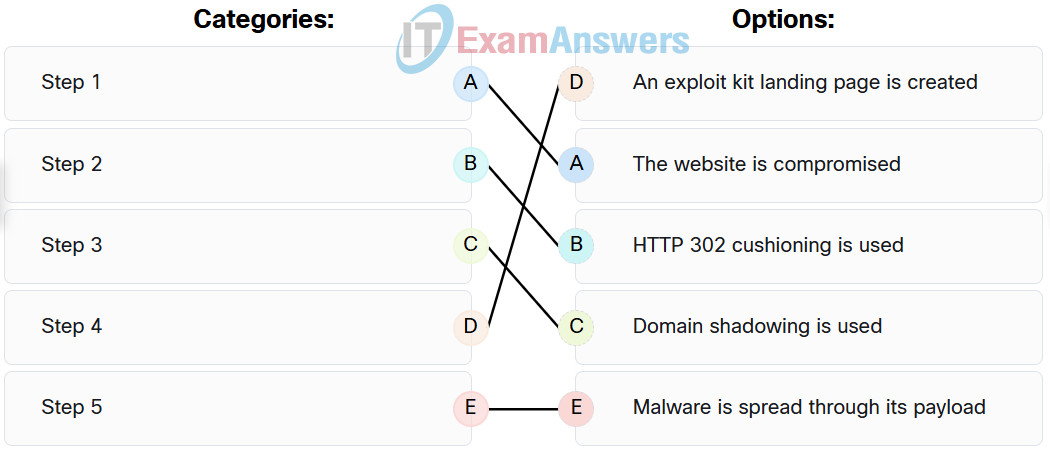
106. Match the correct sequence of steps typically taken by a threat actor carrying out a domain shadowing attack.
107. In the context of a Linux operating system, which command can be used to display the syntax and parameters for a specific command?
- crontab
- man
- grep
- cat
108. Which two methods help to ensure data integrity? (Choose two.)
- data consistency checks
- privacy
- hashing
- availability
- authorization
- repudiation
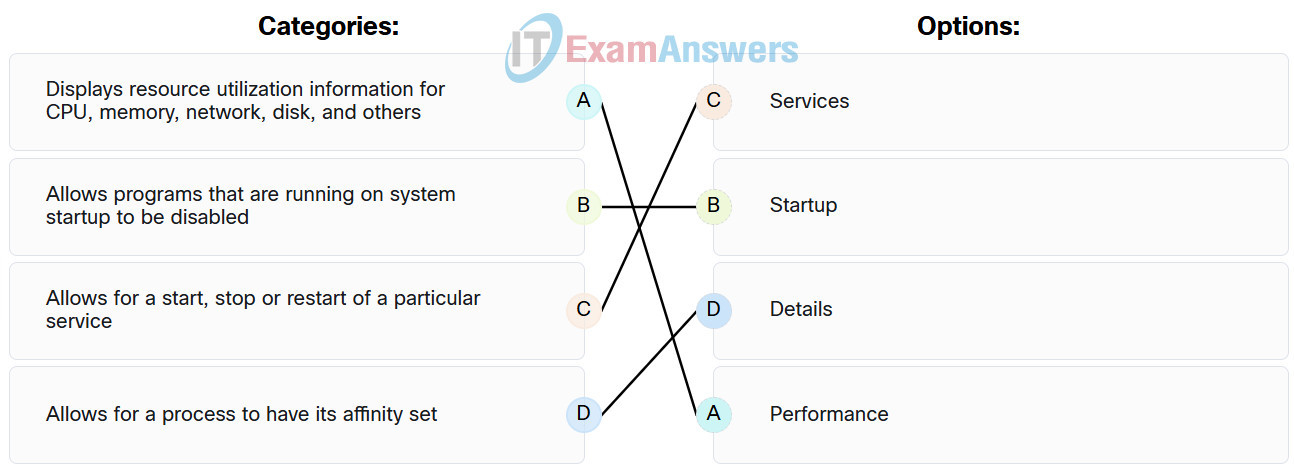
109. Match the tabs of the Windows 10 Task Manager to their functions. (Not all options are used.)
110. A user is proposing the purchase of a patch management solution for a company. The user wants to give reasons why the company should spend money on a solution. What benefits does patch management provide? (Choose three.)
- Patches can be written quickly.
- Administrators can approve or deny patches.
- Patches can be chosen by the user.
- Updates cannot be circumvented.
- Computers require a connection to the Internet to receive patches.
- Updates can be forced on systems immediately.
111. How is a source IP address used in a standard ACL?
- It is used to determine the default gateway of the router that has the ACL applied.
- It is the address that is unknown, so the ACL must be placed on the interface closest to the source address.
- It is the address to be used by a router to determine the best path to forward packets.
- It is the criterion that is used to filter traffic.
112. What are two shared characteristics of the IDS and the IPS? (Choose two.)
- Both have minimal impact on network performance.
- Both are deployed as sensors.
- Both analyze copies of network traffic.
- Both use signatures to detect malicious traffic.
- Both rely on an additional network device to respond to malicious traffic.
113. What type of cybersecurity laws protect you from an organization that might want to share your sensitive data?
- authentication
- confidentiality
- nonrepudiation
- privacy
- integrity
114. What are two advantages of the NTFS file system compared with FAT32? (Choose two.)
- NTFS is easier to configure.
- NTFS provides more security features.
- NTFS supports larger files.
- NTFS allows faster access to external peripherals such as a USB drive.
- NTFS allows faster formatting of drives.
- NTFS allows the automatic detection of bad sectors.
115. Which statement describes agentless antivirus protection?
- Host-based antivirus systems provide agentless antivirus protection.
- The antivirus protection is provided by the router that is connected to a cloud service.
- The antivirus protection is provided by the ISP.
- Antivirus scans are performed on hosts from a centralized system.
116. All employees in an organization receive an email stating that their account password will expire immediately and that they should reset their password within five minutes. Which of the following statements best describes this email?
- It is a piggyback attack
- It is an impersonation attack
- It is a hoax
- It is a DDoS attack
117. Which security measure is best used to limit the success of a reconnaissance attack from within a campus area network?
- Implement restrictions on the use of ICMP echo-reply messages.
- Implement a firewall at the edge of the network.
- Implement access lists on the border router.
- Implement encryption for sensitive traffic.
118. What tasks are accomplished by a comprehensive security policy? (Select three answers)
- It sets rules for expected behavior
- It defines legal consequences of violations
- It gives security staff the backing of management
- It provides vagueness
- It is is useful for management
- It is not legally binding
119. A network administrator of a small advertising company is configuring WLAN security by using the WPA2 PSK method. Which credential do office users need in order to connect their laptops to the WLAN?
- the company username and password through Active Directory service
- a user passphrase
- a key that matches the key on the AP
- a username and password configured on the AP
120. Match the Linux command to the function. (Not all options are used.)
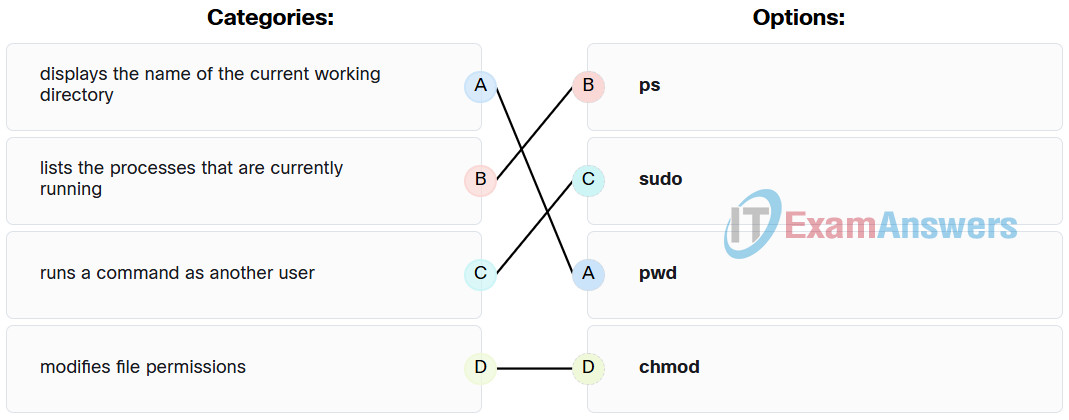
- Displays the name of the current working directory: pwd
- runs a command as another user: sudo
- modifies file permissions: chmod
- shuts down the system: Empty
- lists the processes that are currently running: ps
121. Which statement describes the anomaly-based intrusion detection approach?
- It compares the antivirus definition file to a cloud based repository for latest updates.
- It compares the behavior of a host to an established baseline to identify potential intrusions.
- It compares the signatures of incoming traffic to a known intrusion database.
- It compares the operations of a host against a well-defined security policy.
122. A security incident has been filed and an employee believes that someone has been on the computer since the employee left last night. The employee states that the computer was turned off before the employee left for the evening. The computer is running slowly and applications are acting strangely. Which Microsoft Windows tool would be used by the security analyst to determine if and when someone logged on to the computer after working hours?
- Task Manager
- Event Viewer
- PowerShell
- Performance Monitor
123. What is a method of sending information from one device to another using removable media?
- wired
- infrared
- LAN
- packet
- wireless
- sneaker net
124. What type of attack occurs when data goes beyond the memory areas allocated to an application?
- RAM spoofing
- SQL injection
- RAM injection
- Buffer overflow
125. Which technique could be used by security personnel to analyze a suspicious file in a safe environment?
- sandboxing
- baselining
- allow listing
- block listing
126. What principle prevents the disclosure of information to unauthorized people, resources, and processes?
- integrity
- confidentiality
- nonrepudiation
- accounting
- availability
127. Which type of tool is used by a Linux administrator to attack a computer or network to find vulnerabilities?
- Firewall
- PenTesting
- Malware analysis
- Intrusion detection system
128. What is a wireless security mode that requires a RADIUS server to authenticate wireless users?
- personal
- shared key
- enterprise
- WEP
129. The employees in a company receive an email stating that the account password will expire immediately and requires a password reset within 5 minutes. Which statement would classify this email?
- It is a hoax.
- It is an impersonation attack.
- It is a piggy-back attack.
- It is a DDoS attack.
130. Match the attack to the definition. (Not all options are used.)
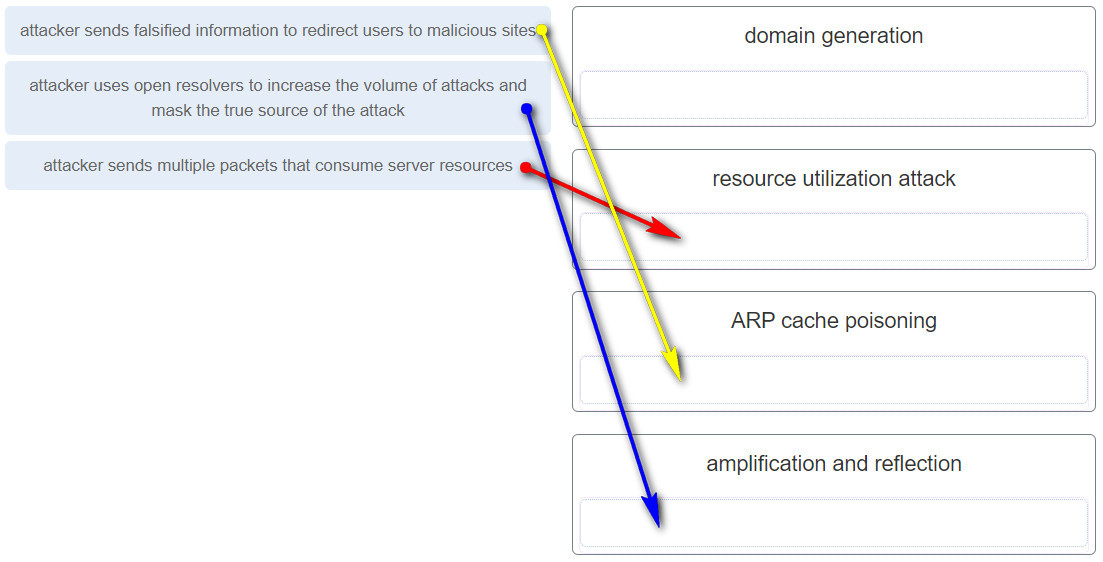
| attacker uses open resolvers to increase the volume of attacks and mask the true source of the attack | amplification and reflection |
| attacker sends falsified information to redirect users to malicious sites | ARP cache poisoning |
| attacker sends multiple packets that consume server resources | resource utilization attack |
131. What three methods help to ensure system availability? (Choose three.)
- system backups
- equipment maintenance
- system resiliency
- integrity checking
- up-to-date operating systems
- fire extinguishers
132. A penetration test carried out by an organization identified a backdoor on the network. What action should the organization take to find out if their systems have been compromised?
- Scan the systems for viruses
- Look for policy changes in Event Viewer
- Look for unauthorized accounts
- Look for usernames that do not have passwords
133. For which discovery mode will an AP generate the most traffic on a WLAN?
- passive mode
- open mode
- mixed mode
- active mode
134. What is the function of the kernel of an operating system?
- It provides a user interface that allows users to request a specific task.
- The kernel links the hardware drivers with the underlying electronics of a computer.
- It is an application that allows the initial configuration of a Cisco device.
- The kernel provisions hardware resources to meet software requirements
135. In most host-based security suites, which function provides robust logging of security-related events and sends logs to a central location?
- telemetry
- anti-phishing
- safe browsing
- intrusion detection and prevention
136. What is identified by the first dimension of the cybersecurity cube?
- safeguards
- goals
- rules
- tools
- knowledge
137. Why would a network administrator choose Linux as an operating system in the Security Operations Center (SOC)?
- It is easier to use than other operating systems.
- It is more secure than other server operating systems.
- More network applications are created for this environment.
- The administrator has more control over the operating system.
138. Which best practices can help defend against social engineering attacks? Select three correct answers
- Add more security guards
- Educate employees regarding security policies
- Enable a policy that states that the IT department should supply information over the phone only to managers
- Deploy well-designed firewall appliances
- Resist the urge to click on enticing web links
- Do not provide password resets in a chat window
139. Which two roles are typically performed by a wireless router that is used in a home or small business? (Choose two.)
- repeater
- access point
- WLAN controller
- Ethernet switch
- RADIUS authentication server
