
16.2.1 Packet Tracer - Configure GRE (Answers)
Topology
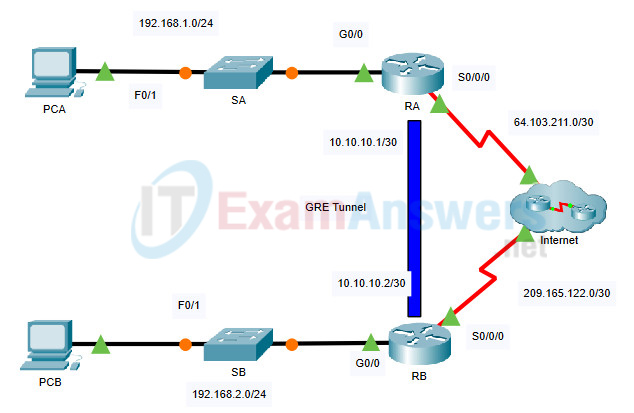
16.2.1 Packet Tracer - Configure GRE
Addressing Table
| Device | Interface | IP Address | Subnet Mask | Default Gateway |
|---|---|---|---|---|
| RA | G0/0 | 192.168.1.1 | 255.255.255.0 | N/A |
| S0/0/0 | 64.103.211.2 | 255.255.255.252 | ||
| Tunnel 0 | 10.10.10.1 | 255.255.255.252 | ||
| RB | G0/0 | 192.168.2.1 | 255.255.255.0 | N/A |
| S0/0/0 | 209.165.122.2 | 255.255.255.252 | ||
| Tunnel 0 | 10.10.10.2 | 255.255.255.252 | ||
| PCA | NIC | 192.168.1.2 | 255.255.255.0 | 192.168.1.1 |
| PCB | NIC | 192.168.2.2 | 255.255.255.0 | 192.168.2.1 |
Objectives
- Part 1: Verify Router Connectivity
- Part 2: Configure GRE Tunnels
- Part 3: Verify PC Connectivity
Scenario
You are the network administrator for a company which wants to set up a GRE tunnel to a remote office. Both networks are locally configured. You need configure the tunnel and static routes.
Instructions
Part 1: Verify Router Connectivity
Step 1: Ping RA from RB.
Use the show ip interface brief command on RA to determine the IP address of the S0/0/0 port.
From RB ping the IP S0/0/0 address of RA.
Step 2: Ping PCA from PCB.
Attempt to ping the IP address of PCA from PCB. We will repeat this test after configuring the GRE tunnel. What were the ping results? Explain.
The pings failed because there is no route to the destination.
Part 2: Configure GRE Tunnels
Step 1: Configure the Tunnel 0 interface of RA.
a. Enter into the configuration mode for RA Tunnel 0.
RA(config)# interface tunnel 0
b. Set the IP address as indicated in the Addressing Table.
RA(config-if)# ip address 10.10.10.1 255.255.255.252
c. Set the source and destination for the endpoints of Tunnel 0.
RA(config-if)# tunnel source s0/0/0
RA(config-if)# tunnel destination 209.165.122.2
d. Configure Tunnel 0 to convey IP traffic over GRE.
RA(config-if)# tunnel mode gre ip
e. The Tunnel 0 interface should already be active. In the event that it is not, treat it like any other interface.
RA(config-if)# no shutdown
Step 2: Configure the Tunnel 0 interface of RB.
Repeat Steps 1a – e with RB. Be sure to change the IP addressing as appropriate.
RB(config)# interface tunnel 0
RB(config-if)# ip address 10.10.10.2 255.255.255.252
RB(config-if)# tunnel source s0/0/0
RB(config-if)# tunnel destination 64.103.211.2
RB(config-if)# tunnel mode gre ip
RB(config-if)# no shutdown
Step 3: Configure a route for private IP traffic.
Establish a route between the 192.168.X.X networks using the 10.10.10.0/30 network as the destination.
RA(config)# ip route 192.168.2.0 255.255.255.0 10.10.10.2
RB(config)# ip route 192.168.1.0 255.255.255.0 10.10.10.1
Part 3: Verify Router Connectivity
Step 1: Ping PCA from PCB.
Attempt to ping the IP address of PCA from PCB. The ping should be successful.
Step 2: Trace the path from PCA to PCB.
Attempt to trace the path from PCA to PCB. Note the lack of public IP addresses in the output.
Device Configs - Final
ROUTER RA
! ==============================================================
!--- 16.2.1 Packet Tracer - Configure GRE
!--- ANSWER SCRIPT FOR ROUTER RA
!--- Usage: copy this whole file and paste it into the RA terminal (start at the RA> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- Scope: LAN/WAN IP addressing is already configured per the activity's
!--- own topology - this script only builds the GRE tunnel to RB and the
!--- static route that sends LAN-to-LAN traffic through it.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2, Step 1: Build the Tunnel 0 interface - a GRE tunnel is a
!--- logical (virtual) interface, so it needs its own IP address plus a
!--- source and destination pair naming the two real interfaces it rides on.
! --------------------------------------------------------------

interface tunnel 0

!--- Tunnel-side address, from the Addressing Table's 10.10.10.0/30 network.
 ip address 10.10.10.1 255.255.255.252

!--- Endpoints of the tunnel: RA's own WAN interface, and RB's WAN address
!--- on the other side of the Internet cloud.
 tunnel source serial 0/0/0
 tunnel destination 209.165.122.2

!--- Explicit GRE-over-IP encapsulation mode.
 tunnel mode gre ip

!--- Tunnel interfaces usually come up active by default - this is only a
!--- safeguard in case Tunnel 0 is administratively down.
 no shutdown
 exit

! --------------------------------------------------------------
!--- Part 2, Step 3: Route RA's LAN toward RB's LAN through the tunnel,
!--- not through the real WAN link - the tunnel is what makes the private
!--- 192.168.x.x addresses reachable across the public Internet cloud.
! --------------------------------------------------------------

ip route 192.168.2.0 255.255.255.0 10.10.10.2

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief         -> Tunnel0 10.10.10.1, status/protocol up/up
!---   show interfaces tunnel 0        -> source 64.103.211.2, destination 209.165.122.2, GRE/IP
!---   show ip route static            -> S 192.168.2.0/24 [1/0] via 10.10.10.2
!---   ping 10.10.10.2 (from RA)        -> tunnel endpoint reachable
!---   ping 192.168.1.1 (from RB, after RB is configured)  -> Part 1 Step 1 repeated, succeeds now
!---   ping 192.168.1.2 (from PCB, after RB is configured) -> Part 3 Step 1, succeeds
!--- Note: no functional errors found versus the lab's own Instructions or
!--- Device Configs section - both agree with the Addressing Table.
! ==============================================================
ROUTER RB
! ==============================================================
!--- 16.2.1 Packet Tracer - Configure GRE
!--- ANSWER SCRIPT FOR ROUTER RB
!--- Usage: copy this whole file and paste it into the RB terminal (start at the RB> prompt). Every line beginning with "!" is a comment; IOS ignores it, so pasting a comment by accident is harmless.
!--- Scope: LAN/WAN IP addressing is already configured per the activity's
!--- own topology - this script only builds the GRE tunnel to RA and the
!--- static route that sends LAN-to-LAN traffic through it.
! ==============================================================

enable
configure terminal

! --------------------------------------------------------------
!--- Part 2, Step 2: Build the Tunnel 0 interface - same 5 sub-commands as
!--- RA, mirrored: same tunnel-network address (the other /30 host), and
!--- source/destination swapped to point back at RA.
! --------------------------------------------------------------

interface tunnel 0

!--- Tunnel-side address, from the Addressing Table's 10.10.10.0/30 network.
 ip address 10.10.10.2 255.255.255.252

!--- Endpoints of the tunnel: RB's own WAN interface, and RA's WAN address
!--- on the other side of the Internet cloud.
 tunnel source serial 0/0/0
 tunnel destination 64.103.211.2

!--- Explicit GRE-over-IP encapsulation mode.
 tunnel mode gre ip

!--- Tunnel interfaces usually come up active by default - this is only a
!--- safeguard in case Tunnel 0 is administratively down.
 no shutdown
 exit

! --------------------------------------------------------------
!--- Part 2, Step 3: Route RB's LAN toward RA's LAN through the tunnel,
!--- not through the real WAN link - the tunnel is what makes the private
!--- 192.168.x.x addresses reachable across the public Internet cloud.
! --------------------------------------------------------------

ip route 192.168.1.0 255.255.255.0 10.10.10.1

end

! --------------------------------------------------------------
!--- Save the configuration to NVRAM. (Press Enter when prompted for the destination filename.)
! --------------------------------------------------------------
copy running-config startup-config


! ==============================================================
!--- Verification:
!---   show ip interface brief         -> Tunnel0 10.10.10.2, status/protocol up/up
!---   show interfaces tunnel 0        -> source 209.165.122.2, destination 64.103.211.2, GRE/IP
!---   show ip route static            -> S 192.168.1.0/24 [1/0] via 10.10.10.1
!---   ping 10.10.10.1 (from RB)        -> tunnel endpoint reachable
!---   ping 192.168.1.2 (from PCB, once both routers are configured)  -> Part 3 Step 1, succeeds
!---   tracert 192.168.1.2 (from PCB)   -> Part 3 Step 2, shows only the tunnel/private hops, no public WAN addresses
!--- Note: no functional errors found versus the lab's own Instructions or
!--- Device Configs section - both agree with the Addressing Table.
! ==============================================================

