
Lab Objective:
The objective of this lab exercise is for you to configure VTP and trunking settings.
Lab Purpose:
Configuring VTP and securing the trunk link is a vital CCNA-level skill. Rather than watch a video solution, I have provided show runs and test commands where appropriate.
Certification Level:
This lab is suitable for both CCENT and CCNA certification exam preparation.
Lab Difficulty:
This lab has a difficulty rating of 7/10.
Readiness Assessment:
When you are ready for your certification exam, you should complete this lab in no more than 15 minutes.
Lab Topology:
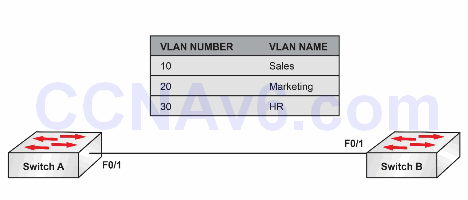
Please use the following topology to complete this lab exercise:
Task 1:
Connect two switches together as shown above. Set the relevant hostnames and the F0/1 interfaces to trunk.
Task 2:
Configure SwitchA as a VTP server with the VTP domain howtonetwork.com and VTP password Cisco. Set SwitchB as a VTP client with the same VTP domain settings.
Task 3:
Configure the three VLANs as per the diagram.
Task 4:
Turn off DTP for the trunk interfaces.
Task 5:
Set the native VLAN on both switches to VLAN888. Shut down VLAN1 on both switches.
Task 6:
Permit only VLANs 10, 20, and 30 to cross the trunk link. I know we haven’t covered this yet so feel free to take a peek at the configurations. It’s a Layer 2 security step that you will need to know.
Task 7:
Issue relevant show commands to verify your configurations.
Solution
Many of the Layer 2 settings do not show in the show run (they are held in the vlan database). All of the commands are in the videos though if you are using these to accompany the book. You have already seen the VTP commands in previous labs. You would permit VLAN888 in the real world but don’t worry about that for this lab.
Show Runs
hostname SwitchA
!
spanning-tree mode pvst
!
interface FastEthernet0/1
switchport trunk native vlan888
switchport trunk allowed vlan10,20,30
switchport mode trunk
switchport nonegotiate

hostname SwitchB
!
spanning-tree mode pvst
!
interface FastEthernet0/1
switchport trunk native vlan888
switchport trunk allowed vlan10,20,30
switchport mode trunk
switchport nonegotiate
TEST:
SwitchB#show vtp status
VTP Version                     : 2
Configuration Revision          : 6
Maximum VLANs supported locally : 255
Number of existing VLANs        : 8
VTP Operating Mode              : Client
VTP Domain Name                 : howtonetwork.com
VTP Pruning Mode                : Disabled
VTP V2 Mode                     : Disabled
VTP Traps Generation            : Disabled
MD5 digest                      : 0xA7 0x6A 0x55 0x45 0xBB 0x6B 0x23 0x14
 Configuration last modified by 0.0.0.0 at 3-1-93 00:19:44

SwitchB#show in trunk
Port        Mode         Encapsulation  Status        Native vlan
Fa0/1       on           802.1q         trunking      888

Port        Vlans allowed on trunk
Fa0/1       10,20,30

Port        Vlans allowed and active in management domain
Fa0/1       10,20,30

Port        Vlans in spanning tree forwarding state and not pruned
Fa0/1       10,20,30
SwitchB#

SwitchB#show int f0/1 switchport
Name: Fa0/1
Switchport: Enabled
Administrative Mode: trunk
Operational Mode: trunk
Administrative Trunking Encapsulation: dot1q
Operational Trunking Encapsulation: dot1q
Negotiation of Trunking: Off
Access Mode VLAN: 1 (default)
Trunking Native Mode VLAN: 888 (Inactive)

VLAN Name                    Status    Ports
---- ----------------------- --------- -------------------------------
1    default                 active    Fa0/2, Fa0/3, Fa0/4, Fa0/5
                                       Fa0/6, Fa0/7, Fa0/8, Fa0/9
                                       Fa0/10, Fa0/11, Fa0/12, Fa0/13
                                       Fa0/14, Fa0/15, Fa0/16, Fa0/17
                                       Fa0/18, Fa0/19, Fa0/20, Fa0/21
                                       Fa0/22, Fa0/23, Fa0/24, Gig1/1
                                       Gig1/2
10   Sales                   active
20   Marketing               active
30   HR                      active
1002 fddi-default            active