Endpoint Security (ESec) Final Exam Answers (Course Final Exam)
Modules 1 - 10 Endpoint Security (Esec) Course Final Exam Answers
1. Which two commands could be used to check if DNS name resolution is working properly on a Windows PC? (Choose two.)
- ping cisco.com
- net cisco.com
- ipconfig /flushdns
- nslookup cisco.com
- nbtstat cisco.com
Explanation: Topic 7.3.7
The ping command tests the connection between two hosts. When ping uses a host domain name to test the connection, the resolver on the PC will first perform the name resolution to query the DNS server for the IP address of the host. If the ping command is unable to resolve the domain name to an IP address, an error will result.
Nslookup is a tool for testing and troubleshooting DNS servers.
2. A technician notices that an application is not responding to commands and that the computer seems to respond slowly when applications are opened. What is the best administrative tool to force the release of system resources from the unresponsive application?
- Event Viewer
- Add or Remove Programs
- System Restore
- Task Manager
Explanation: Topic 7.3.6
Use the Task Manager Performance tab to see a visual representation of CPU and RAM utilization. This is helpful in determining if more memory is needed. Use the Applications tab to halt an application that is not responding.
3. What is required in order to connect a Wi-Fi enabled laptop to a WPA secured wireless network?
- a MAC address
- a username and password
- a security encryption key
- an updated wireless driver
Explanation: Topic 5.3.3
Regardless of the levels of security configured on a WLAN, a WPA secured WLAN always requires the use of an encryption key. Without the proper key, a device cannot connect to the network.
4. Why would an attacker want to spoof a MAC address?
- so that the attacker can launch another type of attack in order to gain access to the switch
- so that the attacker can capture traffic from multiple VLANs rather than from just the VLAN that is assigned to the port to which the attacker device is attached
- so that a switch on the LAN will start forwarding frames to the attacker instead of to the legitimate host
- so that a switch on the LAN will start forwarding all frames toward the device that is under control of the attacker (that can then capture the LAN traffic)
Explanation: Topic 3.2.5
MAC address spoofing is used to bypass security measures by allowing an attacker to impersonate a legitimate host device, usually for the purpose of collecting network traffic.
5. What is a wireless security mode that requires a RADIUS server to authenticate wireless users?
- personal
- enterprise
- shared key
- WEP
Explanation: Topic 5.3.7
WPA and WPA2 come in two types: personal and enterprise. Personal is used in home and small office networks. Shared key allows three different authentication techniques: (1) WEP, (2) WPA, and (3) 802.11i/WPA2. WEP is an encryption method.
6. What are three functions provided by the syslog service? (Choose three.)
- to select the type of logging information that is captured
- to provide traffic analysis
- to specify the destinations of captured messages
- to provide statistics on packets that are flowing through a Cisco device
- to gather logging information for monitoring and troubleshooting
- to periodically poll agents for data
Explanation: Topic 6.2.8
There are three primary functions provided by the syslog service:
- gathering logging information
- selection of the type of information to be logged
- selection of the destination of the logged information
7. A network administrator is checking the system logs and notices unusual connectivity tests to multiple well-known ports on a server. What kind of potential network attack could this indicate?
- access
- denial of service
- reconnaissance
- information theft
Explanation: Topic 4.3.4
A reconnaissance attack is the unauthorized discovery and mapping of systems, services, or vulnerabilities. One of the most common reconnaissance attacks is performed by using utilities that automatically discover hosts on the networks and determine which ports are currently listening for connections.
8. A technician has installed a third party utility that is used to manage a Windows 7 computer. However, the utility does not automatically start whenever the computer is started. What can the technician do to resolve this problem?
- Set the application registry key value to one.
- Use the Add or Remove Programs utility to set program access and defaults.
- Change the startup type for the utility to Automatic in Services.
- Uninstall the program and then choose Add New Programs in the Add or Remove Programs utility to install the application.
Explanation: Topic 7.2.8
The Services console in Windows OS allows for the management of all the services on the local and remote computers. The setting of Automatic in the Services console enables the chosen service to start when the computer is started.
9. What is the motivation of a white hat attacker?
- discovering weaknesses of networks and systems to improve the security level of these systems
- studying operating systems of various platforms to develop a new system
- fine tuning network devices to improve their performance and efficiency
- taking advantage of any vulnerability for illegal personal gain
Explanation: Topic 2.2.2
White hat attackers break into networks or computer systems in order to discover weaknesses for the purpose of improving the security of these systems. These break-ins are done with permission from the owner or the organization. Any results are reported back to the owner or the organization.
10. Which two types of hackers are typically classified as grey hat hackers? (Choose two.)
- hacktivists
- cyber criminals
- state-sponsored hackers
- script kiddies
- vulnerability brokers
Explanation: Topic 2.2.3
Grey hat hackers may do unethical or illegal things, but not for personal gain or to cause damage. Hacktivists use their hacking as a form of political or social protest, and vulnerability brokers hack to uncover weaknesses and report them to vendors. Depending on the perspective one possesses, state-sponsored hackers are either white hat or black hat operators. Script kiddies create hacking scripts to cause damage or disruption. Cyber criminals use hacking to obtain financial gain by illegal means.
11. What are two shared characteristics of the IDS and the IPS? (Choose two.)
- Both have minimal impact on network performance.
- Both analyze copies of network traffic.
- Both are deployed as sensors.
- Both rely on an additional network device to respond to malicious traffic.
- Both use signatures to detect malicious traffic.
Explanation: Topic 6.1.6
Both the IDS and the IPS are deployed as sensors and use signatures to detect malicious traffic. The IDS analyzes copies of network traffic, which results in minimal impact on network performance. The IDS also relies on an IPS to stop malicious traffic.
12. An attacker is sitting in front of a store and wirelessly copies emails and contact lists from nearby unsuspecting user devices. What type of attack is this?
- bluejacking
- RF jamming
- bluesnarfing
- smishing
Explanation: Topic 1.4.6
Blusnarfing is the copying of user information through unauthorized Bluetooth transmissions.
13. An organization allows employees to work from home two days a week. Which technology should be implemented to ensure data confidentiality as data is transmitted?
Explanation: Topic 10.2.6
Protecting data confidentiality requires an understanding of the technologies used to protect data in all three data states.
14. A new PC is taken out of the box, started up and connected to the Internet. Patches were downloaded and installed. Antivirus was updated. In order to further harden the operating system what can be done?
- Turn off the firewall.
- Remove unnecessary programs and services.
- Disconnect the computer from the network.
- Give the computer a nonroutable address.
- Install a hardware firewall.
- Remove the administrator account.
Explanation: Topic 9.1.2
When hardening an operating system, patching and antivirus are part of the process. Many extra components are added by the manufacturer that are not necessarily needed.
15. Which type of networks poses increasing challenges to cybersecurity specialists due to the growth of BYOD on campus?
- wired networks
- virtual networks
- wireless networks
- sneaker net
Explanation: Topic 10.2.5
A cybersecurity specialist must be familiar with the types of technologies used to store, transmit, and process data.
16. What are two types of attacks used on DNS open resolvers? (Choose two.)
- ARP poisoning
- resource utilization
- cushioning
- amplification and reflection
- fast flux
Explanation: Topic 4.1.3
Three types of attacks used on DNS open resolvers are as follows:
* DNS cache poisoning – attacker sends spoofed falsified information to redirect users from legitimate sites to malicious sites
* DNS amplification and reflection attacks – attacker sends an increased volume of attacks to mask the true source of the attack
* DNS resource utilization attacks – a denial of service (DoS) attack that consumes server resources
17. What would be the target of an SQL injection attack?
Explanation: Topic 4.2.4
SQL is the language used to query a relational database. Cybercriminals use SQL injections to get information, create fake or malicious queries, or to breach the database in some other way.
18. A security specialist is asked for advice on a security measure to prevent unauthorized hosts from accessing the home network of employees. Which measure would be most effective?
- Implement a VLAN.
- Implement intrusion detection systems.
- Implement RAID.
- Implement a firewall.
Explanation: Topic 10.3.2
Protecting data confidentiality requires an understanding of the technologies used to protect data in all three data states.
19. Match the network service with the description.
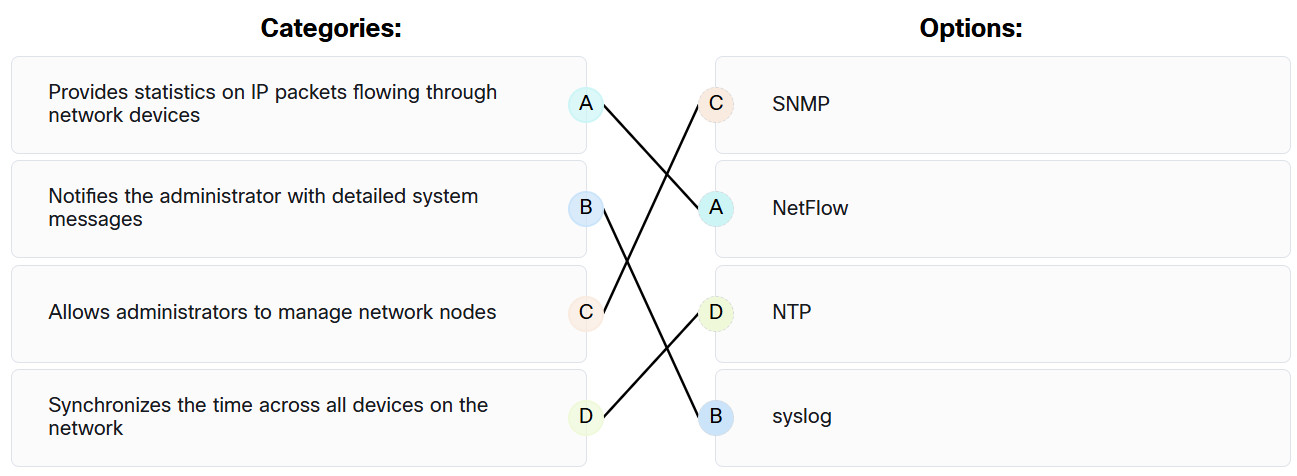
Endpoint Security (ESec) Final Exam Answers 19
Explanation: Topic 6.3.1
Place the options in the following order:
| Notifies the administrator with detailed system messages |
Syslog |
| Provides statistics on IP packets flowing through network devices |
NetFlow |
| Synchronizes the time across all devices on the network |
NTP |
| Allows administrators to manage network nodes |
SNMP |
20. Which method can be used to harden a device?
- allow USB auto-detection
- use SSH and disable the root account access over SSH
- allow default services to remain enabled
- maintain use of the same passwords
Explanation: Topic 8.4.2
The basic best practices for device hardening are as follows:
- Ensure physical security.
- Minimize installed packages.
- Disable unused services.
- Use SSH and disable the root account login over SSH.
- Keep the system updated.
- Disable USB auto-detection.
- Enforce strong passwords.
- Force periodic password changes.
- Keep users from re-using old passwords.
- Review logs regularly.
21. Which user can override file permissions on a Linux computer?
- root user
- any user that has 'group' permission to the file
- only the creator of the file
- any user that has 'other' permission to the file
Explanation: Topic 8.5.2
A user has as much rights to a file as the file permissions allow. The only user that can override file permission on a Linux computer is the root user. Because the root user has the power to override file permissions, the root user can write to any file.
22. Which wireless parameter is used by an access point to broadcast frames that include the SSID?
- passive mode
- channel setting
- active mode
- security mode
Explanation: Topic 5.1.6
The two scanning or probing modes an access point can be placed into are passive or active. In passive mode, the AP advertises the SSID, supported standards, and security settings in broadcast beacon frames. In active mode, the wireless client must be manually configured for the same wireless parameters as the AP has configured.
23. What is the outcome when a Linux administrator enters the man man command?
- The man man command provides documentation about the man command
- The man man command provides a list of commands available at the current prompt
- The man man command opens the most recent log file
- The man man command configures the network interface with a manual address
Explanation: Topic 8.2.2
The man command is short for manual and is used to obtain documentation about a Linux command. The command man man would provide documentation about how to use the manual.
24. Which technique could be used by security personnel to analyze a suspicious file in a safe environment?
- allow listing
- baselining
- block listing
- sandboxing
Explanation: Topic 9.4.3
Sandboxing allows suspicious files to be executed and analyzed in a safe environment. There are free public sandboxes that allow for malware samples to be uploaded or submitted and analyzed.
25. What are three benefits of using symbolic links over hard links in Linux? (Choose three.)
- Symbolic links can be exported.
- They can be compressed.
- They can link to a file in a different file system.
- They can link to a directory.
- They can be encrypted.
- They can show the location of the original file.
Explanation: Topic 8.5.3
In Linux, a hard link is another file that points to the same location as the original file. A soft link (also called a symbolic link or a symlink) is a link to another file system name. Hard links are limited to the file system in which they are created and they cannot link to a directory; soft links are not limited to the same file system and they can link to a directory. To see the location of the original file for a symbolic link use the ls –l command.
26. Which field in the IPv6 header points to optional network layer information that is carried in the IPv6 packet?
- traffic class
- version
- flow label
- next header
Explanation: Topic 3.1.4
Optional Layer 3 information about fragmentation, security, and mobility is carried inside of extension headers in an IPv6 packet. The next header field of the IPv6 header acts as a pointer to these optional extension headers if they are present.
27. What is the term used when a malicious party sends a fraudulent email disguised as being from a legitimate, trusted source?
- phishing
- backdoor
- Trojan
- vishing
Explanation: Topic 1.5.12
Phishing is used by malicious parties who create fraudulent messages that attempt to trick a user into either sharing sensitive information or installing malware.
28. Which technology is used by Cisco Advanced Malware Protection (AMP) in defending and protecting against known and emerging threats?
- website filtering and block listing
- threat intelligence
- network admission control
- network profiling
Explanation: Topic 6.1.9
Cisco AMP uses threat intelligence along with known file signatures to identify and block policy-violating file types and exploitations.
29. After host A receives a web page from server B, host A terminates the connection with server B. Match each option to its correct step in the normal termination proccess for a TCP connection.
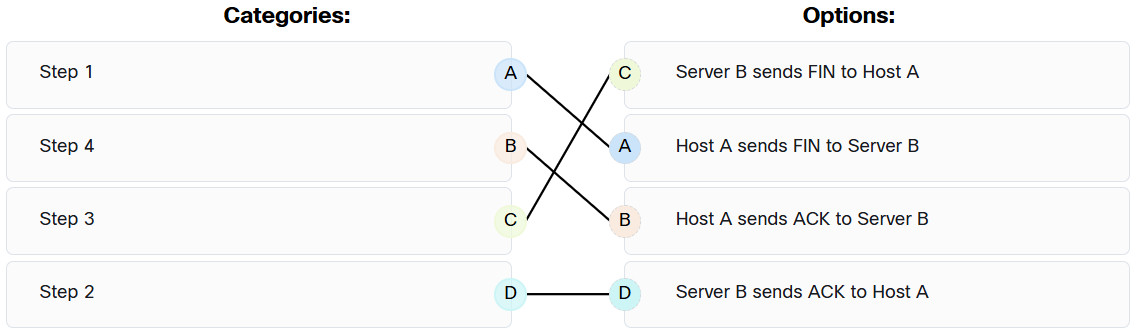
Explanation: Topic 3.3.3
Place the options in the following order:
| Host A sends FIN to Server B |
Step 1 |
| Server B sends ACK to Host A |
Step 2 |
| Server B sends FIN to Host A |
Step 3 |
| Host A sends ACK to Server B |
Step 4 |
30. A flood of packets with invalid source IP addresses requests a connection on the network. The server busily tries to respond, resulting in valid requests being ignored. What type of attack has occurred?
- TCP session hijacking
- TCP reset
- TCP SYN flood
- UDP flood
Explanation: Topic 3.3.3
The TCP SYN Flood attack exploits the TCP three-way handshake. The threat actor continually sends TCP SYN session request packets with a randomly spoofed source IP address to an intended target. The target device replies with a TCP SYN-ACK packet to the spoofed IP address and waits for a TCP ACK packet. Those responses never arrive. Eventually the target host is overwhelmed with half-open TCP connections and denies TCP services.
31. Which Windows tool can be used by a cybersecurity administrator to secure stand-alone computers that are not part of an active directory domain?
- Windows Defender
- Local Security Policy
- Windows Firewall
- PowerShell
Explanation: Topic 7.4.4
Windows systems that are not part of an Active Directory Domain can use the Windows Local Security Policy to enforce security settings on each stand-alone system.
32. Match the correct sequence of steps typically taken by a threat actor carrying out a domain shadowing attack.
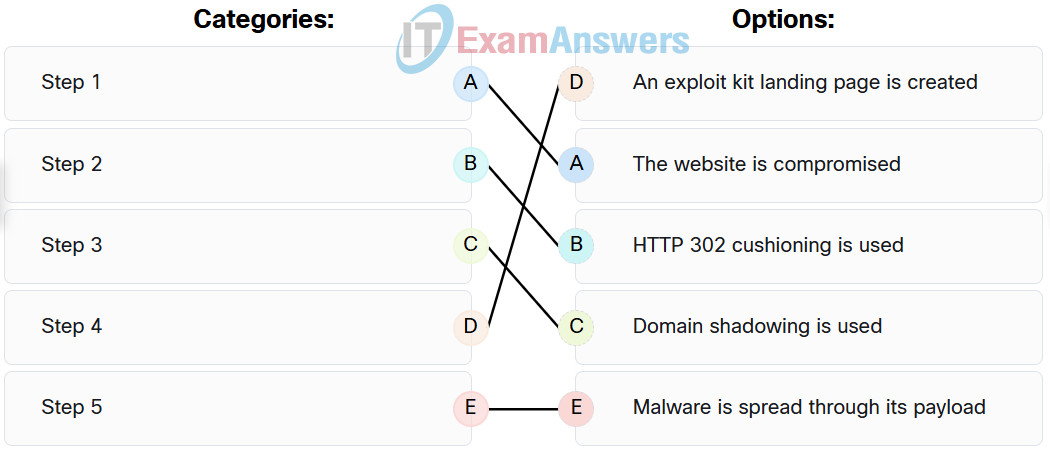
Explanation: Topic 4.2.2
Place the options in the following order:
| The website is compromised. |
Step 1 |
| HTTP 302 cushioning is used. |
Step 2 |
| Domain shadowing is used. |
Step 3 |
| An exploit kit landing page is created. |
Step 4 |
| Malware is spread through its payload. |
Step 5 |
33. What is a feature of distributed firewalls?
- They combine the feature of host-based firewalls with centralized management.
- They all use an open sharing standard platform.
- They use only TCP wrappers to configure rule-based access control and logging systems.
- They use only iptables to configure network rules.
Explanation: Topic 9.3.1
Distributed firewalls combine features of host-based firewalls with centralized management, which pushes rules to the hosts.
34. What does the telemetry function provide in host-based security software?
- It updates the heuristic antivirus signature database.
- It enables host-based security programs to have comprehensive logging functions.
- It blocks the passage of zero-day attacks.
- It enables updates of malware signatures.
Explanation: Topic 9.2.3
The telemetry function allows for robust logging functionality that is essential to cybersecurity operations. Some host-based security programs will submit logs to a central location for analysis.
35. What is an attack vector as it relates to network security?
- a path by which a threat actor can gain access to an internal network device
- a defense-in-depth approach to security
- a particular section of a network design where security is applied
- a method of reverse engineering binary files
Explanation: Topic 2.1.4
An attack vector is a path used by a threat actor to gain access to a server, host, or network and can originate from within the company or from the outside.
36. What occurs when a rogue access point is added to a WLAN?
- Authorized access points can transmit excess traffic to rogue access points to help alleviate congestion.
- Unauthorized users can gain access to internal servers, thus causing a security hole.
- All traffic that uses the same channel as the rogue access point will be encrypted.
- All traffic that uses the same channel as the rogue access point will be required to authenticate.
37. What is the reason for disabling SSID broadcasting and changing the default SSID on a wireless access point?
- The access point stops broadcasting its own MAC address, thus preventing unauthorized wireless clients from connecting to the network.
- Anyone with the default SSID can gain access to the access point and change the configuration.
- Disabling SSID broadcasting frees up radio frequency bandwidth and increases the data throughput of the access point.
- Wireless clients must then have the SSID manually configured to connect to the wireless network.
Explanation: Topic 5.3.2
The SSID is the name of the wireless network. Changing the default SSID forces device users to manually enter the SSID in order to gain access to the network. Broadcasting the SSID does not allow other devices to access the configuration, or to discover the MAC address of the device. SSID broadcasts do not affect radio frequency bandwidth.
38. Which two options can limit the information discovered from port scanning? (Choose two.)
- encryption
- firewall
- authentication
- intrusion prevention system
- passwords
Explanation: Topic 4.3.4
Using an intrusion prevention system (IPS) and firewall can limit the information that can be discovered with a port scanner. Authentication, encryption, and passwords provide no protection from loss of information from port scanning.
39. What does a rootkit modify?
- Microsoft Word
- operating system
- programs
- Notepad
- screen savers
Explanation: Topic 1.1.19
A rootkit commonly modifies an operating system to create a backdoor to bypass normal authentication mechanisms.
40. What is a nontechnical method that a cybercriminal would use to gather sensitive information from an organization?
- pharming
- man-in-the-middle
- social engineering
- ransomeware
Explanation: Topic 1.2.1
A cybersecurity specialist needs to be familiar with the characteristics of the different types of malware and attacks that threaten an organization.
41. Match the commonly used ports on a Linux server with the corresponding service.
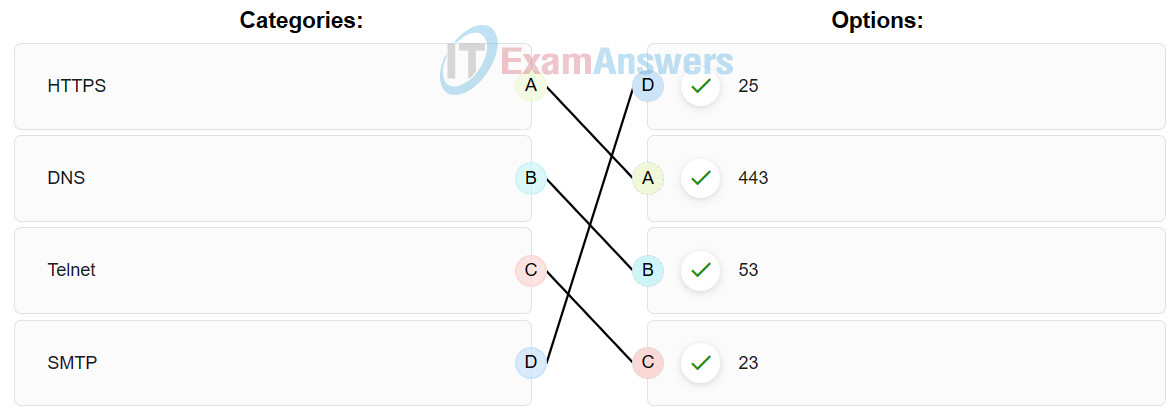
Explanation: Topic 8.3.2
Place the options in the following order:
| SMTP |
25 |
| DNS |
53 |
| HTTPS |
443 |
| Telnet |
23 |
42. Which statement describes the anomaly-based intrusion detection approach?
- It compares the antivirus definition file to a cloud based repository for latest updates.
- It compares the signatures of incoming traffic to a known intrusion database.
- It compares the operations of a host against a well-defined security policy.
- It compares the behavior of a host to an established baseline to identify potential intrusions.
Explanation: Topic 9.3.3
With an anomaly-based intrusion detection approach, a baseline of host behaviors is established first. The host behavior is checked against the baseline to detect significant deviations, which might indicate potential intrusions.
43. Match the security service with the description.

Explanation: Topic 6.3.1
| Allows administrators to manage network devices |
SNMP |
| Provides statistics on packets flowing through a Cisco router or multilayer switch |
NetFlow |
| Allows a switch to make duplicate copies of traffic that is sent to a traffic analyzer |
Port mirroring |
| A series of commands that control whether a device forwards or drops packets |
ACL |
44. What is an example of a local exploit?
- A threat actor tries to gain the user password of a remote host by using a keyboard capture software installed on it by a Trojan.
- A buffer overflow attack is launched against an online shopping website and causes the server crash.
- Port scanning is used to determine if the Telnet service is running on a remote server.
- A threat actor performs a brute force attack on an enterprise edge router to gain illegal access.
Explanation: Topic 2.2.1
Vulnerability exploits may be remote or local. In a local exploit, the threat actor has some type of user access to the end system, either physically or through remote access. The exploitation activity is within the local network.
45. Match the tabs of the Windows 10 Task Manager to their functions.
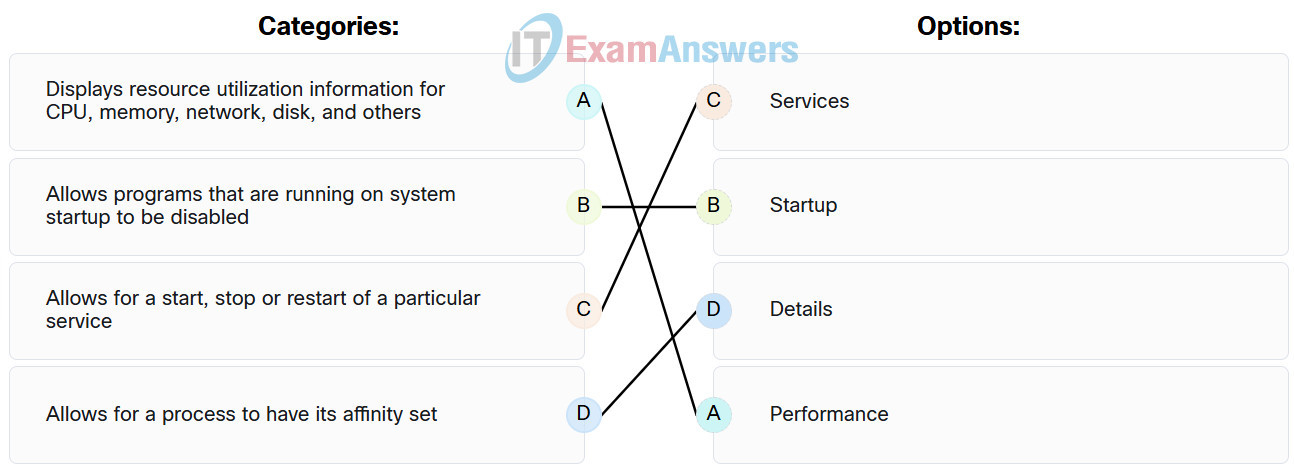
Explanation: Topic 7.3.6
| Details |
Allows for a process to have its affinity set. |
| Performance |
Displays resource utilization information for CPU, memory, network, disk, and others. |
| Startup |
Allows programs that are running on system startup to be disabled. |
| Services |
Allows for a start, stop or restart of a particular service. |
46. In an attempt to prevent network attacks, cyber analysts share unique identifiable attributes of known attacks with colleagues. What three types of attributes or indicators of compromise are helpful to share? (Choose three.)
- netbios names of compromised firewalls
- BIOS of attacking systems
- features of malware files
- IP addresses of attack servers
- changes made to end system software
- system ID of compromised systems
Explanation: Topic 2.2.6
Many network attacks can be prevented by sharing information about indicators of compromise (IOC). Each attack has unique identifiable attributes. Indicators of compromise are the evidence that an attack has occurred. IOCs can be identifying features of malware files, IP addresses of servers that are used in the attack, filenames, and characteristic changes made to end system software.
47. Which data state is maintained in NAS and SAN services?
- data in-process
- stored data
- data in-transit
- encrypted data
Explanation: Topic 10.2.2
A cybersecurity specialist must be familiar with the types of technologies used to store, transmit, and process data.
48. What is the result of a passive ARP poisoning attack?
- Network clients experience a denial of service.
- Multiple subdomains are created.
- Data is modified in transit or malicious data is inserted in transit.
- Confidential information is stolen.
Explanation: Topic 4.1.2
ARP poisoning attacks can be passive or active. The result of a passive attack is that cybercriminals steal confidential information. With an active attack, cybercriminals modify data in transit or they inject malicious data.
49. The entrepreneur is concerned about company employees having uninterrupted access to important resources and data. Which of the CIA triad components would address the concern?
- integrity
- availability
- authentication
- confidentiality
Explanation: Topic 10.1.7
Communications security is usually discussed using the CIA triad: confidentiality, integrity, and availability. Confidentiality ensures that only authorized individuals, devices, entities, or processes can access sensitive information. Integrity protects data from unauthorized alteration. Availability provides uninterrupted access for authorized users to important resources and data.
50. Users report that a database file on the main server cannot be accessed. A database administrator verifies the issue and notices that the database file is now encrypted. The organization receives a threatening email demanding payment for the decryption of the database file. What type of attack has the organization experienced?
- Trojan horse
- ransomware
- DoS attack
- man-in-the-middle attack
Explanation: Topic 1.3.3
A cybersecurity specialist needs to be familiar with the characteristics of the different types of malware and attacks that threaten an organization.
51. Which is a Windows 10 feature that encrypts removable drives?
- BitLocker To Go
- MRT
- LeafPad
- XProtect
Explanation: Topic 9.1.8
BitLocker To Go is a specialized feature in Windows 10 designed specifically to encrypt removable drives, such as USB flash drives. Unlike standard BitLocker, which often requires a TPM chip for internal disk encryption, BitLocker To Go secures data on portable media by requiring a password to decrypt and access the contents.
52. What is the function provided by the Burpsuite tool in Kali Linux?
- managing
- logging
- scanning
- penetration test
Explanation: Topic 8.1.4
Burpsuite is a specialized tool integrated into Kali Linux, a distribution designed to provide cybersecurity professionals with a comprehensive suite of programs for network security penetration testing. It is primarily used to identify, analyze, and exploit vulnerabilities in web applications to help organizations evaluate and improve their security posture.
53. Which file system is for MAC OS X computers, and Windows users may use third-party software to open and save files from this file system?
Explanation: Topic 7.2.3
HFS+ (Hierarchical File System Plus) is the primary file system used on MAC OS X computers. Although it is not natively supported by the Windows operating system, Windows users can open and save files from HFS+ partitions by using specialized third-party software or drivers.
54. A student is learning about authentication protocols and how they are used to communicate with AAA servers. Which statement describes a characteristic of such protocols?
- TACACS+ is a standard mostly Cisco equipment support, while RADIUS is an open standard.
- TACACS+ combines authentication and authorization, while RADIUS separates AAA according to the AAA architecture.
- RADIUS is considered the more secure protocol because all RADIUS protocol exchanges are encrypted.
- RADIUS uses a bidirectional challenge and response (CHAP), while TACACS+ uses a unidirectional challenge.
Explanation: Topic 6.2.10
TACACS+ is a Cisco-proprietary protocol, whereas RADIUS is an open/RFC standard used across various vendors. Furthermore, TACACS+ separates authentication and authorization for better modularity and encrypts the entire packet for higher security, while RADIUS combines those functions and only encrypts the password.
55. Which statement describes a characteristic on WLANs?
- IEEE 802.11 prescribes CSMA/CD for media access to proactively avoid collisions within the media.
- An attacker may not have to physically enter the workplace to gain access to a WLAN.
- Tethering is a variation of infrastructure mode
- The 5GHz band is more prone to interference than the 2.4 GHz.
Explanation: Topic 5.2.2
WLANs use radio frequencies that can extend beyond the physical walls of a building. Because the signal is available to anyone within range who has a wireless NIC, a threat actor can attempt to intercept data or exploit vulnerabilities from outside the organization's boundaries, making physical entry unnecessary.
56. What kind of attack is performed by a threat actor that places non-DNS traffic in DNS records?
- DNS resource utilization
- DNS cache poisoning
- DNS tunneling
- DNS amplification and reflection
Explanation: Topic 4.1.4
DNS tunneling is an attack where threat actors place non-DNS traffic within DNS traffic to circumvent security solutions. By altering various DNS records (such as TXT, MX, or CNAME), they can encapsulate data or commands to exfiltrate sensitive information or communicate with infected hosts within a botnet.
57. What are the characteristics of IPv4 and IPv6 protocols?
- IPv6 packets are not fragmented by routers, unlike IPv4 packets
- Both IP versions use the same checksum calculation
- Only IPv4 has a counter field to limit the lifetime of a packet on a network
- Both IP versions have the same size of header, but with different fields
Explanation: Topic 3.1.4
IPv4 and IPv6 protocols differ significantly in how they handle packet lifetime and size constraints. In IPv4, routers can fragment packets that are too large for a specific route, whereas in IPv6, routers do not perform fragmentation. Additionally, while IPv4 uses a "Time-to-Live" (TTL) field, IPv6 replaces this with a "Hop Limit" field to achieve the same goal of limiting packet lifetime. Finally, the IPv6 header is a fixed 40 bytes, which is larger than the minimum 20-byte IPv4 header.
58. Which type of cyber threat would cause electrical power outages?
- Utility interruption
- Human error
- Sabotage
- Hardware failure
Explanation: Topic 1.1.2
Utility interruption is a cyber threat that can cause Electrical power outages and water damage resulting from sprinkler failure.

